Kratos
- 36
- Global rank
- 23
- Month rank
- 26
- Week rank
Kratos is a mature Phishing-as-a-Service (PhaaS) platform that evolved from the Sneaky2FA kit to specialize in stealing Microsoft 365 credentials through sophisticated Adversary-in-the-Middle (AiTM) techniques. The service provides low-skilled affiliates with a turnkey solution featuring an advanced administrative dashboard, integrated anti-bot defenses, and real-time data exfiltration via the Telegram Bot API. Although an international law enforcement action known as Operation Olympus Blade disrupted its central infrastructure in July 2026, the kit remains a primary example of the industrialization of modern cybercrime.
- Phishingkit
- Type
- Unknown
- Origin
- 1 September, 2025
- First seen
- 20 October, 2026
- Last seen
How to analyze Kratos with ANY.RUN
IOCs
IP addresses
- 2.16.206.14
- 74.178.240.61
- 52.111.240.11
- 23.48.23.24
- 23.48.23.17
- 2.16.204.142
- 20.190.160.5
- 13.107.246.44
- 2.23.244.64
- 23.48.23.30
- 13.69.116.108
- 20.184.175.16
- 150.171.27.11
- 52.108.9.12
- 150.171.109.100
- 20.99.134.80
- 150.171.22.17
- 23.48.23.8
- 23.48.23.50
- 23.11.40.157
Hashes
- 05828d625dcb5781d0a3cc67a2429ced535fdf848b8b8075d49751eb5b30c7af
- db39694c444ea393569aafb2cd8ec865006f3df9ecbcb7996e7b219b30ec366d
- b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
- 96de196759182729159b02436db60cd5a7309170d1056e844c042a32f94a8690
- 0463963d26a98ed6f3512f953ec4f4cf12b0d44fe3ee4b50561736aa39d36383
- 3c8f27e6009ccfd710a905e6dcf12d0ee3c6f2ac7da05b0572d3e0d12e736fc8
- 75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
- 907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
- 22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
- 3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
- 3dbd2c90050b652d63656481c3e5871c52261575292db77d4ea63419f187a55b
- b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
- 4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
- e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
- 3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
- a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
- a41670d52423ba69c7a65e7e153e7b9994e8dd0370c584bda0714bd61c49c578
- 54241ebe651a8344235cc47afd274c080abaebc8c3a25afb95d8373b6a5670a2
- bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
- 35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
Domains
- fa000000111.resources.office.net
- amcdn.msftauth.net
- config.edge.skype.com
- static.edge.microsoftapp.net
- edge.microsoft.com
- self.events.data.microsoft.com
- cdn.onenote.net
- res.cdn.office.net
- www.bing.com
- fa000000128.resources.office.net
- update.googleapis.com
- login.microsoftonline.com
- admin.microsoft.com
- cdn.jsdelivr.net
- xpaywalletcdn.azureedge.net
- ecs.office.com
- arc.msn.com
- aadcdn.msftauth.net
- browser.events.data.microsoft.com
- edge-mobile-static.azureedge.net
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:axabpc08mzuuqtp7rv-sm8ndwhr3symr-v8xyl6uota&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
- https://copilot.microsoft.com/c/api/user/eligibility
- https://vplaza-my.sharepoint.com/:o:/g/personal/vplaza_vplaza_onmicrosoft_com/igboawteggoqtjb7r-yisbefayf_zxykenojct6k1jk6nfm?e=rr2kby
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1792510020&lafgdate=0
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://vplaza-my.sharepoint.com/personal/vplaza_vplaza_onmicrosoft_com/_layouts/15/doc.aspx?sourcedoc=%7bc464014e-6a80-4c10-907b-afec88b0179f%7d&action=default&slrid=92c146a2-e0cf-9000-7a5d-c528aca79522&originalpath=ahr0chm6ly92cgxhemetbxkuc2hhcmvwb2ludc5jb20vom86l2cvcgvyc29uywwvdnbsyxphx3zwbgf6yv9vbm1py3jvc29mdf9jb20vswdct0fxvevnr29rvepcn3iteulzqmvmqvlmx1pyeutftm9qy1q2azfqazzork0_cnrpbwu9uzhhs2w3nhuzmgc&cid=7c5c312d-9958-4e18-a2ad-220778c9eaaa&_srm=0:g:83
- https://euc-onenote.officeapps.live.com/o/remotetelemetry.ashx?usid=a055b5ed-d47e-93ae-1085-75cdc98c6eb2
- https://euc-onenote.officeapps.live.com/o/remoteuls.ashx?usid=a055b5ed-d47e-93ae-1085-75cdc98c6eb2&officeserverversion=
- https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
- https://res.public.onecdn.static.microsoft/wise/owl/owl.slim.c2f100173a3474695a11.js
- https://res.public.onecdn.static.microsoft/wise/owl/onenote-boot.8ce0add4725e96c1c050.js
- https://res.public.onecdn.static.microsoft/files/odsp-web-prod_2026-10-02.003/wacowlhostwebpack/wacowlhostwebpack.js
- https://res.public.onecdn.static.microsoft/files/sp-client/odsp.react-18/odsp.react.lib-6b50f427.js
- https://res.public.onecdn.static.microsoft/files/sp-client/odsp.1ds/odsp.1ds.lib-6cc734ee.js
- https://res.public.onecdn.static.microsoft/files/odsp-web-prod_2026-10-02.003/require-2495d64e.js
Last seen at
- vplaza-my.sharepoint.com
- itgastronomy-my.sharepoint.com
- 459d186c-9d8e-44f4-b745-4b486eadafa4
- te620343503r0-my.sharepoint.com
- attachment (50).eml
- RE Demande sur distribution de dividendes # 260900012.eml (832Ko).msg
- stlm-transportsprojetdocuments.bizfile.my
- stlm-transportsprojetdocuments.bizfile.my
- RE Demande sur distribution de dividendes # 260900012(1).eml (138Ko).msg
- levadadigital.com.br
The Kratos PhaaS: How Turnkey Phishing Scales Microsoft 365 Account Takeovers
Key Takeaways
- Kratos is a sophisticated Phishing-as-a-Service (PhaaS) platform specifically engineered to industrialize the theft of Microsoft 365 credentials and bypass multi-factor authentication (MFA).
- The platform shares hosting infrastructure with other AiTM phishing kits, including Tycoon, Flowerstorm, Sneaky2FA, and EvilProxy.
- In July 2026, a major international law enforcement action known as Operation Olympus Blade disrupted the service, leading to the shutdown of over 200 servers and the arrest of the lead developer in Indonesia.
- Despite its disruption, the kit was highly scalable, supporting over 1,800 criminal subscribers who launched an estimated 15,000 phishing campaigns per month.
- Kratos utilizes a decoupled architecture, ensuring that harvested data is exfiltrated in real-time to Telegram bots, which allows stolen information to remain accessible even if the phishing URLs are taken down.
- ANY.RUN researchers identified unique technical fingerprints, specifically the presence of barr.svg and lg.svg assets, which provide near-100% accuracy in attributing malicious activity to the Kratos family.
What is Kratos?
Kratos is a subscription-based cybercrime service that provides a "turnkey" solution for threat actors looking to compromise Microsoft 365 environments at scale. As a Phishing-as-a-Service (PhaaS) model, it lowers the barrier to entry for low-skilled attackers by offering a centralized administrative dashboard that automates the deployment of phishing domains, VPS infrastructure, and anti-bot protections.
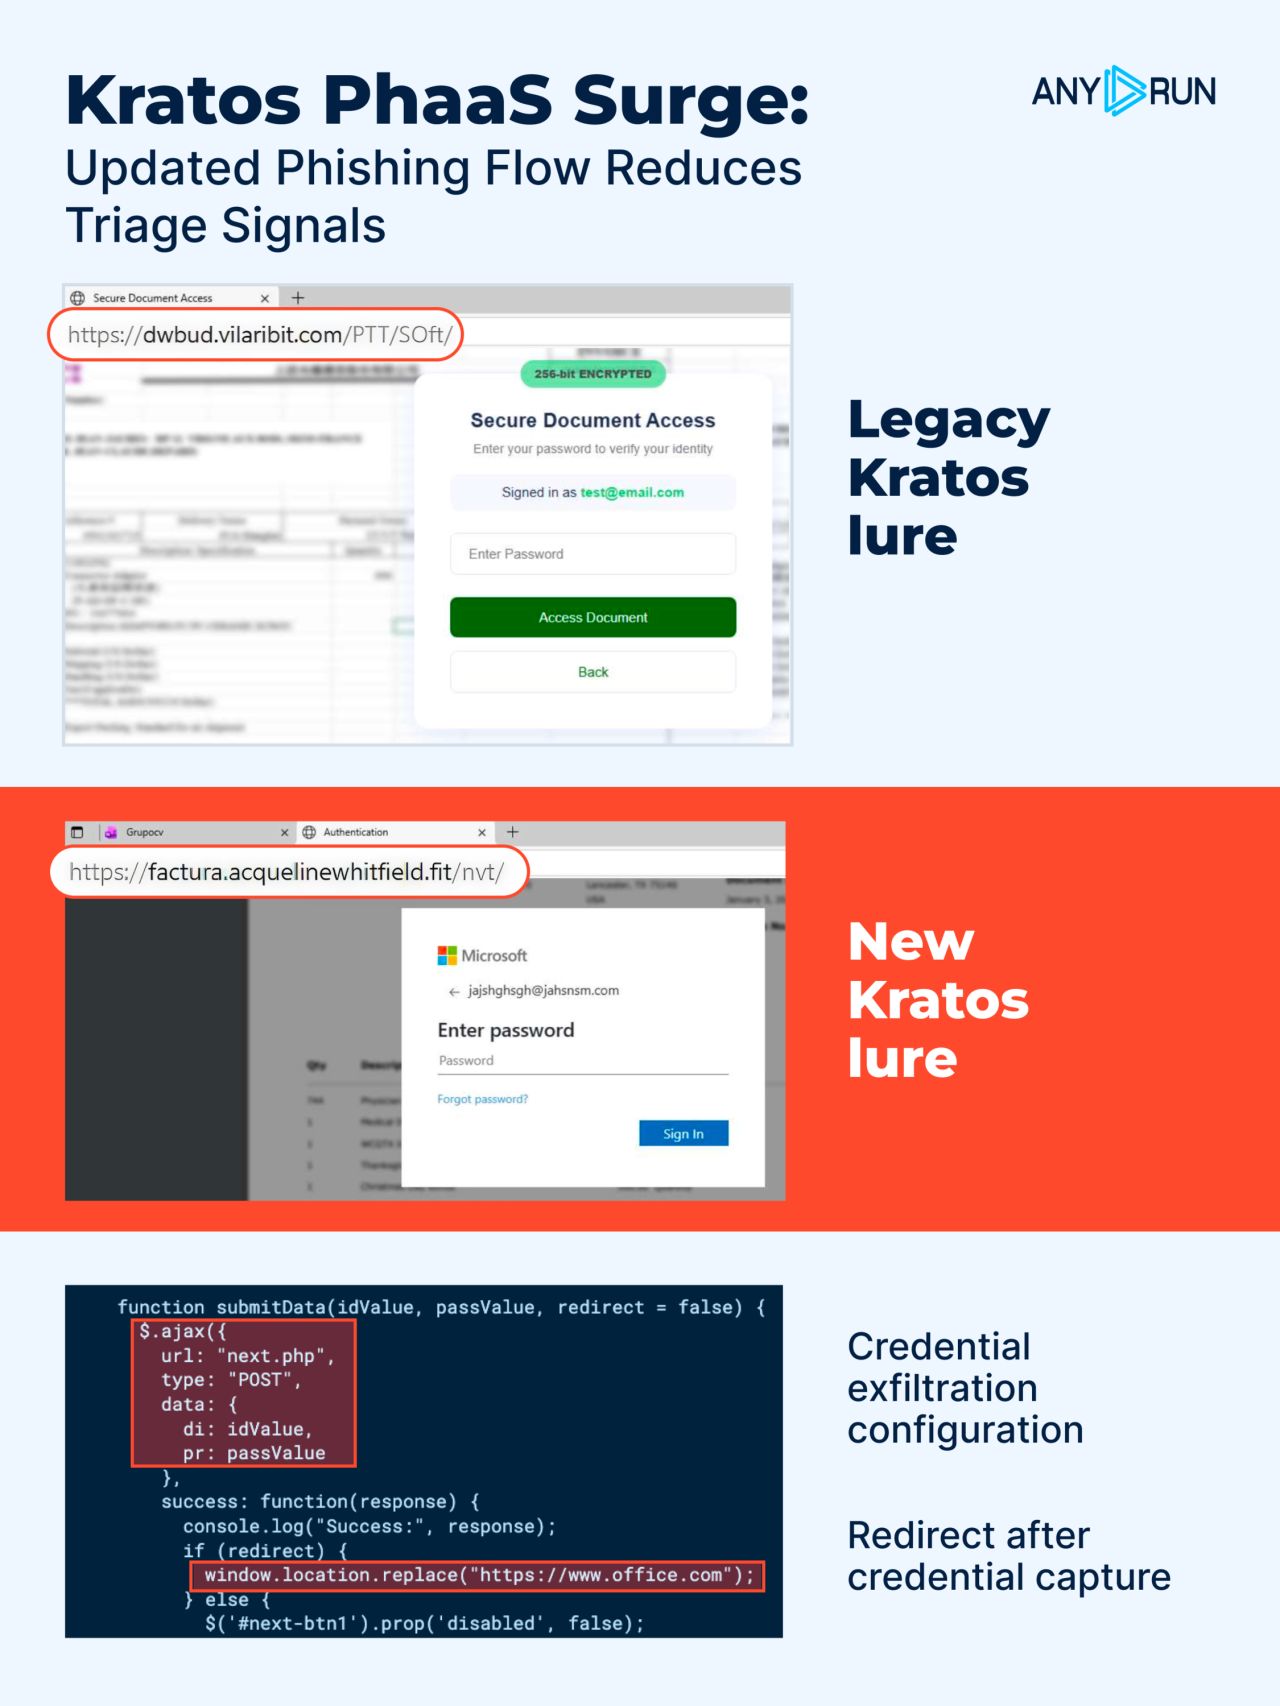
The kit represents a significant technical evolution from its predecessor, Sneaky2FA. While earlier versions functioned as traditional info-stealers, the modern Kratos platform utilizes adversary-in-the-middle (AiTM) techniques to relay live authentication sessions between victims and legitimate Microsoft login servers. This allows the kit to capture not only passwords but also the session tokens required to bypass MFA challenges.
The "business" of Kratos is highly organized, operating through Telegram-based subscriptions where affiliates pay for access to ready-made phishing templates, such as those mimicking Adobe Creative Cloud or DocuSign. The platform's internal logic includes advanced features such as:
- Automated Vetting: Using services like geoplugin[.]net to geolocate victims and filter out non-target regions or security researchers.
- Anti-Analysis Defenses: Integrated support for Cloudflare Turnstile, reCAPTCHA, and hCaptcha to prevent automated scanners from detecting the phishing pages.
- Multi-Generational Development: ANY.RUN has tracked the kit through three distinct generations (V0, V1, and V2), showing a steady progression toward more convincing brand impersonation and more heavily obfuscated code to evade security vendor signatures.
By utilizing an encrypted exfiltration chain via the Telegram Bot API, Kratos ensures that its criminal operators can receive stolen credentials instantly and securely, blending their malicious traffic with legitimate web service activity.
How Kratos Threatens Businesses and Organizations
Kratos represents a significant escalation in the threat landscape because it moves beyond simple password harvesting toward total account takeover (ATO) and long-term persistence within corporate environments.
By industrializing the theft of Microsoft 365 credentials, the platform creates several critical risks for modern enterprises:
- Advanced Business Email Compromise (BEC): Once an account is compromised, attackers can monitor executive communications, intercept ongoing financial conversations, and alter payment instructions. Because these fraudulent requests originate from a legitimate, trusted mailbox, they are extremely difficult for both automated filters and employees to detect.
- Bypassing Multi-Factor Authentication (MFA): Unlike traditional phishing kits that only steal passwords, Kratos employs Adversary-in-the-Middle (AiTM) techniques. By relaying live authentication sessions between the victim and Microsoft's real servers, the kit captures active session tokens. This allows attackers to bypass MFA challenges entirely, as the token confirms to Microsoft that the "user" has already authenticated.
- Persistent Infrastructure Access: A major danger of Kratos is its ability to maintain access even after a security incident is identified. If an attacker gains session access through a stolen token, a simple password reset may not be enough to remove them. Unless security teams explicitly revoke active sessions and refresh tokens, the threat actor can remain inside the environment indefinitely.
- Data and Partner Exposure: Compromised accounts provide a gateway to sensitive business data stored in SharePoint, Teams, and OneDrive. This exposure often extends to third-party partners and suppliers, as attackers can use the compromised account to harvest contact lists and launch secondary attacks against the organization’s entire supply chain.
Victimology: Who Is Most Vulnerable?
The Kratos platform is a global threat that has successfully targeted victims in over 30 countries. While its reach is international, analysis of ANY.RUN Interactive Sandbox data and industry reports reveals specific geographic and sectoral concentrations:
- Primary Focus on the United States: The U.S. remains the most targeted region, accounting for approximately 33% of all observed Kratos activity.
- Strong Concentration in Southern Europe: Researchers have identified a heavy focus on Spain and other Southern European nations. This is evidenced by the use of Spanish-language "tokens" in the phishing URLs, such as abogados (lawyers), factura (invoice), and dgt (Spain’s traffic authority).
- Sector-Agnostic Targeting: While the platform hits a wide range of industries, the targeting is largely opportunistic. Vulnerable sectors include legal and financial services, education and healthcare, industrial and SMBs.
Ultimately, any organization that relies on Microsoft 365 for its daily operations is within the scope of Kratos. The kit does not exploit a software vulnerability but rather exploits the human element and the ubiquitous nature of Microsoft’s authentication workflows.
How Does Kratos Malware Function? (The Sandbox Analysis)
Detonating a Kratos sample in the ANY.RUN Interactive Sandbox provides a clear, step-by-step view of how the PhaaS platform operates. By moving beyond static analysis, defenders can observe the following stages of the attack in real-time:
Stage 1: The Intermediary Lure and "Buffer" Pages
The Kratos infection chain begins with a targeted phishing email that is frequently successful in bypassing corporate email filters and secure email gateways.
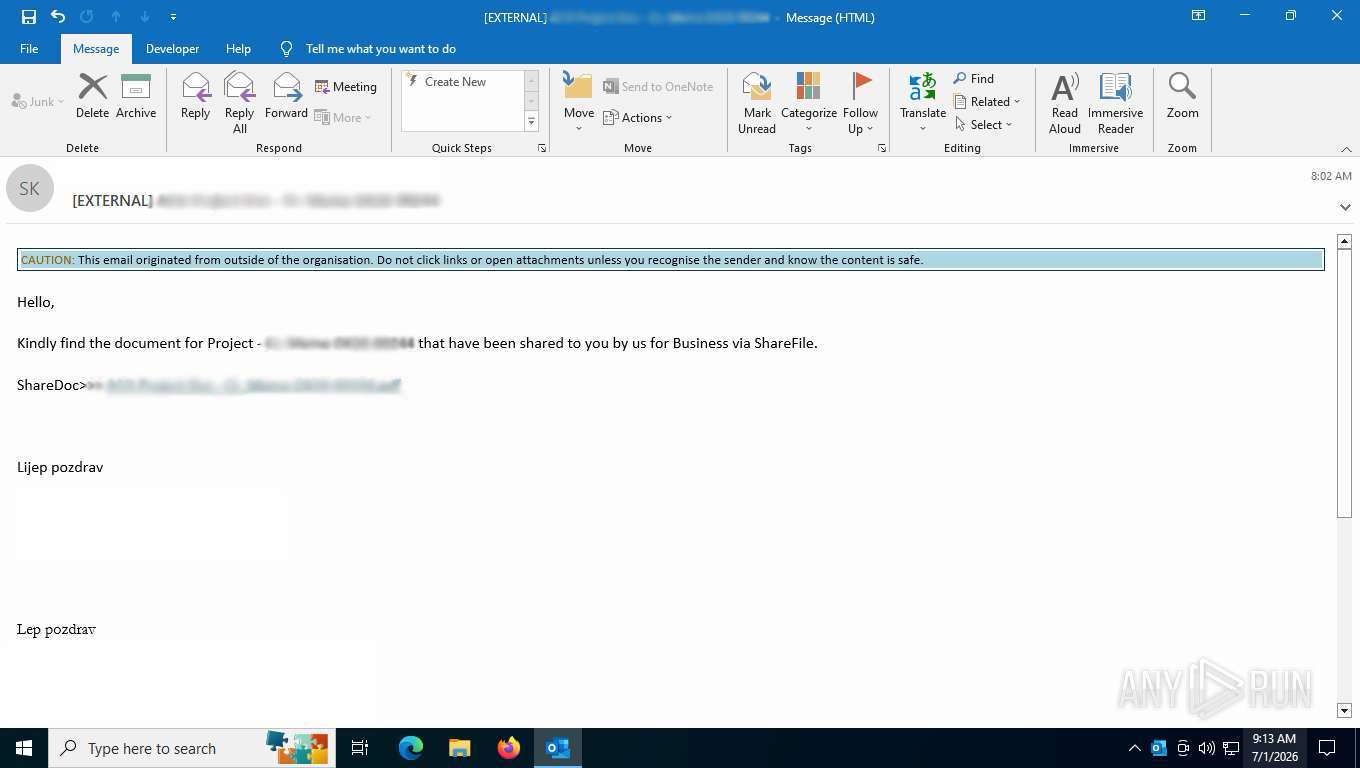
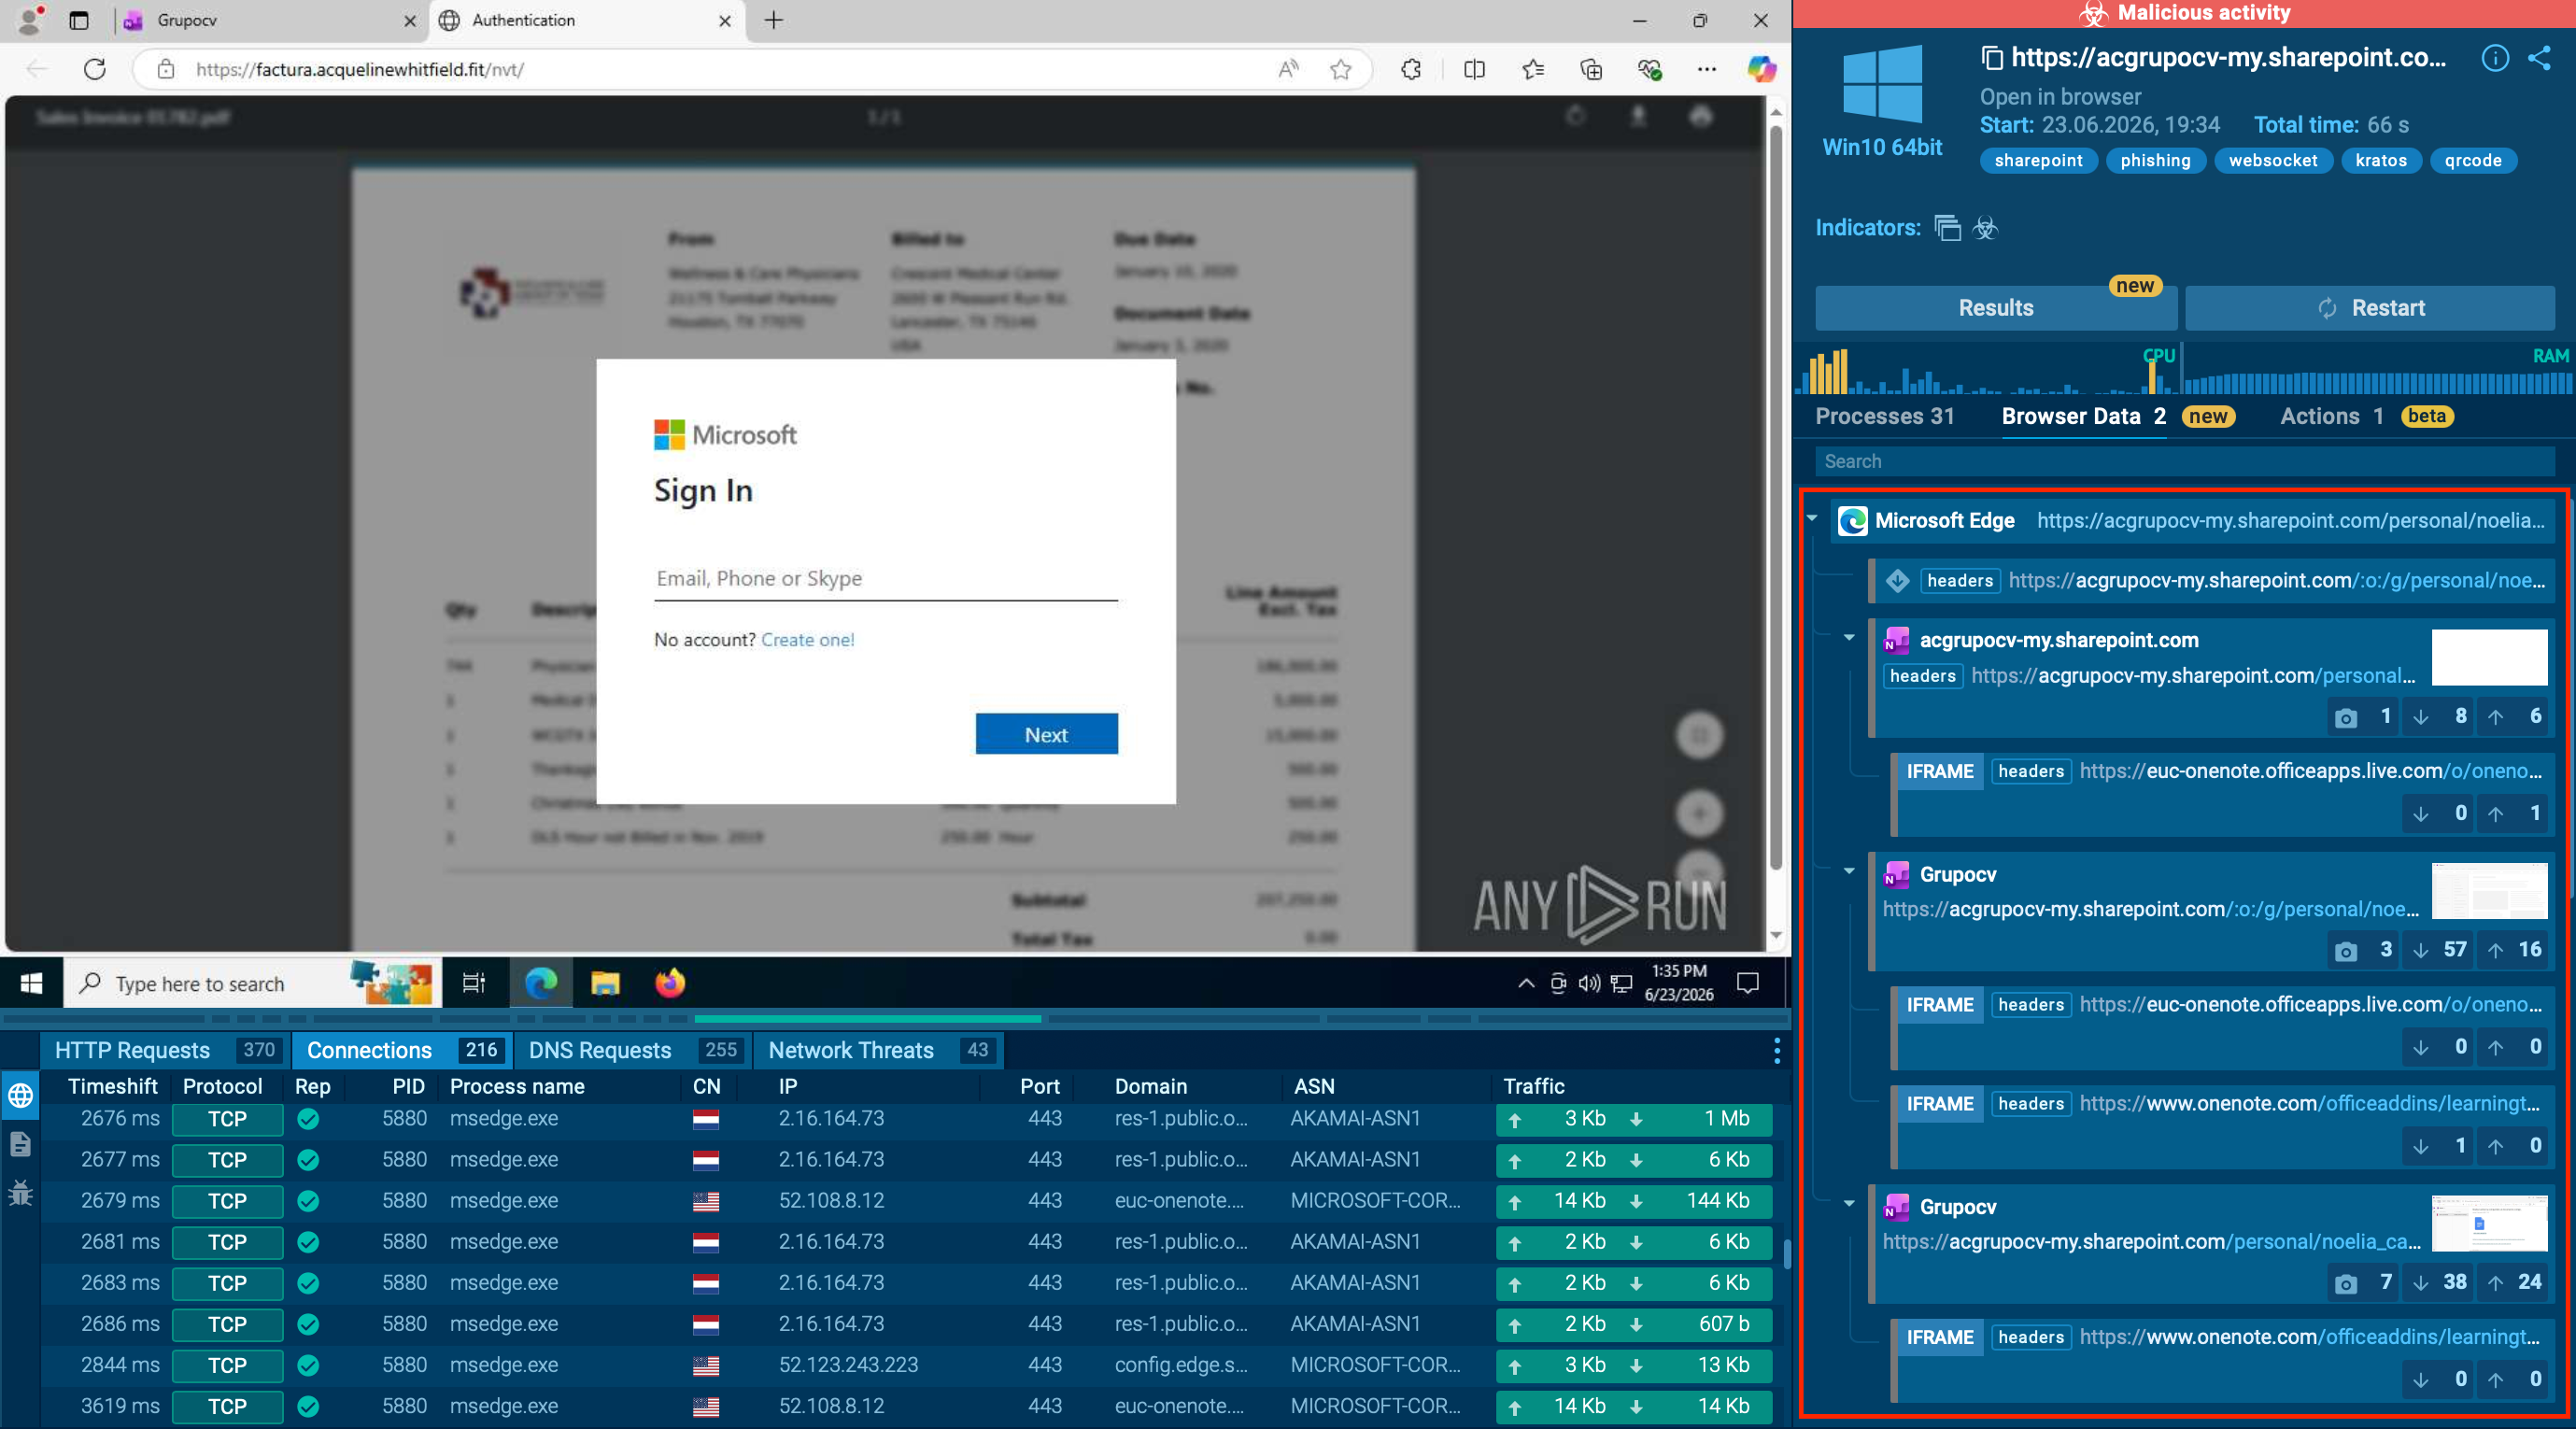
To further evade detection by automated scanners, the attack does not link directly to the final phishing landing page. Instead, the email directs the victim to an intermediary "buffer" site hosted on a legitimate, trusted platform. In the ANY.RUN Sandbox, analysts frequently observe redirects through services such as Microsoft SharePoint, OneDrive, Canva, Tilda, or Microsoft Forms.
Stage 2: Passing the "Challengepoint"
Before the phishing form is even loaded, Kratos initiates a verification gate to filter out automated security crawlers. The victim is presented with a Cloudflare Turnstile or CAPTCHA. In the network logs, this is often identified as "challengepoint". This step ensures that the sandbox is being operated by a human, making it harder for headless security scanners to reach the payload.
Stage 3: Visual Social Engineering Hallmarks
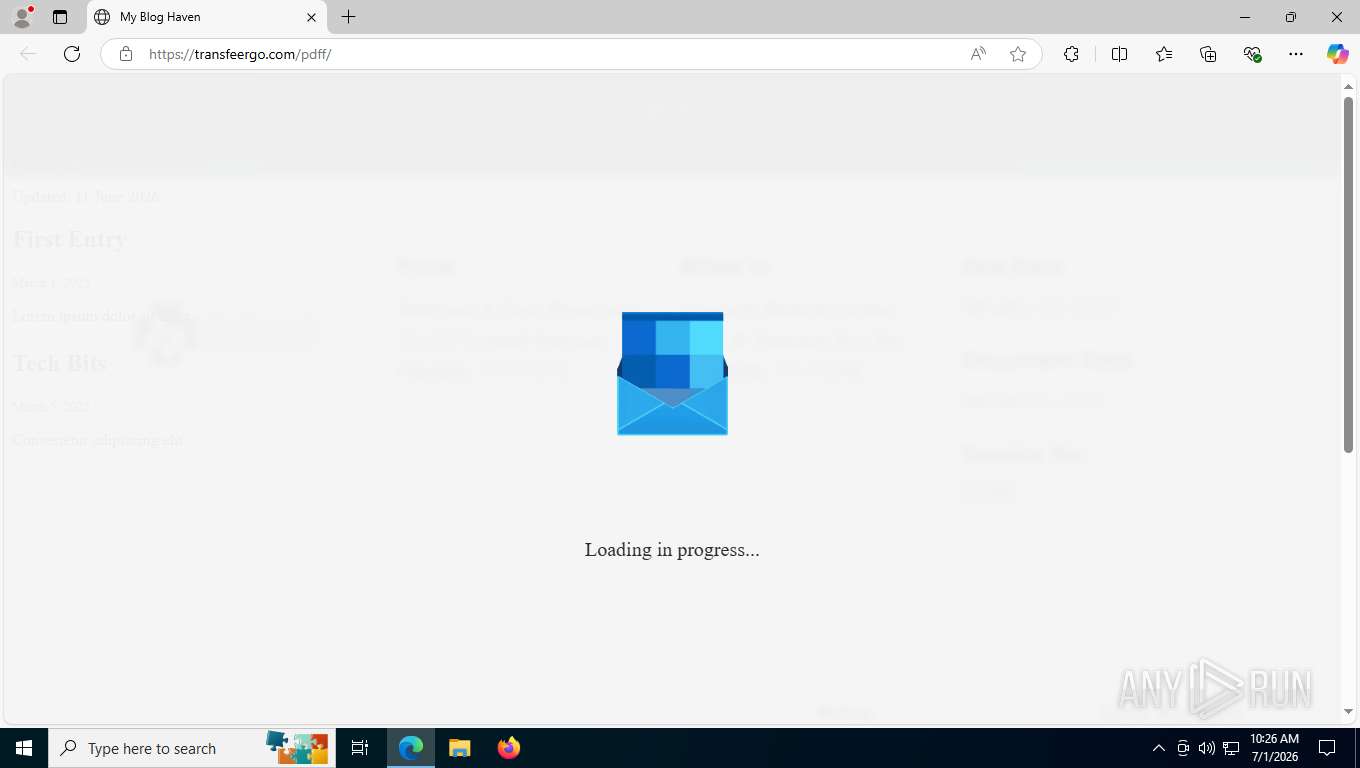
Once verified, the kit presents its unique visual identity. A distinctive feature of Kratos is the animated envelope screen. The victim sees an animation with the message “Loading in progress…” overlaid on a blurred image of an invoice or document. The browser tab title typically changes to “Authentication” during this phase. This high-fidelity branding is designed to build trust immediately before requesting credentials.
Stage 4: Real-Time Data Harvesting and Exfiltration
The most critical part of the analysis occurs during the login attempt. Using ANY.RUN’s In-browser data inspection, analysts can deobfuscate the script behavior:
- The Functionality: Analysts can see the submitData() function capturing the user's input (marked as di and pr parameters).
- The Endpoints: Depending on the generation, the data is sent via a POST request to specific PHP endpoints: /next.php (V1), /save.php (V2), or /mini.php (V0).
- AiTM Indicators: The sandbox may also record WebSocket activity, which is a strong behavioral signal of Adversary-in-the-Middle (AiTM) behavior, where the kit relays session data in real-time to bypass MFA.
Stage 5: Telegram Bot Communication
Kratos uses a decoupled architecture, meaning the exfiltration happens server-side, but its traces are visible in the sandbox's network traffic:
The Dropzone: The kit communicates with the Telegram Bot API to send stolen data to the attacker’s private channel.
Data Packaging: Credentials, IP addresses, geolocations, and device types are bundled into JSON logs, ensuring the attacker receives the data even if the phishing site is taken down immediately.
Stage 6: The Exit and Redirection
To avoid suspicion, the kit limits login attempts. In the sandbox, analysts can observe that after three failed attempts, the victim is automatically redirected to a legitimate URL. This final step is intended to make the victim believe they simply had a minor login error, delaying any potential report to their IT security team.
How Businesses Can Use ANY.RUN’s Threat Intelligence Against Kratos
ANY.RUN’s Threat Intelligence serves as a powerful proactive defense solution, allowing SOC teams to move beyond a single indicator and view the entire Kratos ecosystem through a continuously updated threat database that is based on sandbox submissions by 15K organizations and 600K security analysts.
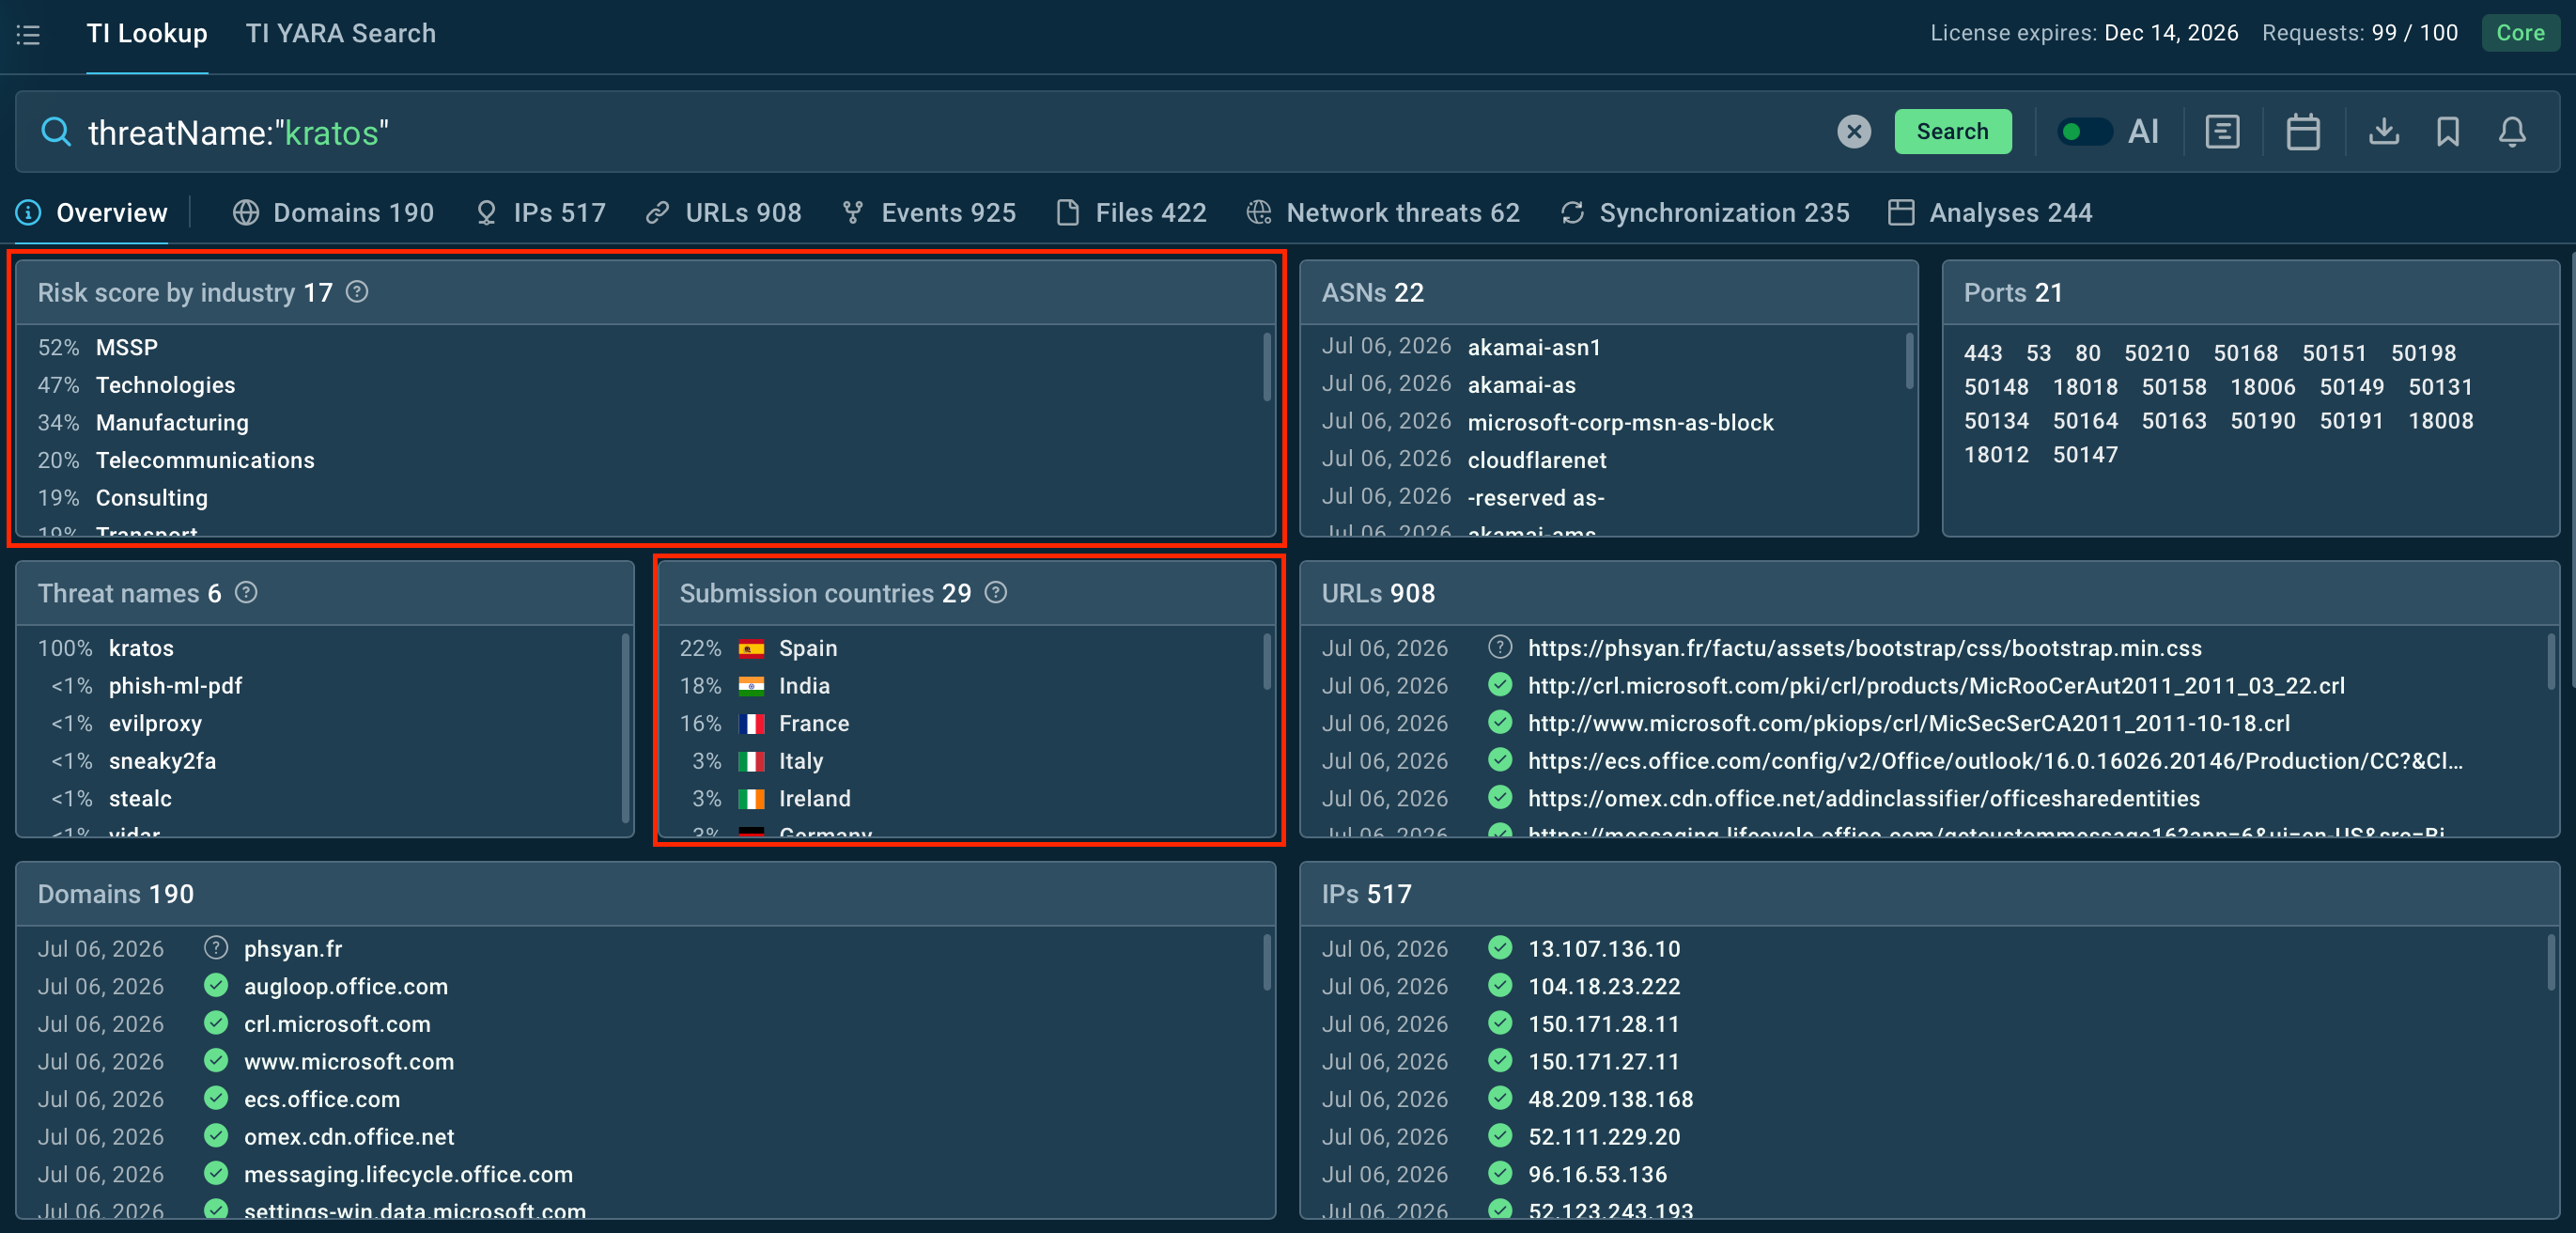
Threat Intelligence Lookup allows for precise family-level identification. By using the query threatName:"kratos", analysts can instantly access a consolidated view of all data related to Kratos attacks globally. This helps teams understand the current scale of the threat and determine if their specific industry or region is currently being targeted by active clusters.
One of the most effective ways to use TI Lookup against Kratos is by searching for static asset hashes. Even when attackers change their domain names or rename files, the underlying content of the kit remains largely the same.
Cross-Campaign Linking: Analysts can query for the specific SHA256 hash of the styles.css file, which has been found to connect over 630 sandbox analyses across both the V1 and V2 generations of the kit.
Asset Fingerprinting: Searching for the unique hashes of files like lg.svg (V1) or dsa.svg (V2) allows teams to identify Kratos landing pages with near-100% accuracy, even on compromised legitimate websites where the file path might be hidden.
Check this TI Lookup query based on the lg.svg and styles.css hashes:
By integrating TI Lookup queries into their regular hunting workflows, SOC and MSSP teams can significantly reduce business exposure to Kratos and contain account compromise attempts before they escalate into full-scale data breaches.
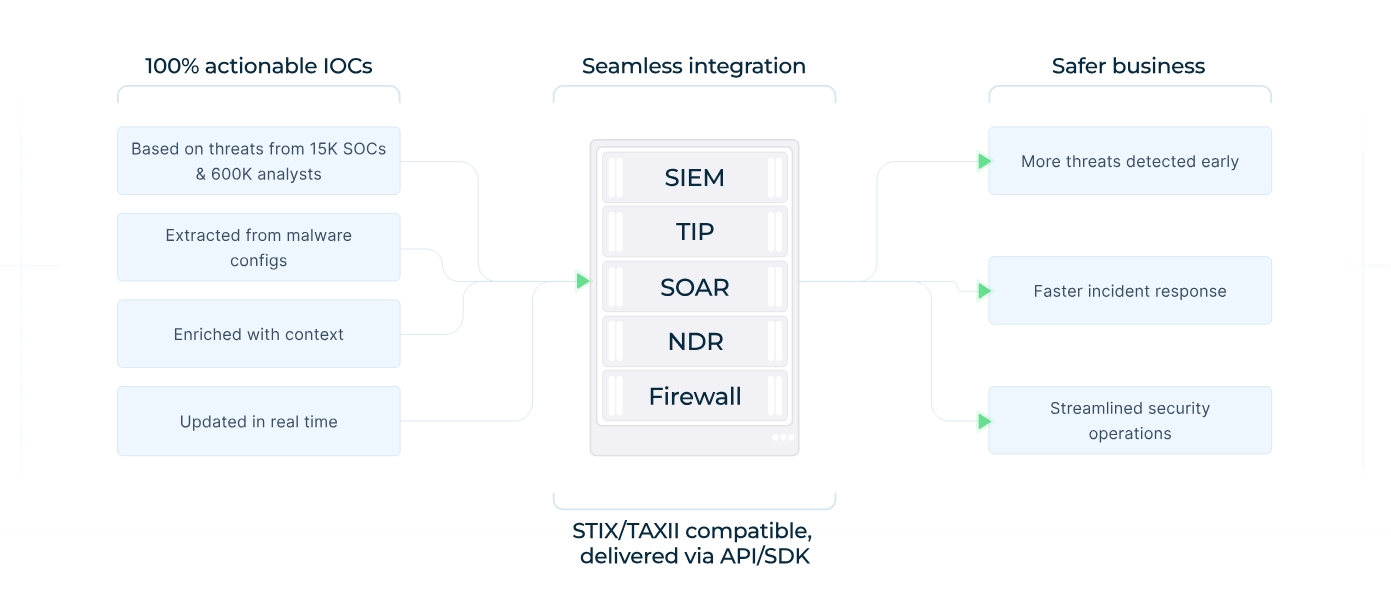
For organizations looking to automate their defense, ANY.RUN’s Threat Intelligence Feeds provide a continuous stream of the most recent network indicators (IPs, domains, and URLs) associated with active phishing campaigns. The TI Feeds are updated in real time based on the latest threat submissions to ANY.RUN’s Sandbox from 15K organizations and 600K analysts.
By integrating these feeds into SIEMs and security controls, teams can automatically block emerging phishing infrastructure and detect malicious activity before attackers establish persistence or hijack session tokens.
Conclusion
While Operation Olympus Blade successfully dismantled the central Kratos infrastructure in July 2026, the broader Phishing-as-a-Service (PhaaS) ecosystem is only gaining momentum. Industry projections estimate that over 90% of all credential compromise attacks will be enabled by modular PhaaS kits by the end of 2026.
The rapid emergence of alternative platforms, such as Kali365, demonstrates that as one service is taken offline, others quickly fill the void to target Microsoft 365 environments. For organizations, the focus must shift from reacting to individual takedowns to maintaining proactive visibility through threat intelligence and adopting defense-in-depth strategies, such as revoking active session tokens rather than relying solely on password resets.
Frequently Asked Questions: Kratos PhaaS
1. What is Kratos PhaaS?
Kratos is a turnkey Phishing-as-a-Service platform used to steal Microsoft 365 credentials. It is a direct evolution of the Sneaky2FA kit.
2. How does it bypass MFA?
It employs Adversary-in-the-Middle (AiTM) techniques to proxy live login sessions and capture session tokens, allowing attackers to bypass multi-factor authentication entirely.
3. What are the key indicators of a Kratos attack?
Visually, victims see a “Loading in progress…” animation over a blurred document. Technically, the kit is identified by assets like barr.svg and lg.svg (V1) or dsa.svg and sid.gif (V2).
4. How is stolen data exfiltrated?
Stolen credentials and metadata are packaged as JSON and sent in real-time to Telegram bots, ensuring data remains accessible even if the phishing site is taken down.
5. Was the Kratos infrastructure shut down?
Yes. In July 2026, Operation Olympus Blade dismantled the service, shutting down over 200 servers and resulting in the lead developer's arrest in Indonesia.
6. Who are the primary targets?
The platform has a global reach (30+ countries), focusing heavily on the United States (33%) and Southern Europe, particularly Spain.
Other malware & phishing threats
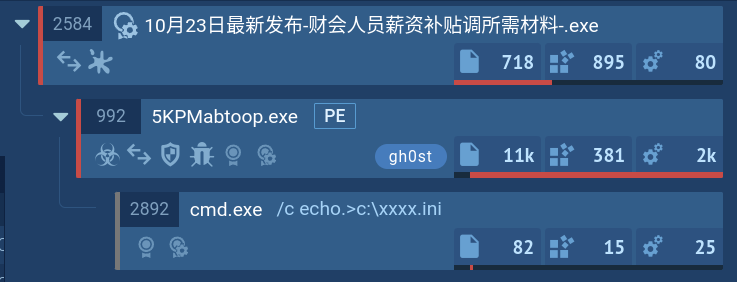 Gh0st RATGh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.
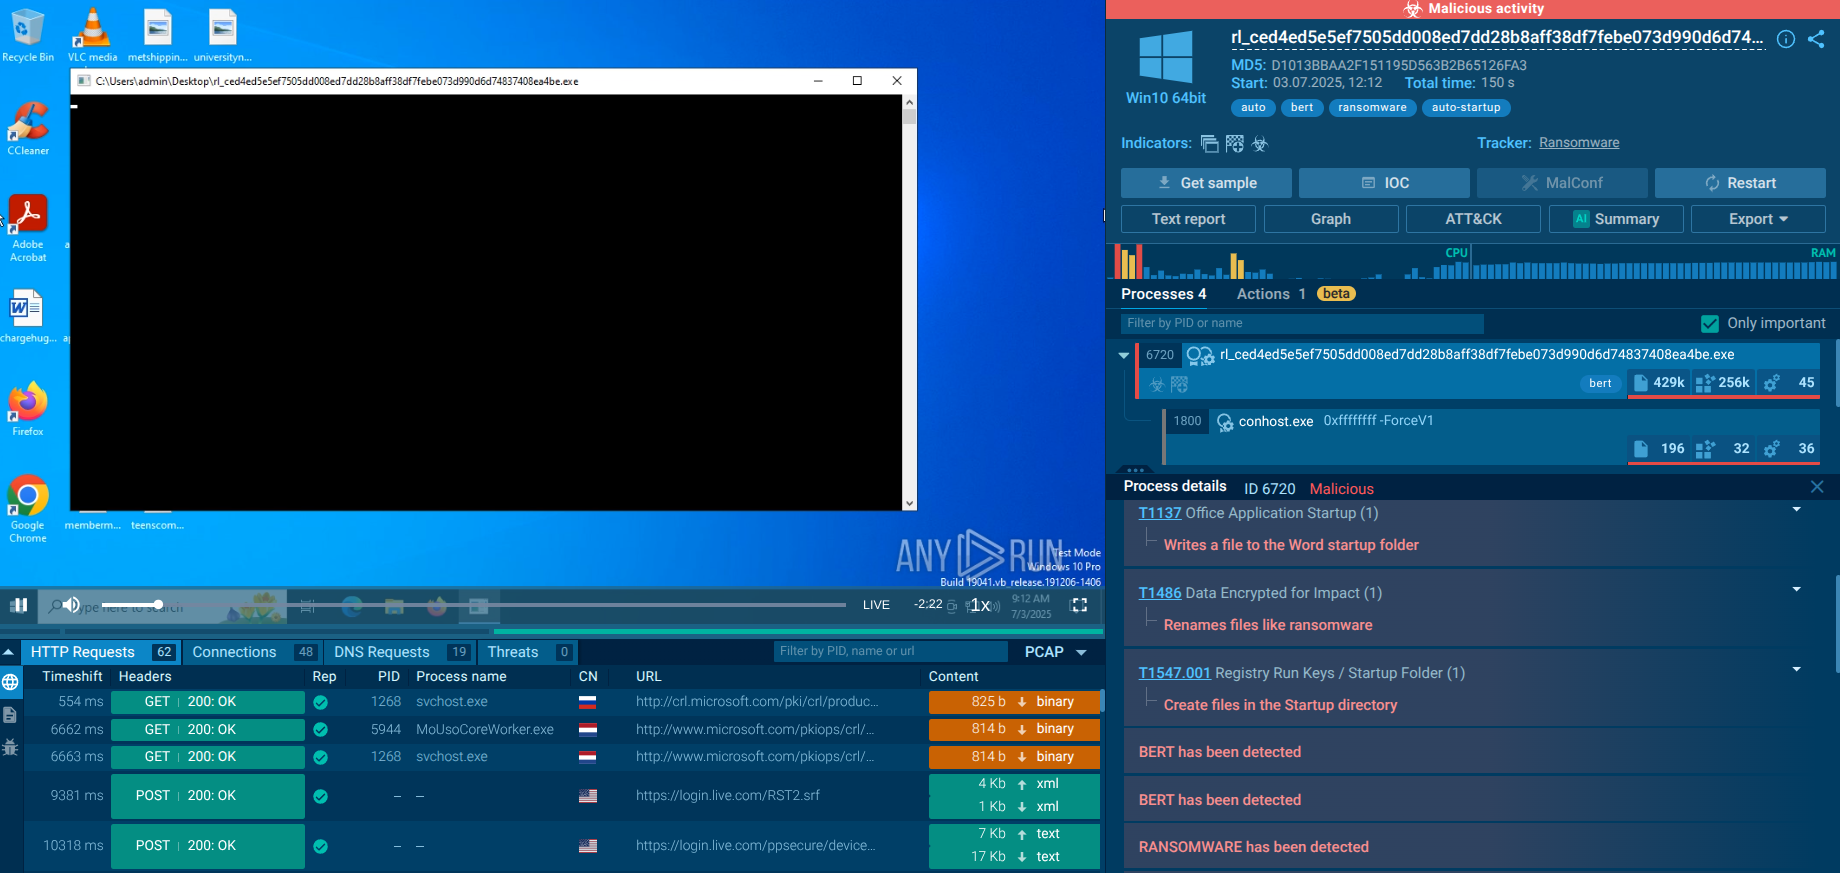 Bert RansomwareBert Ransomware is a newly emerged ransomware group that has been active since April 2025. It deploys variants targeting both Windows and Linux systems, focusing on critical sectors like healthcare, technology, and event services across the US, Asia, and Europe.
 DharmaDharma is advanced ransomware that has been observed in the wild since 2016. It is considered to be the second most profitable RaaS operation by the FBI. The malware targets hospitals and state organizations, encrypts files, and demands a payment to restore access to lost information.
 PonyPony is a malware with two main functions — stealing information and dropping other viruses with different tasks on infected machines. It has been around since 2011, and it still actively attacks users in Europe and America.
 RevengeRevenge was one of the most popular remote access trojans to be used in 2019 when it was featured in a huge malicious campaign named “Aggah”. This malware can take remote control of infected machines and spy after the victims.
 SSLoadSSLoad is a malicious loader or downloader that is used to infiltrate target systems through phishing emails, perform reconnaissance and transmit it back to its operators delivering malicious payloads. To avoid detection, SSLoad employs various encryption methods and delivery techniques highlighting its versatile nature and complexity. It is believed to be a part of Malware-as-a-Service (MaaS) operation given its diverse delivery methods and implemented techniques.