OnyxC2
- 133
- Global rank
- 83
- Month rank
- 93
- Week rank
OnyxC2 is a sophisticated Malware-as-a-Service platform sold on cybercrime forums that provides a turnkey solution for high-volume credential theft. The malware targets over 200 applications, scraping sensitive data from browsers, cryptocurrency wallets, and business-critical tools like FTP and email clients. It employs advanced evasion techniques, such as DLL sideloading and browser fingerprinting, to deliver encrypted payloads through legitimate signed binaries.
- Stealer
- Type
- Unknown
- Origin
- 1 April, 2026
- First seen
- 20 October, 2026
- Last seen
How to analyze OnyxC2 with ANY.RUN
IOCs
IP addresses
- 23.222.81.129
- 23.11.40.157
- 57.153.246.3
- 48.192.1.64
- 150.171.109.105
- 135.233.95.144
- 172.211.123.250
- 2.16.204.134
- 23.59.18.102
- 131.253.33.203
- 2.16.204.138
- 20.190.159.71
- 135.232.92.97
- 198.251.89.237
- 104.18.21.213
- 23.207.210.139
- 172.211.123.248
- 150.171.109.99
- 40.126.31.3
- 150.171.28.11
Hashes
- 3715d1887922bdfaa3b0bbca44bb748417f4c6ed7ae1684bf6a8a1a60398bef6
- 12fd0590708bb38d8039bc994178acee8a3d220f0cd194b0f1c2fc9ba622f927
- 251ed08cc8f5873098ea5ee083034e7cd99ece955920e12a42e50306a94cb6eb
- a4e5b9e377a10dcf8f4a8be4ab389a947396f0232a4bf36b69473871b5488dce
- 923242a721d68e22efa323941768297a9f74ab9be16985378d721023163abef7
- e478de33724ef288215d8f238e52846b5da173574b48825dcdc2ac2627e44535
- 564eb27a495aa92808ac8a47c71f245789c2a480bf0926bc7464eb3f350c23e2
- f694d0633bf5fe8bfaf604fbda4ecb5d64b699e0339bd02d436ef946aa1c2f82
- 96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
- f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
- ac05470242cceb8491ea40eeca387c56926d288e5304939b0d246dac9b9fea84
- 3dd5ea8a14eb665ba6057d424f94e5e83757ffaab456578dbf038af04053b19e
- 6747056bb271d34007c7be35c2fc2a5daa5e4900e6031b9e84ff3e11d4cf4e0d
- faa31eebcb4c0c122b45cf05ad5a0c24ef241117e7e15c37390bc0eaefd706a8
- 7f660b1ef68645d653697daa81f988912095b65b8b6f47ec7188c54afd936002
- 4580077c2259cfaa15072d6f50689d3d382d21557497498965e9cd66ef9becdf
- 67b3f1d7cce728f8c69361100aa9c03711e81be682c3ba51eff0f550e2ce069e
- d5555e9da9c4c597f516451c69dbfff5578e6ec782aa91c6f7ee76d241be5880
- d9e8dd08910e67381ef0d32ea4b644bdc13ccba5240c99be37129250b04fa9ed
- 138167d8f03d48e88da0aec3df38f723bc1895822f75660cccb5e994814bee90
Domains
- www.bing.com
- ye2.c.lencr.org
- login.live.com
- flyfileclouddd.click
- oneocsp.microsoft.com
- ecs.office.com
- www.microsoft.com
- activation-v2.sls.microsoft.com
- fe3cr.delivery.mp.microsoft.com
- ocsp.digicert.com
- google.com
- x1.c.lencr.org
- settings-win.data.microsoft.com
- x2.c.lencr.org
- slscr.update.microsoft.com
- nexusrules.officeapps.live.com
- crl.microsoft.com
- ye.c.lencr.org
- self.events.data.microsoft.com
- api.edgeoffer.microsoft.com
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
- https://flyfileclouddd.click/nqsperph/backend/api/app.php?action=sync&hwid=1fb83ad2fdd479f062154b3aec794d5f&tag=fff-0911&username=admin&osversion=windows+10+%28build+19045%29&privileges=user&antivirusname=windows+defender&cpuname=amd+ryzen+5+3500+6-core+processor&gpuname=nvidia+geforce+gt+730&botversion=3.0&ownertoken=f8bb9e8d19c8d2288565c931c29e6a76090d6f0024520e38b24fd200db629f81
- http://x1.c.lencr.org/
- http://x2.c.lencr.org/
- http://ye.c.lencr.org/
- http://ye2.c.lencr.org/12.crl
- https://flyfileclouddd.click/nqsperph/backend/api/app.php?action=poll&hwid=1fb83ad2fdd479f062154b3aec794d5f&topwindowname=program+manager&userpcstatus=active&botversion=3.0
- https://login.live.com/ppsecure/deviceaddcredential.srf
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:jv-gjdmitpjwlto96yqxym28r_amb2aup3hkdwp2bok&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
Last seen at
Key Takeaways
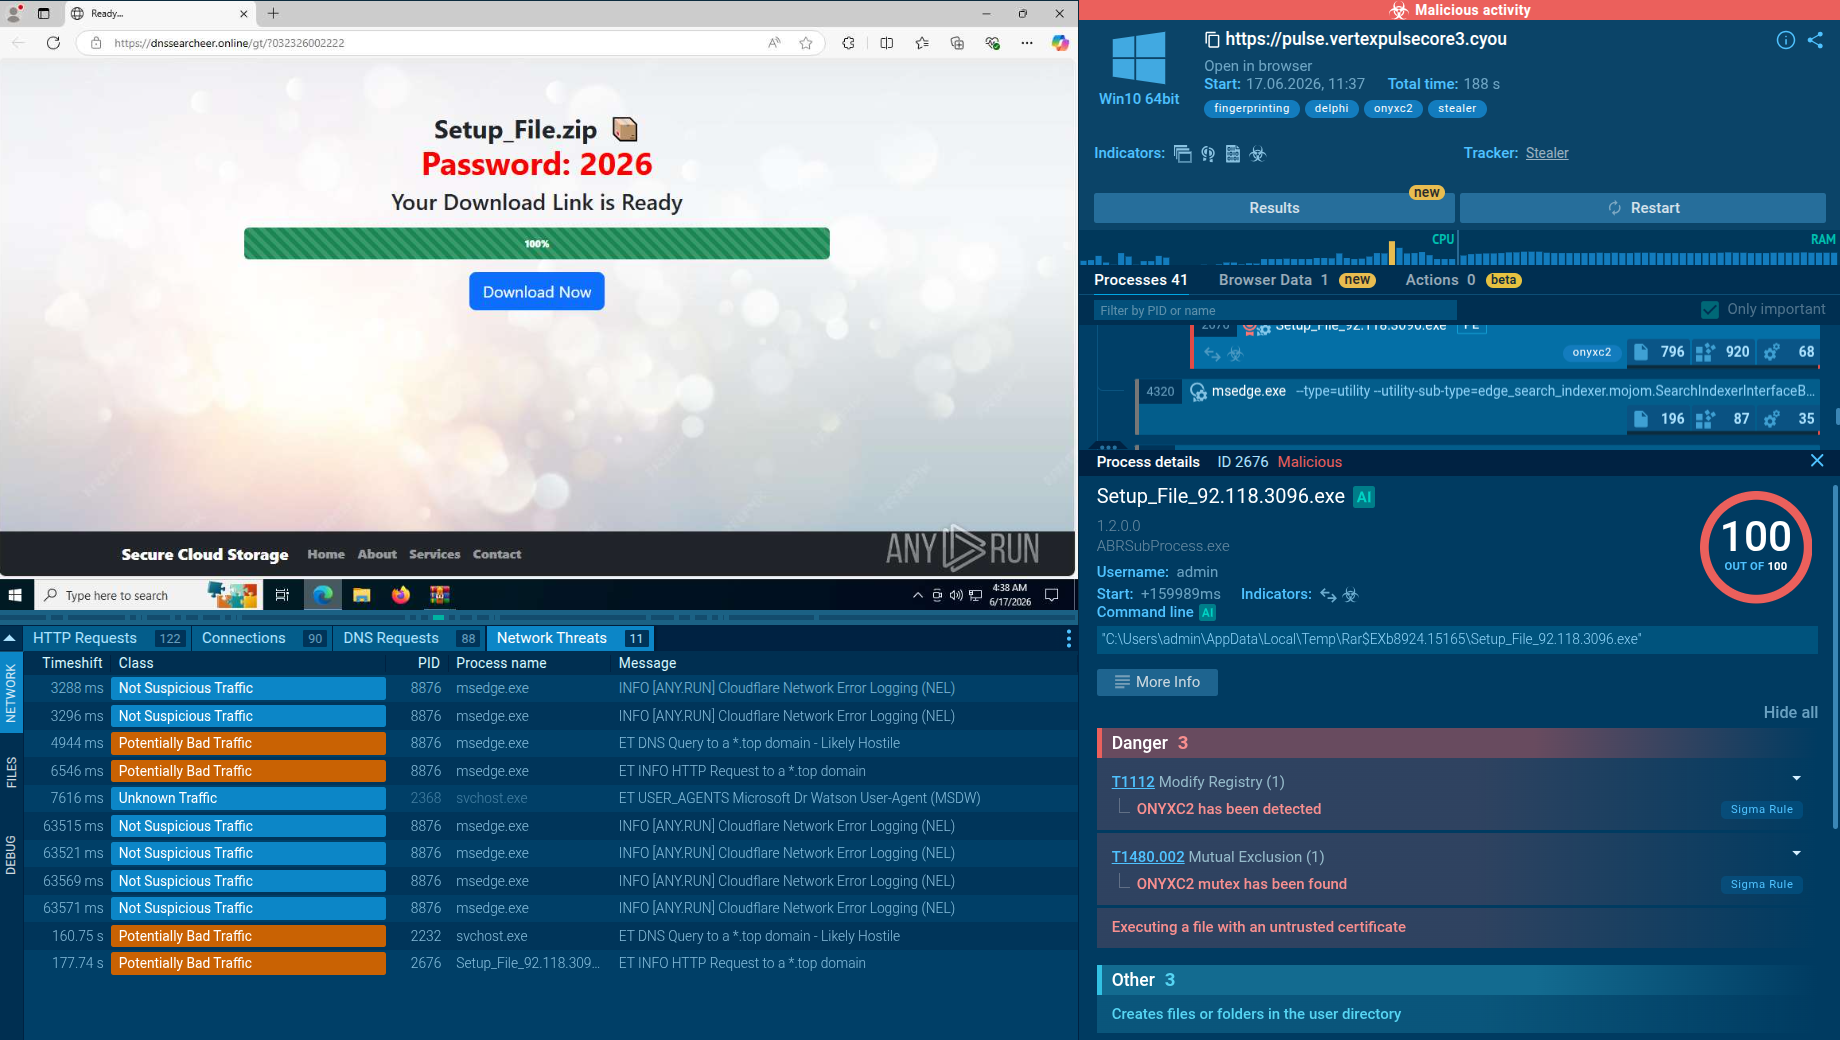
- Advanced Evasion via DLL Sideloading: Similar to other malware like ValleyRAT and XRed OnyxC2 utilizes legitimate applications with valid Authenticode signatures to load malicious payloads disguised as system libraries (e.g., masked as an NVIDIA graphics library). ANY.RUN analysts observed the use of signed binaries like
ABRSubProcess.exeto sideload a maliciousborlndmm.dll, allowing the threat to bypass traditional antivirus engines.
- Massive Application Targeting: The stealer is engineered to scrape data from over 200 applications, including Chromium-based browsers, crypto wallets, and password managers. By specifically targeting 2FA extensions and session cookies, it allows attackers to bypass multi-factor authentication and maintain access that survives password resets.
- Modular Remote Access Capabilities: Beyond credential theft, the "premium" tier of OnyxC2 includes a high-risk remote access toolkit featuring HVNC (Hidden Virtual Network Computing), LSASS memory dumping, and reverse shells. This allows operators to inherit authenticated browser sessions and maintain total control over the victim's environment.
- Strategic Vetting and Delivery: Phishing pages for OnyxC2 employ "Canvas fingerprinting" to profile the victim’s environment before providing the payload. To evade email security gateways, the malware is frequently delivered in password-protected ZIP archives (e.g.,
Setup_File.zip), preventing automated scanners from inspecting the malicious content. - Industrialized MaaS Model: Sold as a subscription, OnyxC2 democratizes sophisticated cybercrime by providing low-skilled affiliates with ready-made lures, a centralized management panel, and a "service guarantee" against detection.
What is OnyxC2?
OnyxC2 is a sophisticated Malware-as-a-Service (MaaS) info-stealer and remote access toolkit that first appeared on cybercrime forums in early 2026. It is designed to be a comprehensive, turnkey solution for threat actors, enabling even those with limited technical skills to launch high-volume credential theft and account takeover campaigns. The malware is particularly dangerous because it does not just harvest passwords; it is specifically engineered to collect session material, cookies, and 2FA backup data that allow attackers to bypass multi-factor authentication and maintain access even after a victim resets their password.
OnyxC2 is highly versatile, with a target list that covers over 200 applications. It targets dozens of Chromium-based and Gecko-based browsers to scrape saved logins and cookies. It specifically hunts for browser-based password managers and two-factor authentication (2FA) extensions, which are critical for bypassing modern security layers. The stealer scrapes data from numerous cryptocurrency wallets, FTP clients, and email clients, pushing the threat beyond consumer-level theft and into the business systems used by finance and operations teams. Beyond credentials, it harvests credit card information, autofill entries, and session tokens.
The malware is delivered via a legitimate application carrying a valid Authenticode signature, which often results in zero detections on platforms like VirusTotal. This signed binary loads a malicious DLL disguised as a legitimate system component, such as an NVIDIA graphics library. The malicious payload remains encrypted until runtime, meaning there is no detectable malicious code on the disk before the execution begins. Payloads are frequently delivered in password-protected ZIP archives to bypass email security gateways that cannot inspect encrypted content.
For a higher subscription price, OnyxC2 evolves from a simple stealer into a modular remote access platform. This "premium" toolkit includes:
- HVNC (Hidden Virtual Network Computing): This allows the operator to inherit the victim's authenticated browser sessions outright, performing actions in the background without the user's knowledge.
- LSASS Memory Dumping: A technique used to extract additional credentials directly from the system memory.
- Operational Control: The toolkit provides a file manager, keylogger, screenshot capture, reverse SOCKS5 proxy, and a reverse shell over HTTP for total system command.
OnyxC2 is managed as a professional commercial product, sold through a tiered subscription model on the dark web. The developers provide a centralized administrative dashboard where affiliates can manage "bots," view logs, and use a builder to generate new malware instances.
How OnyxC2 Threatens Businesses and Organizations
For modern enterprises, OnyxC2 represents a shift from simple credential harvesting toward complete infrastructure takeover and long-term persistence. By industrializing the theft of session material, this platform creates several critical risks:
- Bypassing Multi-Factor Authentication (MFA): Unlike traditional stealers that only capture passwords, OnyxC2 is specifically engineered to scrape session cookies and 2FA backup material. This allows attackers to bypass MFA challenges entirely, as the stolen session tokens confirm to the server that the user has already authenticated.
- Persistent Foothold: OnyxC2 is designed to maintain access across sessions, ensuring that a single compromise yields continuous visibility into the workstation's activities. One successful infection allows threat actors to monitor browsers, password managers, and email sessions in real-time as the victim continues to work.
- Business System Exposure: The malware targets popular enterprise applications, moving beyond consumer data to focus on business-critical systems like FTP clients, VPN credentials, and email accounts. This places the core systems used by finance and operations teams at immediate risk of compromise.
Victimology: Who Is Most Vulnerable?
The targeting profile of OnyxC2 is broad and opportunistic, designed to exploit the ubiquitous nature of modern web-based work and financial applications:
- Cryptocurrency and Financial Sectors: The toolkit is heavily optimized for financial theft, targeting different cryptocurrency wallets and numerous password manager extensions.
- Small and Medium Businesses (SMBs): Phishing lures often masquerade as business software such as "FinePrint" or "SystemSettings," specifically designed to trick office workers and operations teams into running the payload.
- Global Reach: While the malware appears on global cybercrime forums, its targets are universal; any user with a targeted application installed—ranging from messaging apps and VPNs to note-taking and remote access tools—is a potential victim.
- Users Bypassing Security Protocols: Organizations that do not use interactive sandboxing to analyze incoming files are particularly vulnerable, as the malware’s DLL sideloading technique often results in zero detections by traditional antivirus engines.
How Does OnyxC2 Malware Function? (The Sandbox Analysis)
Detonating an OnyxC2 sample in the ANY.RUN Interactive Sandbox provides a transparent, step-by-step look at how this Malware-as-a-Service operation bypasses traditional security perimeters. By moving beyond static signatures, defenders can observe the following stages of the attack in real-time:
Stage 1: The Initial Lure and Strategic Redirects
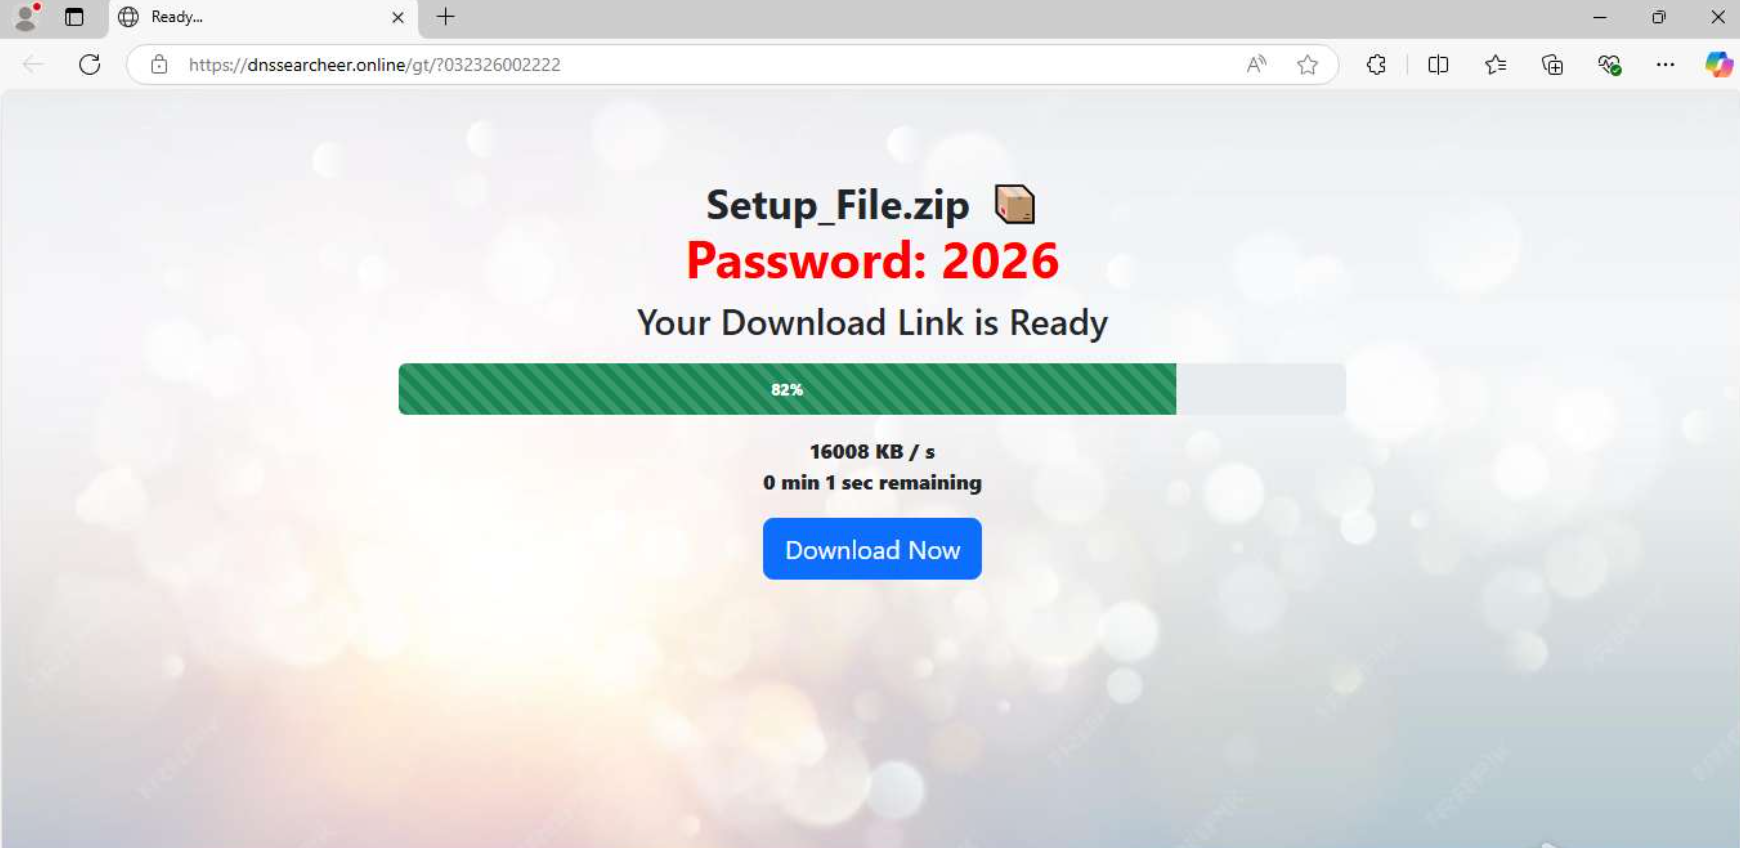
The infection chain often begins with a victim visiting a phishing URL disguised as a legitimate software download page In the sandbox environment, analysts can observe a series of sequential HTTP redirects through multiple intermediary pages designed to obfuscate the final destination of the malware.
Stage 2: Browser Profiling and Vetting
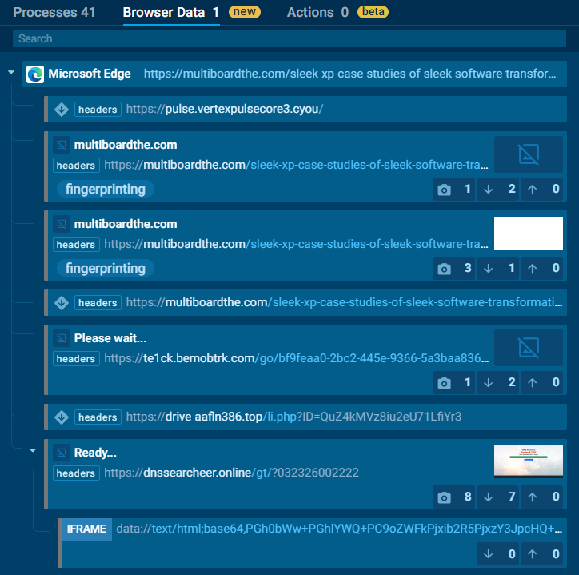
A critical evasion tactic occurs during the redirection phase: the presence of "Canvas fingerprinting". The phishing page actively collects characteristics of the victim's browser and execution environment to verify it is a real user rather than an automated security scanner before delivering the malicious payload.
Stage 3: Protected Archive Delivery
To bypass email security gateways and automated antivirus analysis, OnyxC2 is frequently delivered as a password-protected ZIP archive (e.g., Setup_File.zip with the password 2026). Because most security tools cannot inspect the encrypted contents of the archive, the malicious files are delivered to the user without prior detection.
Stage 4: Execution through DLL Sideloading
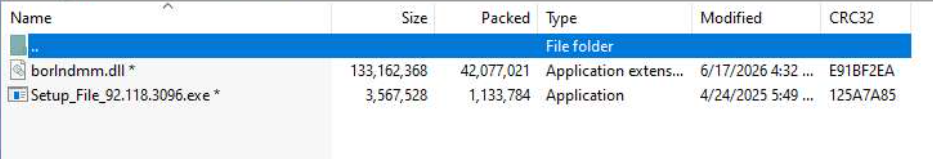
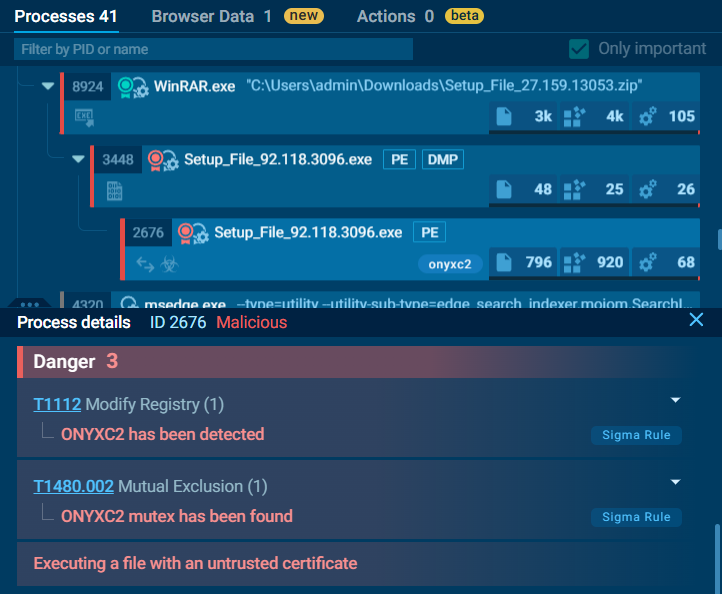
Upon extraction, the archive reveals a legitimate-looking executable (e.g., Setup_File_92.118.3096.exe) and a malicious DLL (borlndmm.dll). The executable often carries valid metadata, such as being described as ABRSubProcess.exe from ACCA software S.p.A., to build trust with the victim. When launched, the signed binary utilizes DLL sideloading to silently load the malicious library into memory.
Stage 5: Payload Deployment and Process Branching
Once the initial execution is successful, the process tree reveals that the malware creates a child instance of itself. This behavior is indicative of the malware unpacking its core payload into the new process, effectively transitioning from the loader stage to the active stealer logic.
Stage 6: Data Harvesting and Remote Access
With the payload fully deployed, OnyxC2 initiates its primary functions: harvesting credentials, session cookies, and financial data from over 200 targeted applications. If the "premium" build is utilized, the malware also activates advanced remote access features, such as HVNC over a web browser and LSASS memory dumping, granting the operator total control over the compromised workstation.
How Businesses Can Use ANY.RUN’s Threat Intelligence Against OnyxC2
Because OnyxC2 operates as a Malware-as-a-Service (MaaS) with infrastructure that rotates rapidly, traditional static blocklists are often insufficient for long-term protection. Security teams must shift from tracking temporary indicators to identifying the durable technical fingerprints and behavioral patterns of the operation. By leveraging ANY.RUN’s Threat Intelligence, organizations can stay ahead of these evolving campaigns.
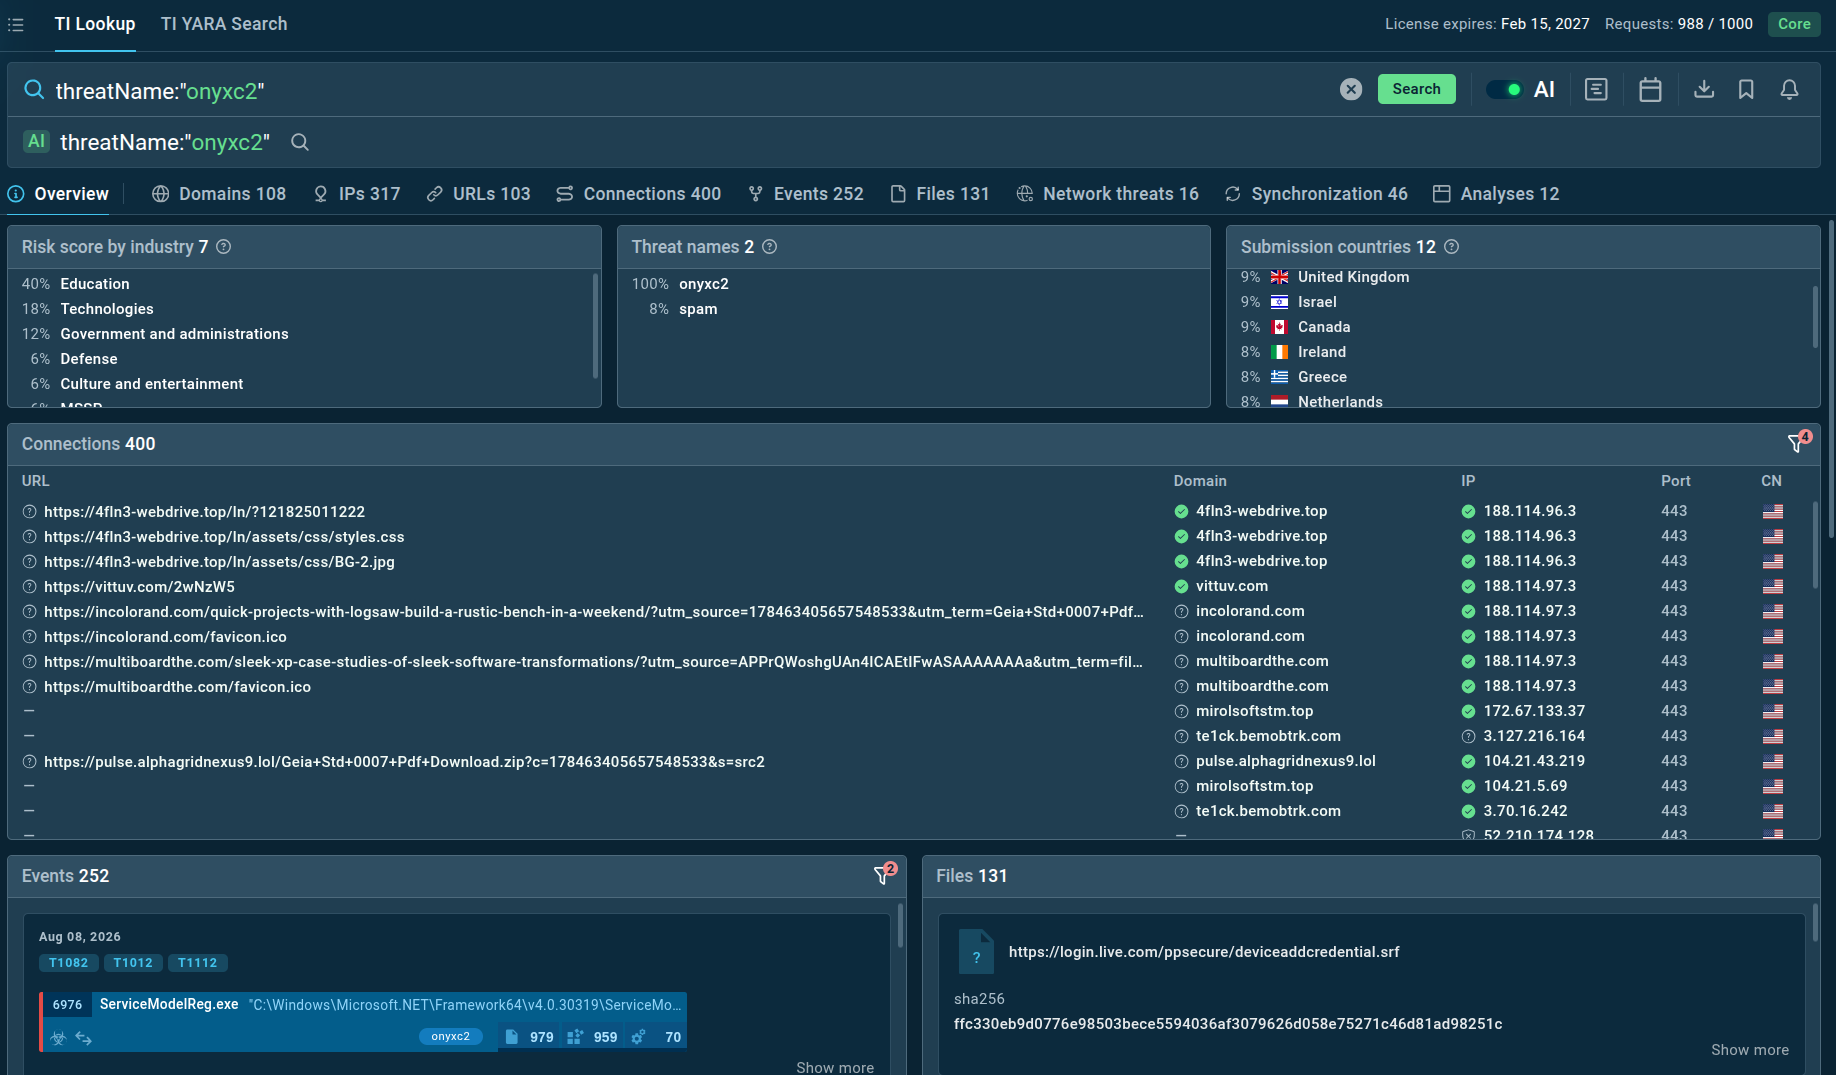
Threat Intelligence Lookup allows analysts to pivot from a single suspicious artifact to an entire cluster of related malicious activity by searching for the "technical DNA" of the malware.
The following TI Lookup query reveals that the malware is linked to attacks on organizations in tech, government, and education from countries like Canada, Israel and the UK.
OnyxC2 consistently uses DLL sideloading, where a legitimate, signed binary (such as ABRSubProcess.exe by ACCA software S.p.A.) is used to load a malicious DLL (like borlndmm.dll). Security teams can use TI Lookup to search for these specific file name combinations or the Authenticode signatures of the legitimate hosts used in the attack chain.
Even when domains change, the underlying assets of the phishing pages, such as the specific scripts used for Canvas fingerprinting to vet victims, remain stable. Analysts can search for these behavioral signatures to identify new phishing URLs before they are widely reported.
For organizations that require automated, high-speed protection, ANY.RUN’s Threat Intelligence Feeds provide a real-time stream of validated indicators. The feeds deliver a continuous flow of the latest C2 domains, IP addresses, and malicious URLs directly into SIEM, SOAR, and EDR platforms. The intel is extracted from the latest malware & phishing investigations of ANY.RUN’s global community of 15K organizations and 600K analysts.
By integrating these feeds, teams can automatically block emerging malicious infrastructure, such as the newly created phishing pages used to harvest credentials. Since OnyxC2 often deploys secondary tools like HVNC or reverse shells, the feeds provide critical network indicators for these remote management protocols, allowing teams to detect active breaches before data exfiltration occurs.
Conclusion
OnyxC2 represents the industrialization of modern cybercrime, providing low-skilled threat actors with a sophisticated platform for large-scale credential theft and account takeover. Its primary danger lies in its move beyond simple password harvesting; by targeting the session cookies and 2FA material that survive a password reset, it grants attackers "standing visibility" into a victim's entire digital working life.
To combat this threat, organizations must move beyond static blocklists and reactive defenses. Because OnyxC2 is sold as a Service (MaaS) with rapidly rotating infrastructure, successful mitigation depends on identifying the durable technical fingerprints. Implementing interactive sandboxing and proactive threat intelligence is essential to deobfuscate encrypted payloads and identify the modular remote access features, such as HVNC, that allow operators to inherit authenticated user sessions outright.
Frequently Asked Questions: OnyxC2
1. What is OnyxC2?
OnyxC2 is a sophisticated Malware-as-a-Service (MaaS) stealer and remote access toolkit that targets browsers, crypto wallets, and business-critical tools like FTP clients. It is sold on a subscription basis, allowing affiliates to deploy high-volume campaigns for a monthly fee.
2. How does OnyxC2 bypass traditional antivirus software?
The malware utilizes DLL sideloading, where a legitimate, signed executable is used to load a malicious DLL disguised as a system library. Because the primary executable carries a valid Authenticode signature, it often results in zero detections by automated security scanners.
3. Why is the "premium" version of OnyxC2 particularly dangerous for businesses?
The premium tier includes a modular remote access toolkit featuring HVNC (Hidden Virtual Network Computing) and LSASS memory dumping. These features allow an attacker to inherit a victim's authenticated browser session and perform actions in the background without the user's knowledge, bypassing MFA entirely.
4. How can organizations mitigate this threat?
Companies must integrate interactive sandboxing and proactive threat intelligence to expose the modular logic that evades traditional scanners. By using tools like TI Lookup and TI Feeds, security teams can identify stable build-chain fingerprints and block rotating infrastructure in real-time.
5. What types of applications does OnyxC2 target?
The stealer scrapes data from Chromium-based and Gecko-based browsers, as well as 2FA extensions and password managers. It specifically targets business systems like email and VPN clients to move beyond consumer theft and into corporate infrastructure.
Other malware & phishing threats
 GootkitGootkit is an advanced banking trojan. It is extremely good at evading detection and has an incredibly effective persistence mechanism, making it a dangerous malware that researchers and organizations should be aware of.
 LummaLumma is an information stealer, developed using the C programming language. It is offered for sale as a malware-as-a-service, with several plans available. It usually targets cryptocurrency wallets, login credentials, and other sensitive information on a compromised system. The malicious software regularly gets updates that improve and expand its functionality, making it a serious stealer threat.
 AdwareAdware is a form of malware that targets users with unwanted advertisements, often disrupting their browsing experience. It typically infiltrates systems through software bundling, malicious websites, or deceptive downloads. Once installed, it may track user activity, collect sensitive data, and display intrusive ads, including pop-ups or banners. Some advanced adware variants can bypass security measures and establish persistence on devices, making removal challenging. Additionally, adware can create vulnerabilities that other malware can exploit, posing a significant risk to user privacy and system security.
 HawkeyeHawkeye often gets installed in a bundle with other malware. This is a Trojan and keylogger that is used to retrieve private information such as passwords and login credentials. This is an advanced malware that features strong anti-evasion functions.
 Kali365Kali365 is an emerging Phishing-as-a-Service (PhaaS) platform that targets Microsoft 365 environments by stealing OAuth authentication tokens instead of passwords. First observed in April 2026, the service enables even low-skilled threat actors to bypass multi-factor authentication (MFA), gain persistent access to corporate cloud accounts, and compromise business communications, files, and collaboration platforms. Kali365 represents a shift from traditional credential theft toward session hijacking and token abuse, making it a significant threat to organizations that rely on Microsoft 365.
 LynxLynx is a double extortion ransomware: attackers encrypt important and sensitive data and demand a ransom for decryption simultaneously threatening to publish or sell the data. Active since mid-2024. Among techniques are terminating processes and services, privilege escalation, deleting shadow copies. Distribution by phishing, malvertising, exploiting vulnerabilities.