PXA Stealer
- 158
- Global rank
- 195
- Month rank
- 193
- Week rank
PXA Stealer is an information-stealing malware that targets individuals and organizations in 60+ countries. It spreads via phishing, archives, and fake software updates. DLL sideloading, decoy documents, and obfuscation help it evade security tools. Exfiltrated data is exfiltrated and monetized through underground marketplaces.
- Stealer
- Type
- Unknown
- Origin
- 1 November, 2024
- First seen
- 13 September, 2026
- Last seen
How to analyze PXA Stealer with ANY.RUN
IOCs
IP addresses
- 155.102.51.14
- 163.181.131.226
- 92.123.104.62
- 192.178.183.132
- 150.171.27.11
- 23.52.181.141
- 172.66.171.73
- 149.154.166.110
- 204.79.197.203
- 150.171.28.12
- 212.56.41.77
- 142.251.110.139
- 48.209.138.168
- 150.171.28.11
- 23.52.181.212
- 172.67.203.222
- 162.159.142.9
- 18.244.18.27
- 150.171.109.105
- 142.251.151.119
Hashes
- bbacea81d4f7a3a7f3c036273a4534d31dbf8b6b5cca2bcc4c00cb1593cf03d8
- 6db59139627d29abd36f38ed2e0de2a6b234a7d7e681c7dbaf8b888f1cac49a5
- 44fb04b5c72b584b6283a99b34789690c627b5083c5df6e8b5b7ab2c68903c06
- 407fc0fe06d2a057e9ba0109ea9356cab38f27756d135ef3b06a85705b616f50
- aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
- bc4cbe4c99fd65abea45fbdaf28cc1d5c42119280125fbbd5c2c11892ae460b2
- 0e0732480338a229cc3ad4cdde09021a0a81902dc6edfb5f12203e2aff44668f
- 2981965bd23a93a09eb5b4a334acb15d00645d645c596a5ecadb88bfa0b6a908
- cead5eb2b0b44ef4003fbcb2e49ca0503992ba1d6540d11acbbb84fdbbd6e79a
- 42ef317ea851a781b041dc1951ea5a3ea1e924149c4b868ecd75f24672b28fa8
- 345f3f9422981cc1591fbc1b5b17a96f2f00f0c191df23582328d44158041cf0
- 2a6856298ec629a16bdd924711dfe3f3b1e3a882ddf04b7310785d83ec0d566c
- ebe5a2b4cbbcd7fd3f7a6f76d68d7856301db01b350c040942a7b806a46e0014
- bf984ec7cf619e700fe7e00381ff58abe9bd2f4b3dd622eb2edaccc5e6681050
- f65c0f8532387afe703facdee325bf8d7f3d1232dee92d65426ff917dd582cb3
- a5dc7bfb4f569361d438c8cf13a146cc2641a1a884acf905bb51da28ff29a900
- 33c6072a006ba4e9513d7b7fd3d08b1c745ca1079b6d796c36b2a5ae8e4ae02b
- 4f32e1518be3270f4db80136fac0031c385dd3ce133faa534f141cf459c6113a
- f39e4cabe33629365c2cef6037871d698b942f0672f753212d768e865480b822
- 7d3a956663c529d07c8a9610414356de717f3a2a2ce9b331b052367270acea94
Domains
- client.wns.windows.com
- ogads-pa.clients6.google.com
- safebrowsingohttpgateway.googleapis.com
- release-assets.githubusercontent.com
- qqwwaa.tos-cn-hongkong.volces.com
- www.bing.com
- update.cg100iii.com
- clientapi.aplus.pptv.com
- neihite.cc
- img-s-msn-com.akamaized.net
- drive.usercontent.google.com
- edge-mobile-static.azureedge.net
- ecs.office.com
- p.vaadv.net
- accounts.google.com
- static.edge.microsoftapp.net
- clients2.google.com
- msedge.b.tlu.dl.delivery.mp.microsoft.com
- api.msn.com
- edge.microsoft.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
- https://urlhaus.abuse.ch/downloads/text_online/
- http://users.atw.hu/zoolatogato/xruhbmzvlaghfnqcerrv.exe
- https://raw.githubusercontent.com/huuuuggga/aaaaa1/refs/heads/main/srtware.exe
- https://www.blackhattoolz.com/licensing/updates/addmefast%20bot.exe
- https://ossapp.suning.com/pcoss/dl/pptv(pplive)_forap_1084_9993.exe
- https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://139.198.15.223:8080/pinginfoview.exe
- http://haeum.nfile.net/files/haeum.exe
- http://ins.pplive.com/config/pptv/qd-all-slient-onelink-autostart/forqd1084/bind_en-us.ini
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- http://178.16.54.109/1.exe
- http://clients2.google.com/time/1/current?cup2key=8:hkp2v16p3z5vxsxlmnunxakw3bzm2k1xceu5qa42qtq&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- http://github.com/vinhuptoday/testbn/raw/refs/heads/main/brbotnet.exe
- http://62.60.226.140/files/unique2/file.exe
- http://update.cg100iii.com/cgpro/update.exe
- http://ocsp.usertrust.com/mfewtzbnmeswstajbgurdgmcgguabbsr83eyjy3njhjvpn5bepfc6mxawqquouejhttpgckwdnrjdtzgnczjy5ocebqer%2bxt6ogbxbkxqbankn0%3d
Last seen at
PXA Stealer Targeting High-Value Data
Key takeaways
- PXA Stealer is an infostealer that primarily targets credentials, browser data, and financial information.
- Its methods include DLL sideloading, multi-stage archives, phishing, and legitimate files abuse.
- Targeted industries include education and government entities.
- Some variants maintain persistence through RAT components or by running alongside legitimate programs.
- Stolen information is monetized on underground marketplaces.
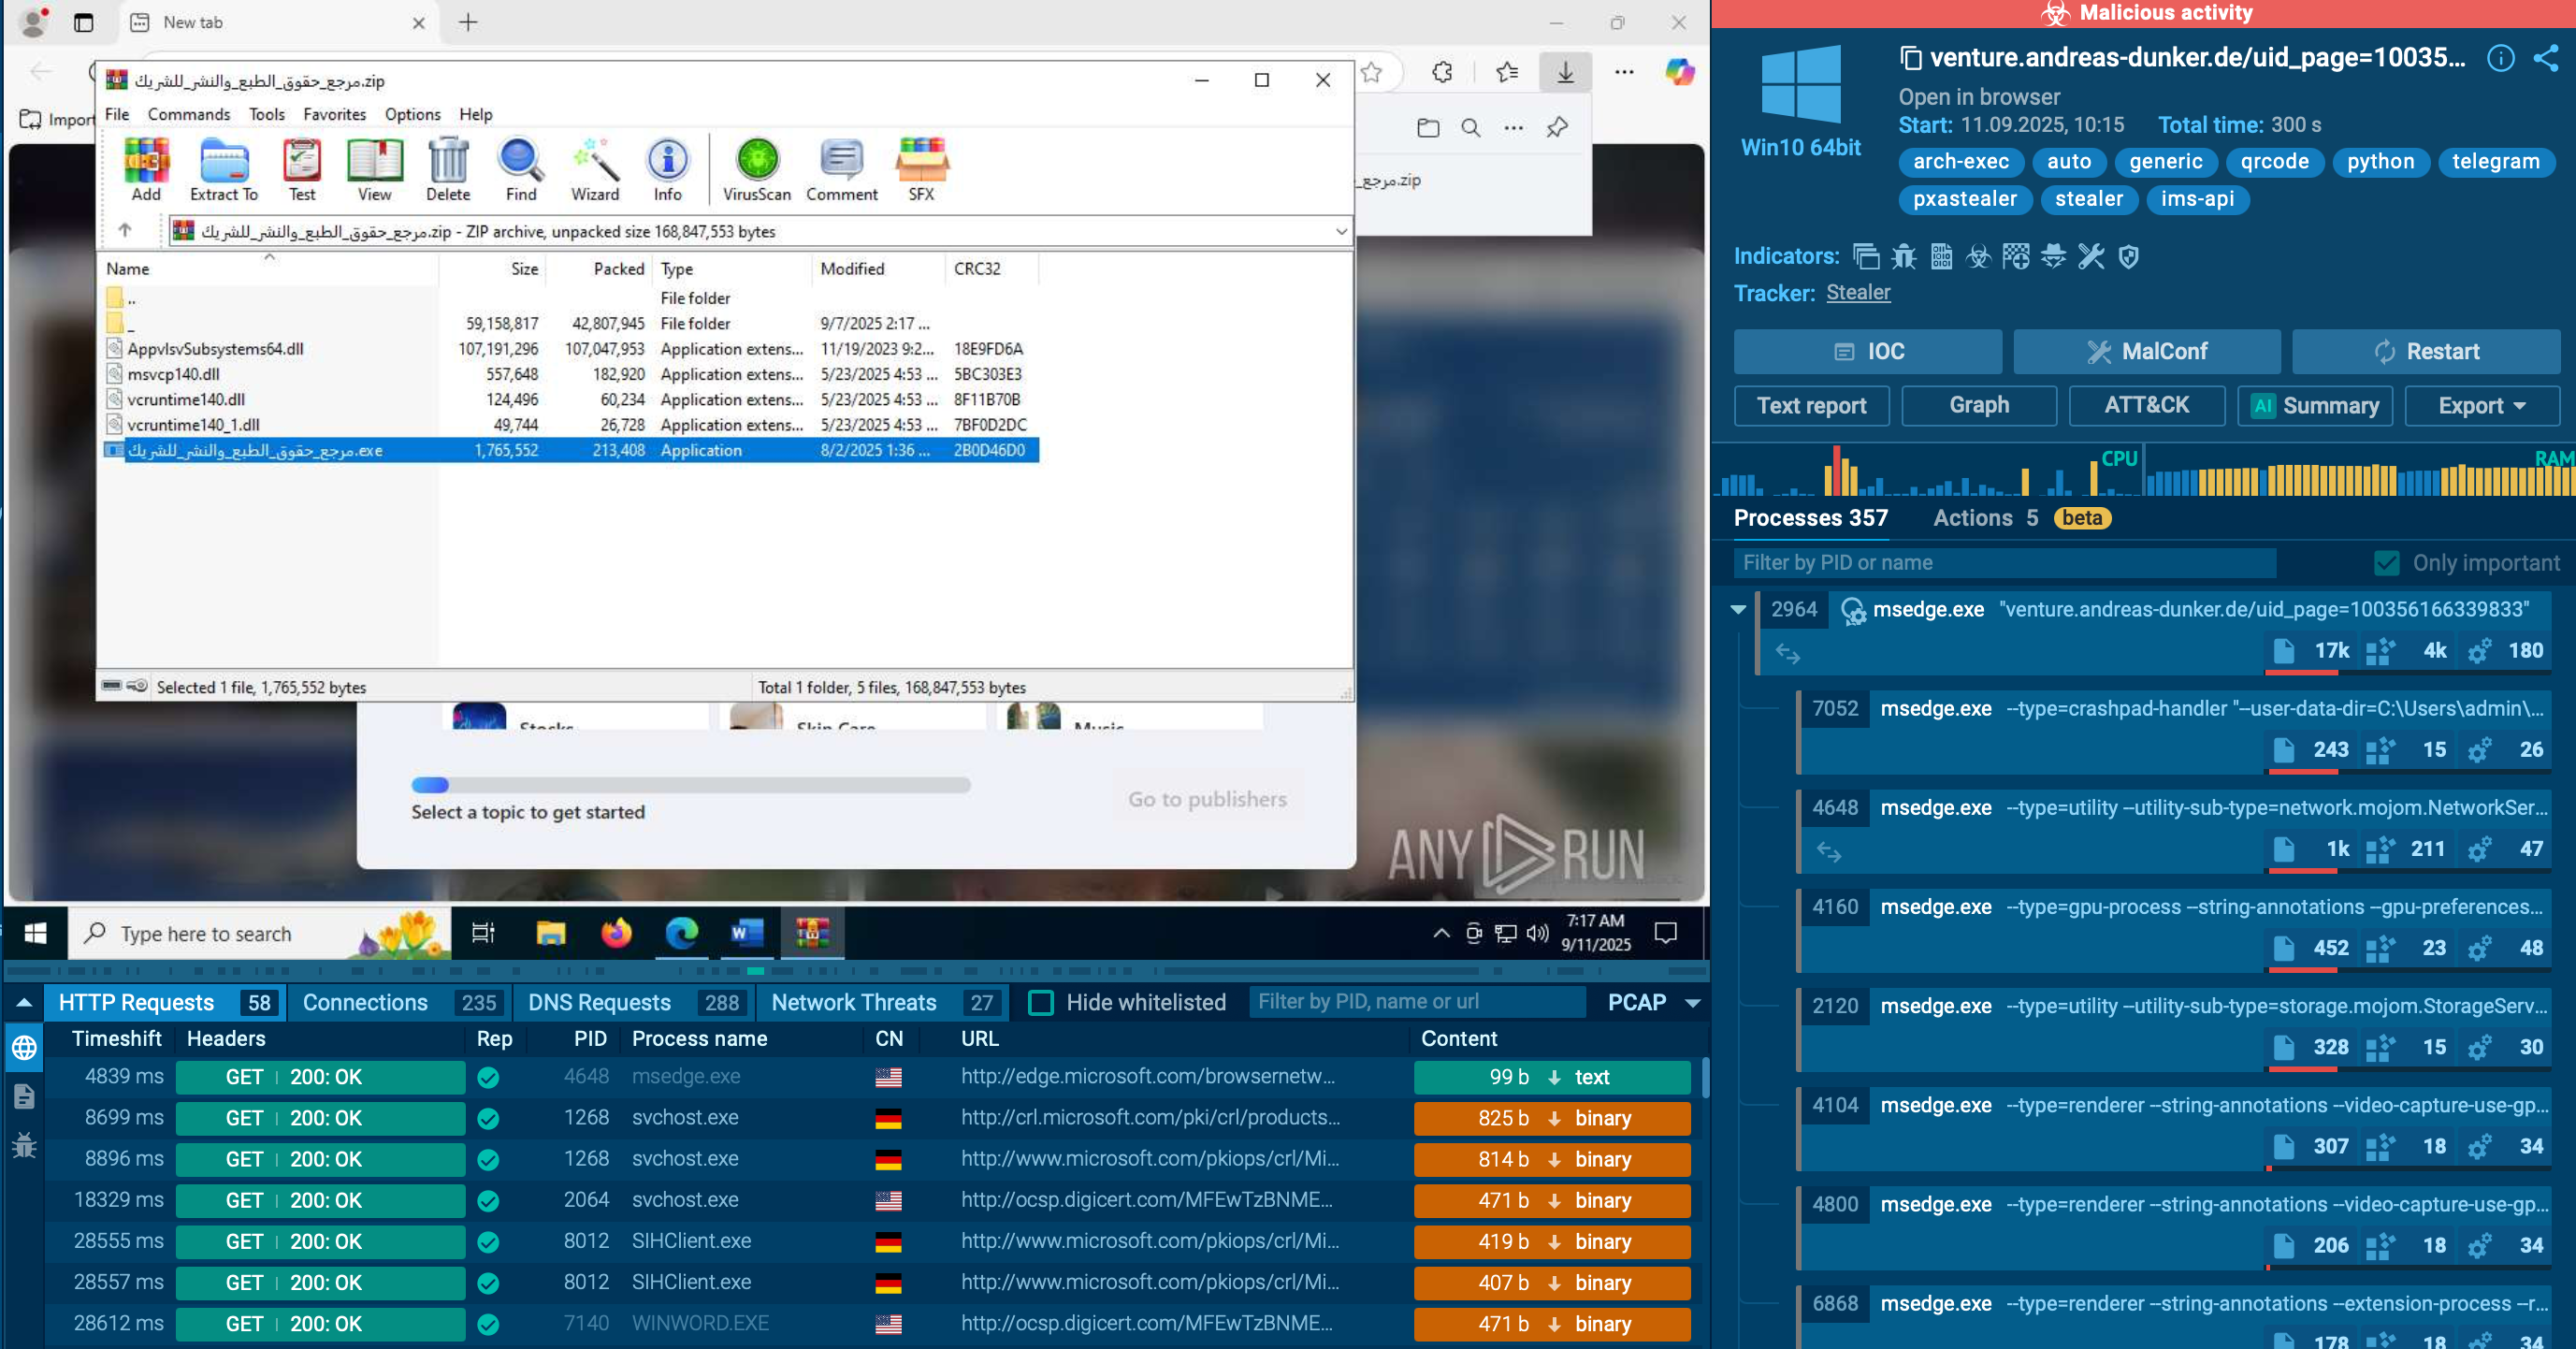
- Analysts can use ANY.RUN’s Interactive Sandbox to expose PXA Stealer. View analysis in ANY.RUN Sandbox
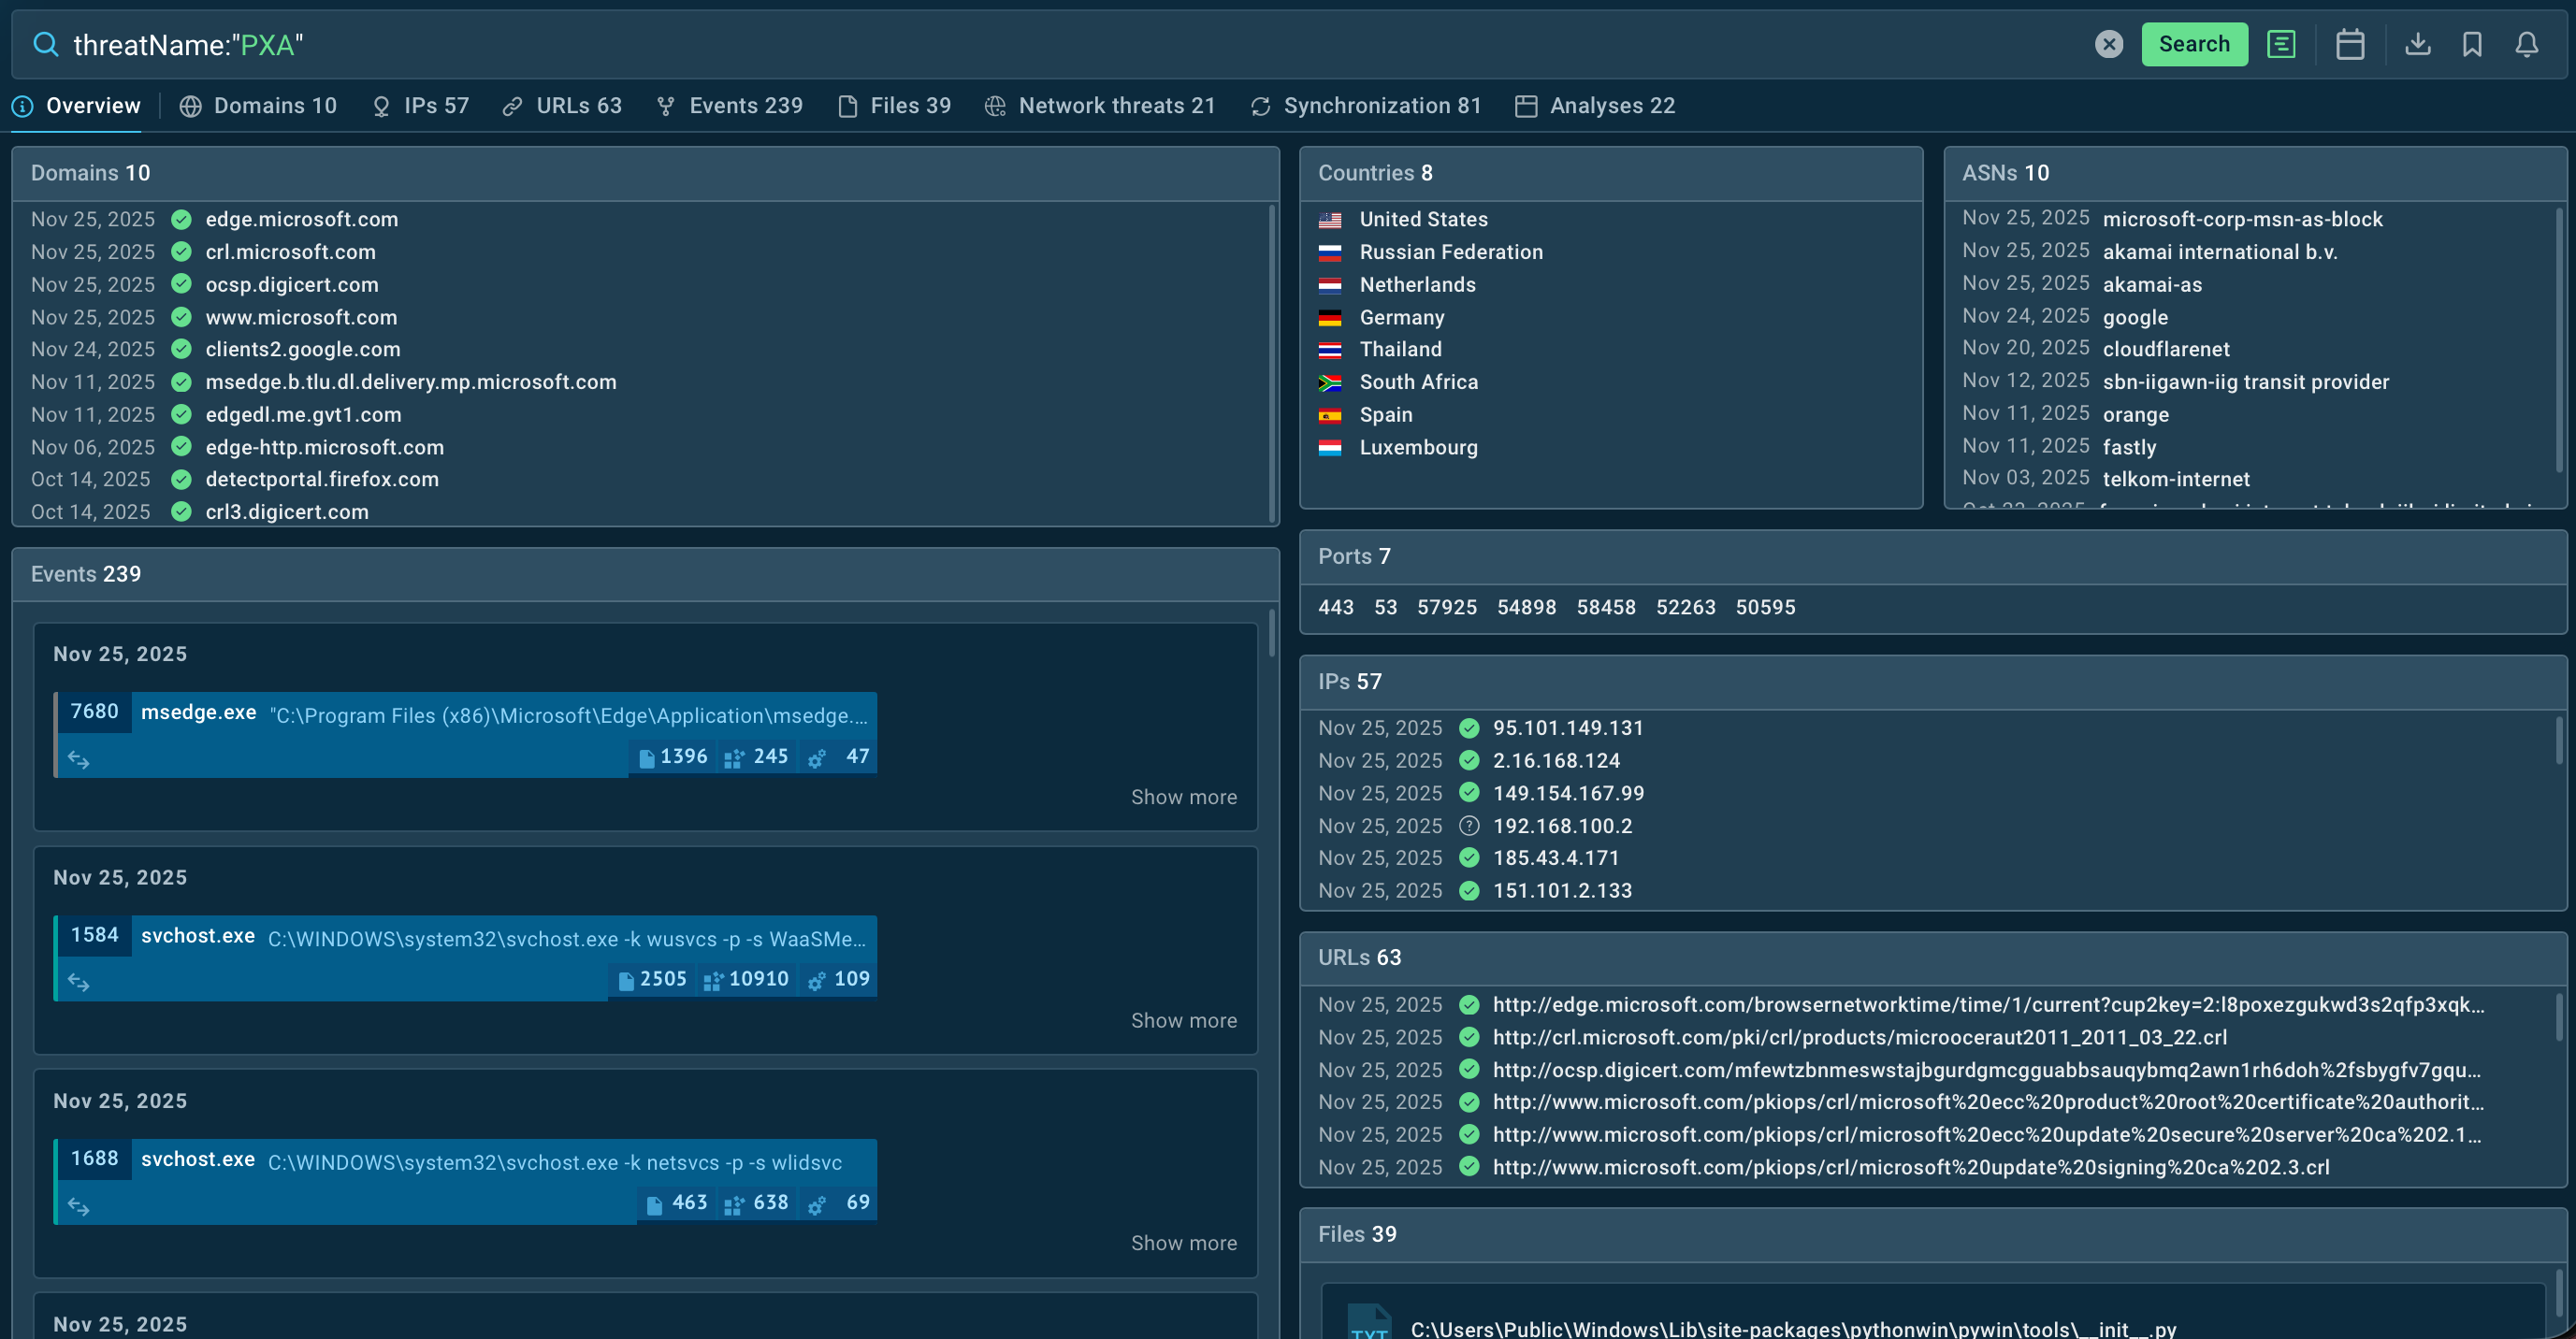
- Browse data on PXA Stealer in Threat Intelligence Lookup to identify and monitor its variants.
What is PXA Stealer malware?
PXA Stealer is designed to harvest sensitive data through malicious software updates, attachments, and phishing links.
In 2024, a large-scale campaign driven by PXA Stealer unfolded. It was deployed as the final payload successfully stealing high-value data, including credentials and financial data via automated bot networks. Over 4,000 users were impacted by this operation, with 200,000+ passwords stolen.
Threat actors behind the malware are believed to be Vietnamese-speaking cybercriminals, based on code comments and Telegram account data linked to the attack.
The initial sideloading-based distribution through legitimate executables paired with a malicious DLL further evolved to include anti-analysis measures and decoys. The general attack methods haven’t changed. Threat actors demonstrated the ability to improve the malware, refining initial access and obfuscation methods.
Stolen data is subsequently monetized through underground marketplaces.
PXA Stealer malware technical details
The primary functionality and feature of malware:
PXA Stealer spreads via DLL sideloading and multi-stage payloads in archived files (e.g., Ghost in the Zip campaign).
During 2025, threat actors continued to refine their initial access and evasion techniques. They started to use benign documents (like PDFs) and legitimate software as decoy for more convincing DLL execution. Such elaborate, layered attacks are harder to detect both by endpoint security tools and analysts.
PXA variants are generally not persistence-oriented. Their primary goal is to steal data in one go and exit. However, in several campaigns additional persistence was achieved by extra tools like RAT components. Persistence was also maintained as the malware stayed active alongside the legitimate program that carried the malicious DLL.
Anti-analysis methods include the abuse of legitimate files and software to distract users and analysts. Layered and nested archives, the mixing of benign and malicious objects – all this contributes to the delay of detection.
As for PXA variants that come with RATs, these often include deeper obfuscations, such as multi-layer encoding and fragmented execution stages, making the reconstruction of execution flow even more complex.
For exfiltration of stolen data, PXA uses legitimate cloud messaging platforms, most often Telegram API and controlled C2 infrastructure.
PXA Stealer victimology
A number victims of PXA Stealer are private individuals, but a large proportion are organizations, particularly educational and government organizations from Asian (e.g., South Korea) and European (e.g. Sweden, Denmark, the Netherlands) countries, as well as the US. The total range of victim’s geography includes over 60 countries.
PXA Stealer execution process
See how PXA Stealer attack unfolds in a VM: View analysis in ANY.RUN Sandbox
The attack starts with the delivery of a large archive that contains an .exe file with a malicious DLL library.
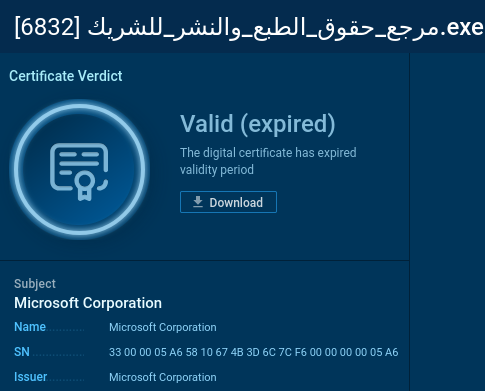
Upon the execution, the DLL activates and creates a script, which begins to unfold the payload. In particular, the .CMD script uses Windows’ certutil utility to decode and extract an encrypted .RAR archive embedded into a corrupted PDF file.
The next step: certutil extracts base64-coded content from the PDF and transforms it into a new archive file – Invoice.pdf (RAR-archived).
After that, WinRar’s package utility masquerading as images.png file extracts the archive using predefined parameters and password.
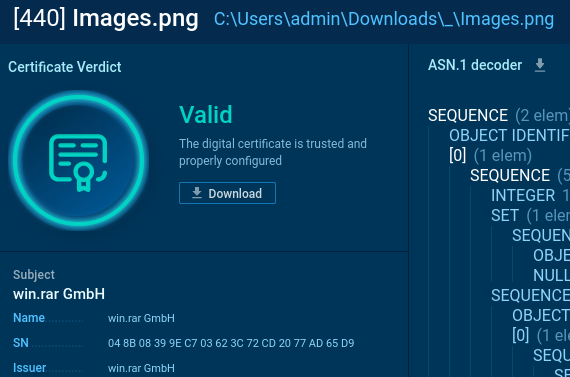
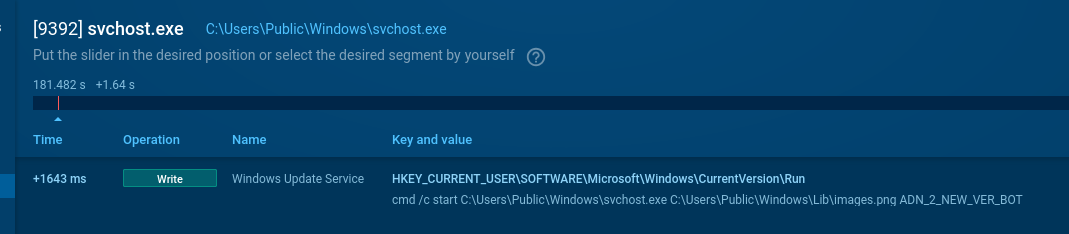
Now several dependencies for Python environment are unpacked, including a renamed legitimate Python 3.10 interpreter under the disguise of svchost.exe.
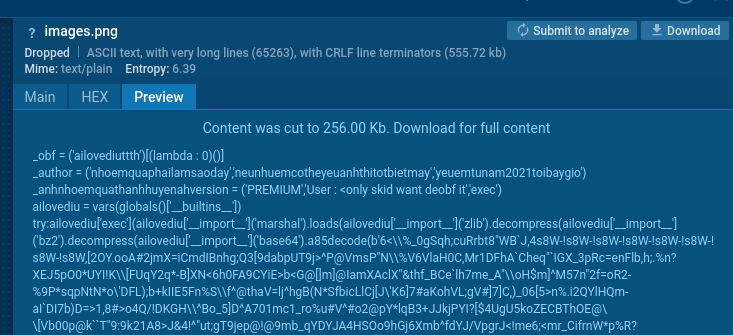
Finally, the Python script is initialized and sets a Run registry key.
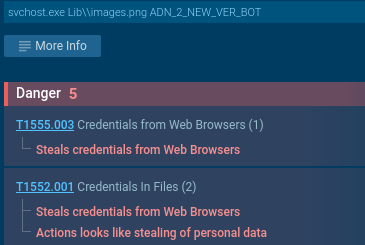
Once launched, the script proceeds to conduct standard functions of a stealer for data harvesting.
PXA Stealer malware distribution methods
PXA Stealer is most commonly distributed through:
- Phishing emails or messages on apps/social platforms
They contain archive attachments, inside of which there’s a legitimate file + a malicious DLL for sideloading. When a user launches the executable, the malicious DLL loads automatically.
- Download links
Threat actors also use malicious links shared via file-sharing or cloud storage services, as this allows them to bypass email filters.
- Files shared on corporate networks (user-initiated)
Notably, as PXA Stealer seemed to targeted government and educational institutions, in some cases it was distributed through internal messaging and storage systems.
- Fake software updates
PXA also spreads through the delivery of legitimate software update files with a malicious DLL in a bundle.
Gathering Threat Intelligence on PXA Stealer Malware
Gain actionable insights on PXA Stealer by browsing Threat Intelligence Lookup that provides:
Instant identification of suspicious files, URLs, domains, and IPs linked to PXA Stealer
Overview of related IOCs, IOBs, IOAs to facilitate threat hunting
Links to live sandbox investigations of PXA Stealer for deeper analysis
Insights into C2 connections, exfiltration methods, and distribution techniques
Streamlined incident response through immediate access to verified threat intelligence
Follow this link or copy the query to browse TI Lookup:
Conclusion
PXA Stealer remains high‑risk information‑stealing threat that abuses legitimate executables to evade detection. It exfiltrates credentials, browser data, cookies, and financial information, enabling account takeover, fraud, and further intrusions. Educational and government institutions seems to be especially endangered.
Adopt a proactive defense strategy with ANY.RUN to mitigate the business risks:
- Analyze suspicious files, archives, and multi‑stage payload chains in sandboxing solutions such as ANY.RUN’s Interactive Sandbox
- Track emerging PXA Stealer campaigns and strengthen detection across your environment in Threat Intelligence Lookup, a browsable collection of fresh IOCs and IOBs sourced from live investigations by over 15,000 SOC teams.
Get 50 trial request and start gathering actionable intelligence in TI Lookup. Sign up now
Other malware & phishing threats
 MiraiMirai is a self-propagating malware that scans the internet for vulnerable IoT devices and infects them to create a botnet. Mirai variants utilize lists of common default credentials to gain access to devices. Mirai's primary use is for launching distributed denial-of-service (DDoS) attacks, but it has also been used for cryptocurrency mining.
 AmadeyAmadey is a formidable Windows infostealer threat, characterized by its persistence mechanisms, modular design, and ability to execute various malicious tasks.
 Cobalt StrikeCobalt Strike is a legitimate penetration software toolkit developed by Forta. But its cracked versions are widely adopted by bad actors, who use it as a C2 system of choice for targeted attacks.
 Neptune RATNeptune RAT is a Visual Basic .NET remote access trojan that gives attackers full control over infected Windows machines while stealing credentials from 270+ applications, hijacking cryptocurrency transactions, spying on victims in real time, and, in its most destructive mode, wiping the operating system entirely. Marketed openly on GitHub, Telegram, and YouTube as the "Most Advanced RAT," it is distributed under a malware-as-a-service model.
 BackdoorA backdoor is a type of cybersecurity threat that allows attackers to secretly compromise a system and conduct malicious activities, such as stealing data and modifying files. Backdoors can be difficult to detect, as they often use legitimate system applications to evade defense mechanisms. Threat actors often utilize special malware, such as PlugX, to establish backdoors on target devices.
 Gh0st RATGh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.