Socelars
- 116
- Global rank
- 198
- Month rank
- 196
- Week rank
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
- Stealer
- Type
- Unknown
- Origin
- 1 December, 2019
- First seen
- 10 September, 2026
- Last seen
How to analyze Socelars with ANY.RUN
IOCs
IP addresses
- 130.211.204.114
- 212.193.30.29
- 91.121.67.60
- 104.247.81.99
- 199.232.214.172
- 172.67.74.161
- 212.192.241.62
- 212.193.30.45
- 172.66.171.73
- 142.251.127.94
- 135.181.129.119
- 162.159.135.233
- 104.26.3.46
- 162.159.133.233
- 192.178.183.94
- 104.20.29.150
- 104.26.2.46
- 142.251.14.94
- 162.159.129.233
- 142.250.154.94
Hashes
- 97de47068327bb822b33c7106f9cbb489480901a6749513ef5c31d229dcaca87
- e5a0ad2e37dde043a0dd4ad7634961ff3f0d70e87d2db49761eb4c1f468bb02f
- f619737825736cb07fa257b49de1473d191f97bfc4865d1d463da4775107cb42
- 2b8b9dd101fc57f8d10ce4f074c0005df955634dbb7d9e49465f9054d66628a9
- 6913b6cc93ab1fb509ab7459d6158be6f1b03ab06d2ed41782b86838bd504c49
- 199b2760ea58e930c7f2f2a4291b0faae59abd9948a35e568eca5a16a40cacf8
- 2d8f31b9af7675e61537ccadf06a711972b65f87db0d478d118194afab5b8ac3
- 45ed5fbac043165057280feac2c2b8afcf9981b5c1b656aa4bf1c03cf3144d42
- 79549765b31c2d546a368b2a75378ff43a859345bb1b5a6263418829baa2d50e
- 03d498a0a514396d851a4da6106d21390781c64409dd3cfc67764f09d7909284
- a86843475eb2d3128158cc781428ecc6ed86e1432ea18dcb74009c805bc15320
- 4feb70ee4d54dd933dfa3a8d0461dc428484489e8a34b905276a799e0bf9220f
- 0300e9ddb527990e8b59d06e9ccf3ec2bd92d3bbd0ef4fba69d6336e4195e82d
- 400800c461437e5e304ec4a597acc79436e522afd0acb7e32cc01ff26d3133dc
- d2bb091268ade68ad8121d2184d0fbce128070156304bd4de312e6fbd267409c
- 5d5c2a71eefddc926a2b5fffa42e74345945f35046d8c244d68caf6db49a15f6
- 56b0089585d0710cd852e486e2ab669d0d2881af34a87d43677f551310d7a553
- e593148ff02faa520ebea683c6898b457b052e2e3945001388e5b687e9d90e69
- a7de5177c68a64bd48b36d49e2853799f4ebcfa8e4761f7cc472f333dc5f65cf
- b02fffaba9e664ff7840c82b102d6851ec0bb148cec462cef40999545309e599
Domains
- m525-blockchain32.bar
- webdeadshare24.me
- wfsdragon.ru
- cdn.discordapp.com
- google.com
- ctldl.windowsupdate.com
- 56.jpgamehome.com
- pastebin.com
- www.listincode.com
- c.pki.goog
- tweakballs.com
- iplogger.org
- my-4ll-group.bar
- t.gogamec.com
- niemannbest.me
- client.wns.windows.com
- yr.c.lencr.org
- ppgggb.com
- directorycart.com
- futurepreneurs.eu
URLs
- https://cdn.discordapp.com/attachments/910281572803047425/910423656306446387/pctool.exe
- http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?6540073d12ca6d95
- https://iplogger.org/143up7
- http://c.pki.goog/r/r4.crl
- http://c.pki.goog/we1/btvd66z9uqy.crl
- https://iplogger.org/1brhn7
- https://iplogger.org/1bthn7
- https://pastebin.com/raw/a7dsg1te
- http://wfsdragon.ru/api/setstats.php
- http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?a371aca49b440c32
- http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?735da80a79cfdb47
- http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?0e8028ac689bf8da
- http://c.pki.goog/r/gsr1.crl
- http://ip-api.com/json/
- https://cdn.discordapp.com/attachments/900442917435473960/900698311521103882/pctool.exe
- https://iplogger.org/1a2jd7
- http://gcl-gb.biz/stats/1.php?pub=/mixone&badparam=nope
- https://iplogger.org/1a3jd7
- https://watson.events.data.microsoft.com/telemetry.request
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
Last seen at
- setup_x86_x64_install.exe
- setup_x86_x64_install.exe
- setup_x86_x64_install.exe
- setup_x86_x64_install.exe
- setup_x86_x64_install.exe
- 644ECDD263538E3F6DA1689A78B77101DD86451AFB376.exe
- 6d2ff3cc83ea214e33e4105ccb1051cd85b82e052f6152d7f252667f2f5a5ecb.exe
- 44e401aaf0b52528aa033257c1a1b8a09a2b10edf26edaafcef0f45a2c40e885.exe
- 17486a31039fa56636c672dba5f9ab12178f888839f41137416b4f85f2affdcb.exe
- dc99510c2660ee64b95820e61184f27d7dda8391f44804c6fe0d045bd106ae56.exe
Socelars: The Stealer That Turns Business Accounts into Cash
Key Takeaways
Built for ad account takeover: Socelars is explicitly associated with stealing data tied to Facebook Ads Manager operations, putting marketing budgets, brand pages, and business accounts at risk.
Cookie theft enables fast account abuse: Reported behavior includes stealing session cookies (Facebook and Amazon mentioned in public reporting), which can allow attackers to access accounts immediately without waiting for password resets.
Social-engineering friendly delivery: Campaigns have used a fake PDF reader lure to get users to install the malware, taking advantage of routine workplace behavior around “helper” tools.
Spyware/stealer family: Security vendors classify Socelars as a spyware/credential-stealing threat, built for quiet data theft rather than loud disruption.
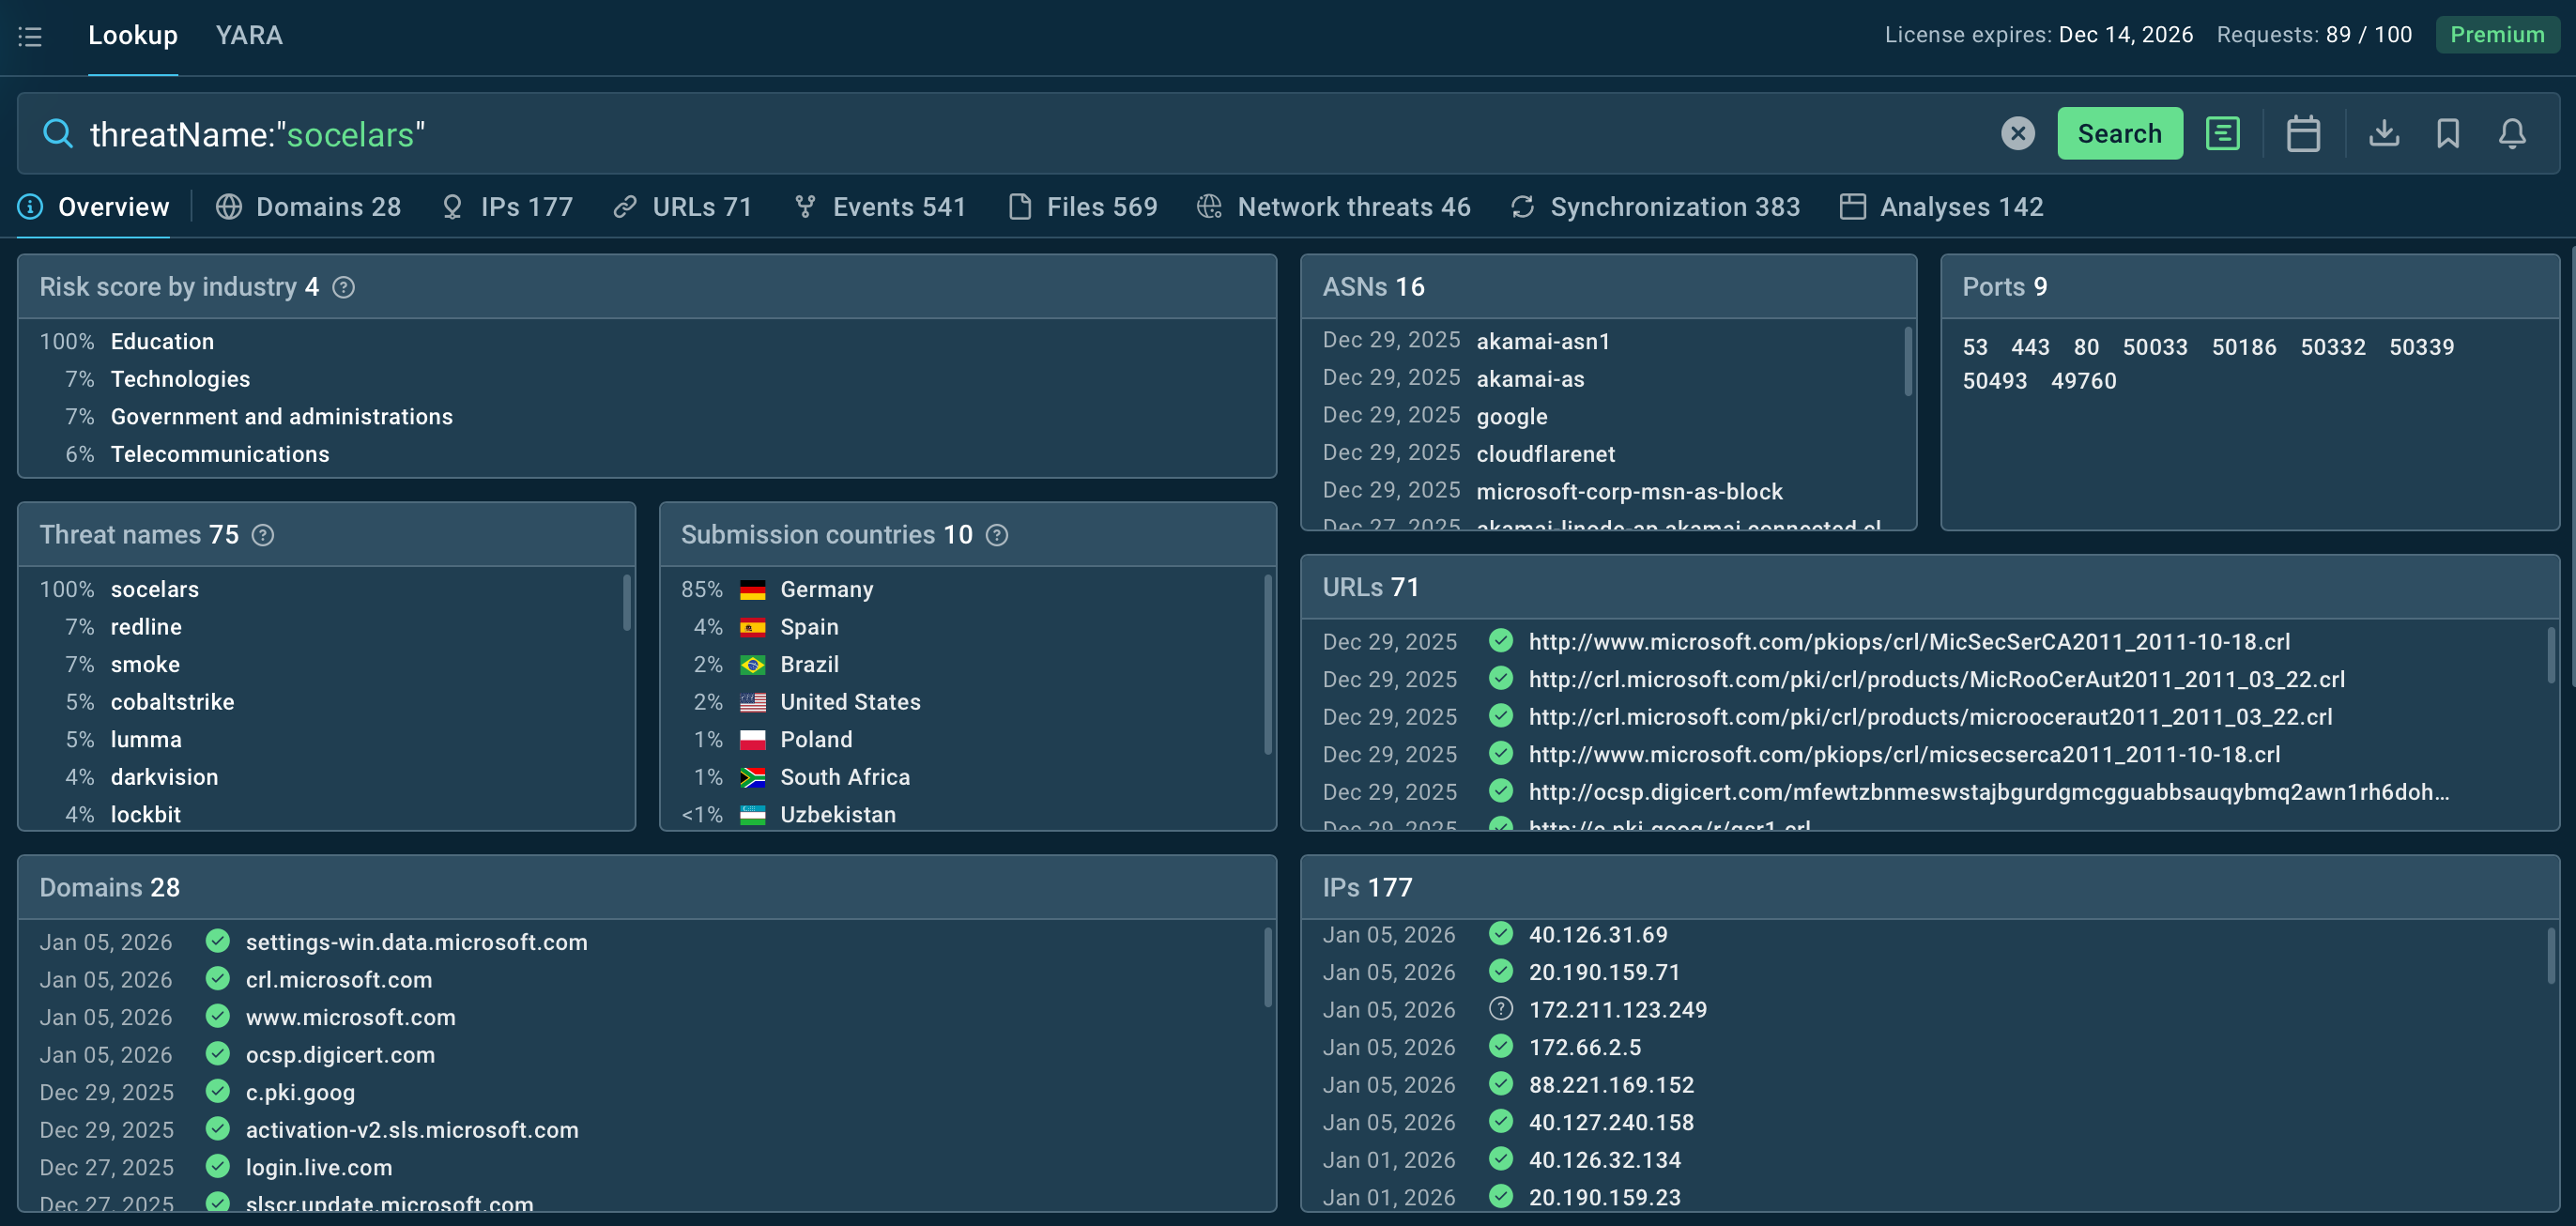
ANY.RUN’s Threat Intelligence Lookup helps SOCs quickly understand Socelars activity at scale and uncover relationships between related samples and infrastructure.
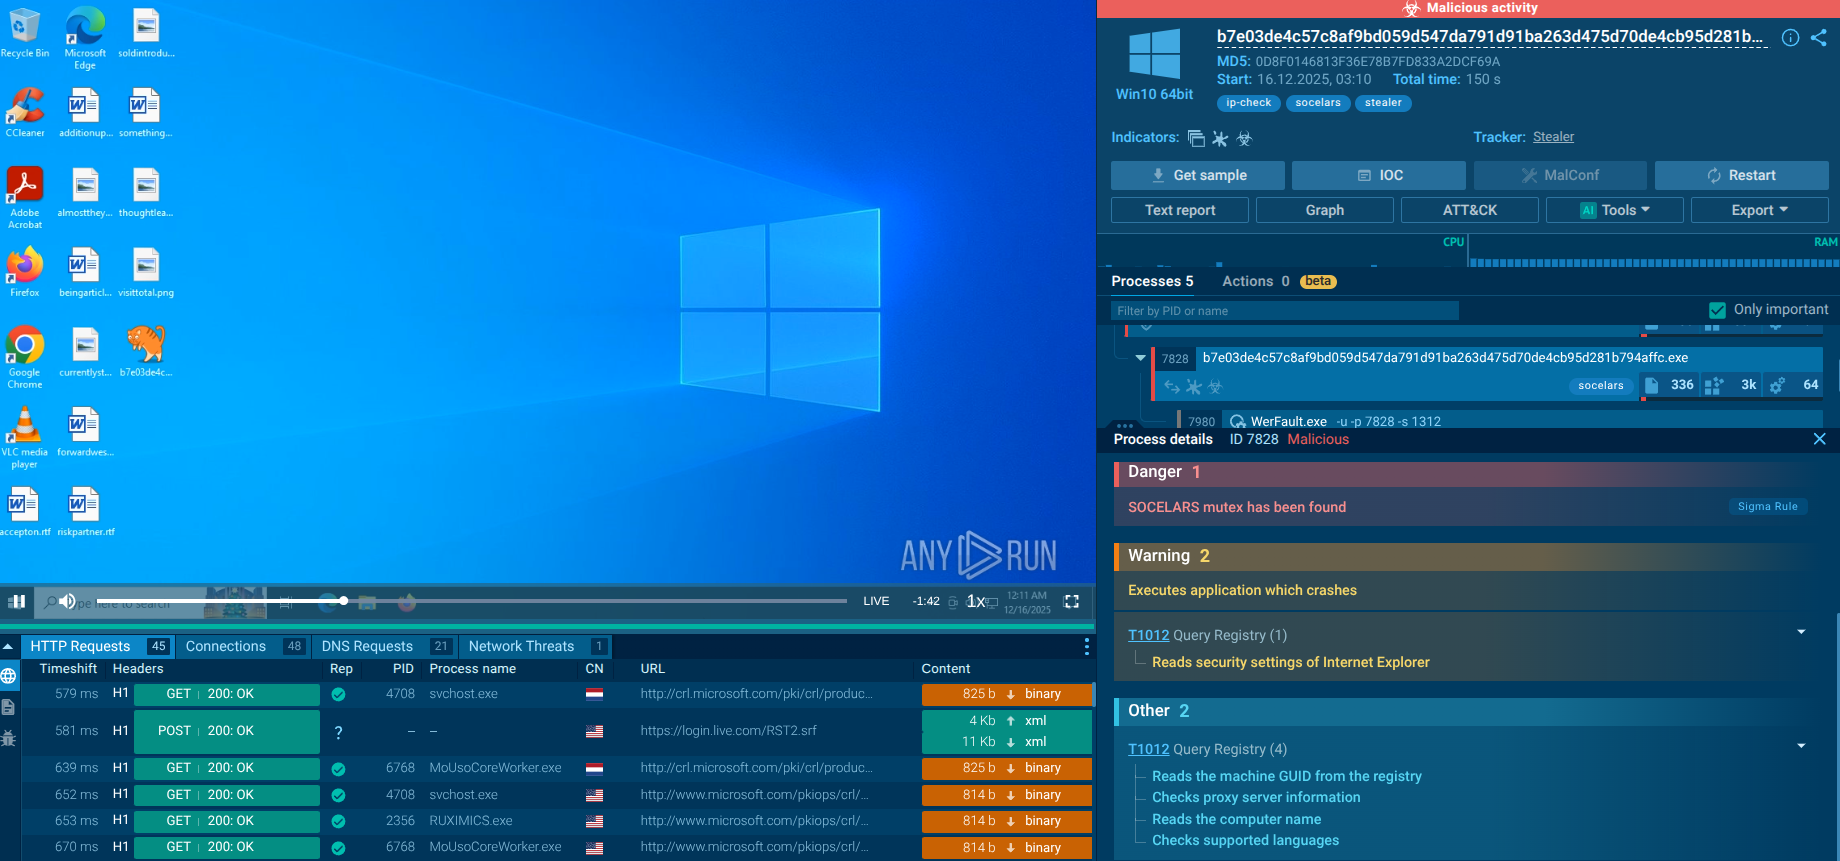
- ANY.RUN’s Interactive Sandbox lets teams safely observe Socelars’ behavior and extract actionable indicators in real time.
What is Socelars Malware?
Socelars is an information-stealing malware family designed to harvest authenticated session data, system identifiers, and other artifacts that enable rapid account takeover and financial abuse.
Rather than disrupting systems immediately, it focuses on quietly collecting the access attackers need to operate inside trusted business services and logged-in environments.
Public reporting links Socelars activity to the theft of session cookies associated with platforms such as Facebook and Amazon, which can allow attackers to access accounts without waiting for password resets or triggering obvious security alerts.
This makes the threat especially dangerous for organizations that rely on advertising platforms, e-commerce accounts, or cloud-based business tools, where stolen sessions can be monetized quickly.
From a technical perspective, Socelars combines:
- System reconnaissance to profile the infected environment
- Privilege escalation techniques, including UAC bypass through COM auto-elevation
- Stealthy data collection targeting browser-stored authentication artifacts
- Minimal visible impact, allowing abuse to occur before detection
As the malware’s primary goal is immediate operational access rather than destruction, traditional defenses that focus on ransomware-style behavior may detect the incident too late.
In practice, Socelars turns a single unnoticed infection into a pathway for account compromise, financial loss, and compliance exposure, making early behavioral detection and threat-intelligence visibility critical for effective defense.
How Socelars Threatens Businesses and Organizations
Socelars is dangerous not because it disrupts systems immediately, but because it quietly targets the accounts and sessions that drive revenue and operations.
Instead of triggering visible alarms, the malware focuses on stealing authenticated browser data and business platform access, allowing attackers to act as legitimate users while remaining unnoticed.
Key business risks include:
Direct financial loss through ad account abuse: Access to Facebook Ads Manager sessions enables attackers to launch fraudulent campaigns, drain advertising budgets, or resell compromised accounts on underground markets.
Account takeover without traditional credential theft: By extracting active session cookies, attackers may bypass password resets and, in some cases, multi-factor authentication flows, gaining immediate control over business services.
Reputational and customer-trust damage: Compromised advertising or brand pages can be used to distribute scams, malicious links, or misleading promotions that impact customer confidence and brand integrity.
Compliance and data-protection exposure: Unauthorized access to business platforms and stored user data may trigger regulatory obligations, breach notifications, and potential financial penalties.
Hidden dwell time before discovery: Because Socelars operates quietly in the background, attackers may maintain access long enough to monetize accounts or expand compromise before defenders notice suspicious activity.
This means a single infected workstation can escalate into a multi-department business incident affecting marketing, finance, legal, and security teams simultaneously.
Victimology: Vulnerable Industries and Sectors
Socelars targets business accounts and browser sessions, not infrastructure, so risk is the highest where authenticated access maps directly to money.
Most exposed sectors include:
Marketing and advertising-driven companies: Heavy use of Facebook Ads Manager creates direct budget and account-takeover risk.
Agencies managing client ad accounts: One infected workstation can impact multiple customers at once.
E-commerce and consumer brands: Ad abuse can quickly translate into lost spend, fraud, and customer trust damage.
SMEs: More likely to fall for fake utility lures (such as PDF tools) due to lighter controls and training.
In practice, exposure depends less on industry and more on how much the organization relies on long-lived browser sessions for business-critical platforms.
How Can Businesses Proactively Protect Against Socelars
ANY.RUN’s Threat Intelligence Feeds deliver real-time, actionable indicators derived from sandbox detonations and global community submissions.
For Socelars, these feeds surface emerging distribution artifacts, related samples, and infrastructure linked to session-stealing activity, enabling automated detection and blocking across firewalls, EDR, and SIEM platforms.
This allows organizations to identify compromise before stolen sessions are abused, shorten attacker dwell time, and prevent follow-on fraud or account takeover, which is critical for threats designed to monetize access quickly rather than disrupt systems immediately.
Business Impact:
Reduced Mean Time to Detect (MTTD): Fresh indicators help teams identify Socelars activity within minutes, limiting the window for silent session theft.
Prevention of Account Abuse and Financial Loss: Blocking known artifacts and related infrastructure reduces the chance of fraudulent ad spending, unauthorized campaigns, and account resale.
Protection of Brand Trust and Compliance Posture: Early detection lowers the risk of customer-facing scams, data exposure, and regulatory consequences tied to compromised business accounts.
Stronger Security ROI Through Shared Intelligence: Leveraging threat intelligence contributed by 15,000+ organizations improves detection coverage without requiring proportional investment in new tooling or staffing.
Infection Vectors and Propagation Methods
Socelars is primarily distributed through social-engineering techniques designed to appear routine and trustworthy rather than overtly malicious.
Public reporting links campaigns to fake software utilities, including installers presented as legitimate PDF readers or similar everyday tools, which encourages users to execute the malware without suspicion.
These delivery methods rely on common workplace behavior: downloading quick-fix utilities, opening attachments tied to business activity, or installing software outside approved channels.
Because the initial file often looks harmless, traditional security controls may not flag the threat before execution.
Propagation Mechanism
After execution on a victim system, Socelars focuses on local data collection and session extraction rather than noisy self-spreading behavior.
Typical post-infection activity includes:
Accessing browser storage and session cookies tied to business services;
Collecting authentication data that enables immediate account takeover or fraud;
Preparing stolen information for exfiltration and attacker monetization.
This approach allows attackers to move directly from a single user action to business-level impact, without requiring lateral movement or complex network propagation.
In practice, Socelars spreads less through automated worm-like behavior and more through repeatable social-engineering campaigns, making user interaction and early detection the critical defensive boundary.
How Socelars Functions
Socelars is designed to quietly extract high-value authentication data from an infected Windows system rather than cause immediate disruption. Its goal is to obtain information that allows attackers to access business-critical online services, especially advertising platforms and other authenticated web applications, without triggering obvious alerts.
Stage 1: Execution and Environment Preparation
After a victim runs the disguised installer or utility, Socelars begins operating in the background with minimal visible activity.
At this stage, the malware prepares the environment for data collection, ensuring it can access local browser storage, session artifacts, and user profile data without interrupting normal system use.
Stage 2: Session and Credential Data Collection
The core capability of Socelars is harvesting information that provides ready-to-use access rather than just raw credentials.
This includes:
Active browser session cookies that may allow attackers to bypass login prompts
Stored authentication data tied to business platforms such as advertising or e-commerce services
Additional local information useful for account takeover or monetization
As session data can remain valid even after passwords change, this stage enables immediate unauthorized access and rapid financial abuse.
Stage 3: Data Exfiltration and Monetization
Once sensitive data is collected, Socelars prepares it for exfiltration to attacker-controlled infrastructure.
The stolen access can then be used to:
Launch fraudulent advertising campaigns or drain marketing budgets
Resell compromised business accounts on underground markets
Expand compromise into related services or customer-facing assets
Unlike ransomware, which reveals itself through visible disruption, Socelars completes its objective silently, allowing attackers to profit before defenders detect the intrusion.
Sandbox Analysis of a Socelars Sample
To understand how Socelars behaves in a real environment, analysts can detonate a suspected sample inside ANY.RUN’s Interactive Sandbox, where execution unfolds safely and every action is recorded in real time.
View analysis session with Socelars
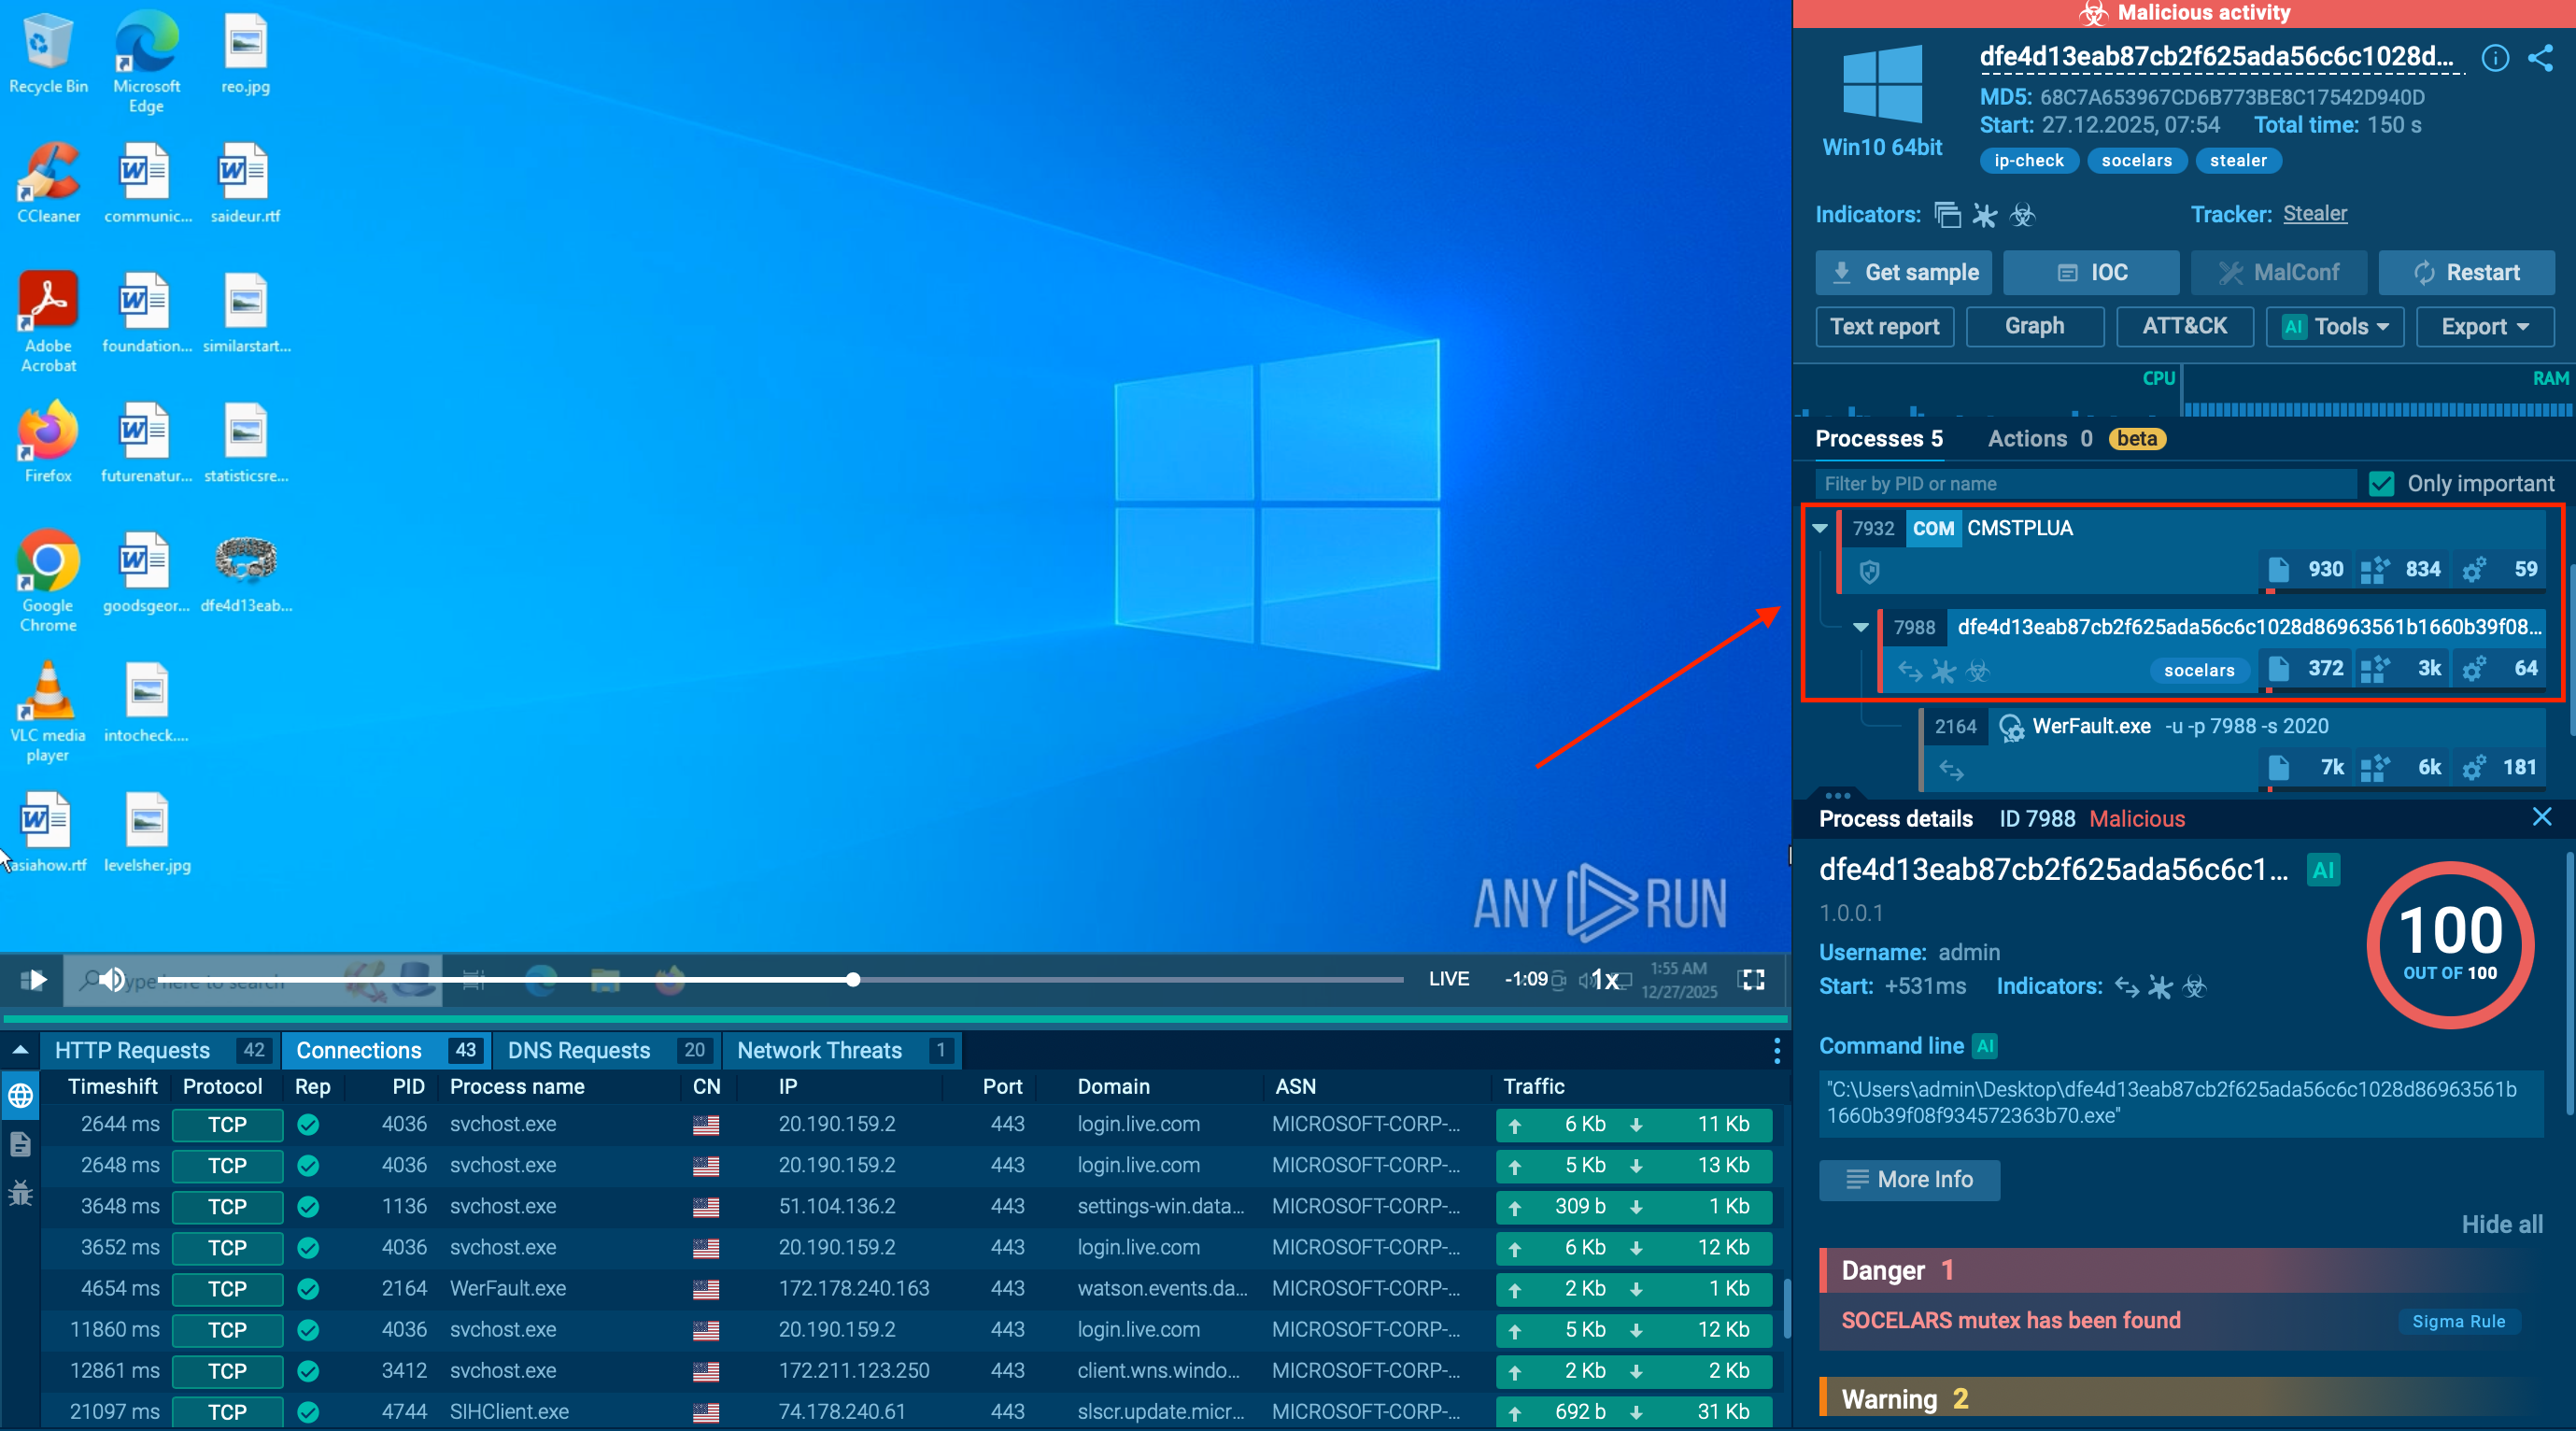
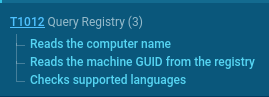
Immediately after execution, the malware begins system reconnaissance on the infected host. It collects the computer name, extracts the Machine GUID from the registry, checks installed system languages, reads Internet Settings parameters, and inspects system certificate configuration.
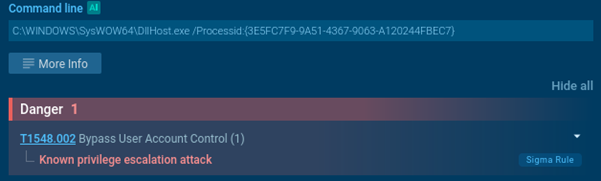
The next stage involves a User Account Control (UAC) bypass. Socelars launches dllhost.exe with the parameter /Processid:{CLSID}, where the CLSID corresponds to the ICMLuaUtil interface from cmlua.dll, a component that allows auto-elevated privilege execution.
Through this COM object, the malware invokes the **ShellExec method to run its payload with elevated rights.
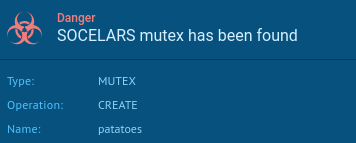
After successful privilege escalation, the sample creates a mutex named “patatoes”, a distinctive artifact associated with this Socelars variant.
The malware then contacts the iplogger[.]org service. In this context, the public IP-logging service acts as a proxy layer, recording the victim’s IP address, User-Agent, timestamp, and geographic location for the attacker before transparently redirecting the request further, potentially toward a command-and-control server or the next attack stage.
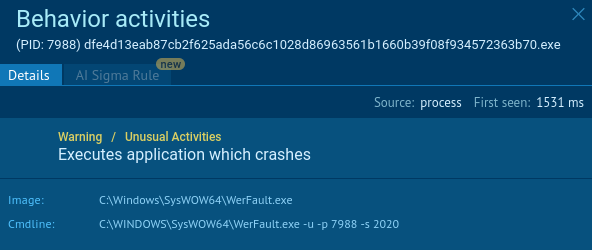
At this point, all analyzed samples were observed to terminate intentionally with a crash, preventing further visible execution while preserving the attacker’s collected reconnaissance and telemetry.
Gathering Threat Intelligence on Socelars Stealer
ANY.RUN’s Threat Intelligence Lookup provides critical capabilities for detecting, investigating, and responding to Socelars activity across environments.
Rapid Indicator Validation and Context Enrichment
When security alerts surface potential Socelars-related artifacts, such as suspicious installers, file hashes, domains, or browser-data access behavior, SOC analysts can query TI Lookup to immediately determine whether those indicators are linked to known session-stealing campaigns.
TI Lookup enriches raw indicators with:
- malware family classification,
- related samples and execution history,
- behavioral context tied to account-takeover activity
This turns isolated alerts into actionable intelligence within seconds, enabling faster containment of threats that monetize access quickly.
Direct Access to Confirmed Behavioral Analysis
TI Lookup connects indicators to interactive sandbox sessions where Socelars attack chains have already been executed and recorded.
Instead of re-analyzing suspicious files from scratch, teams can:
- Observe how the malware accesses browser storage and session data;
- Review outbound communication and potential exfiltration patterns;
- Extract high-confidence indicators for environment-wide blocking.
Start exploring Socelar’s activity using a threat-name search:
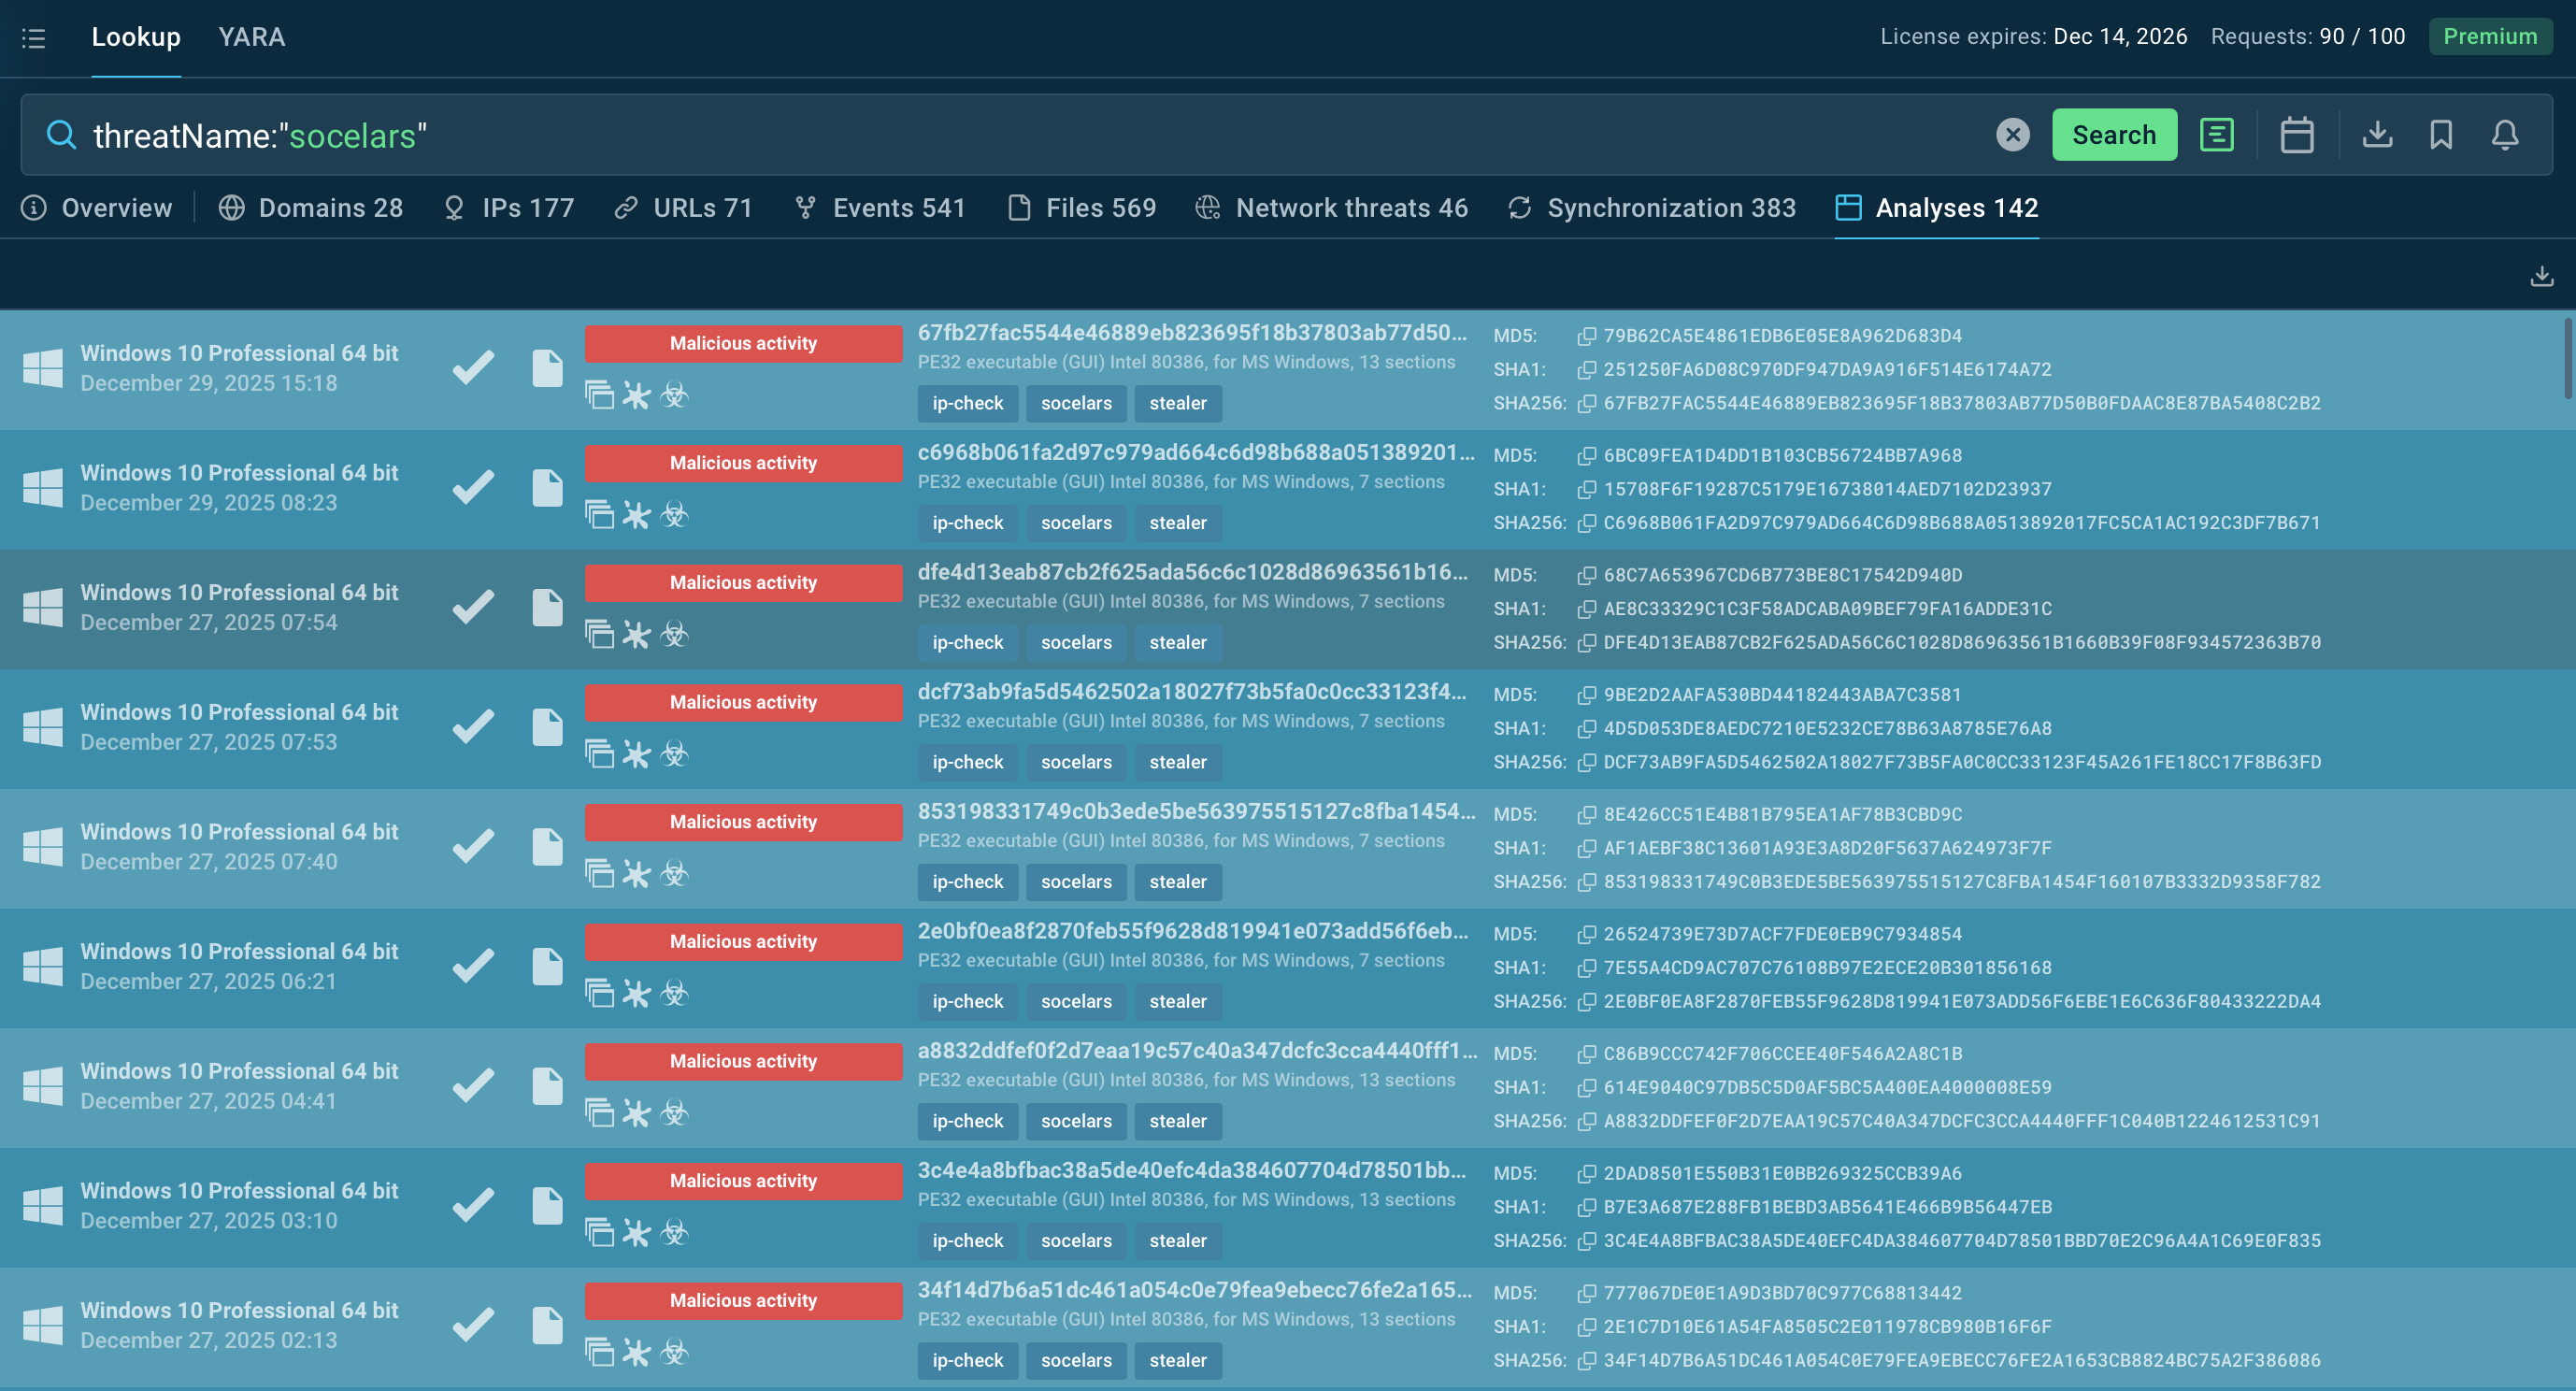
This immediate visibility shortens investigation time and accelerates response decisions.
Multi-Dimensional Event Correlation
With 40+ searchable parameters, including process activity, command lines, file paths, registry interaction, and network indicators, analysts can investigate Socelars infections from multiple angles.
For example, correlating browser-data access patterns or suspicious installer execution across submissions can reveal:
- Repeated distribution techniques,
- Shared infrastructure,
- Evolving campaign behavior.
This allows defenders to move from single-incident response to campaign-level understanding.
Detection Engineering and Rule Validation
TI Lookup supports YARA-based searching and validation, allowing security teams to test custom detection logic against a large corpus of analyzed malware.
For Socelars, this helps teams:
- Identify unique data-collection or execution traits;
- Validate detection rules against real samples;
- Reduce false positives before deployment in production controls.
Proactive Threat Hunting
Beyond reactive investigation, analysts can use TI Lookup to hunt for hidden Socelars activity that may have bypassed initial alerts, particularly important for malware focused on quiet session theft rather than visible disruption.
Operational Value for SOCs and MSSPs
Combining sandbox intelligence with large-scale threat correlation delivers measurable outcomes:
- Reduced Mean Time to Respond (MTTR),
- Lower false-positive investigation overhead,
- Broader detection coverage across environments,
- Improved analyst efficiency and workload balance,
- Optimized security cost through shared intelligence.
Conclusion
Socelars is dangerous because it targets business access instead of systems, stealing sessions and account data that attackers can monetize quickly, often before teams realize anything is wrong. The fastest way to reduce impact is to confirm behavior early and widen visibility beyond a single alert with threat intelligence.
Try TI Lookup to find related Socelars activity, validate indicators in seconds, and understand campaign scope fast: just sign up to ANY.RUN.
Other malware & phishing threats
 QbotQbot is a banking Trojan — a malware designed to collect banking information from victims. Qbot targets organizations mostly in the US. It is equipped with various sophisticated evasion and info-stealing functions and worm-like functionality, and a strong persistence mechanism.
 Fog RansomwareFog is a ransomware strain that locks and steals sensitive information both on Windows and Linux endpoints. The medial ransom demand is $220,000. The medial payment is $100,000.
First spotted in the spring of 2024, it was used to attack educational organizations in the USA, later expanding on other sectors and countries. Main distribution method — compromised VPN credentials.
 KeyloggerA keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
 SmartLoaderSmartLoader is a Windows malware loader that uses multi-stage execution to deliver secondary payloads. It supports system discovery, screenshot capture, persistence through scheduled tasks, C2 communication, and anti-analysis techniques.
 STRRATSTRRAT is a type of malicious software known as a remote access trojan (RAT). It gives attackers the ability to gain full control over a victim's computer system, enabling them to steal confidential information, spy on their activities, and drop other malware. STRRAT has been in operation since 2020 and is regularly updated to increase its complexity and make it more difficult to detect.