Chaos Ransomware
- 67
- Global rank
- 62
- Month rank
- 108
- Week rank
Chaos ransomware is a malware family known for its destructive capabilities and diverse variants. It first appeared in 2021 as a ransomware builder and later acted as a wiper. Unlike most ransomware strains that encrypt data to extort payment, early Chaos variants permanently corrupted files, while later versions adopted more conventional encryption techniques.
- Ransomware
- Type
- Unknown
- Origin
- 1 June, 2021
- First seen
- 16 October, 2026
- Last seen
How to analyze Chaos Ransomware with ANY.RUN
IOCs
IP addresses
- 107.174.192.179
- 48.209.138.189
- 82.29.67.160
- 142.251.20.132
- 104.26.9.202
- 2.23.246.9
- 142.251.13.154
- 142.251.110.102
- 172.211.123.250
- 23.59.18.102
- 142.251.154.119
- 20.166.131.27
- 2.16.204.135
- 142.251.20.155
- 188.114.97.3
- 23.59.17.18
- 150.171.27.11
- 104.26.13.64
- 192.178.183.139
- 185.111.111.157
Hashes
- 74441313bb1fb62500484443c4937e90d4e335351a4fcd12a9ac48448500e33e
- 2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
- 4094d158e3b0581ba433a46d0dce62f99d8c0fd1b50bb4d0517ddc0a4a1fde24
- 99653a38c445ae1d4c373ee672339fd47fd098e0d0ada5f0be70e3b2bf711d38
- c158322bd963d2a68ffc878d72213a7394d8c16de72279771ffc924365eec0df
- 59345c006cd9bde5ef532aae1f119758d45030993181c272bb0dd6fc0c5d01e5
- 2ae1142b08d296c25000e451237ea919f981da28f6a723d39540f43f18bac762
- 5639c845d56dedecd2cfdb082b734593b5d618a87f1bd8ec612a8b3f4245566a
- 32ae9531405ef3c59448fe6dbd3be435e726eb17f3ca0d16530a4c6317dea286
- 7c68f28c6995f47dd77596bab28c6b4388ff93840c3becfd37733ddb640cd0cd
- 40cf1af5650b699a947899d2b43a00dcb64cdeaf080651c82a7930910c1c03f4
- ec249b0dab6fda20cc24f0f25a504c55a05b23fb6cbb4938aa7a41df0c8744b6
- 0162159b64eb092f94964faf937f263fb9947b25d40e0d82bd3224d136a140de
- 77eed9211cd8464482f0da3fac4c0f003c2b8a6d76f15445927e66400f102d60
- 6558013f984e594bb57534910ce0b17bfa15da3cc9bb4b6e0b5c6e4ddf9eb14e
- a7109b8374dffa7a0cd69558990f7e96fea9ef61736d89043dad5a6694cdfa4a
- 758a0b404b3daadbd0d4e88a0bedf5c21d5507392f7b54d4906ffea49d58ab32
- 558bbe6193a202dcb00cc441421f5d838764e495b8e4d2e10877db7f661b8cd5
- db3ac1fd3d65df45d805adb8dfe0c5209db07ef93406db17dfb783dd8048720a
- 19acfa0adce363a9c9a3be73f5ec0fac0dcf3c630ce18125fd265040ad6ffb6c
Domains
- fundingchoicesmessages.google.com
- pagead2.googlesyndication.com
- copilot.microsoft.com
- t.me
- ip-api.com
- jackthyfuc.run
- laminaflbx.shop
- identitytoolkit.googleapis.com
- fonts.googleapis.com
- plausible.io
- edge.microsoft.com
- tracenep-eu.admaster.cc
- ep1.adtrafficquality.google
- update.googleapis.com
- www.bing.com
- must-directed.gl.at.ply.gg
- uploadnow.io
- oneocsp.microsoft.com
- www.googletagmanager.com
- edge-consumer-static.azureedge.net
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:qyiwdga5l7ws_4bzfjxxyioxf9ookxt0g7n-czu98sk&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://copilot.microsoft.com/c/api/user/eligibility
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://uploadnow.io/en/share?utm_source=0bcds7g
- https://cdn.uploadnow.io/_next/static/css/5117ad1bbac15a06.css
- https://cdn.uploadnow.io/_next/static/css/bdb3e22b41fb00da.css
- https://cdn.uploadnow.io/_next/static/css/5ded0d5ca9ecc5c1.css
- https://cdn.uploadnow.io/_next/static/css/56b52b0051b23322.css
- https://cdn.uploadnow.io/_next/static/chunks/framework-76034876ab87df27.js
- https://cdn.uploadnow.io/_next/static/chunks/webpack-601ccb16b36d1888.js
- https://cdn.uploadnow.io/_next/static/chunks/main-8d1cee1b5c7f376f.js
- https://cdn.uploadnow.io/_next/static/chunks/pages/_app-090ad369d35c5500.js
- https://cdn.uploadnow.io/_next/static/chunks/62867-3e700a701aca7086.js
- https://cdn.uploadnow.io/_next/static/chunks/38993-242fdc22cc1c9823.js
Last seen at
What is Chaos Ransomware?
Observed since 2021, Chaos Ransomware has undergone an eventful yet rapid evolution. At its early stage, it branded itself as “Ryuk .Net Ransomware Builder” and mimicked Ryuk ransom notes but actually had little in common with Ryuk. Later it became known as Yashma and was spotted functioning as a wiper, a remote access trojan (RAT) and DDoS botnet (Kaiji variant).
Written in Golang, it targets both Windows and Linux systems across various hardware architectures. Unlike traditional ransomware, Chaos often corrupts files beyond recovery rather than providing a decryption option, making it particularly dangerous.
The malware attacks critical infrastructure sectors like manufacturing, healthcare, and energy, but also is a constant menace to SMEs with limited cybersecurity resources since its low-cost deployment via ransomware-as-a-service (RaaS) models makes it accessible to less sophisticated cybercriminals.
Chaos ransomware employs common yet effective methods to gain initial access to networks:
- Phishing and Social Engineering;
- Exploit Kits and Vulnerabilities (e.g. misconfigured Apache Tomcat servers);
- Malvertising and Compromised Websites (particularly those running outdated CMS versions, e.g.WordPress);
- Remote Code Execution (RCE), often targeting weak authentication protocols or unpatched software;
- Fake Software Updates;
- Trojanized Installers or cracked software (commonly found on torrent sites);
- Post-Exploitation Deployment via tools like Cobalt Strike or remote access trojans (RATs).
Chaos Ransom’s Prominent Features
Chaos is notable for:
- Widespread availability: Chaos as a ransomware builder allows even low-skilled actors create their own variants.
- Fast mutation: the ease of customization leads to countless versions, making signature-based defenses ineffective.
- Dual-purpose use: Chaos can be used both as ransomware and as a wiper, making it appealing for political or destructive campaigns.
- Irrecoverable data loss: early versions destroy files rather than encrypt them.
Once inside, Chaos affiliates use tools like AngryIPScanner, Nmap, or PowerShell to map networks and identify high-value targets for encryption or data exfiltration.
Once deployed, Chaos ransomware follows a typical ransomware kill chain. It ensures persistence by leveraging system startup scripts, such as init.d or systemd, to execute malicious files (e.g., /boot/System.img.config) on boot. Then it encrypts files and may exfiltrate sensitive data for double-extortion tactics. A ransom note is generated, demanding payment in cryptocurrency.
The malware may attempt to disable recovery features and security tools and delete shadow copies. Evasion techniques include code obfuscation, packing and encryption, fileless execution in some versions, and use of legitimate certificates in rare cases. Polymorphism is also important: multiple Chaos builds differ in structure and behavior, frustrating signature-based antivirus tools.
Chaos’s Execution Process and Technical Details
A sample of Chaos ransomware can be thoroughly studied in the safe environment of ANY.RUN’s Interactive Sandbox with its processes, artifacts, and the typical kill chain.
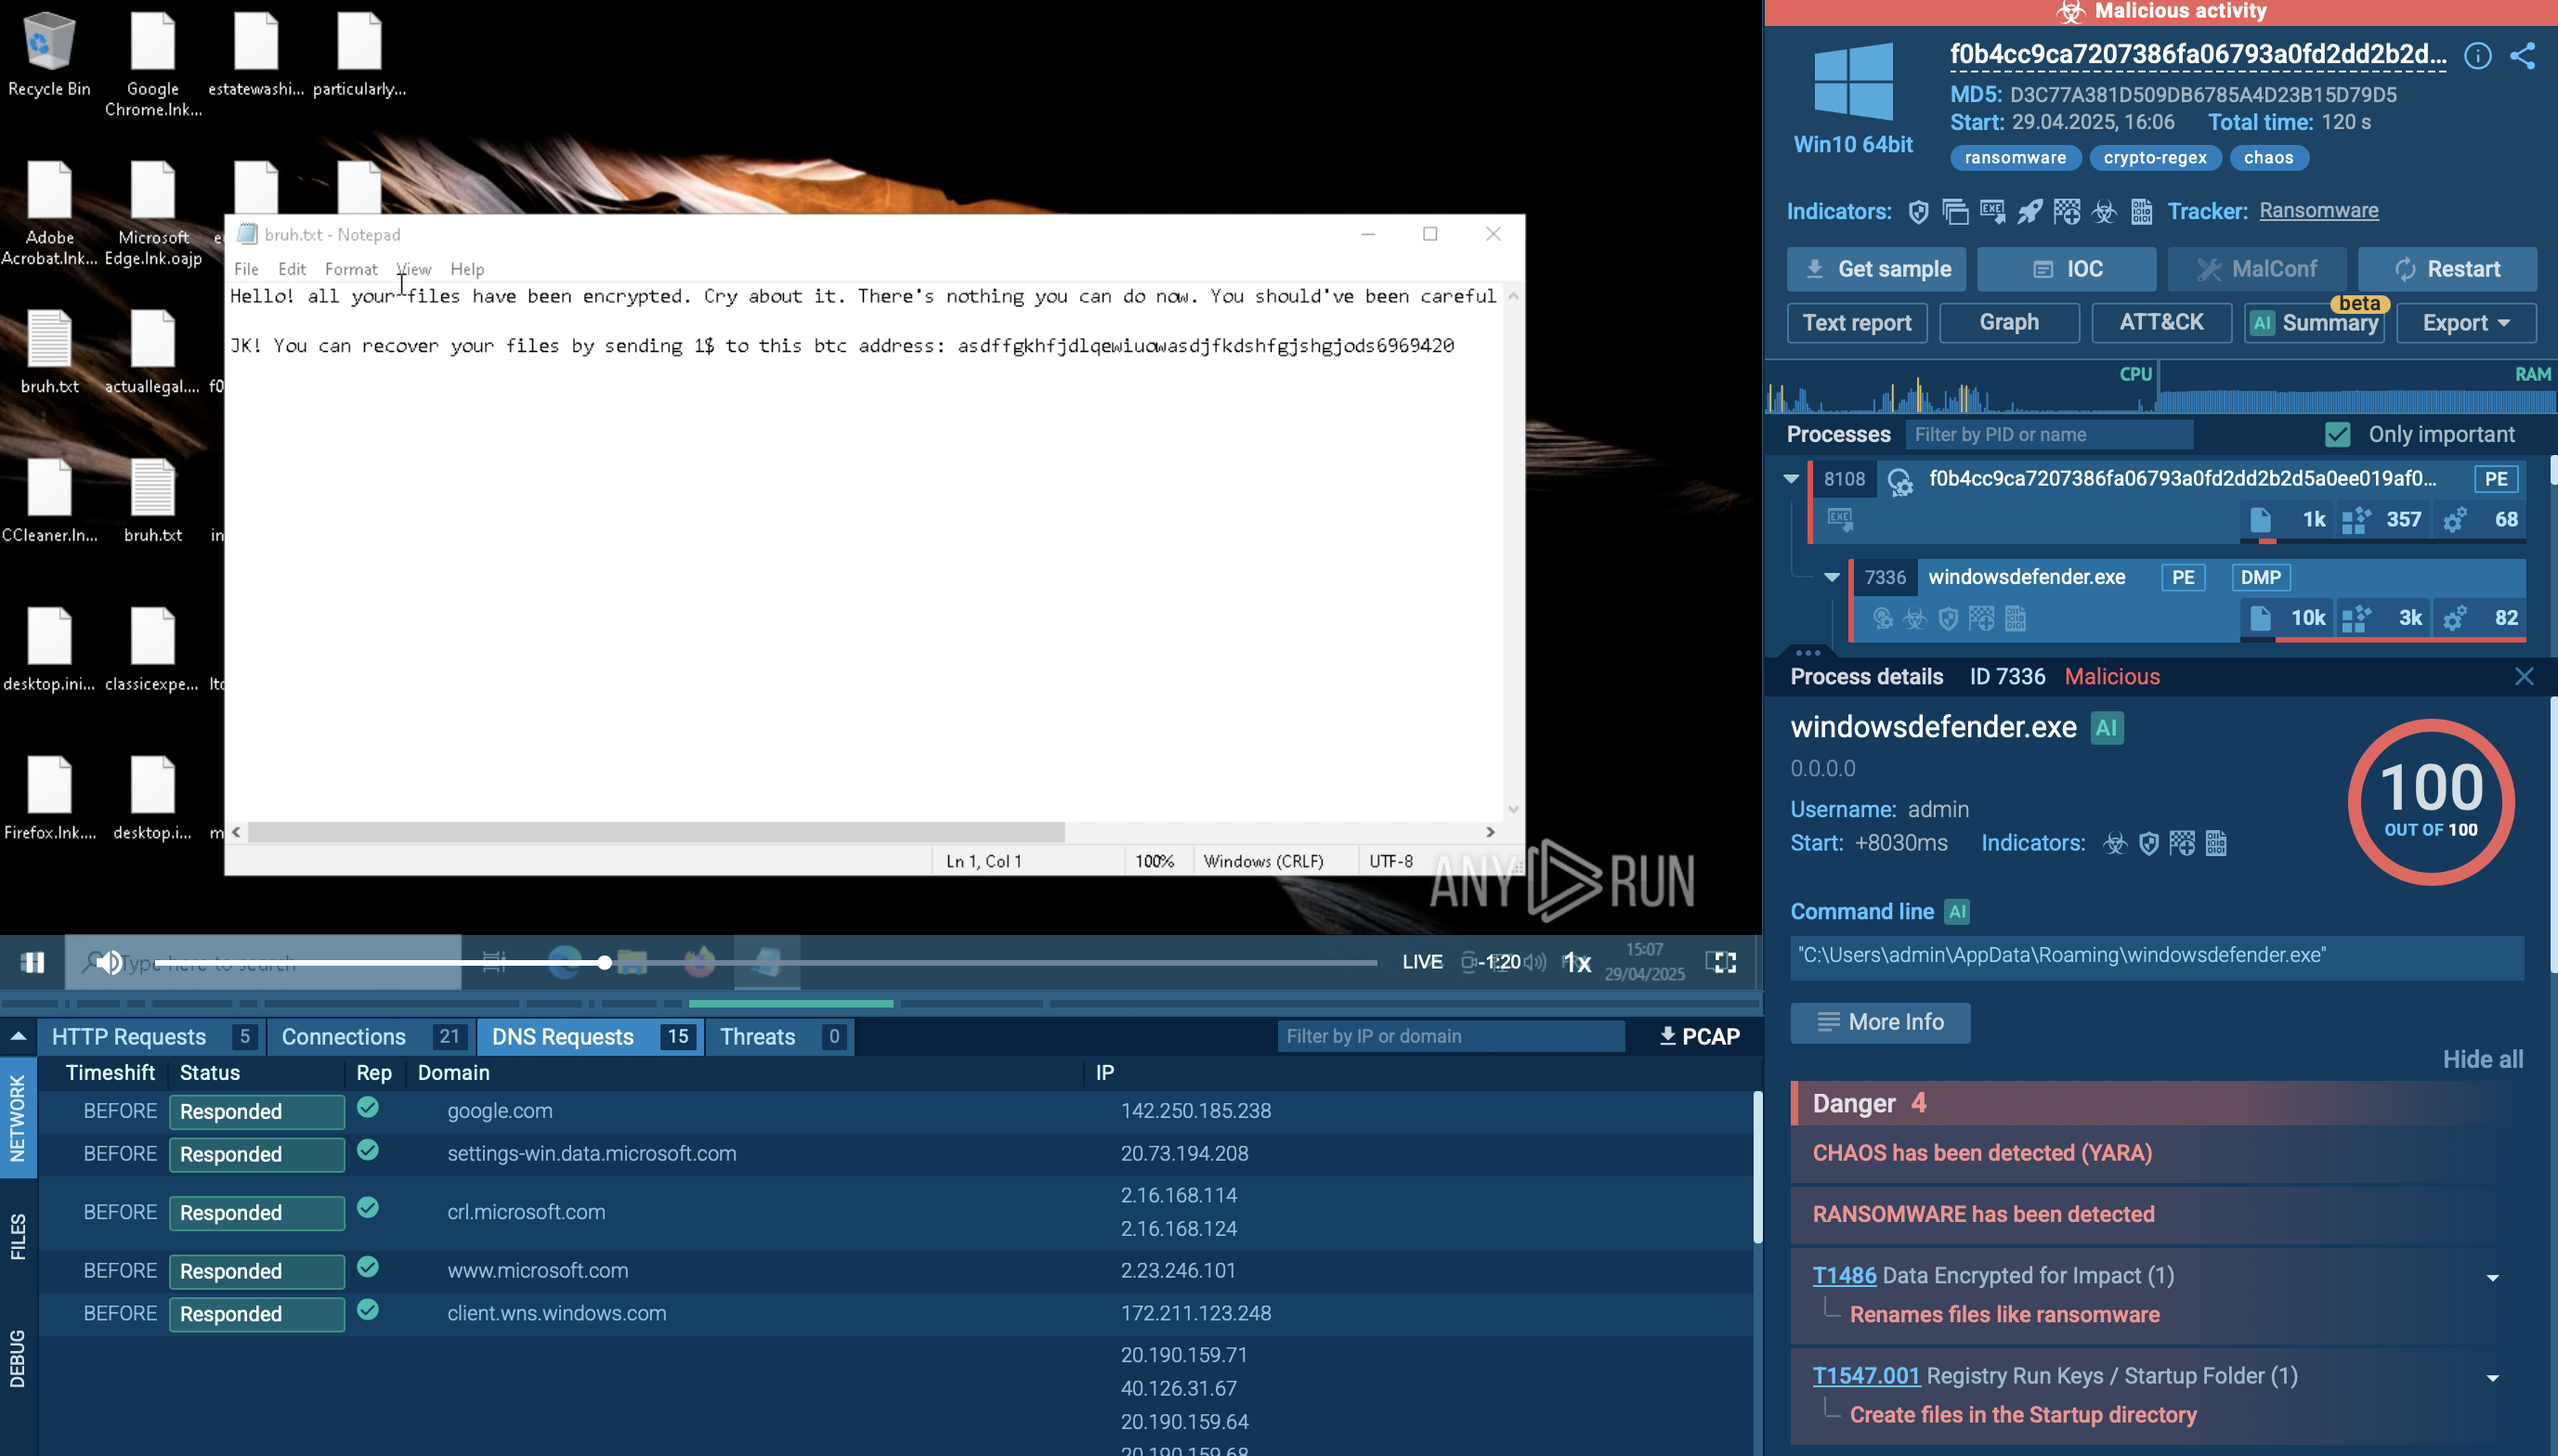
The execution chain of Chaos ransomware typically starts with phishing emails that carry malicious LNK shortcuts. Opening one of these files launches obfuscated PowerShell commands that retrieve a self-extracting archive from a remote server. The archive contains the Chaos ransomware executable together with loaders for additional malware. Once run, Chaos copies itself to a hidden location such as %AppData%\windowsdefender.exe and achieves persistence by placing a shortcut in the Windows Startup folder, guaranteeing execution after every reboot.
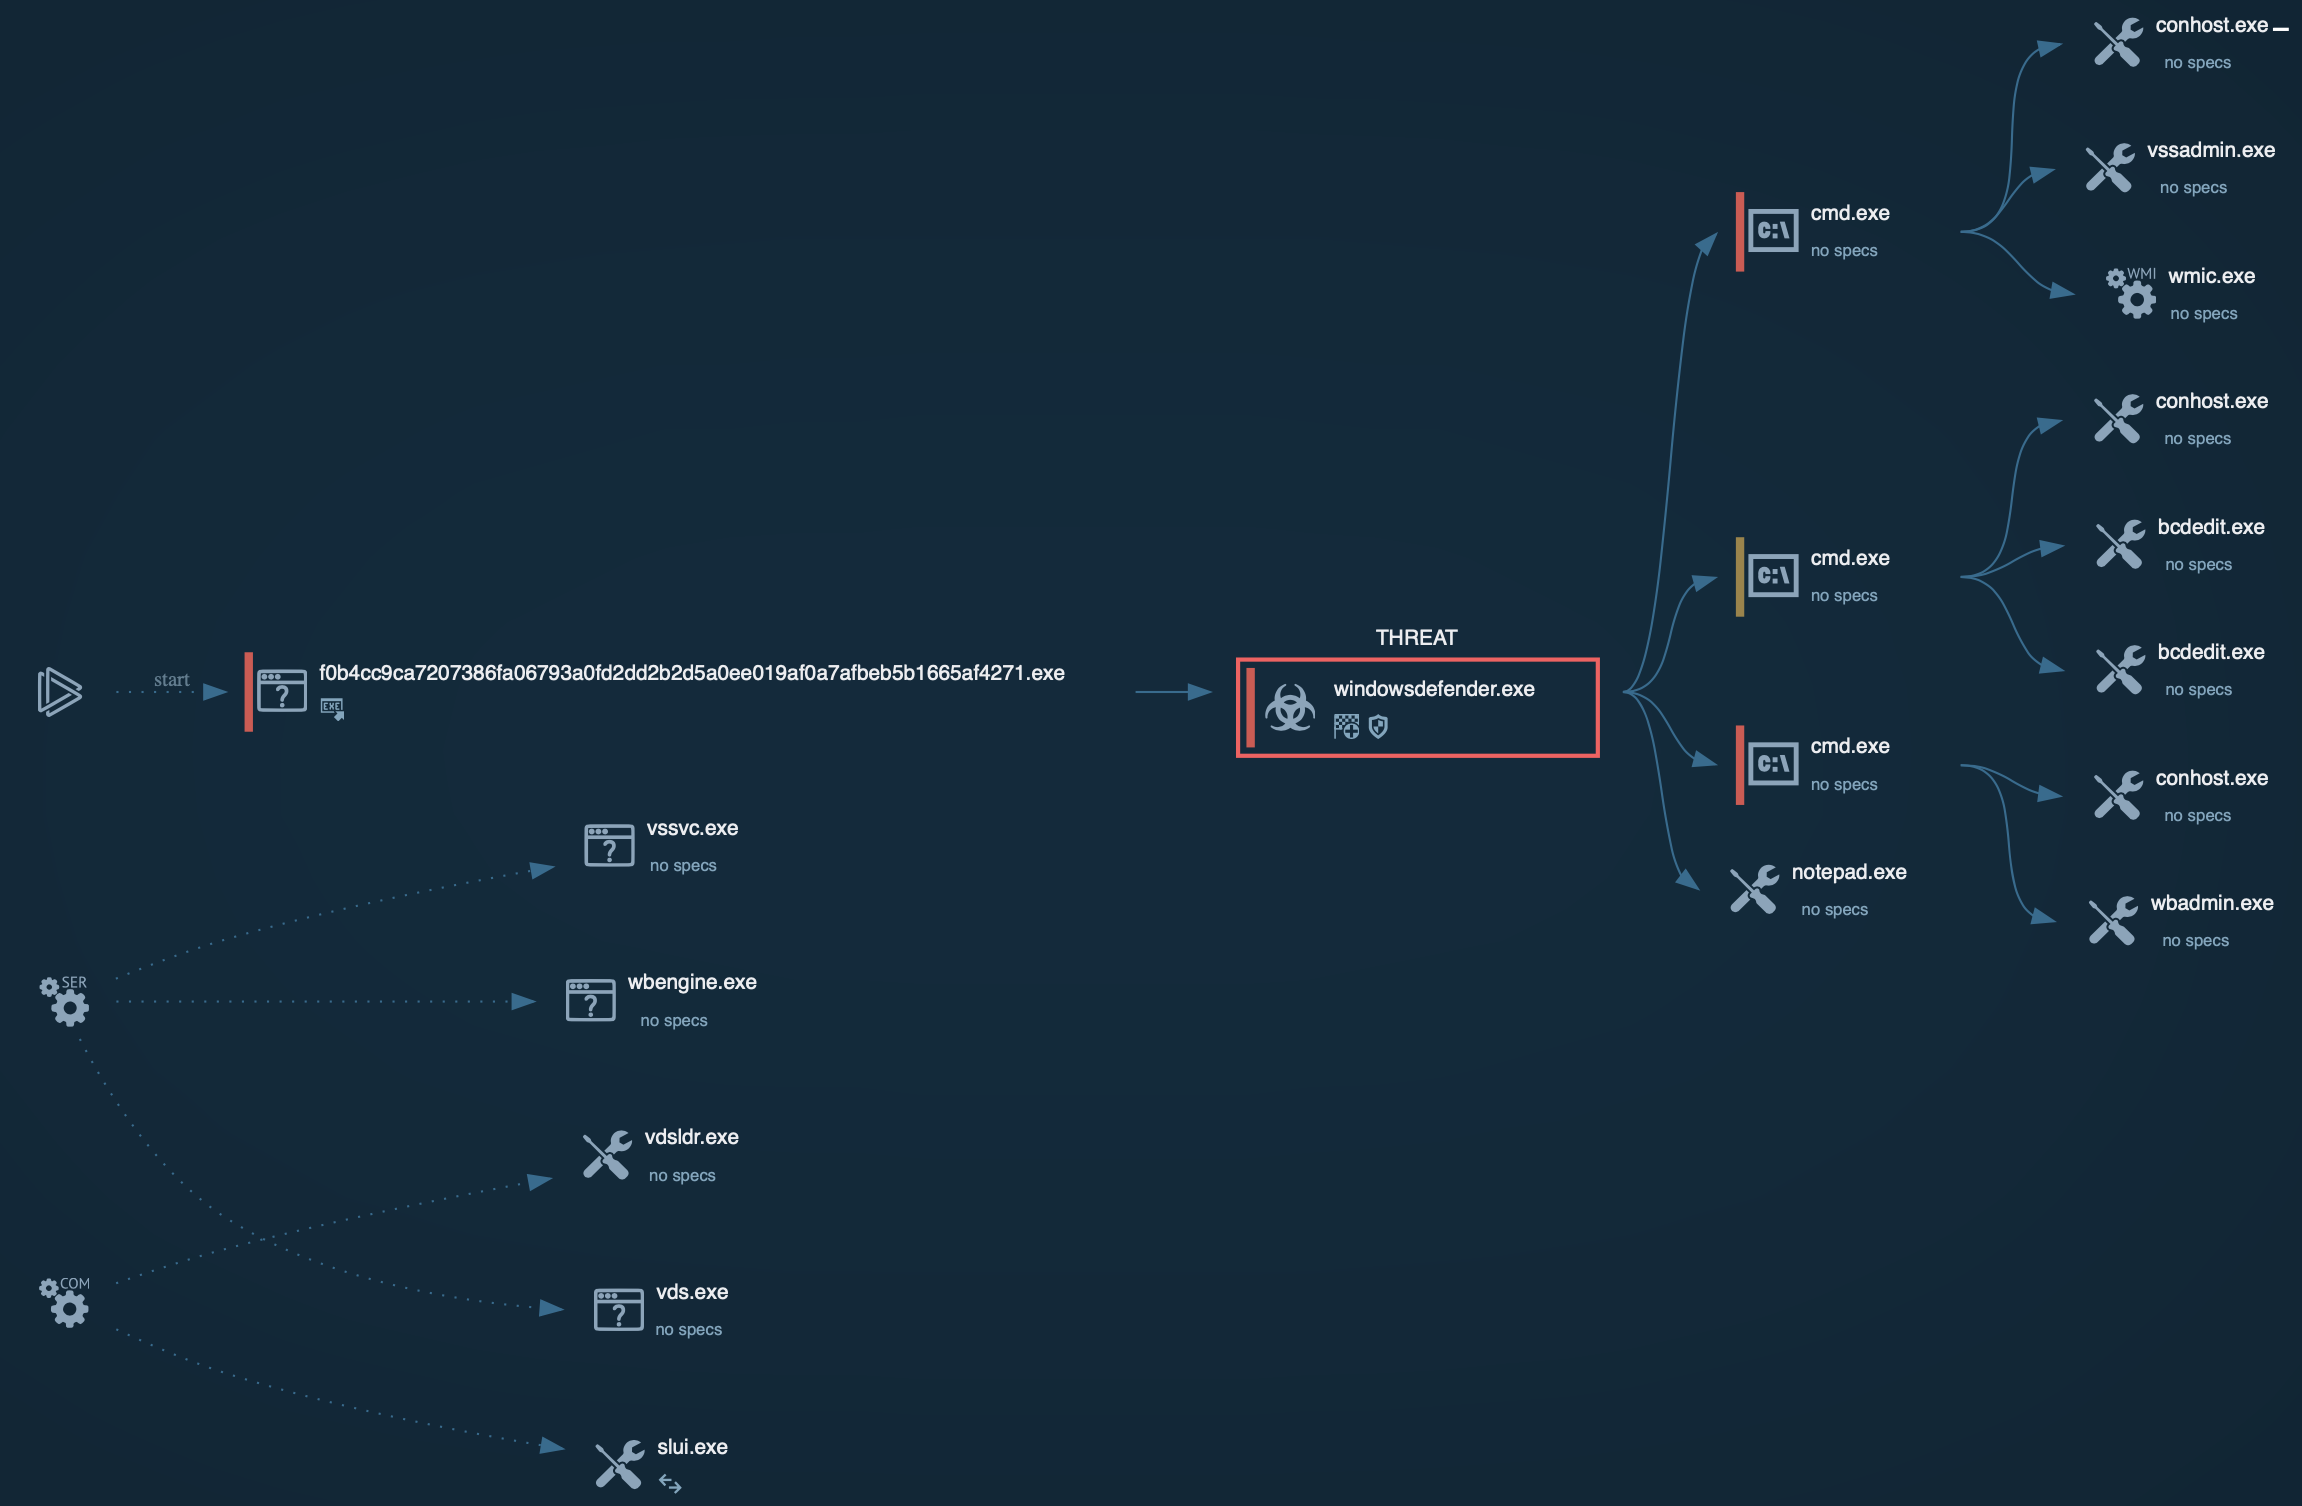
After persistence is in place, Chaos spawns a new process to encrypt the victim’s files. It targets specific extensions to maximize damage and uses vssadmin, WMIC, wbadmin, and bcdedit to delete shadow copies and disable other backup mechanisms. By scanning the file system and encrypting valuable data, it effectively blocks the user’s access. Chaos ransomware also changes the desktop wallpaper on the infected system.
When encryption is complete, Chaos may contact its command-and-control (C2) server to upload encryption keys and system details. This channel also delivers ransom-payment instructions and, if the attackers choose, additional payloads or a decryption key once payment is confirmed. Finally, the victim receives a ransom note outlining the steps required to regain access to their data.
What are the best-known Chaos attacks?
- “File Corruption” Campaigns (2021–2022). Many victims reported irrecoverable data loss instead of encryption. These attacks mostly hit small businesses and individuals. Chaos spread widely across forums, affecting users who downloaded pirated software or opened phishing emails.
- Targeting Healthcare & Education Sectors (2022). Chaos ransomware builders were used in several attacks against small hospitals, private schools and colleges, municipal organizations. Systems mostly were rendered unusable even if ransoms were paid.
- CHAOS 4.0 & 5.0 “Actual Encryption” Campaigns. More organized groups began using Chaos as an entry-level extortion tool, but these versions still lacked features of advanced ransomware (like data exfiltration). These versions switched from file destruction to proper AES encryption.
Chaos ransomware is not associated with famous victim names because:
- It’s a ransomware builder, not a specific group’s tool.
- It’s used by script kiddies, lone hackers, and non-sophisticated actors.
- It targets low-hanging fruit, like poorly secured RDP servers or people downloading pirated software.
- Most campaigns are uncoordinated, small-scale, and poorly operationalized.
Gathering Threat Intelligence on Chaos Ransomware
Threat Intelligence plays a key role in detecting and countering Chaos ransomware. IOCs must be gathered to enable monitoring and prevention: IP addresses and domains for C2 servers, file names and hashes.
Start with searching by the malware’s name via Threat Intelligence Lookup to find an assortment of fresh public analyses and harvest IOCs for tuning your security systems.
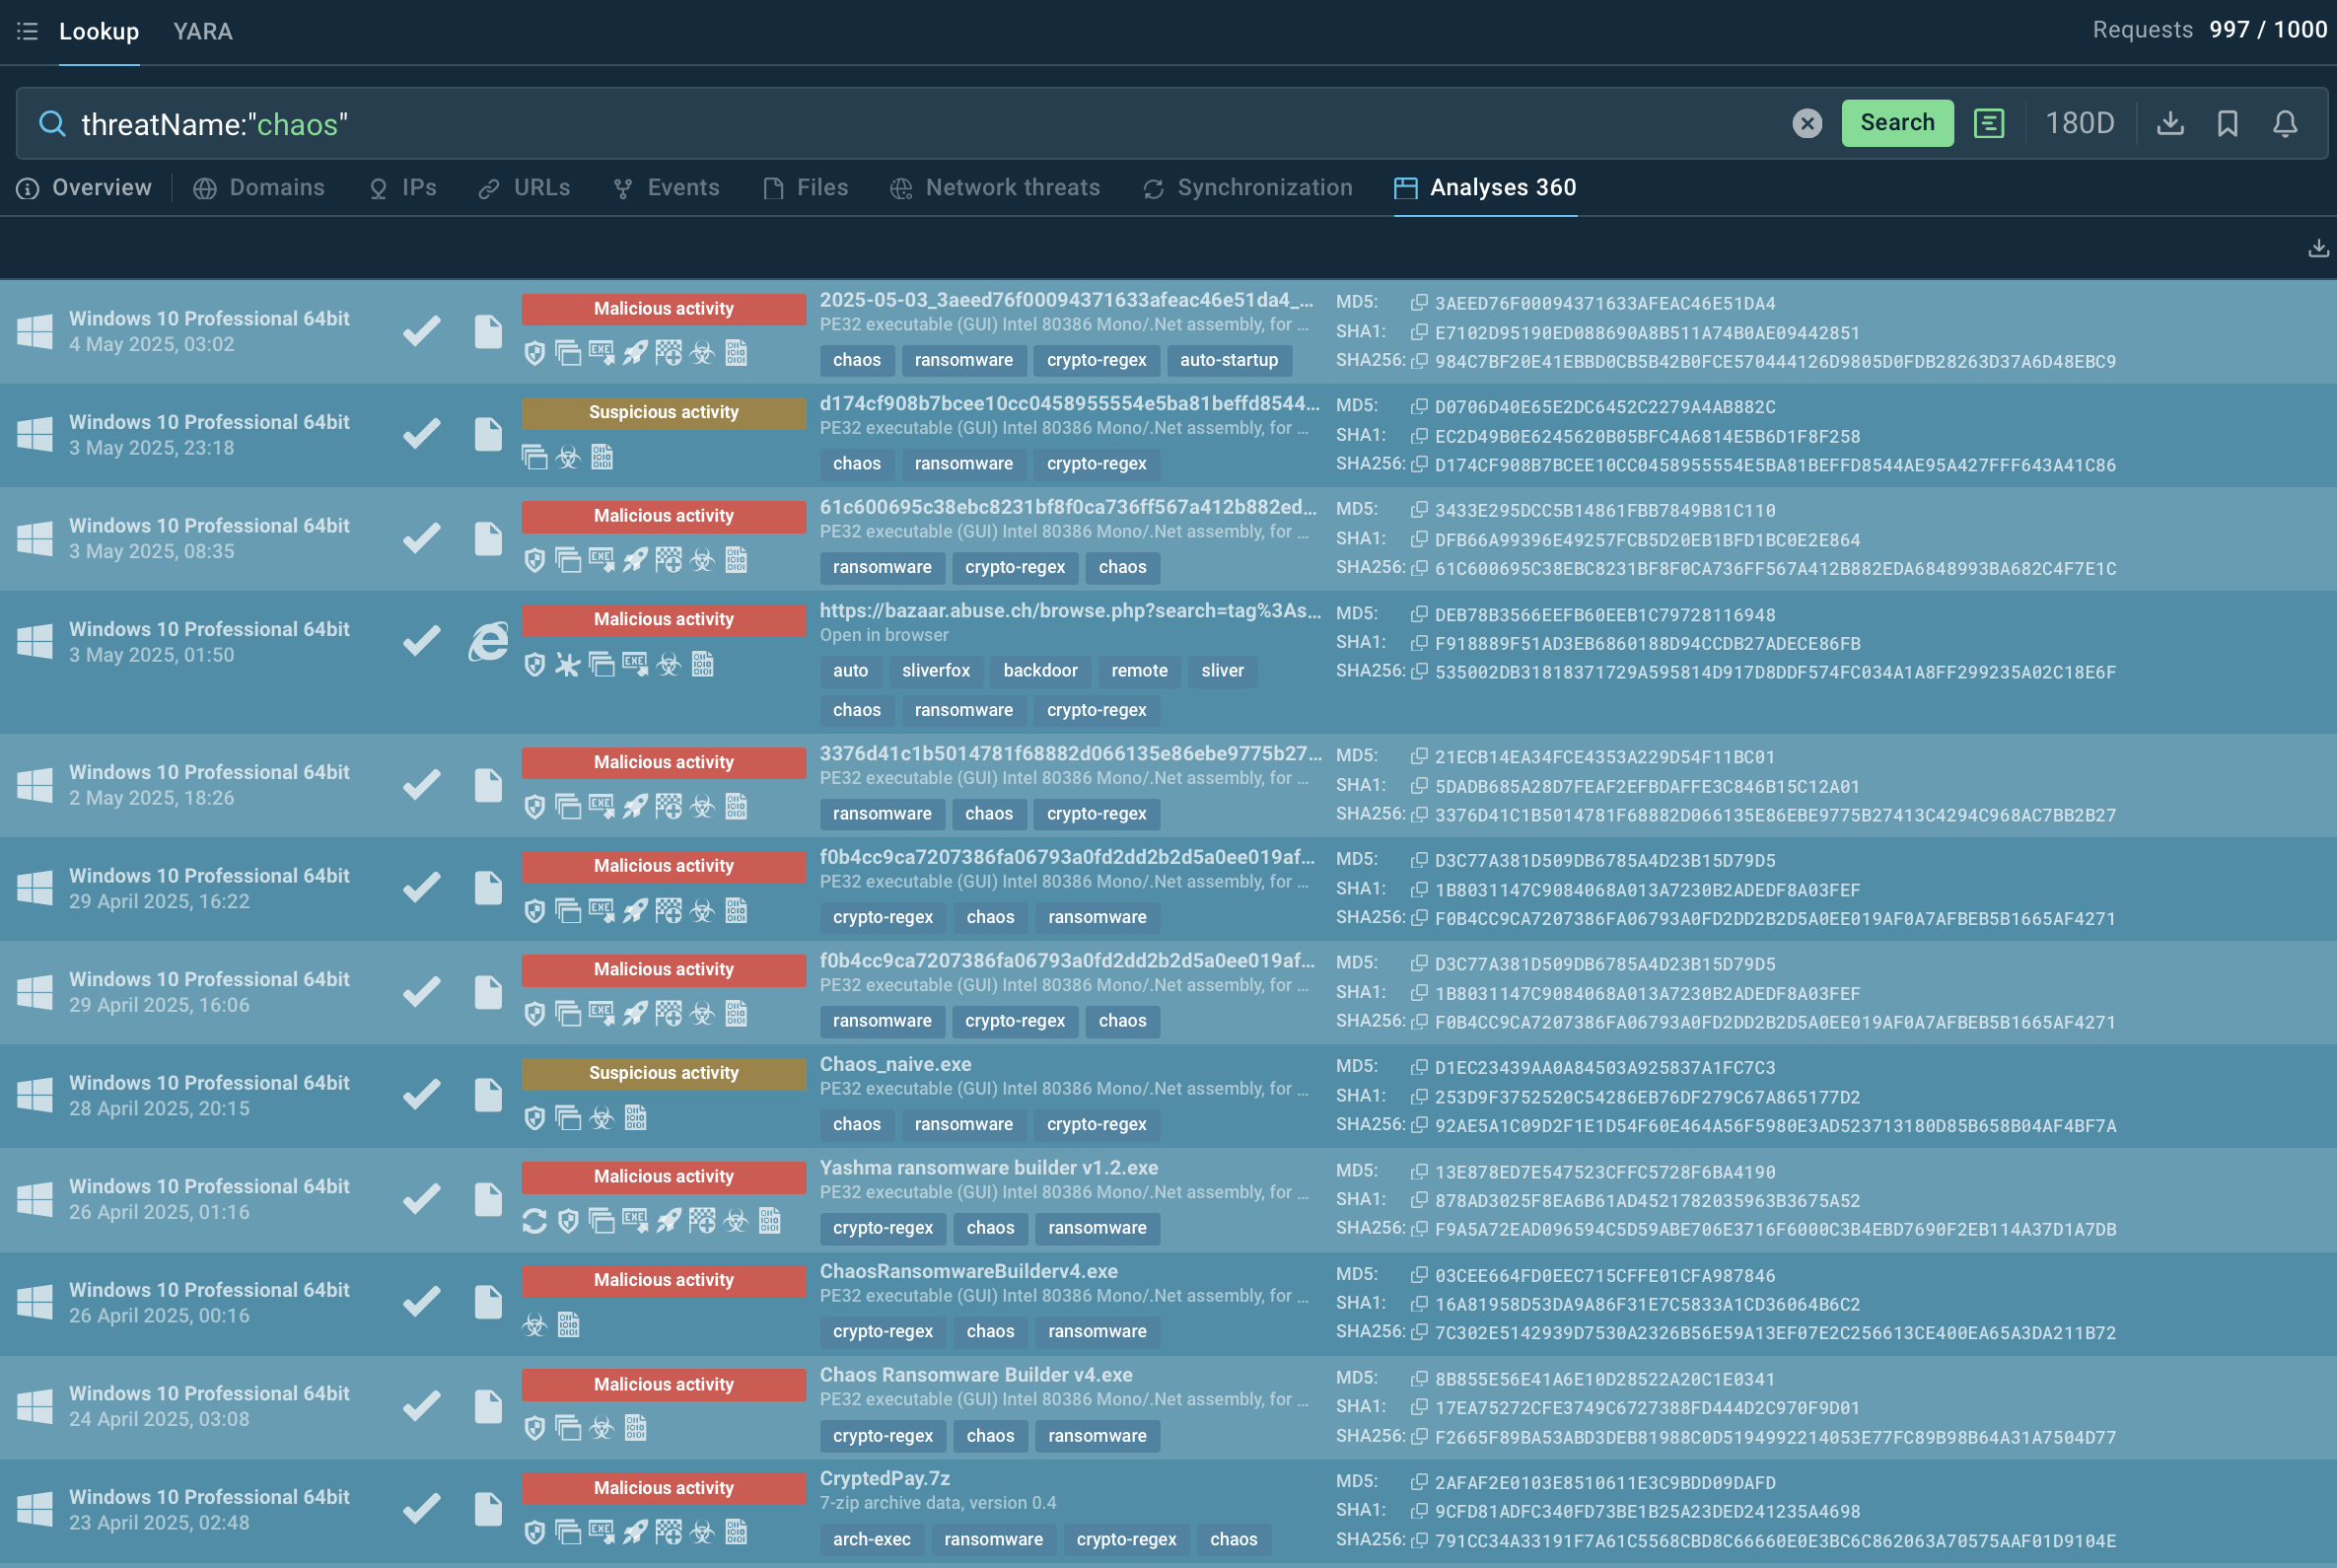
TI Lookup also provides sandbox reports containing behavioral analysis of Chaos samples. You'll be able to see how the use of vssadmin, bcdedit, and wbadmin to remove backups, overwriting of small files, unusual PowerShell or script activities trigger detection of Chaos variants.
Conclusion
Chaos ransomware is a multifaceted threat that combines ransomware, RAT, and DDoS capabilities. It is a significant risk to diverse industries, particularly those with unpatched systems or sensitive data. Its ability to infiltrate networks via phishing, exploits, and fake updates, coupled with advanced evasion techniques like port-hopping and binary obfuscation, requires robust detection and response strategies.
By leveraging threat intelligence, anomaly-based detection, and proactive countermeasures like Zero Trust and chaos engineering, organizations can mitigate Chaos’s impact.
Employ Threat Intelligence Lookup to counter Chaos: start with 50 test requests.
Other malware & phishing threats
 XWormXWorm is a remote access trojan (RAT) sold as a malware-as-a-service. It possesses an extensive hacking toolset and is capable of gathering private information and files from the infected computer, hijacking MetaMask and Telegram accounts, and tracking user activity. XWorm is typically delivered to victims' computers through multi-stage attacks that start with phishing emails.
 GootLoaderGootLoader is an initial-access-as-a-service malware that operates by delivering the GootKit banking trojan and other malicious payloads. It utilizes techniques such as fileless execution and process injection to avoid detection. The malware is often distributed through SEO poisoning and compromised websites, deceiving users into downloading infected files.
 Remote Access TrojanRemote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
 Balada InjectorBalada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
 GuLoaderGuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.