ClickLock
- 207
- Global rank
- 206
- Month rank
- 206
- Week rank
ClickLock is a macOS information stealer and remote backdoor distributed via deceptive, terminal-based social engineering pages. Once executed, it bypasses Gatekeeper checks by stripping download quarantine flags and signing its executable with ad-hoc digital certificates. If users resist its initial demands, the malware initiates high-frequency background loops that repeatedly kill vital operating system applications to force plaintext password entry. It exfiltrates captured browser data, system keychain credentials, and cryptocurrency wallets to a Telegram bot before establishing a permanent backdoor.
- Stealer
- Type
- Unknown
- Origin
- 1 May, 2026
- First seen
- 1 January, 1970
- Last seen
How to analyze ClickLock with ANY.RUN
Key Takeaways
- The "ClickFix" Social Engineering Vector: Initial access relies entirely on user deception, using fake browser verification screens (such as simulated Cloudflare CAPTCHA blocks) to trick users into copying and running terminal commands.
- Bypassing macOS Security Guardrails: The threat successfully evades built-in macOS defenses by silently stripping file quarantine flags and applying ad-hoc digital signatures to bypass Gatekeeper.
- High-Value Data Extraction Matrix: The malware is engineered to scrape a comprehensive vault of credentials, system logs, and digital assets, including records from 8 major web browsers, 31 cryptocurrency wallet extensions, and 7 password manager extensions. Silent, Long-Term Network Backdoor: While local data-harvesting modules are designed to clean up and delete themselves after exfiltration, the malware establishes permanent reverse shell access on the system using a customized open-source utility.
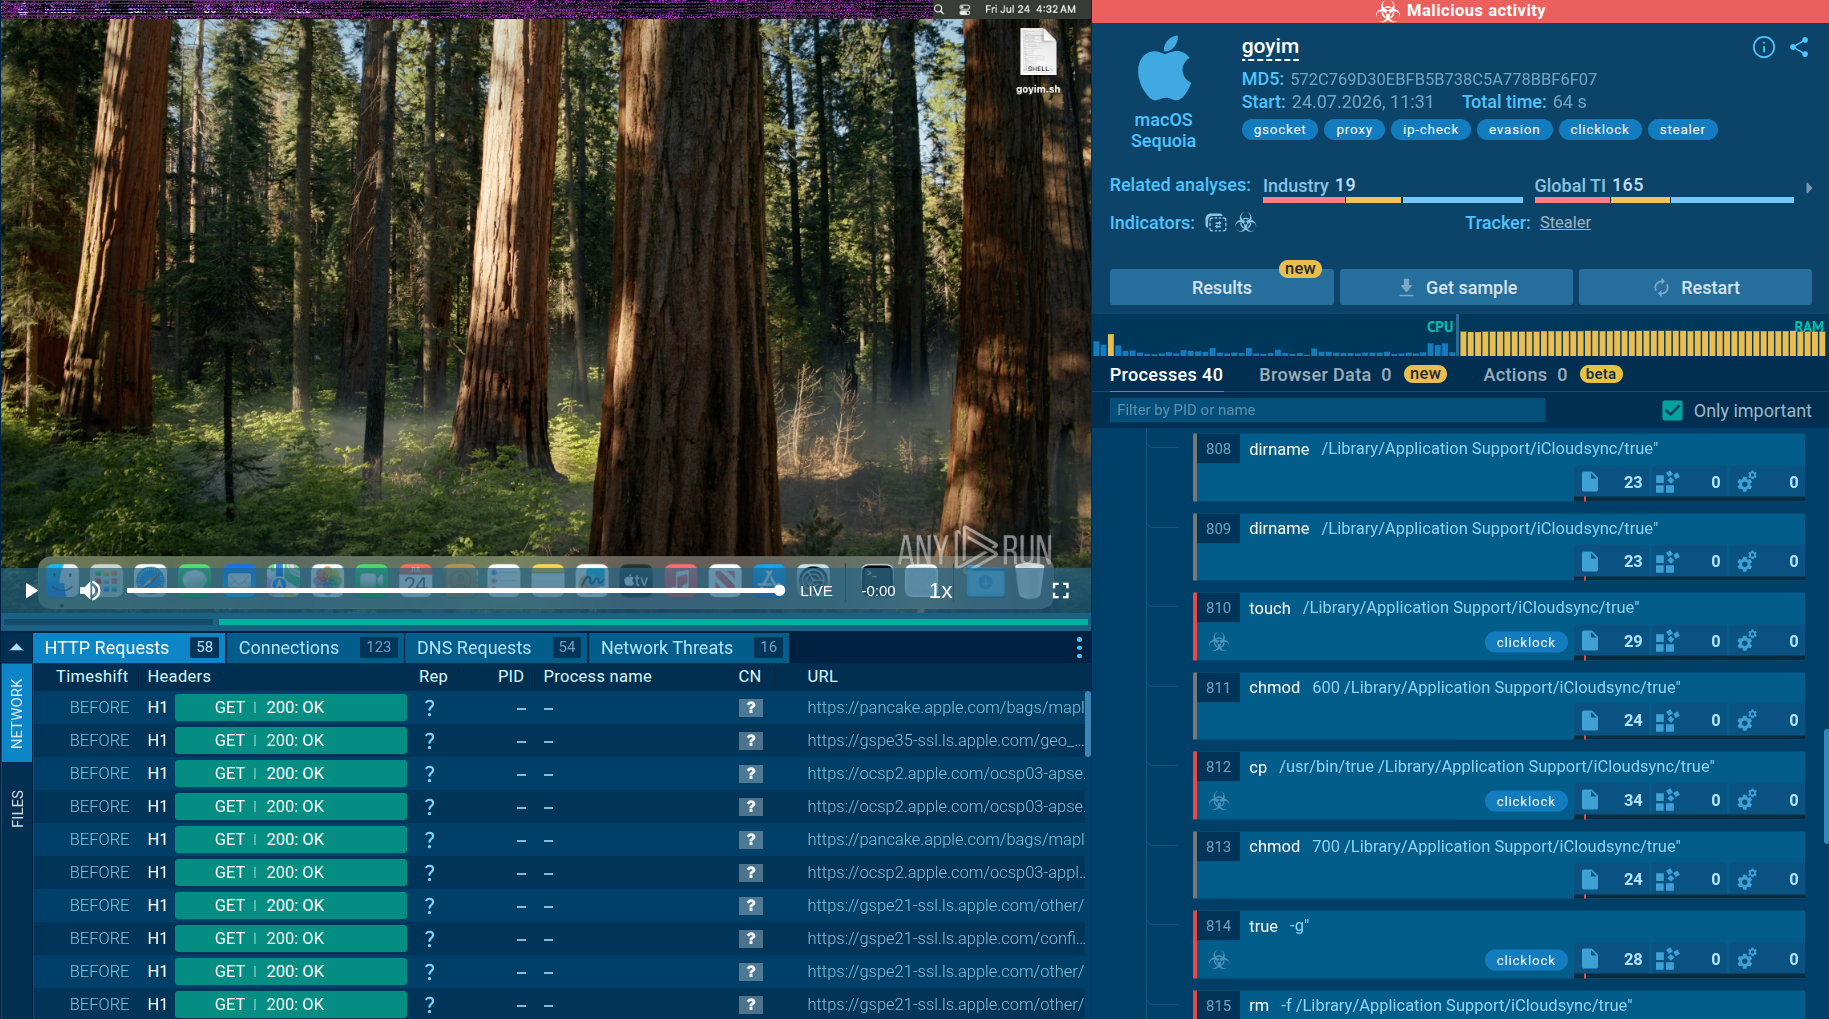
- Proactive SOC Sandboxing: Integrating interactive sandboxing within Security Operations Center (SOC) workflows is essential to proactively identify attacks like ClickLock, since the orchestrator bypasses traditional signature-based tools, detonating suspected payloads in a safe VM is the only reliable way for analysts to trigger and observe these sub-second process-killing loops and malicious keychain queries before they hit production endpoints.
What is ClickLock Stealer?
ClickLock Stealer is a newly documented macOS-focused information stealer and persistent backdoor developer. First discovered in May 2026 with zero initial detections, this threat is designed to secure an immediate, unmonitored foothold on Apple devices. Since its emergence, the campaign has compromised victims in across 30 countries, displaying a heavy geographic focus on high-income regions, with over 50% of its targets located in Europe.
The malware’s name is derived from the distinct combination of its delivery and enforcement mechanisms: it pairs "ClickFix" social engineering lures with "locker" process-termination tactics to coerce target users. Unlike traditional threats that attempt to run silently in the background or exploit complex system vulnerabilities, ClickLock Stealer requires no specialized software exploits or elevated system privileges to succeed. Instead, it relies on human-in-the-loop interaction, exploiting a single moment of user trust to initiate its infection chain.
Once active, the malware orchestrates several parallel modules to execute a thorough harvest of sensitive personal and corporate data. Similar to other stealers like ACR Stealer and Remus Stealer, it targets stored logins, cookies, and local data databases across major Chromium and Firefox-based browsers, while explicitly hunting for cryptocurrency wallet extensions, desktop wallets, and browser-based password managers. To decrypt these stolen browser databases offline, the malware forces the user to yield both their macOS login password and authorization for the system's underlying Chrome Safe Storage key. This combination of credential theft, telemetry blinding, and permanent backdoor installation ensures that the attacker retains continuous, remote access to the victim's digital environment long after the initial infection has completed.
How ClickLock Threatens Businesses and Organizations
For modern enterprises, ClickLock Stealer presents a severe risk by combining user coercion with long-term network persistence. Rather than attempting to remain silent, the malware actively disrupts system operations to achieve its goals.
The primary business risks associated with this threat include:
- Compromise of System-Level Credentials: By triggering persistent process-termination loops, the malware renders the victim’s desktop unusable until they input their macOS system login password. This gives attackers plaintext administrative credentials, which are often reused for corporate Single Sign-On (SSO) portals, VPNs, and internal network infrastructure.
- Offline Decryption of Corporate Databases: The malware specifically targets the macOS Keychain to extract encryption keys, such as the Chrome Safe Storage key. Acquiring this key allows attackers to exfiltrate browser databases and decrypt stored passwords, cookies, and session tokens offline. This bypasses local security boundaries and exposes sensitive corporate portal logins.
- Persistent Infrastructure Backdoors: While the local data-harvesting modules are designed to delete themselves after exfiltrating data, the malware leaves behind a modified open-source remote-access tool. This tool establishes a permanent, secure reverse shell back to the attacker, providing ongoing command execution and a backdoor into the corporate network that survives standard file cleanups.
- Bypassing Multi-Factor Authentication (MFA): By stealing active session cookies and credentials from major web browsers and popular password manager extensions, attackers can inherit the victim’s authenticated browser sessions. This enables threat actors to log directly into sensitive corporate cloud services without triggering multi-factor authentication prompts.
ClickLock Victimology: Who Is Most Vulnerable?
The target profile of ClickLock Stealer is highly opportunistic but strategically focused on environments with high-value digital assets. Its distribution methods and technical behavior exploit specific operational and regional vulnerabilities:
- Companies in EU and US: Most of the ClickLock victims are located in Europe, followed by North America and the Middle East and Africa (MEA), aligning with a financially-motivated focus on regions with high macOS market share and corporate wealth.
- Technical Staff and Power Users: Because the initial infection relies on the "ClickFix" technique. This threat is highly effective against developers, IT administrators, and power users. These individuals frequently use the terminal in their daily workflows, making them far more likely to trust a prompt requesting terminal-based verification.
- Cryptocurrency Holders and Financial Managers: The malware is heavily optimized to scan for, extract, and exfiltrate data from different cryptocurrency browser extensions, 8 desktop wallet applications, and cached blockchain addresses across multiple chains. This makes organizations in the Web3 space, financial services, or those managing digital corporate treasuries prime targets.
How Does ClickLock Malware Function?
Detonating a ClickLock Stealer sample inside ANY.RUN’s Interactive Sandbox exposes a highly calculated, multi-stage execution chain designed to bypass macOS security frameworks, force user compliance, and establish permanent remote access.
1. Deployment and Masquerading
When the malware first runs, it tries to hide itself on the computer. It creates a hidden folder at /Library/Application Support/iCloudsync/. It uses the name "iCloudsync" so it looks like a normal Apple service.
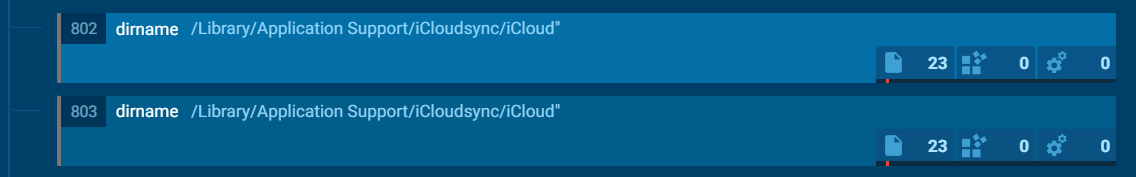
It uses chmod 600 to lock its files so regular users or security tools can't easily see them. It uses chmod 711 to make its main program runnable.
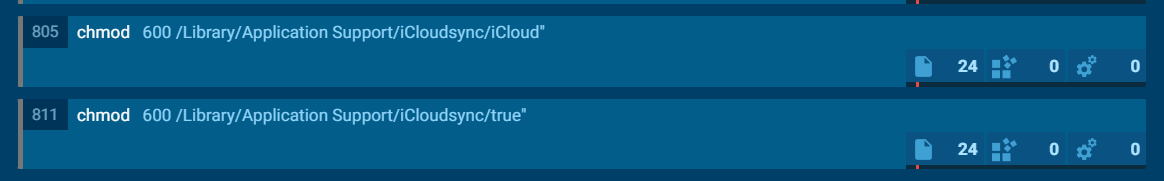
It uses xattr -d com.apple.quarantine to remove the standard Mac warning that pops up when you open downloaded files ("This file was downloaded from the Internet").

It uses codesign to add a basic code signature to the file. This tricks Mac's Gatekeeper protection into thinking the program is safe to run.

2. Persistence and Payload Execution
The malware copies a harmless, built-in Mac tool called true into its hidden folder. It uses this harmless file to trick the system while starting up.
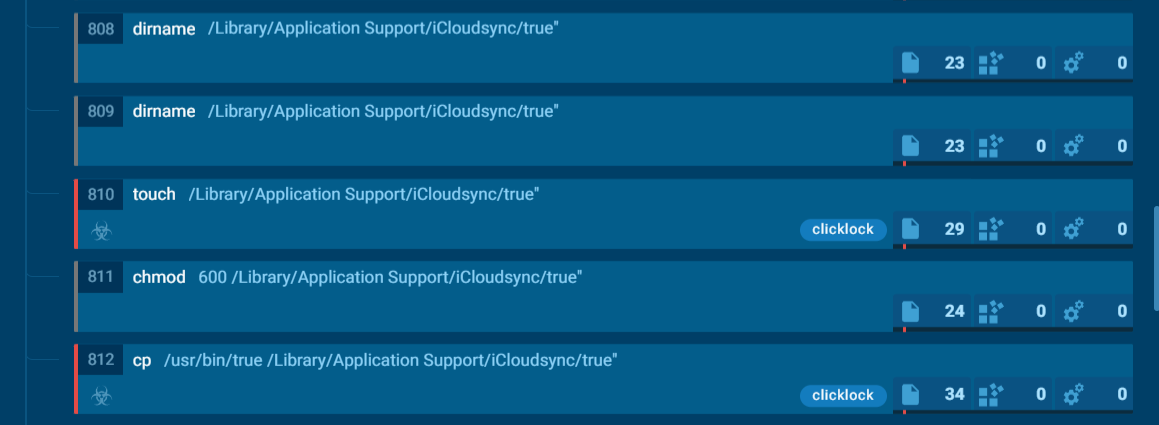
The main malware runs under the process name iCloud with a command line target of SystemUIServerl. This is a typo of a real Mac process (SystemUIServer), designed to blend in if someone checks Activity Monitor.
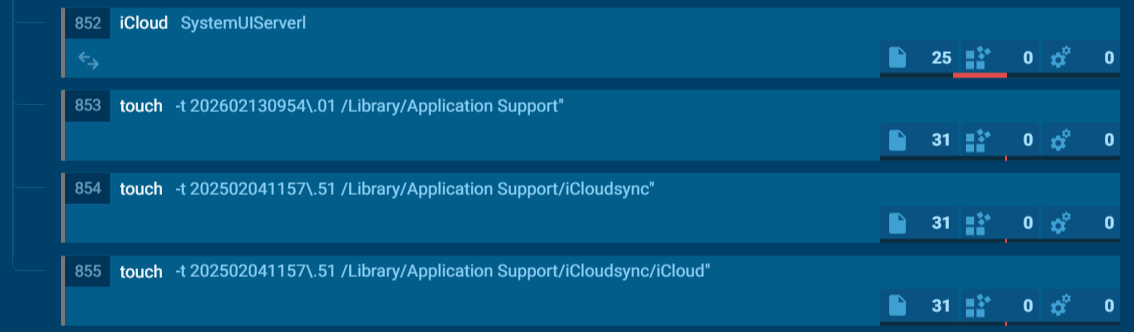
It uses touch commands to change file creation dates so they look older, hiding when the infection actually happened.
3. Reconnaissance
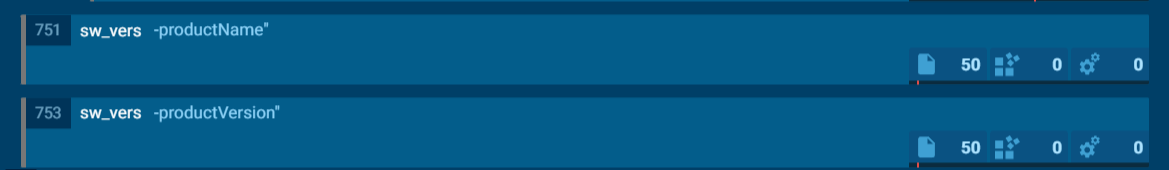
Concurrently, sw_vers processes (PID 751, 753) execute with -productName and -productVersion flags to harvest macOS version data, enabling the malware to adapt execution or confirm execution within a targeted host environment.
Integrate ANY.RUN's Interactive Sandbox in your SOC for early detection of ClickLock →
Conclusion
ClickLock Stealer demonstrates a fundamental shift in the macOS threat landscape, proving that attackers do not require sophisticated software exploits or zero-day vulnerabilities to successfully compromise secure systems. By shifting the attack focus from technical exploit development to human-in-the-loop social engineering, this threat leverages a single moment of user trust to bypass core operating system security boundaries. Once active on a machine, the combination of desktop lockout loops, telemetry blinding, and permanent backdoor installations allows attackers to secure indefinite remote control and decrypt stolen databases offline.
Frequently Asked Questions: ClickLock Stealer
1. What is ClickLock Stealer?
ClickLock Stealer is a sophisticated, newly identified macOS-focused information stealer and remote backdoor. It is designed to capture highly sensitive corporate and personal assets, including system login passwords, keychain encryption keys, session cookies, and digital wallets, while maintaining permanent remote access to the compromised machine.
2. How does the malware bypass standard macOS security features?
The malware bypasses built-in operating system security layers by running commands that strip standard download quarantine flags and apply ad-hoc digital signatures to its files. It also prompts the user to grant Full Disk Access to the command-line interface, exposing highly protected directories and databases to the harvester without exploiting any software vulnerabilities.
3. How does the malware force users to surrender their passwords?
If a victim attempts to reject the malware's initial prompts, ClickLock triggers a background loop that repeatedly terminates critical system user-interface components, desktop applications, and system monitors at sub-second intervals. This locks the screen and leaves a fake system authorization dialog as the only interactive element, rendering the desktop unusable until the user complies.
4. Why are traditional endpoint antivirus solutions unable to detect this threat?
At its discovery, the orchestrator script bypassed detection on major scanning engines completely, as it is primarily distributed through trusted, compromised websites and relies on user-initiated commands. Additionally, its temporary data-harvesting components are programmed to self-delete once exfiltration is complete, leaving behind very few physical files for scanners to flag.
5. How can interactive sandboxing help defend against ClickLock?
Interactive sandboxing allows defenders to detonate suspicious script sequences and safely map out hidden administrative actions, such as the rapid application-killing behavior, which automated systems often miss.
Other malware & phishing threats
 MetamorfoMetamorfo is a trojan malware family that has been active since 2018. It remains a top threat, focusing on stealing victims’ financial information, including banking credentials and other data. The malware is known for targeting users in Brazil.
 KeyloggerA keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
 MispaduMispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
 Oblivion RATOblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
 Blank GrabberBlank Grabber is an infostealer written in Python. It is designed to steal a wide array of data, such as browser login credentials, crypto wallets, Telegram sessions, and Discord tokens. It is an open-source malware, with its code available on GitHub and regularly receiving updates. Blank Grabber builder’s simple interface lets threat actors even with basic skills to deploy it and conduct attacks.
 RiseProRisePro, an information-stealing malware, targets a wide range of sensitive data, including credit cards, passwords, and cryptocurrency wallets. By compromising infected devices, RisePro can steal valuable information and potentially cause significant financial and personal losses for victims.