DEVMAN
- 186
- Global rank
- 196
- Month rank
- 194
- Week rank
DEVMAN is a fast-evolving malware family targeting Windows environments with a mix of credential theft, remote control capabilities, and persistence techniques typical of modern crimeware. Initially observed in early 2025, DEVMAN quickly became a favorite tool among cybercriminal groups thanks to its stealth, modular structure, and ability to bypass traditional AV solutions.
- Ransomware
- Type
- Unknown
- Origin
- 1 April, 2025
- First seen
- 11 September, 2026
- Last seen
How to analyze DEVMAN with ANY.RUN
IOCs
IP addresses
- 23.59.18.102
- 40.71.11.133
- 74.178.76.128
- 2.23.246.9
- 142.251.13.94
- 34.160.176.28
- 23.11.41.157
- 34.111.175.102
- 34.117.223.223
- 48.209.133.15
- 23.194.190.165
- 172.211.123.248
- 2.16.241.205
- 2.21.239.140
- 135.232.92.97
- 128.24.231.65
- 48.209.138.168
- 2.21.239.157
- 172.64.149.23
- 2.18.64.27
Hashes
- befea596b4676ccf7cc37ea8048044bfa0556c8931d76fdeeb693d20264e50d6
- 07854d2fef297a06ba81685e660c332de36d5d18d546927d30daad6d7fda1541
- eaab30ed3bde0318e208d83e6b0701b3ee9eb6b11da2d9fbab1552e8e4ce88f8
- 7d3d7c3b6e16591b894a5ce28f255cb136bb6c45f5038c3b120b44b413082e35
- c48e42e9ab4e25b92c43a7b0416d463b9ff7c69541e4623a39513bc98085f424
- ee1ed3b49720b22d5fda63d3c46d62a96ca8838c76ab2d2f580b1e7745521aa5
- 1b1aed169f2acfae4cf230701bda91229cb582ff2ce29a413c5b8fe3b890d289
- 5a00cc998e0d0285b729964afd20618cbaecfa7791fecdb843b535491a83ae21
- 54097cccae0cfce5608466ba5a5ca2a3dfeac536964eec532540f3b837f5a7c7
- 77739084a27cb320f208ac1927d3d9c3cac42748dbdf6229684ef18352d95067
- 18619b678a5c207a971a0aa931604f48162e307c57ecdec450d5f095fe9f32c7
- 7190fa9449fd51b4dac65d68c40530ff359c96229d1b7148b236f35dfa662db6
- 9655d302cfdd780e5eccfc297f277af2d2b87f8f850b1fee522efc82f0355cd8
- 581ae7382ea9ae4935984bb6f95411d2146e207f4bc39539a30a186d8d68f17a
- 8f7a066fba201d4bb9aa992e0bddad1162618beebaff5c47943a32328b57e21a
- 6fac3cba525b7d4b75e056c6c5c849840eaa70436032985f0914e1ba69b967f0
- 7f047d62d9f647fb1ca8d7fd7227528c781c0a13e4c5cc5e830c261bd8babee7
- b72211ff34392a0c9bcb52424a7392f45b490b77302c0753d61b5294ce865a6f
- 52f9047e9a072554a68045fd0215b8484c2d6d758fee82543fbaa7c7f7d163d9
- 5276fcecf37e5ff6cb3e0b081c97a02e3648bf2e442e4f7f07dcb53acfa3c3ac
Domains
- www.microsoft.com
- client.wns.windows.com
- www.ccleaner.com
- softwareupdatechecker.live-everest-media.net
- c.pki.goog
- fe3cr.delivery.mp.microsoft.com
- slscr.update.microsoft.com
- ocsp.rootca1.amazontrust.com
- go.microsoft.com
- google.com
- settings-win.data.microsoft.com
- crl.microsoft.com
- self.events.data.microsoft.com
- ocsp.digicert.com
- download.ccleaner.com
- ncc.avast.com
- activation-v2.sls.microsoft.com
- login.live.com
- ocsp.comodoca.com
- shepherd.ff.avast.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
- https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
- https://login.live.com/rst2.srf
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://login.live.com/ppsecure/deviceaddcredential.srf
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
- http://ncc.avast.com/ncc.txt
- http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
- http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
- https://analytics.avcdn.net/receive3
- http://ocsp.pki.goog/gsr1/mfewtzbnmeswstajbgurdgmcgguabbs3v7w2naf4fimtjpdjkg6%2bmggqmqquyhtmgkunl8qjuc99bm00qp%2f8%2fuscehe9dwzbnvka6iepxpby0w0%3d
Last seen at
- df5ab9015833023a03f92a797e20196672c1d6525501a9f9a94a45b0904c7403.exe
- webOS.Dev.Manager_1.99.20_x64_en-US.msi
- webOS.Dev.Manager_1.99.20_x64_en-US.msi
- windows-41a024ec-c787-443a-a5f5-0fe62be122e4.exe
- windows-41a024ec-c787-443a-a5f5-0fe62be122e4.exe
- df5ab9015833023a03f92a797e20196672c1d6525501a9f9a94a45b0904c7403.exe
- df5ab9015833023a03f92a797e20196672c1d6525501a9f9a94a45b0904c7403.exe
- bazaar.abuse.ch
- df5ab9015833023a03f92a797e20196672c1d6525501a9f9a94a45b0904c7403.exe
- bazaar.abuse.ch
From Conti Clone to RaaS King: DEVMAN’s 2025 Rampage Exposed
Key Takeaways
- Global Reach, Regional Focus: Over 120 victims since April 2025, hitting Asia/Africa hardest but sparing no sector except pediatric care.
- Double-Extortion Mastery: Pairs encryption with massive exfiltrations (e.g., 2.5 TB), scaling ransoms to millions for high-revenue targets.
- Code Reuse Fuels Speed: DEVMAN's DragonForce/Conti foundations enable rapid deployment but introduce bugs like self-encrypting notes, exploitable for detection.
- SMB and GPO Propagation: Relies on network shares and policies for stealthy spread, bypassing traditional perimeter defenses.
- RaaS Democratization: DEVMAN 2.0's affiliate model (78-93% cuts) floods the market with attacks, requiring ecosystem-wide vigilance.
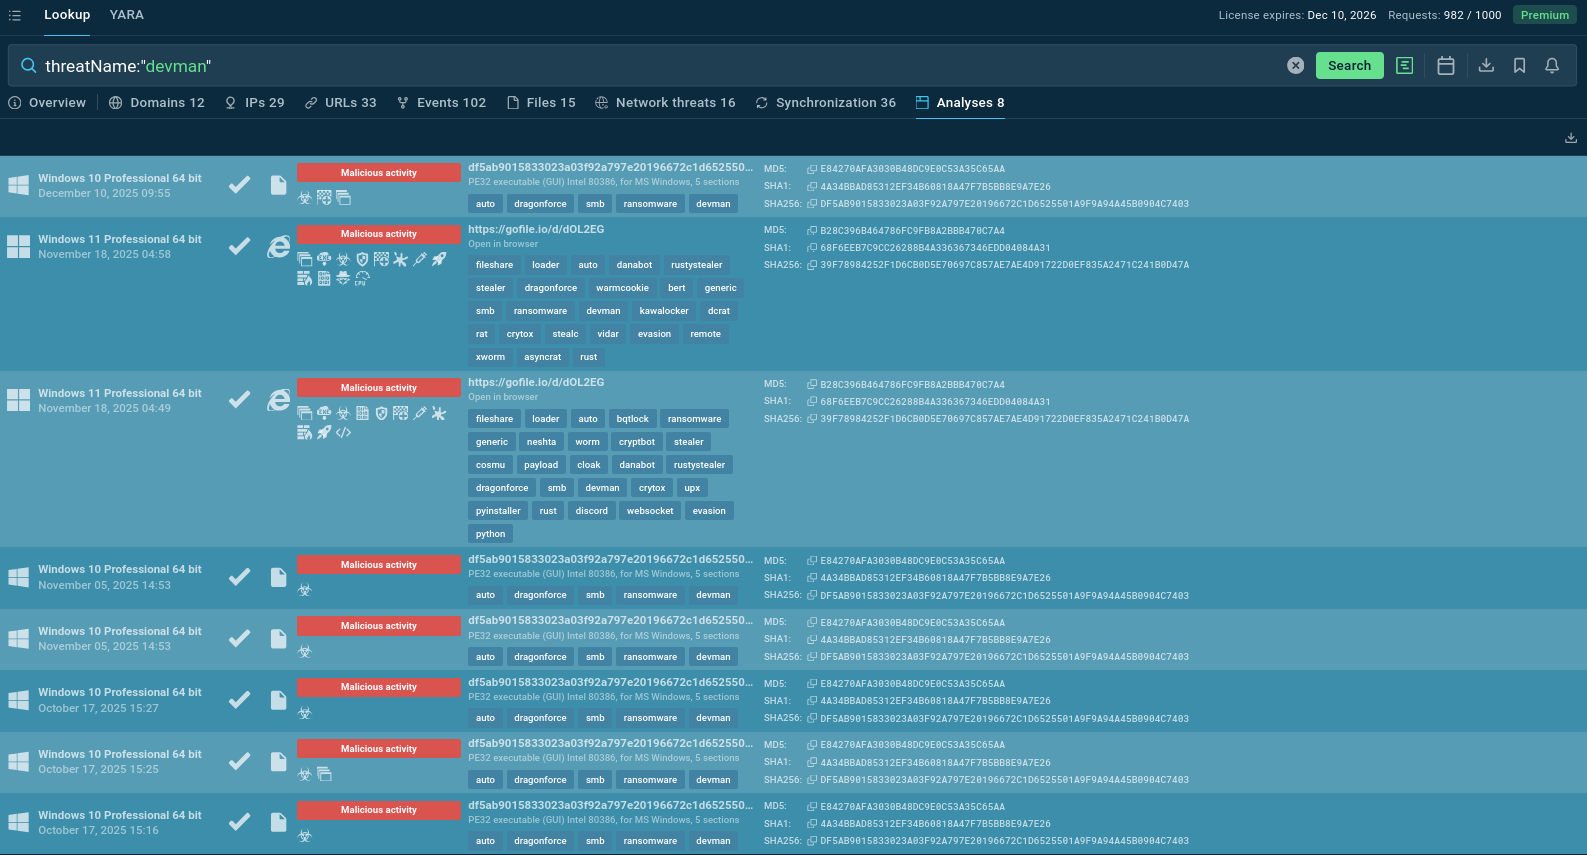
- Leverage Threat Intelligence Lookup for Proactive Defense: Services like ANY.RUN’s TI Lookup aggregate real-time IOCs and TTPs from DEVMAN's malware samples, empowering teams to block threats before encryption hits. Search by the ransomware’s name to explore sandbox analysis sessions and gather indicators.
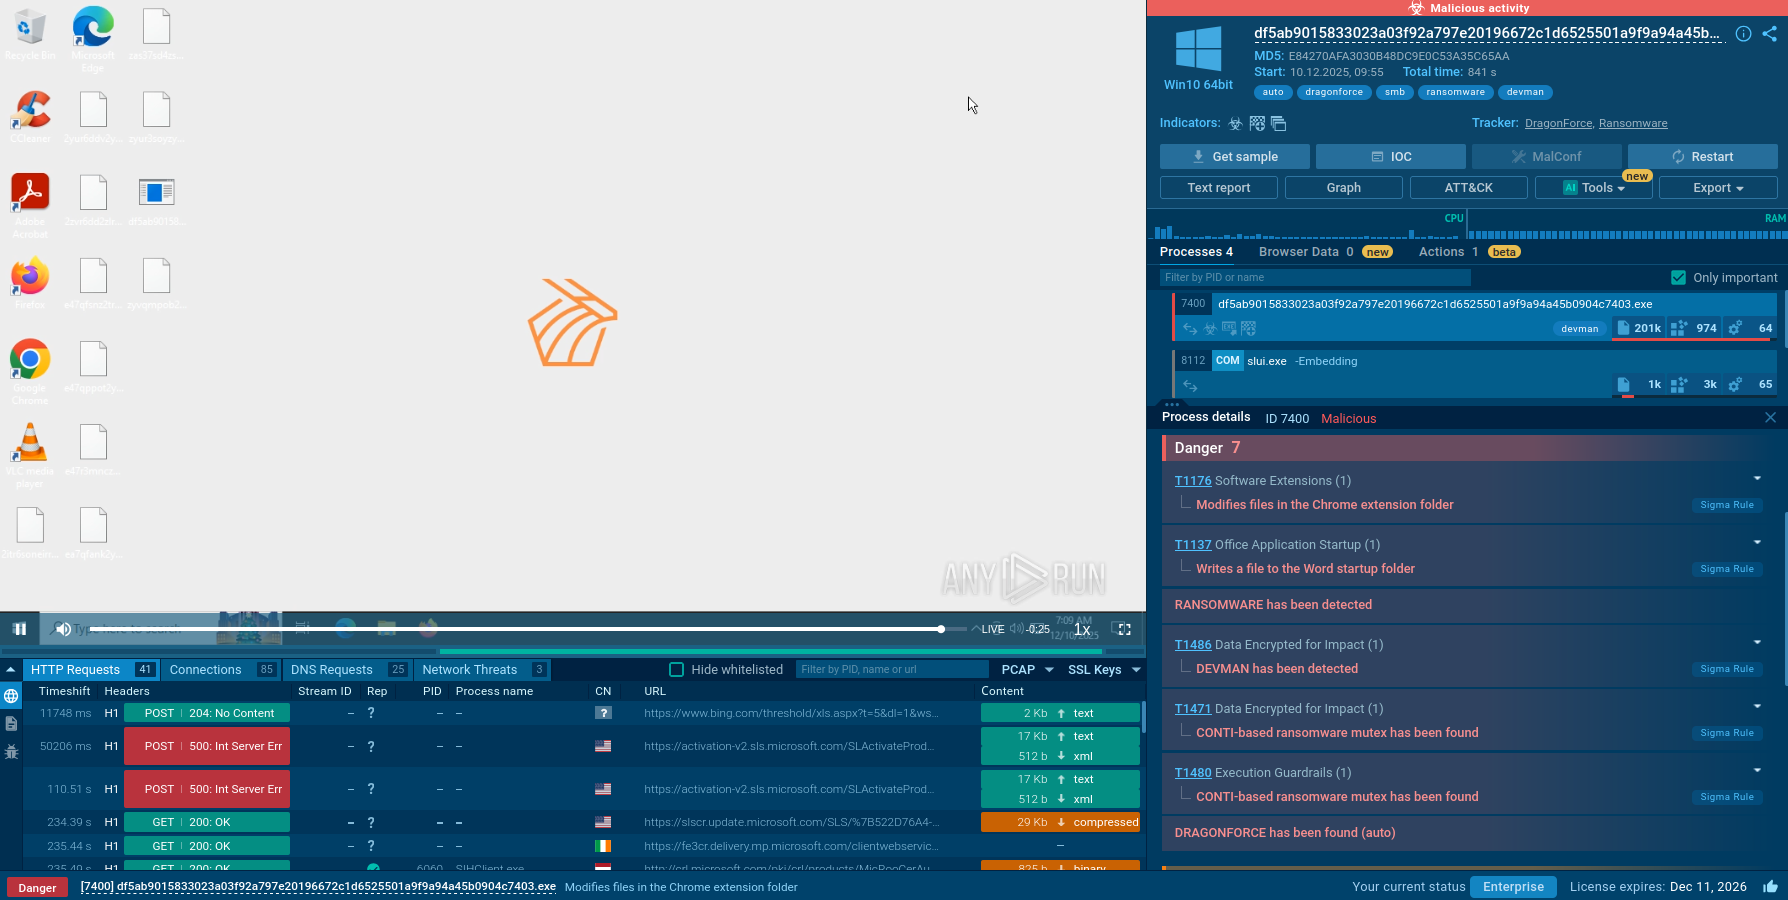
- ANY.RUN's Interactive Sandbox provides unparalleled visibility into DEVMAN's complex behaviors through real-time logging of file system changes, registry modifications, and mutex creation. The platform's interactive analysis capabilities enable security teams to investigate unusual variants, extract comprehensive IOCs, and understand threat evolution — critical advantages when defending against rapidly changing ransomware families like DEVMAN.
What is DEVMAN Ransomware?
DEVMAN ransomware emerged in early 2025 as a sophisticated threat that shares its genetic code with two notorious predecessors: DragonForce and Conti. This ransomware uses the .devman file extension for encrypted files and evolved from DragonForce code, representing a new chapter in the ongoing evolution of ransomware-as-a-service operations. It has proven to be a persistent and evolving threat with over 120 documented victims across multiple continents.
The malware implements three distinct encryption modes: full encryption for comprehensive data corruption, header-only encryption for speed optimization, and custom encryption for targeted scenarios. This flexibility allows attackers to balance speed against thoroughness depending on their objectives.
The ransomware operates almost entirely offline, with no external command-and-control communication observed during analysis. Instead, it relies on local SMB probing to facilitate lateral movement within compromised networks. DEVMAN creates a temporary session under the registry key HKEY_CURRENT_USER\Software\Microsoft\RestartManager\Session0000 to bypass file locks, a technique inherited from its Conti lineage that enables encryption of active user session files.
One of the most distinctive characteristics is its use of a hardcoded mutex named "hsfjuukjzloqu28oajh727190" to prevent multiple instances from running simultaneously. This anti-reentry mechanism is standard among Conti-derived ransomware families and provides a reliable indicator of compromise for defenders.
The ransomware also contains notable flaws that suggest rushed development or incomplete testing. Due to builder misconfiguration, the malware often encrypts its own ransom notes, making them inaccessible to victims. Additionally, the wallpaper-changing function works on Windows 10 but fails on Windows 11, indicating compatibility issues or incomplete adaptation to newer operating systems.
DEVMAN Ransomware Victimology
DEVMAN primarily targets mid-to-large enterprises in non-Western markets, with a heavy focus on Asia (e.g., Thailand, Indonesia) and Africa (e.g., healthcare and government sectors), though it has expanded to Europe, Latin America, and North America.
The group favors critical infrastructure, including transportation, social security funds, and media outlets, as well as healthcare providers (excluding pediatric cases to avoid backlash).
Early victims included government agencies and funds with massive data hauls (e.g., 2.5 TB exfiltrated from a national social security entity via compromised RDP). By May 2025, DevMan claimed 13 victims in a single month, rivaling top-tier groups, and has since amassed nearly 120 confirmed cases. Sectors hit hardest include manufacturing, finance, and public services, with ransoms scaling from $50,000 for smaller entities to over $2.5 million for high-revenue targets, often auctioned if unpaid.
How DEVMAN Ransomware Functions
The group functions as an affiliate across multiple Ransomware-as-a-Service platforms while also conducting direct attacks with their proprietary toolset.
Primary infection vectors include compromised Remote Desktop Protocol (RDP) connections. The group gains initial access via VPN and RDP connections, often using stolen credentials or password spraying attacks.
Phishing campaigns serve as another significant attack vector. Exploitation of edge-facing services represents a third major vector. The group exploits VPN gateways and remote management interfaces through vulnerabilities in public-facing applications.
DEVMAN implements faster lateral movement via Group Policy Object deployment from compromised domain controllers. This allows rapid propagation across enterprise environments once administrative credentials are obtained.
DEVMAN’s evolution includes the use of various tools for reconnaissance and privilege escalation. BloodHound is deployed for Active Directory attack path visualization, while SoftPerfect Network Scanner facilitates network reconnaissance. These tools enable sophisticated understanding of the target environment before encryption begins.
The ransomware uses hybrid cryptography combining AES-256 symmetric encryption for speed with RSA-2048 asymmetric encryption for key protection. This combination ensures both rapid file processing and cryptographic security that prevents decryption without the attacker's private key.
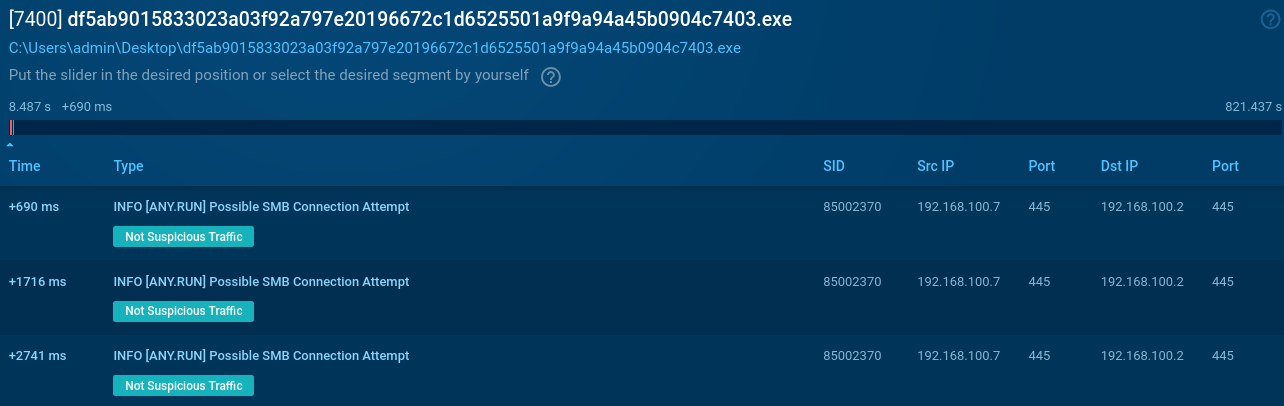
The execution flow begins with environment reconnaissance. DEVMAN enumerates all accessible drives and network shares, building a comprehensive target list. The malware specifically probes for SMB shares within local network ranges, attempting to spread laterally to maximize impact across the organization.
Persistence mechanisms leverage the Windows Restart Manager API in a manner characteristic of Conti-derived malware. The ransomware logs metadata for critical files, identifies processes locking those files, and forces their termination or restart to gain encryption access. Registry entries are created under the Restart Manager session key, then rapidly deleted to minimize forensic traces.
Process execution follows a carefully orchestrated sequence. The malware first disables security tools where possible, deletes shadow copies to prevent recovery, and empties recycle bins. Only then does encryption begin, with the ransomware processing files according to the selected mode while avoiding system-critical extensions that would render the machine unbootable.
The ransom note generation process contains a critical flaw. Due to a builder flaw, the ransomware encrypts its own ransom note files, renaming them deterministically to e47qfsnz2trbkhnt.devman. This means victims may not receive payment instructions, effectively severing the communication channel needed for ransom negotiation.
Network activity is deliberately minimal. Unlike many modern ransomware variants that maintain constant communication with command servers, DEVMAN operates in an almost completely offline mode. The only network traffic involves SMB scanning for lateral movement opportunities, making network-based detection more challenging.
Sandbox Analysis of a DEVMAN Sample
ANY.RUN’s Interactive Sandbox provides isolated, instrumented environments where security researchers and analysts can safely execute suspicious files without risking production systems.
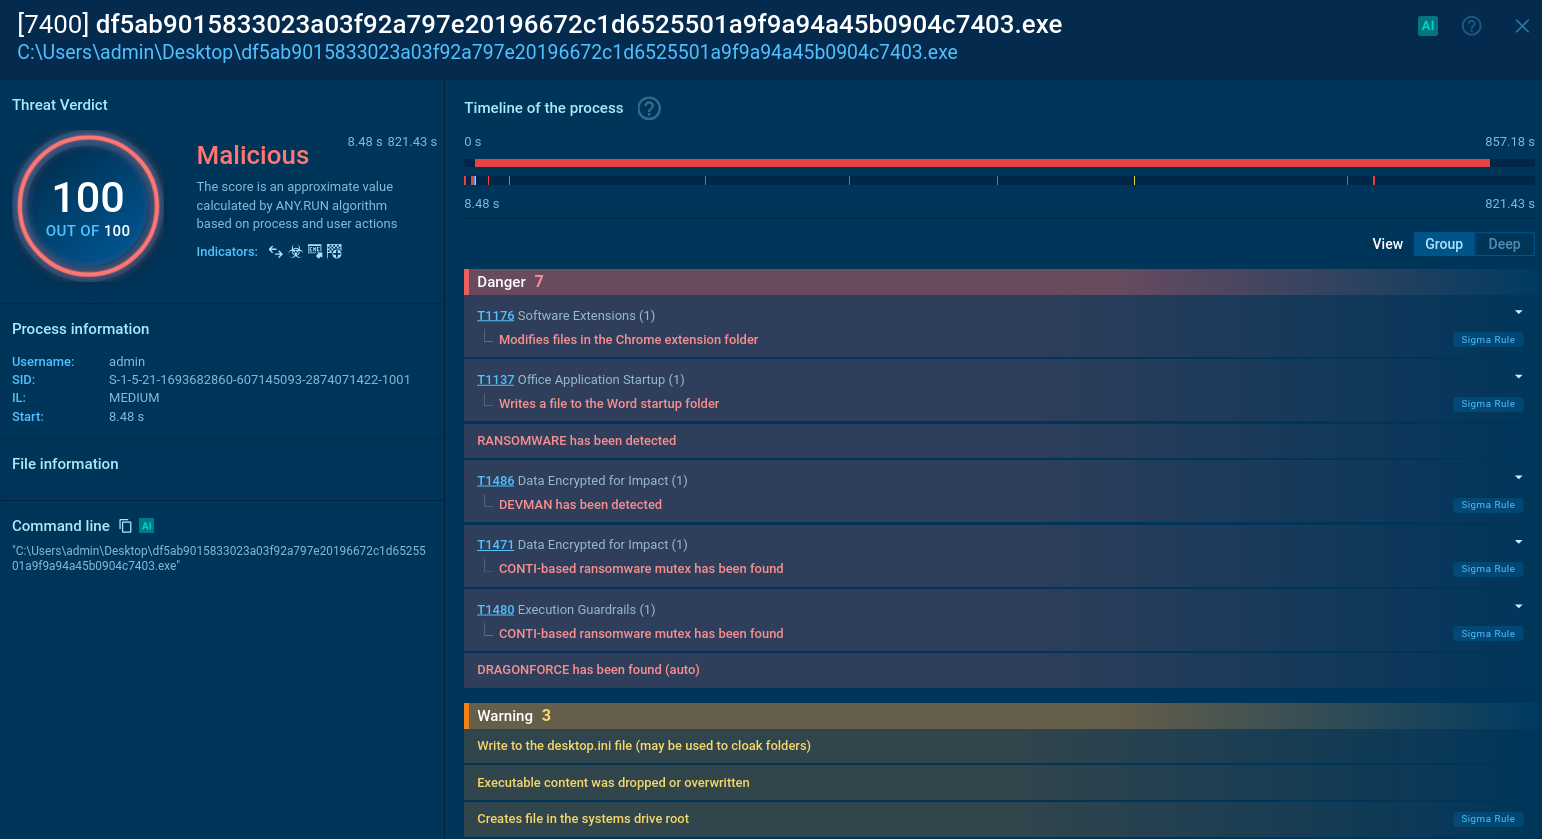
An analyst can view the ransomware’s process tree mapped to MITRE ATT&CK Matrix, explore connections, files, scripts, registry changes and more.
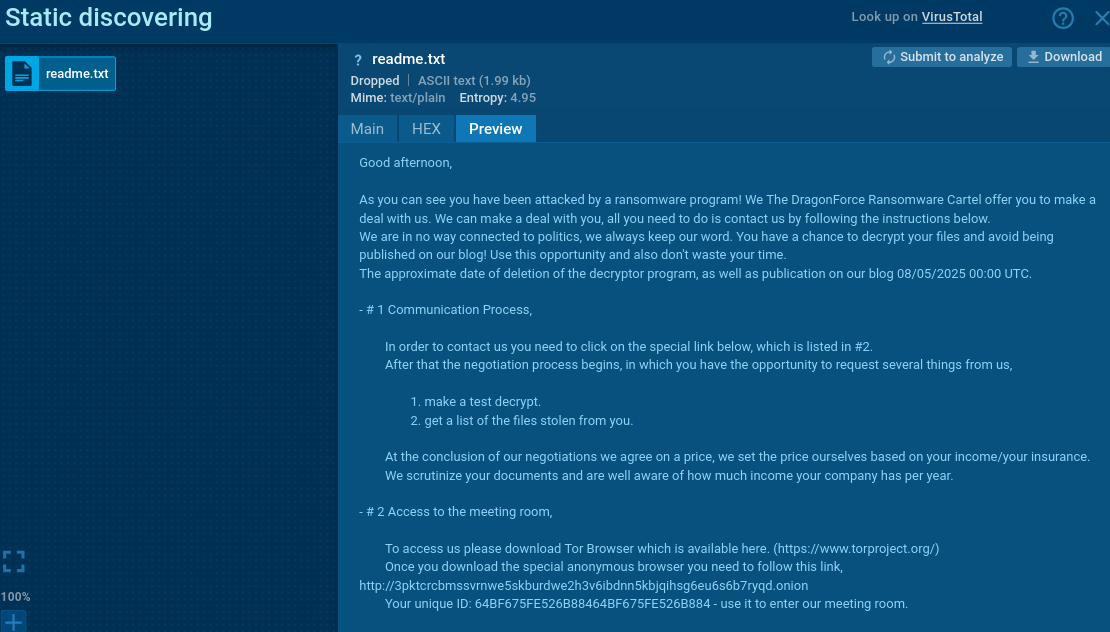
For example, one can view DEVMAN’s ransom note with a reference to DragonForce:
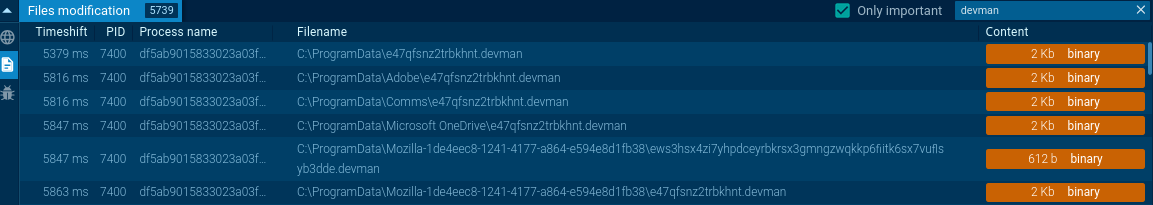
Or observe DEVMAN converting filenames via a specific function and adding a .devman extension.
The ransomware scans for SMB shares for lateral movement.
Examples of the Most Successful DEVMAN Ransomware Attacks
DEVMAN’s most impactful strikes highlight its efficiency in high-stakes sectors:
French Transport Authority (April 2025): Initial claim via X (formerly Twitter), with full network encryption disrupting operations; exact ransom undisclosed but marked DEVMAN’s debut as a standalone threat.
Thai Media Outlet (May 2025): Exfiltrated 170 GB using a customized encryptor with ".devman" extension; screenshots showed domain controller access and GPO deployment, with data offered for single-buyer sale post-encryption.
National Social Security Fund (Early 2025): Compromised via RDP, yielding 2.5 TB exfiltration; ransom demand hit $2.5 million, showcasing DevMan's scale against critical public services.
Abdulhadi Hospital and Easter Seals (December 2025): Recent healthcare hits with 246 GB and 236 GB stolen, respectively; ransoms of $350k and $90k, emphasizing permissible targeting of adult medical data.
Gathering Threat Intelligence on DEVMAN Malware
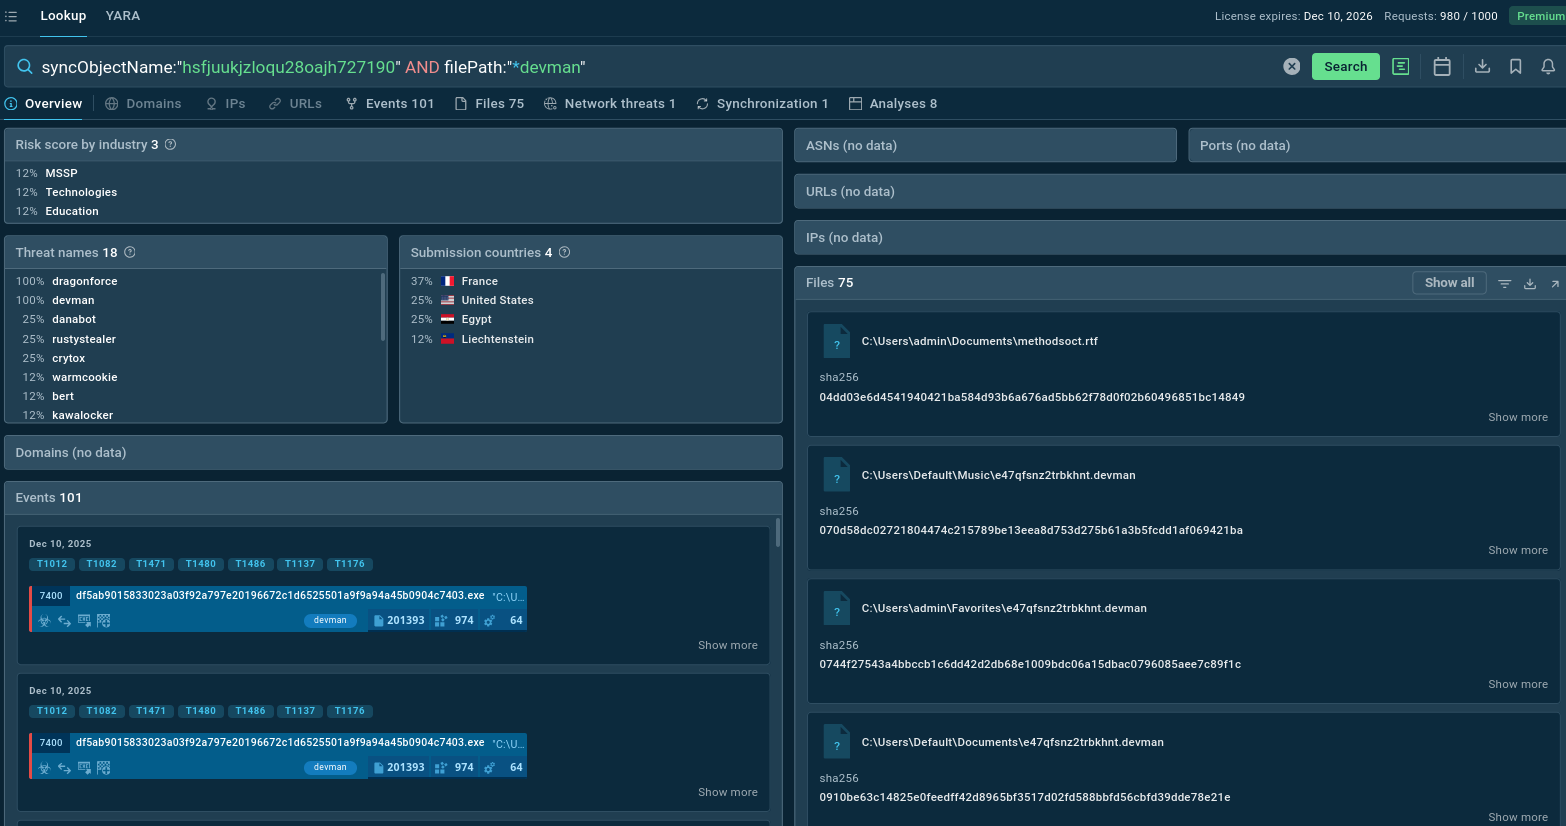
By querying suspicious files or network indicators against a vast database of malware samples analyzed in the Sandbox by over 15K SOCs worldwide, security teams can quickly determine whether observed activity relates to known DEVMAN campaigns.
You can also use Threat Intelligence Lookup to find more live DEVMAN samples and indicators by searching a signature IOC like the mutex this ransomware usually features:
syncObjectName:"hsfjuukjzloqu28oajh727190" and filePath:"devman"
Conclusion
DEVMAN exemplifies the ransomware ecosystem's resilience, recycling Conti-era code into a profitable RaaS machine that preys on global enterprises with surgical precision. From its affiliate roots to independent empire-building, it underscores the need for vigilant, layered defenses amid code-sharing cartels. As attacks proliferate (now over 120 victims), organizations must invest in TI, sandboxes, and resilience to outpace these digital extortionists, turning potential catastrophes into manageable risk.
Trial TI Lookup to start gathering actionable threat intelligence on emerging malware: just sign up to ANY.RUN.
Other malware & phishing threats
 MassLoggerMassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems.
It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
 ClickFixClickFix is a sophisticated social engineering technique that tricks users into manually executing malicious commands on their devices. It masquerades as a "quick fix" for fake technical issues, CAPTCHA verifications, or error messages, often hijacking the clipboard to paste harmful PowerShell or terminal commands. This user-assisted approach helps it bypass traditional security controls, leading to infostealers like Lumma Stealer, RATs, and other malware.
 Mamba 2FAMamba 2FA is an advanced phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) and target Microsoft 365 accounts. It focuses on intercepting authentication flows in real-time and enables threat actors to hijack user sessions and access sensitive systems even when additional security measures are in place.
 GravityRATGravityRAT is a sophisticated spyware and remote access trojan that has been actively targeting organizations and government entities since 2016. It uses innovative anti-analysis techniques and made an evolution from a Windows-only threat to a cross-platform espionage tool capable of compromising Windows, Android, and macOS systems.
 DarkTortillaDarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.
 FormbookFormBook is a data stealer that is being distributed as a MaaS. FormBook differs from a lot of competing malware by its extreme ease of use that allows even the unexperienced
threat actors to use FormBook virus.