SolarisLoader
- 56
- Global rank
- 43
- Month rank
- 40
- Week rank
SolarisLoader is a malware loader designed to neutralize security infrastructure before deploying high-risk secondary payloads. It utilizes a "Bring Your Own Vulnerable Driver" technique to gain kernel-level access and terminate antivirus processes. To remain undetected, the malware patches internal Windows monitoring interfaces and isolates the machine from security updates. Finally, it establishes a resilient three-layer persistence mechanism involving scheduled tasks, registry backups, and a watchdog component.
- Loader
- Type
- Unknown
- Origin
- 1 June, 2026
- First seen
- 19 October, 2026
- Last seen
How to analyze SolarisLoader with ANY.RUN
IOCs
IP addresses
- 104.20.29.150
- 140.82.121.4
- 142.251.20.100
- 178.33.86.200
- 185.199.109.133
- 188.114.96.3
- 142.251.127.84
- 152.236.9.75
- 213.190.6.96
- 64.89.163.22
- 45.141.27.27
- 91.92.242.236
- 142.251.20.102
- 208.67.222.222
- 40.91.108.115
- 193.178.158.57
- 23.52.181.212
- 89.208.104.175
- 149.154.167.99
- 61.249.139.64
Hashes
- ab5c71347d95f319781df230012713c7819ac0d69373e8c9a7302cae3f9a04b7
- 92804faaab2175dc501d73e814663058c78c0a042675a8937266357bcfb96c50
- 42b55d126d1e640b1ed7a6bdcb9a46c81df461fa7e131f4f8c7108c2c61c14de
- e728f79439e07df1afbcf03e8788fa0b8b08cf459db31fc8568bc511bf799537
- 7f0121322785c107bfdfe343e49f06c604c719baff849d07b6e099675d173961
- aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
- 2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
- f096bc366a931fba656bdcd77b24af15a5f29fc53281a727c79f82c608ecfab8
- c43668eec4a8d88a5b3a06a84f8846853fe33e54293c2db56899a5a5dfb4d944
- 14dec7d1c20fc426ad5463d1b658f87a22f7e576ba4a08905caf399551813a72
- a3c916ba16bcac9faa5a1ccc62aca61452d581cd8ba3ee07ec39122c697274c9
- 1700af47dc012a48cec89cf1dfae6d1d0d2f40ed731eff6ca55296a055a11c00
- 294f3e46c55453edad44567e1330f9b43e69a07fa0655b24dd2780a4490c1194
- cfe4e44a3a751f113847667ec9ea741e762bbde0d4284822cb337df0f92c1aca
- 1fc13070cf661488e90fece84274c46b1f4cc7e1565eab8f829ccaa65108dfca
- dba0584b8e1925b439f06e0bf0965e97afb7eb39e70e0e4c9b70769ebc5f996c
- e269029c8263e3cbc1920c3604ecdcf15edccb208a0d68f9eb42b73954d620c0
- 3e59379f585ebf0becb6b4e06d0fbbf806de28a4bb256e837b4555f1b4245571
- 031ed0378f819926d7b5b2c6c9367a0fb1cbae40e1a3959e2652fe30a47d52f2
- 27f13c4829994b214bb1a26eef474da67c521fd429536cb8421ba2f7c3e02b5f
Domains
- optimizationguide-pa.googleapis.com
- rr3---sn-aj5goc-5x.gvt1.com
- star.zcnet.net
- clientservices.googleapis.com
- redirector.gvt1.com
- clients2.google.com
- login.live.com
- clients2.googleusercontent.com
- mf.91yunma.cn
- amm-frosty.lol
- th.bing.com
- cs.go.kg
- www.vuelaviajero.com
- parad0x.hopto.org
- cdasqoryfbdg.co.uk
- crl.microsoft.com
- safebrowsingohttpgateway.googleapis.com
- yr.c.lencr.org
- steamcommunity.com
- safebrowsing.googleapis.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f19%2f2026%2c%202%3a35%3a43%20pm
- https://www.bing.com/th?id=odswg.07bae8d4-9f7f-4621-a752-18358a102dfc&pid=dsb
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
- http://31.77.144.86:49104/rigel.exe
- http://31.77.144.86:49104/xmrig.exe
- http://193.178.158.107/bin/54b1d5157895e316_visionary_7030.74.5_install.exe
- http://193.178.158.57/bin/a0573101cdb434fe_build_x64.exe
- http://62.60.226.140/amka/file.exe
- http://193.178.158.57/bin/054b66d3943934ef_cryptoclipper.exe
- http://193.178.158.57/bin/7e2e3164f26a442a_syshost_loader.exe
- http://31.40.204.4/24/secured_stub.ps1
- http://31.40.204.4/22/wemadebest.hta
Last seen at
Key Takeaways
- Kernel-Level Defense Dismantling: SolarisLoader utilizes a "Bring Your Own Vulnerable Driver" (BYOVD) technique, exploiting a vulnerable Safetica endpoint protection driver (CVE-2026-0828) to gain kernel-level access and forcibly terminate security processes.
- Telemetry Blinding: The malware prevents the operating system from logging or reporting malicious activity by patching the Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW) in memory via direct opcode modification.
- Resilient Triple-Layer Persistence: The infection survives standard cleanup through a combination of scheduled tasks, registry-backed backups (ICtrlData), and a watchdog process that injects code into legitimate system files like RuntimeBroker.exe.
- ANY.RUN’s Interactive Sandbox analysis confirms that the loader utilizes a silent COM-elevation/UAC-bypass path via dllhost.exe, enabling it to gain administrative privileges without triggering user-facing notifications or consent prompts.
- Active Malware-as-a-Service (MaaS) Cycle: The loader is in active development, functioning as a primary delivery vehicle for secondary payloads such as StealC, Amadey, and REMCOS RAT.
What is SolarisLoader?
SolarisLoader is a sophisticated Malware-as-a-Service (MaaS) delivery vehicle designed to dismantle a system's security infrastructure before deploying high-risk secondary payloads. First identified in early 2026, the malware is characterized by its aggressive approach to antivirus software: rather than merely attempting to hide, it actively seeks and destroys security processes from the kernel level. While it does not typically steal data itself, it creates a "blind spot" on the infected host, clearing the way for infamous stealers and loaders like Amadey.
The malware is primarily distributed through fake software installers bundled with cracked or pirated versions of popular applications and games. This distribution strategy exploits users who are already attempting to bypass legitimate software protocols, making them less likely to question the silent background installations or administrative requests that occur during the infection chain. In some instances, the loader will even drop and execute the legitimate cracked software after the infection is complete to further reduce user suspicion.
Technical analysis reveals that SolarisLoader is a highly professional product undergoing rapid evolution. Since its emergence, researchers have tracked its maturation from version 1.2.0 to 1.8.2, observing iterative refinements in its C2 communication protocols, anti-analysis techniques, and persistence mechanisms. Its core design prioritizes persistence and stealth; it utilizes a dedicated watchdog component (often recovered via PDB paths as "Solaris") that monitors the system and automatically re-initiates the malware implant if it is terminated or deleted. By combining kernel-level exploits with telemetry patching, SolarisLoader ensures that a compromised system's own security stack reports nothing unusual even as secondary payloads are actively executed.
How SolarisLoader Threatens Businesses and Organizations
For modern enterprises, SolarisLoader’s primary threat lies in its ability to create a "permanent blind spot" on an infected workstation, ensuring that subsequent malicious activities go entirely undetected by traditional monitoring tools.
Unlike most loaders that attempt to hide from security software, SolarisLoader uses a "Bring Your Own Vulnerable Driver" (BYOVD) technique to gain kernel-level access. By exploiting CVE-2026-0828 in the Safetica endpoint protection driver, the malware achieves the same system privileges as the security software itself, allowing it to forcibly terminate Windows Defender and major third-party antivirus processes like Avast, AVG, and 360 Total Security. The malware systematically "blinds" the operating system by patching the Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW) directly in memory. This ensures that even if follow-on payloads execute suspicious scripts or file operations, the OS will not generate the event logs or telemetry needed for EDR (Endpoint Detection and Response) or SOC teams to flag the intrusion.
Victimology: Who Is Most Vulnerable?
The targeting profile of SolarisLoader is opportunistic and designed to exploit gaps in both technical controls and user behavior. While its distribution is global, specific technical markers reveal focused targeting strategies:
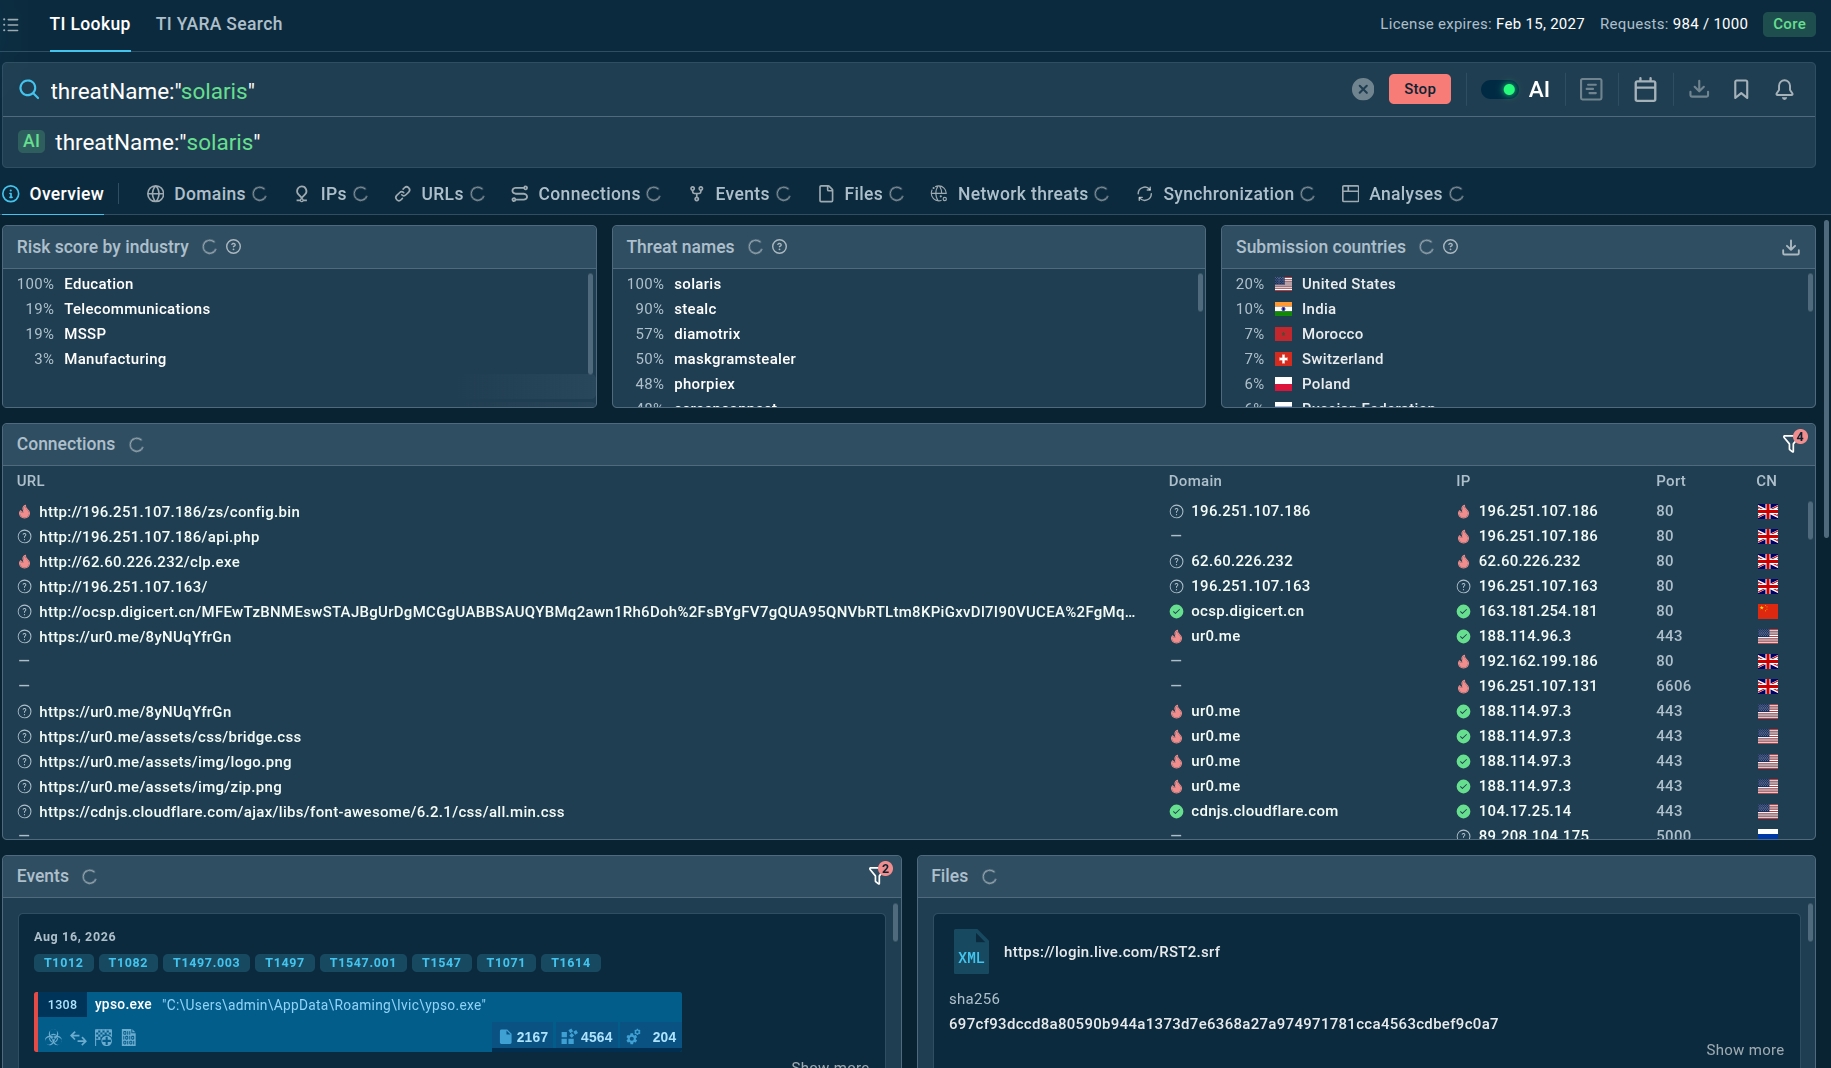
- US and EU Companies: According to ANY.RUN’s [Threat Intelligence Lookup], the majority of Solaris Loader attacks affected businesses from the United States and the European Union.
- Organizations with Permissive Local Admin Rights: SolarisLoader relies on gaining administrative privileges to execute its most damaging stages, such as driver loading and hosts file modification. It utilizes a silent COM-elevation/UAC-bypass path via dllhost.exe, which means users running with local administrative rights can be compromised without ever seeing a permission prompt.
- Global Enterprise Users: The malware's targeting of global suites like Avast, AVG, and ReasonLabs makes it a universal threat. Any organization relying solely on signature-based antivirus or standard Windows telemetry (AMSI/ETW) is highly vulnerable, as SolarisLoader's telemetry-blinding and BYOVD techniques are specifically designed to defeat these common defenses.
- Secondary Infection Targets: Systems already compromised by other loaders, such as XTinyLoader or Amadey, are frequently targeted for SolarisLoader deployment, as it is often used as an intermediate stage to clear security hurdles before a final payload is delivered.
How Does SolarisLoader Function?
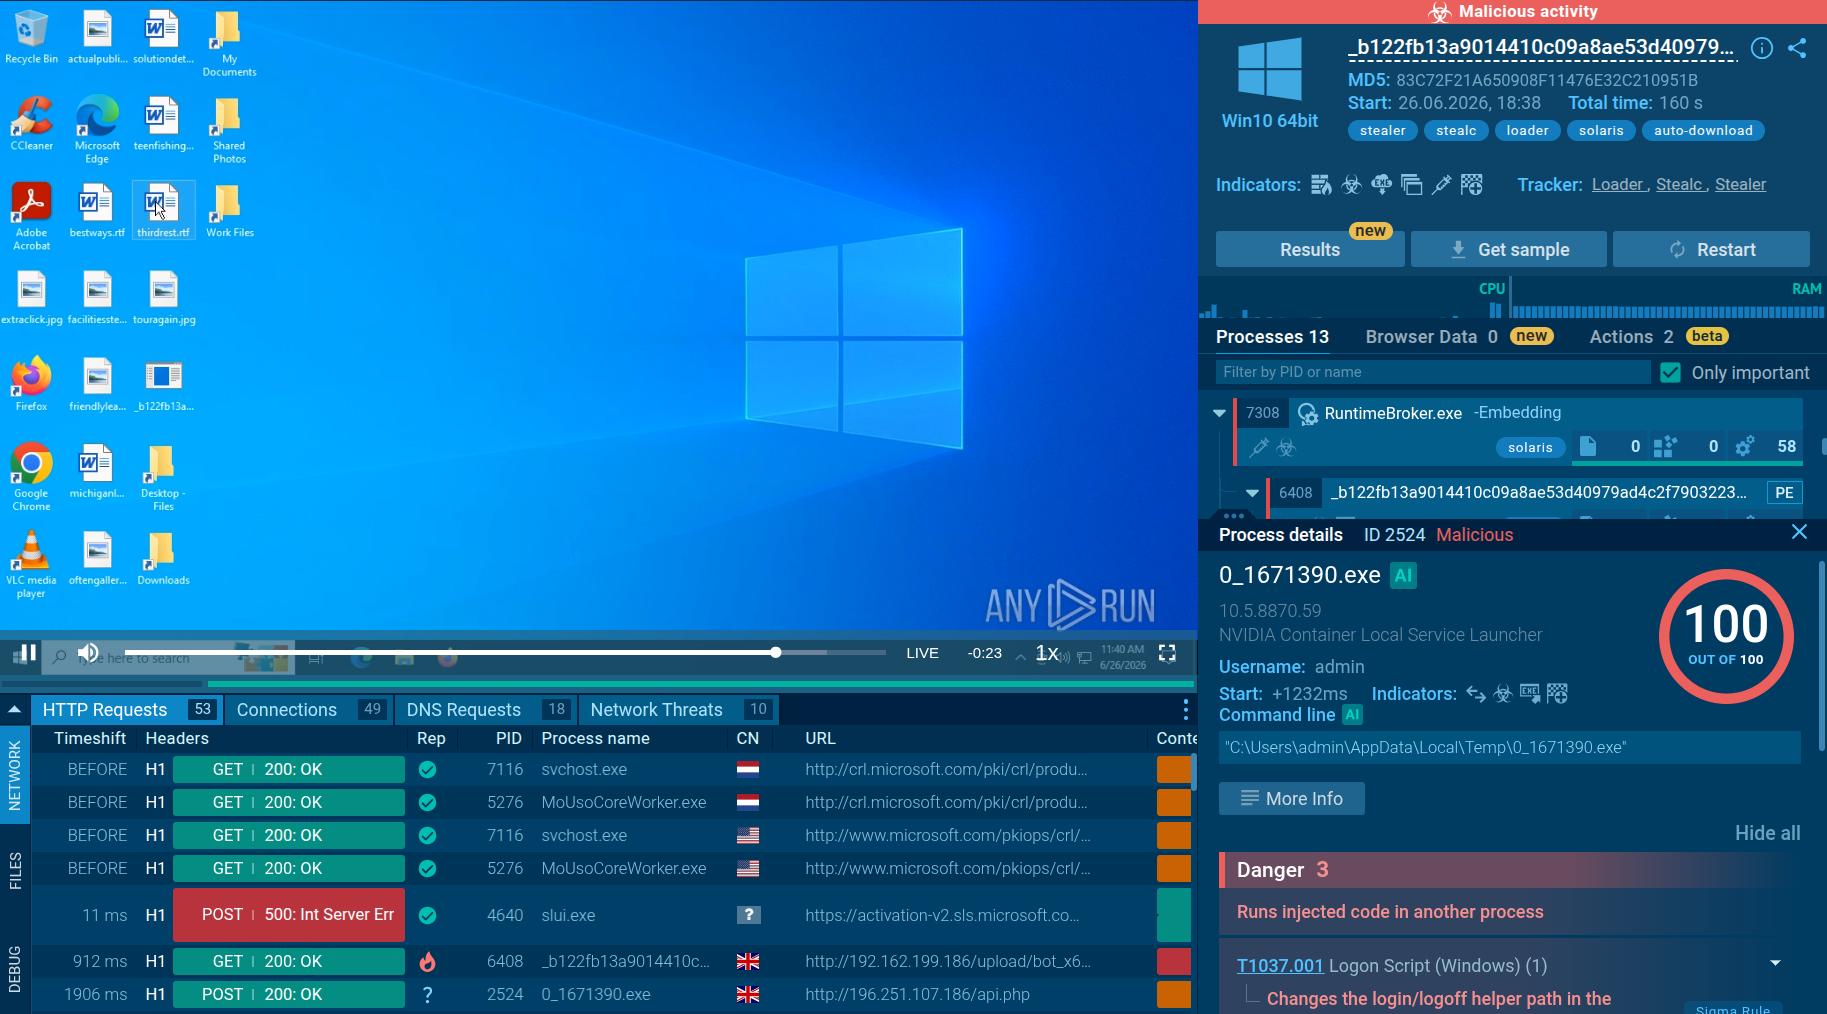
Detonating a SolarisLoader sample inside ANY.RUN’s Interactive Sandbox reveals a highly aggressive and multi-staged attack chain designed to neutralize system defenses before establishing a permanent foothold. By moving beyond simple file execution, the loader utilizes a series of strategic maneuvers to blind the operating system and deliver high-risk secondary payloads.
Stage 1: Initial Execution and Silent Elevation
The infection typically begins when the user executes a malicious installer, which runs from the user's Temp directory. Upon launch, the malware drops several staged components into the %TEMP% folder, including WinSysKdrv.exe, 0_1671390.exe, and 1_1675328.exe.
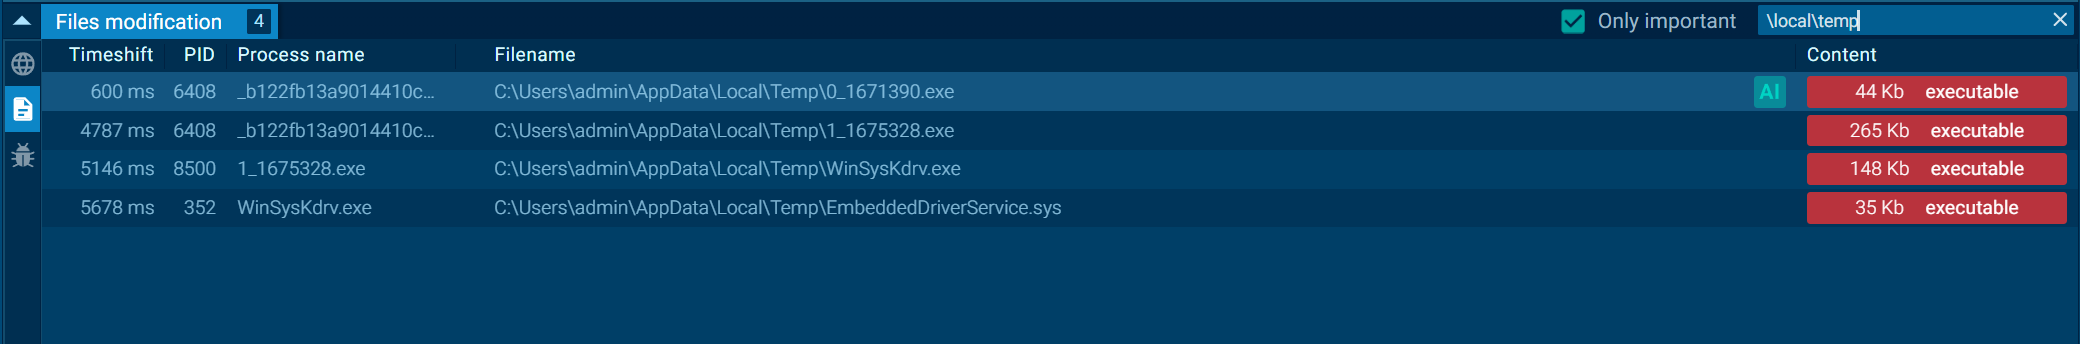 SolarisLoader detonated inside ANY.RUN’s Interactive Sandbox
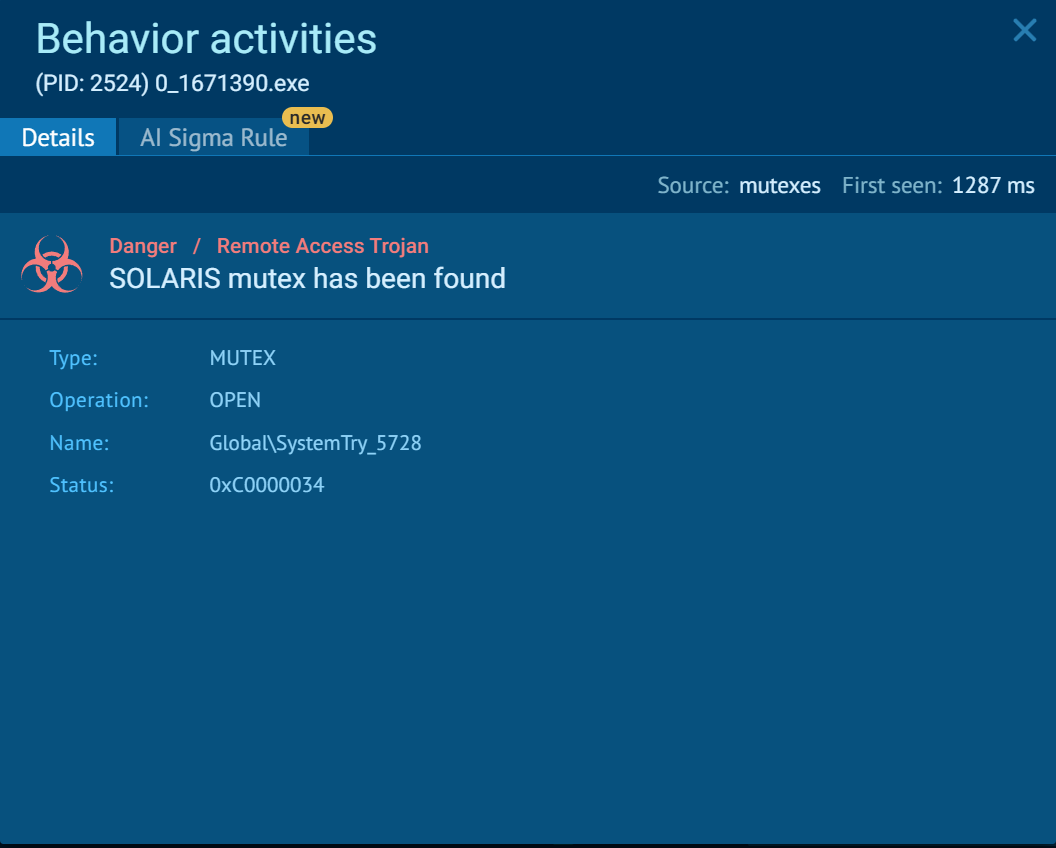
To gain the administrative privileges necessary for its subsequent stages without alerting the user, the loader spawns WinSysKdrv.exe through dllhost.exe (COM surrogate), a technique consistent with a silent COM-elevation/UAC-bypass path. Early in this execution phase, the sample creates the SOLARIS mutex, which acts as both an execution guard and an infection marker on the host to prevent multiple instances from running simultaneously.
Stage 2: Defense Dismantling and Network Isolation
Once elevated, SolarisLoader immediately begins systematically dismantling the endpoint's security stack. The sandbox analysis highlights several critical actions:
- Neutralizing Windows Defender: The malware disables real-time protection and modifies registry values associated with security policies and exclusion lists to prevent detection.
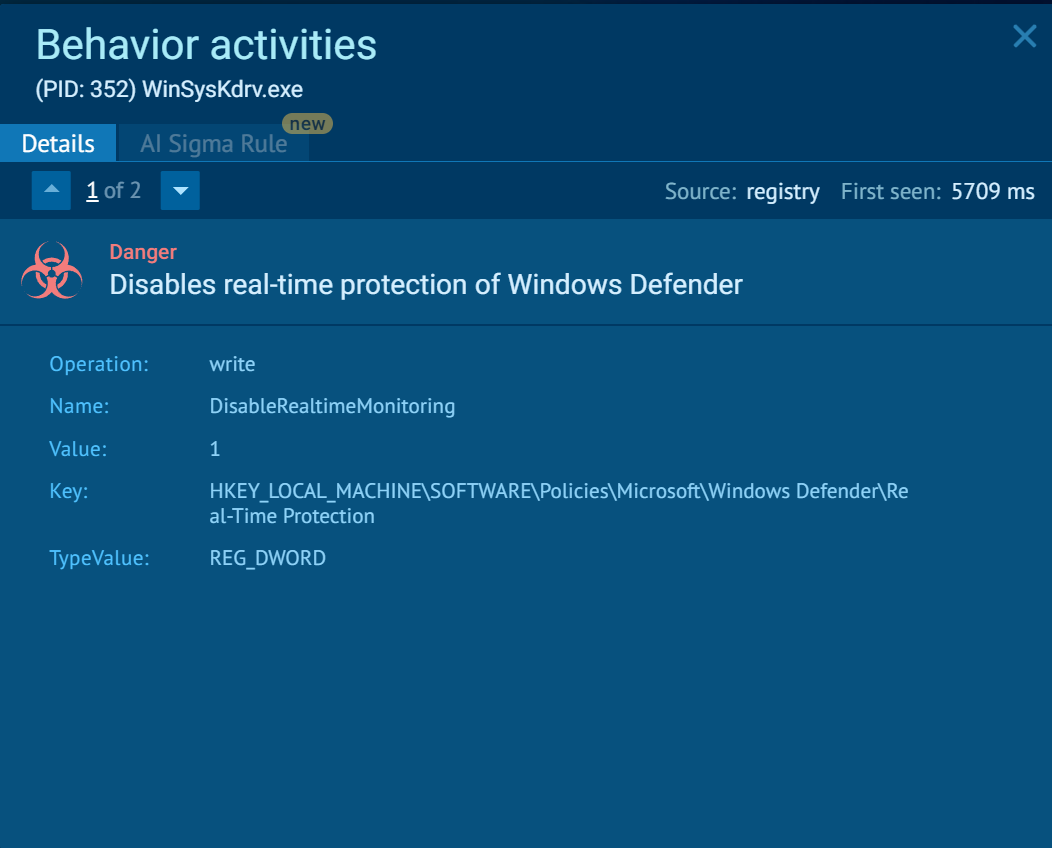
- Kernel-Level Tampering: The loader creates or modifies Windows services specifically tied to kernel-driver loading. This allows the malware to achieve defense evasion by operating at the same privilege level as the operating system's core.
- Network Isolation: To prevent the machine from receiving updates or communicating with security telemetry servers, the malware rewrites the Windows hosts file. It redirects critical security and telemetry domains to unreachable local addresses, effectively isolating the host from external remediation.
Stage 3: Resilient Persistence and Watchdog Behavior
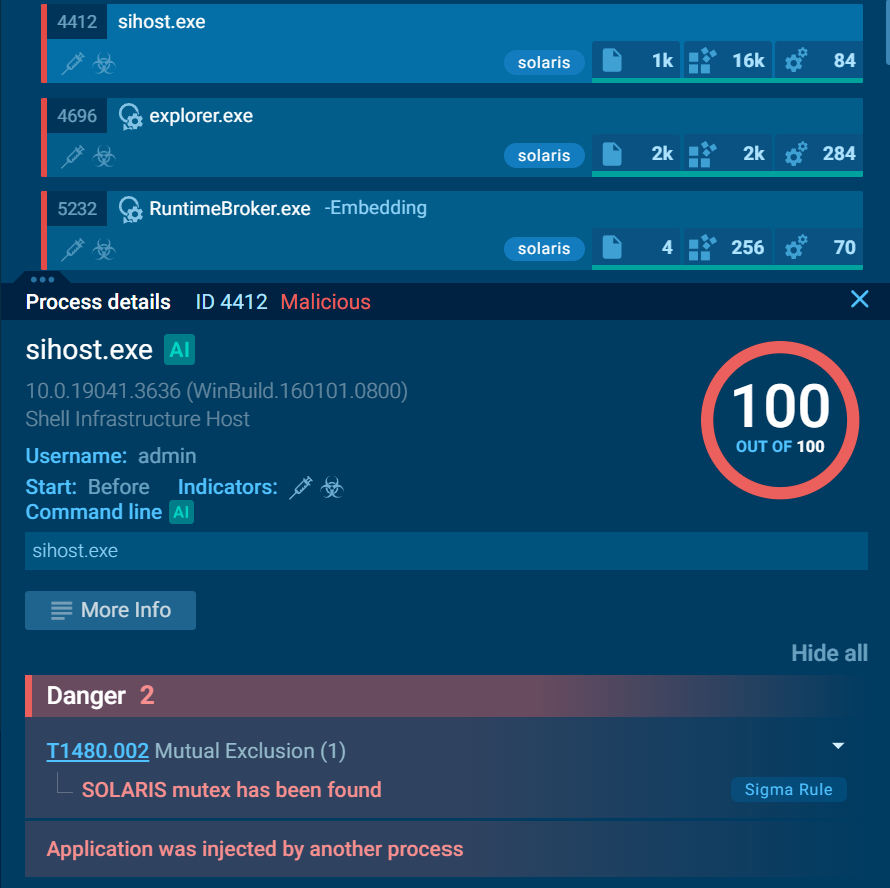
SolarisLoader is engineered for maximum resilience against manual or automated cleanup. It ensures survival through two primary mechanisms:
- Process Injection: The malware injects malicious code into legitimate system processes, specifically RuntimeBroker.exe and sihost.exe. This acts as a watchdog, where these trusted system components monitor the infection and can re-initiate the malware if it is interrupted.
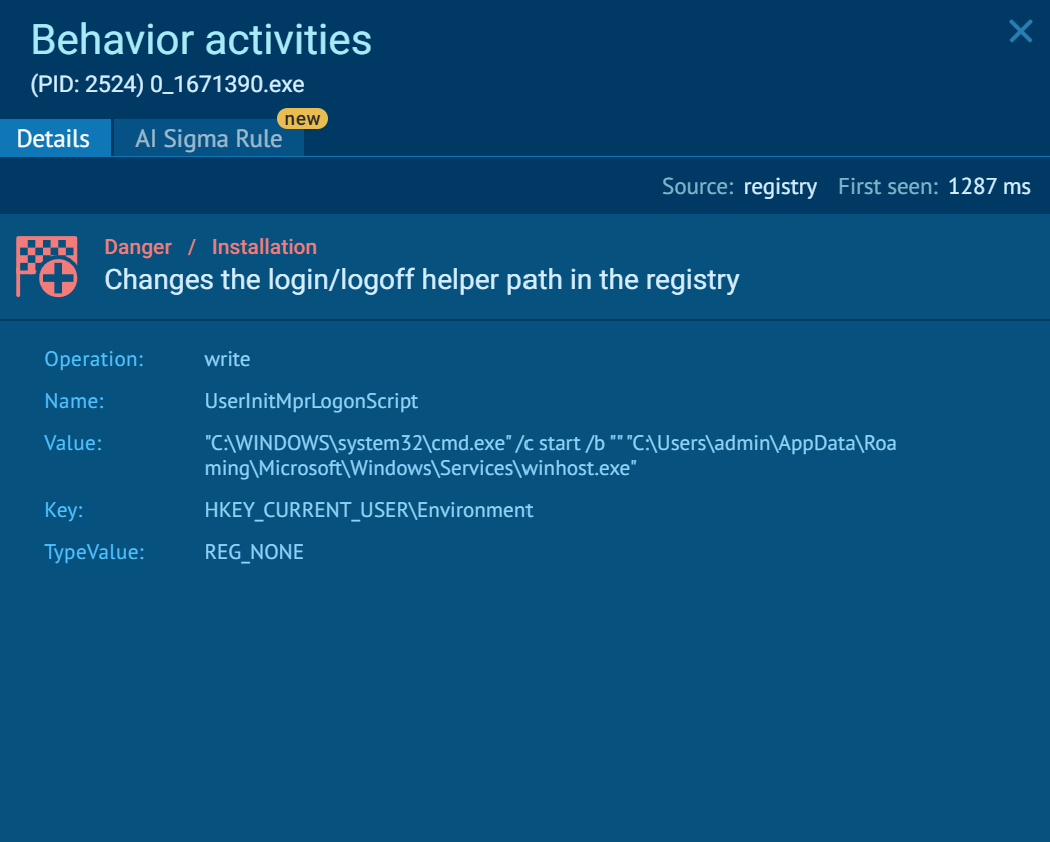
- Registry-Based Fallback: For long-term survival, it sets a login/logoff helper path in the registry as a fallback mechanism, ensuring the loader re-executes whenever a user logs into the system.
Stage 4: Host Reconnaissance (Fingerprinting)
Before contacting its command-and-control (C2) infrastructure, SolarisLoader performs a thorough reconnaissance of the infected workstation to create a unique host fingerprint.
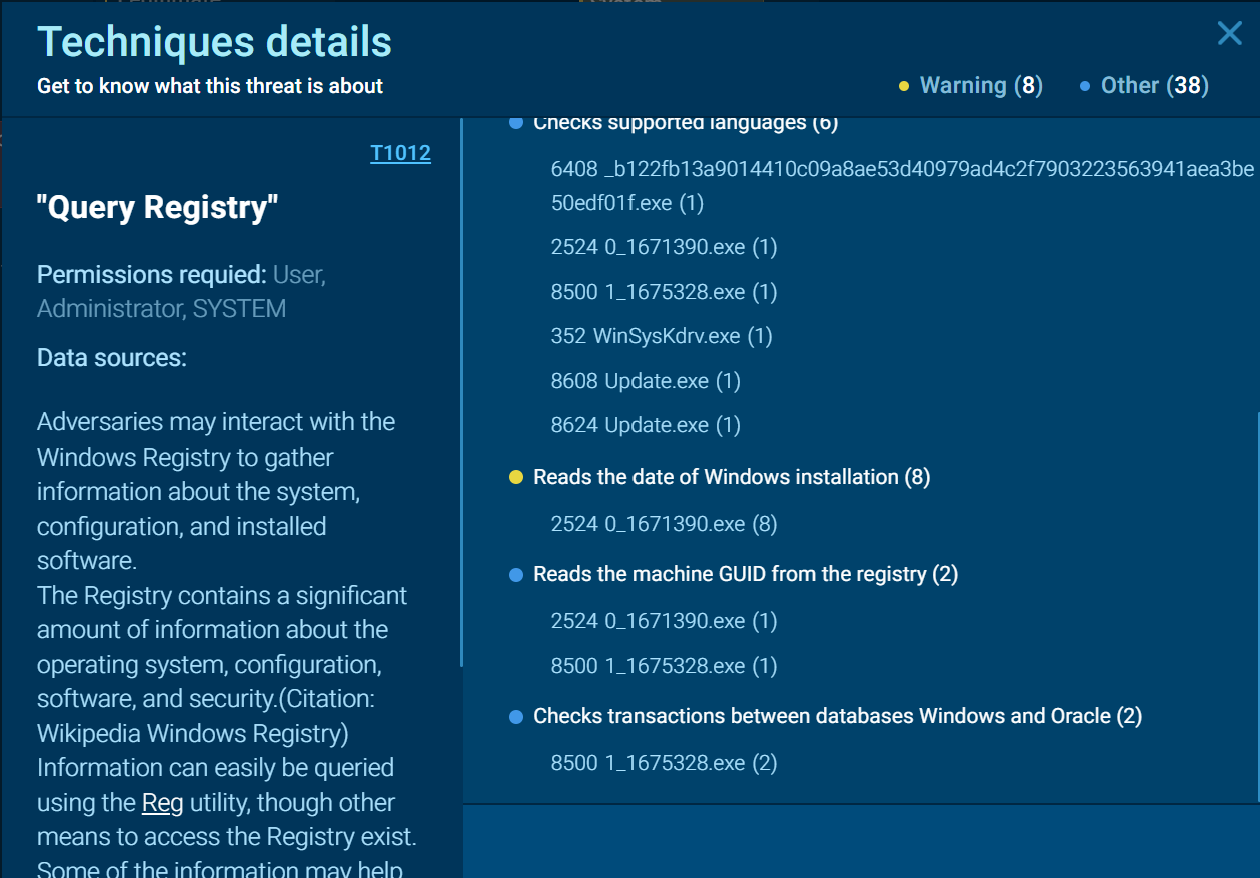
The sandbox observed the malware harvesting the following data points: Computer name and machine GUID, Windows installation date and system location settings, Supported system languages.
Stage 5: C2 Communication and Payload Delivery
The final stage of the attack involves establishing communication with the attacker's infrastructure to fulfill its role as a loader. The sample beacons to a specific C2 endpoint at 196[.]251[.]107[.]186/api.php.

Following this check-in, the loader was observed pulling additional malicious payloads, including bot_x64.exe and klr.exe, from a secondary IP address (192[.]162[.]199[.]186) that has been flagged as malicious. This confirms that SolarisLoader's ultimate goal is to serve as a delivery vehicle for further staged malicious activity.
How Businesses Can Use ANY.RUN’s Threat Intelligence Against Solaris
Because SolarisLoader operates as an evolving Malware-as-a-Service (MaaS) with infrastructure and file names that rotate rapidly, traditional static blocklists are often insufficient for long-term protection. Security teams must shift from tracking temporary indicators to identifying the durable technical fingerprints and behavioral patterns of the operation. By leveraging ANY.RUN’s Threat Intelligence, organizations can stay ahead of these evolving campaigns.
Threat Intelligence Lookup allows analysts to pivot from a single suspicious artifact to an entire cluster of related malicious activity.
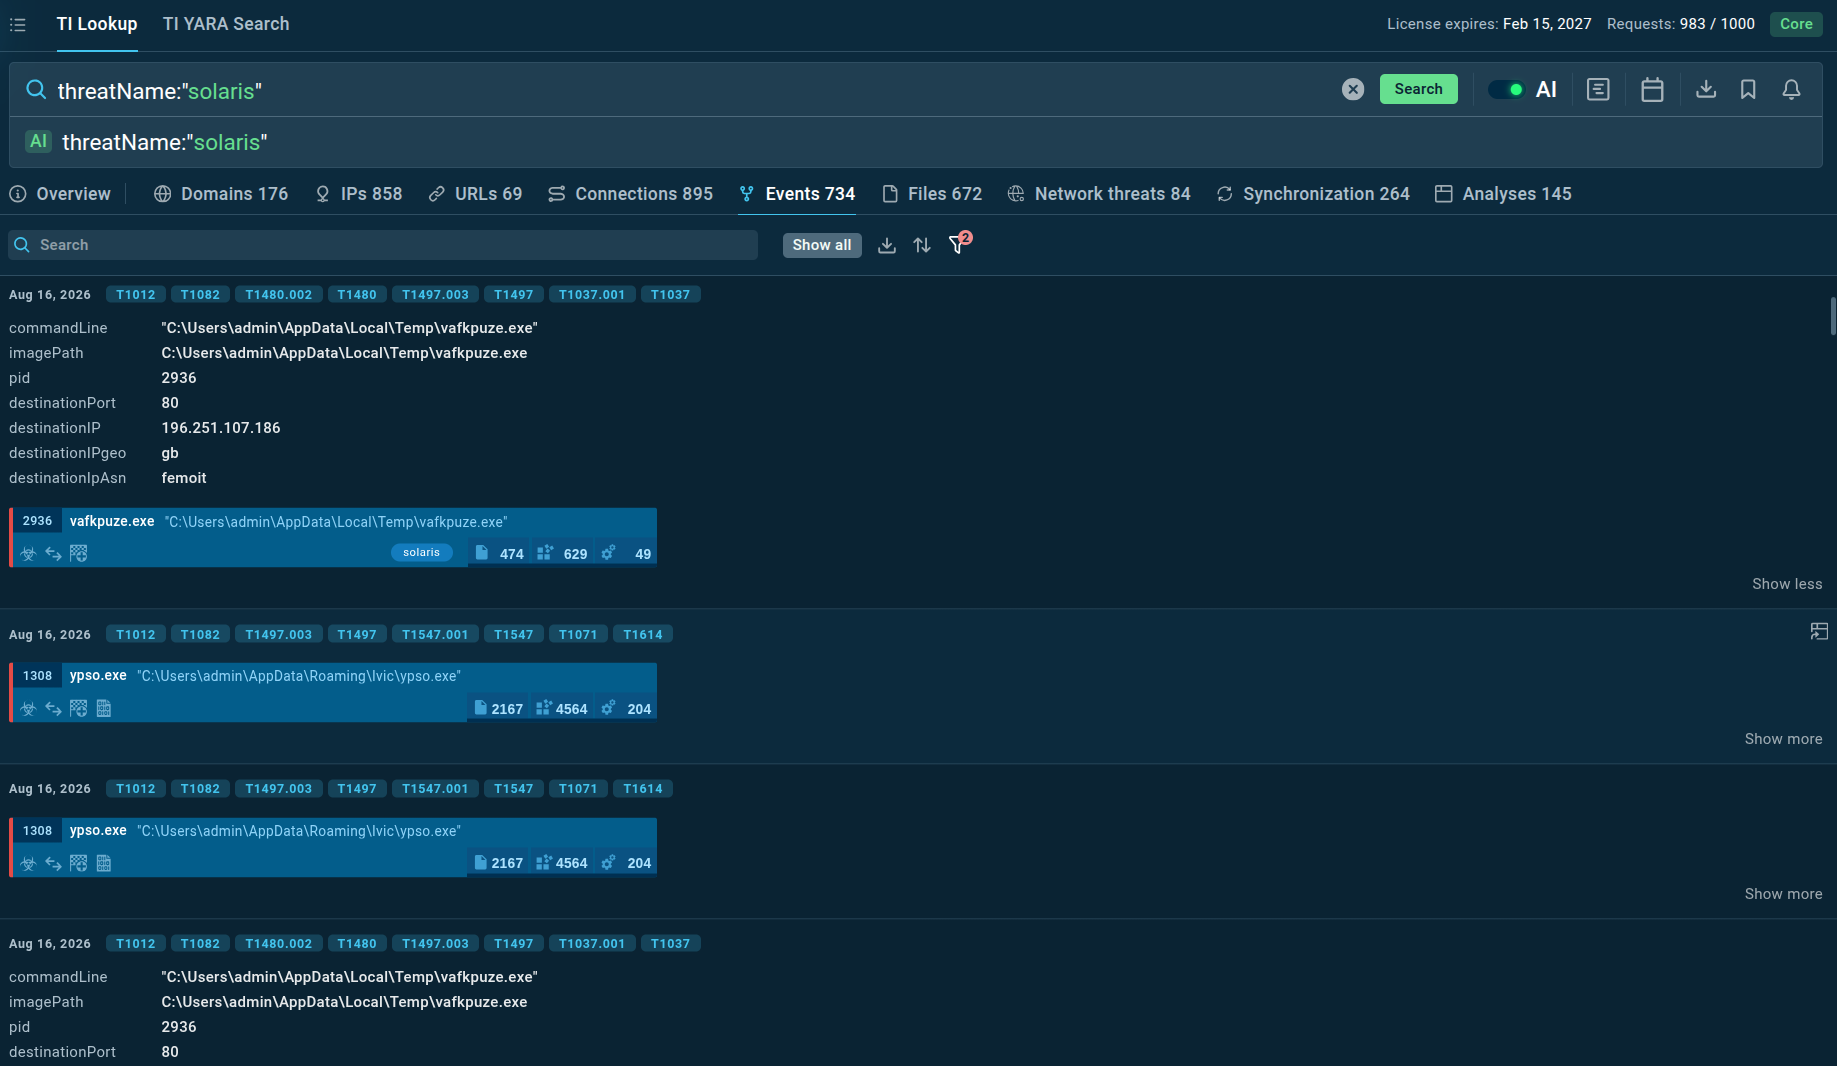
TI Lookup delivers a complete context on the threat, providing rich intelligence on SolarisLoader attacks, including network indicators, mutexes, file names, as well as full sandbox sessions that demonstrate the entire execution cycle from start to finish. For organizations requiring automated, high-speed protection, ANY.RUN’s Threat Intelligence Feeds provide a real-time stream of validated indicators. These feeds deliver a continuous flow of the latest C2 domains and malicious IPs directly into SIEM, SOAR, and EDR platforms. By integrating these feeds, teams can automatically block emerging malicious infrastructure, such as rotating fake-installer portals, and detect active breaches before data exfiltration occurs.
Conclusion
SolarisLoader represents a strategic shift in the cybercrime landscape, moving beyond simple evasion to the systematic neutralization of the entire security stack. By combining kernel-level exploits with telemetry blinding, the malware creates an environment where secondary payloads can operate with total visibility while the operating system remains unaware of the intrusion. To combat this evolving threat, organizations must move beyond static blocklists and reactive defenses, adopting a strategy that prioritizes behavioral analysis and proactive threat intelligence. Utilizing interactive sandboxing is essential to deobfuscate the loader's multi-stage logic and identify the durable technical signals, such as unauthorized driver loading and system-level telemetry tampering, before the successful delivery of high-risk secondary infections.
Frequently Asked Questions: SolarisLoader
1. What is SolarisLoader?
SolarisLoader is a specialized malware delivery vehicle designed to gain a persistent foothold on a host, disable its security tools, and deliver secondary infections like stealers and remote access trojans. It is sold on a subscription basis, allowing various threat actors to deploy it as a primary entry point for broader campaigns.
2. How does SolarisLoader bypass traditional security software?
The malware utilizes a "Bring Your Own Vulnerable Driver" (BYOVD) technique, exploiting a documented vulnerability in a legitimate third-party driver to achieve kernel-level privileges. This gives the loader the same system permissions as the security software it is attacking, allowing it to forcibly terminate security processes and endpoint detection services.
3. Why is a "clean" security scan result not trustworthy if this malware is present?
SolarisLoader specifically patches internal monitoring interfaces, such as the Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW), in memory. This "blinds" the system’s own telemetry, preventing it from logging or reporting malicious activity even if the security software remains active.
4. How can organizations use interactive sandboxing and threat intelligence to stay protected?
Interactive sandboxing is essential to expose the modular logic that evades automated scanners, allowing defenders to see how the malware escalates privileges and dismantles defenses in real-time. Proactive threat intelligence allows teams to identify stable build-chain fingerprints and block rotating C2 infrastructure before it reaches the endpoint.
5. What are the key indicators of a SolarisLoader infection?
Defenders should monitor for unauthorized redirects in the system hosts file (pointing security domains to unroutable addresses), the creation of scheduled tasks disguised as system security checks, and unauthorized additions to security exclusion lists. The presence of specific binary data in the system registry also serves as a backup for the malware's self-healing loop.
Other malware & phishing threats
 GCleanerGCleaner is a type of malware loader that has the capability to deliver numerous malicious software programs, which differ based on the location of the targeted victim. This malware is commonly spread through fraudulent websites that advertise free PC optimization tools
 NemtyNemty is ransomware with an unusually complex encryption algorithm. This malware encrypts user files and demands money so that they can be unlocked again. It may be connected to other famous ransomware, but we don’t know for sure.
 Play RansomwarePlay aka PlayCrypt ransomware group has been successfully targeting corporations, municipal entities, and infrastruction all over the world for about three years. It infiltrates networks via software vulnerabilities, phishing links and compromised websites. The ransomware abuses Windows system services to evade detection and maintain persistence. Play encrypts user files and steals sensitive data while demanding a ransom.
 Crimson RATCrimson is a Remote Access Trojan — a malware that is used to take remote control of infected systems and steal data. This particular RAT is known to be used by a Pakistani founded cybergang that targets Indian military objects to steal sensitive information.
 BlindEagleBlindEagle is a cyber threat actor primarily associated with espionage and credential theft campaigns targeting organizations in Latin America, especially Colombia. Active since at least 2018, the group relies heavily on phishing, remote access trojans (RATs), PowerShell scripts, and social engineering to infiltrate systems and maintain persistence. BlindEagle is known for continuously evolving its delivery mechanisms and malware stack to bypass detection and compromise high-value targets.
 KrakenKeyloggerKraken is a trojan malware with infostealing capabilities that was first spotted in May of 2023. The malware can perform a wide range of malicious activities, including logging users’ keystrokes. The data then can be sent to the attacker using several protocols. The operators behind the Kraken stealer usually distribute it via phishing emails.